Pentest
Sponsored
·
 SiteGround - Reliable hosting with speed, security, and support you can count on.
→
SiteGround - Reliable hosting with speed, security, and support you can count on.
→

Share
Embed
Pentest

वेणु गोपाल
February 20, 2010
Transcript
70 slides
-
Proposal Presentation for Secure Wired & Wireless Networks Project By
Maneesh & Venu Gopal -
Hacking is the unauthorized break in into computers/networks ...
Usually done by a bad guy (a.k.a Black Hat). Its not magic. It has a methodology. Many different Techniques (often change over time). New vulnerabilities are found (therefore new attacks over time). -
Testing the security of systems and architectures by a
white hat from a hacker’s (a.k.a black hats) point of view. A “simulated attack” with a predetermined goal. Telling too many people may invalidate the test. -
Footprinting Reconnaissance Scanning Enumeration Attack
Vulnerabilities Exploits Wipe off Traces Get out -
Application Specific Scanners Password Crackers Disassemblers
OS Detection Tools Sniffers Vulnerability Scanners Web Scanners Wireless Exploitation Packet Crafters Port Scanners 6 -
Footprinting is the technique of gathering information to
create a complete profile of an organization’s security posture. 8 -
1. Find out initial information: Open Source Whois
Nslookup 2. Find out address range of the network: ARIN (American registry for internet numbers) Traceroute 3. Find active machines: Ping 9 -
Locations Related companies or entities Merger or
acquisition news Phone numbers Contact names and email addresses Privacy or security policies indicating the types of security mechanisms in place Links to other web servers related to the organization 10 -
DNS queries The registrant The domain name
The administrative contact When the record was created and updated The primary and secondary DNS servers Network Ranges & blocks 11 -
Domain Name Network blocks Specific IP addresses
of systems reachable via the Internet TCP and UDP services running on each system identified System architecture (for example, SPARC vs. X86) Access control mechanisms and related access control lists (ACLs) Intrusion detection systems (IDSes) System enumeration (user- and group names, system banners, routing tables, SNMP information) 12 -
Networking protocols in use (for example, IP, IPX, )
Internal domain names Network blocks Specific IP addresses of systems reachable via the intranet TCP and UDP services running on each system identified System architecture (for example SPARC vs. X86) Access control mechanisms and related access control lists (ACLs) Intrusion detection systems System enumeration (user- and group names, system banners, routing tables, SNMP information) 13 -
Remote system type Authentication mechanisms Connection origination
and destination Type of connection Access control mechanism 14 -
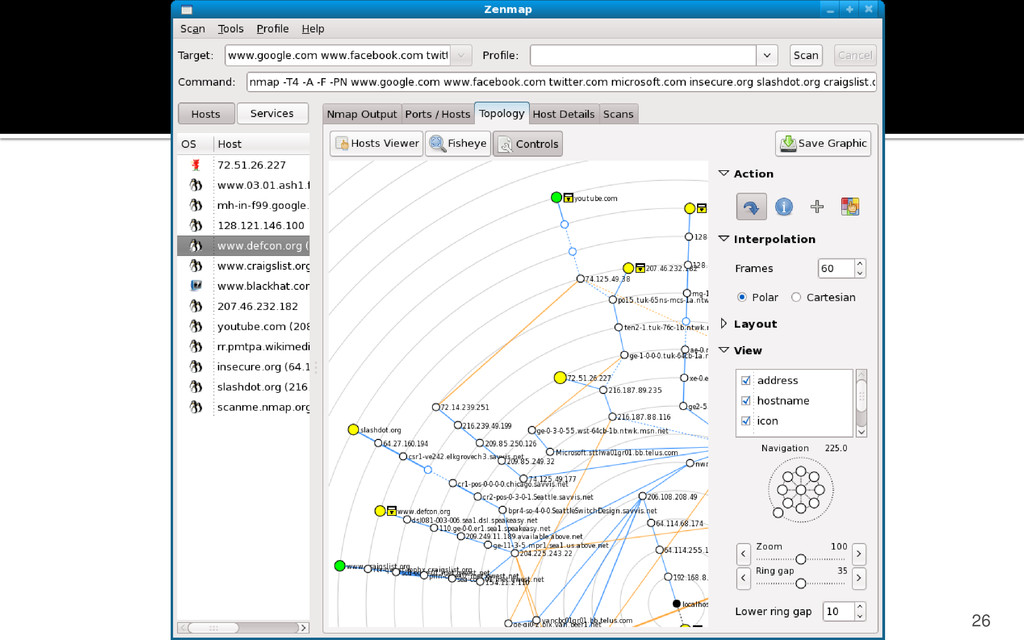
4. Find open ports or access points: Portscanners:
Nmap ScanPort War Dialers THC-Scan 5. Figure out the operating systems: Queso Nmap 16 -
6. Figure out which services are running on each port:
Default port and OS Vulnerability scanners 7. Map out the network: Traceroute Visual ping Cheops 17 -
Hosts that are accessible Locations of routers and
firewalls Operating systems running on key components Ports that are open Services that are running Versions of applications that are running 18 -
FIN probe A FIN packet is sent to an
open port. As mentioned previously, RFC 793 states that the correct behavior is not to respond; however, many stack implementations (such as Windows NT) will respond with a FIN/ACK. Bogus Flag probe An undefined TCP flag is set in the TCP header of a SYN packet. Some operating systems, such as Linux, will respond with the flag set in their response packet. Initial Sequence Number (ISN) sampling The basic premise is to find a pattern in the initial sequence chosen by the TCP implementation when responding to a connection request. “Don’t fragment bit” monitoring Some operating systems will set the “Don’t fragment bit” to enhance performance. This bit can be monitored to determine what types of operating systems exhibit this behavior. TCP initial window size Initial window size on returned packets is tracked. For some stack implementations, this size is unique and can greatly add to the accuracy of the fingerprint mechanism. 20 -
ACK value IP stacks differ in the sequence value
they use for the ACK field, so some implementations will send back the sequence number you sent, and others will send back a sequence number + 1. ICMP error message quenching Operating systems may follow RFC 1812 (www.ietf.org/rfc/rfc1812.txt) and limit the rate at which error messages are sent. By sending UDP packets to some random high-numbered port, it is possible to count the number of unreachable messages received within a given amount of time. ICMP message quoting Operating systems differ in the amount of information that is quoted when ICMP errors are encountered. By examining the quoted message, you may be able to make some assumptions about the target operating system. ICMP error message–echoing integrity Some stack implementations may alter the IP headers when sending back ICMP error messages. By examining the types of alterations that are made to the headers, you may be able to make some assumptions about the target operating system. 21 -
Type of service (TOS) For “ICMP port unreachable” messages,
the TOS is examined. Most stack implementations use 0, but this can vary. Fragmentation handling As pointed out by Thomas Ptacek and Tim Newsham in their landmark paper “Insertion, Evasion, and Denial of Service: Eluding Network Intrusion Detection” (http://www.clark.net/ ~roesch/idspaper.html), different stacks handle overlapping fragments differently. Some stacks will overwrite the old data with the new data and vice versa when the fragments are reassembled. By noting how probe packets are reassembled, you can make some assumptions about the target operating system. TCP options TCP options are defined by RFC 793 and more recently by RFC 1323 (www.ietf.org/rfc/rfc1323.txt). The more advanced options provided by RFC 1323 tend to be implemented in the most current stack implementations. By sending a packet with multiple options set, such as no operation, maximum segment size, window scale factor, and timestamps, it is possible to make some assumptions about the target operating system. 22 -
TTL What does the operating system set as the
time-to-live on the outbound packet? Window Size What does the operating system set as the Window Size? DF Does the operating system set the Don’t Fragment bit? TOS Does the operating system set the type of service, and if so, at what? 23 -
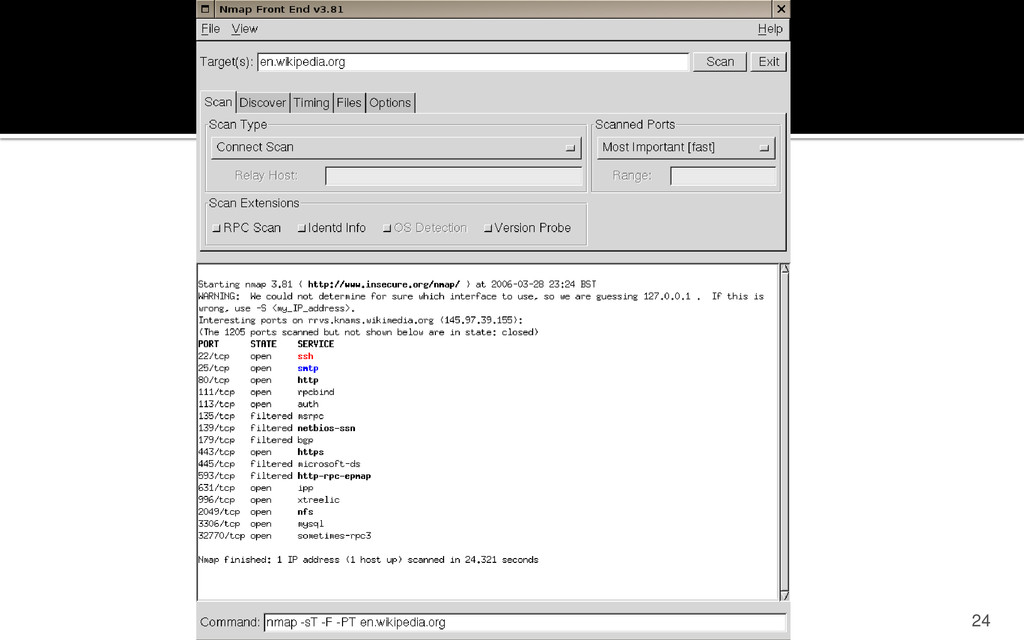
nmap -I 192.168.1.10 Starting nmap V. 2.53 by [email protected] Port
State Protocol Service Owner 22 open tcp ssh root 25 open tcp smtp root 80 open tcp http root 110 open tcp pop-3 root 113 open tcp auth root 6000 open tcp X11 root 25 -
Network resources and shares Users and groups
Applications and banners 28 -
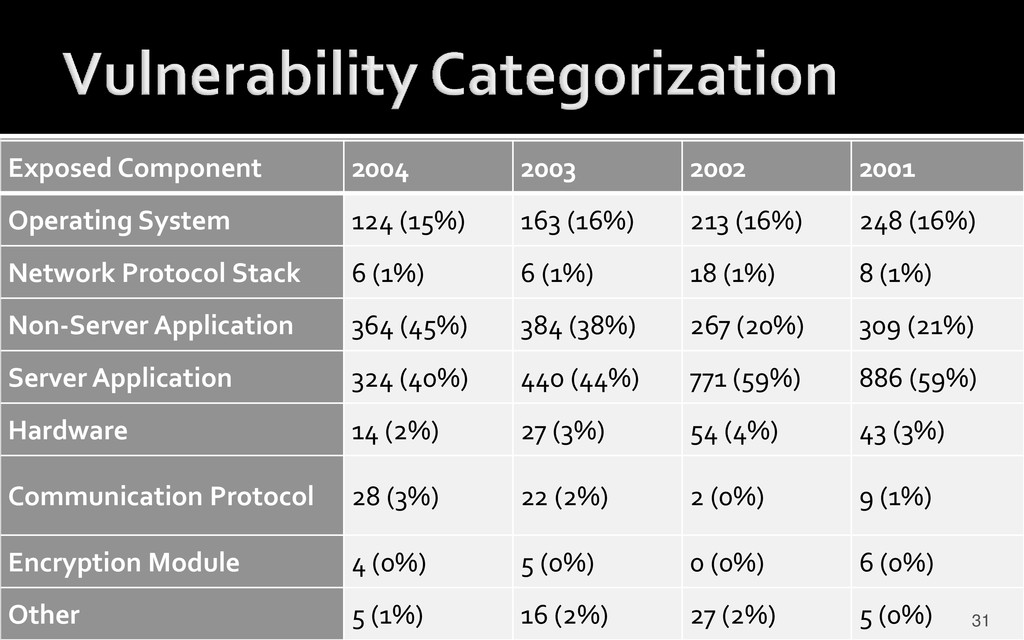
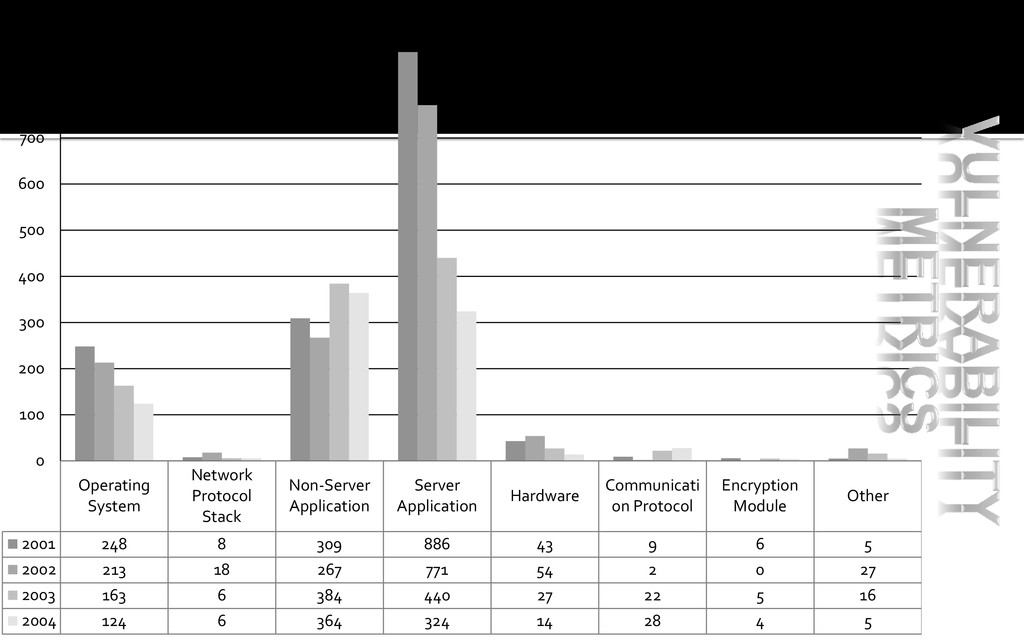
Exposed Component 2004 2003 2002 2001 Operating System 124 (15%)
163 (16%) 213 (16%) 248 (16%) Network Protocol Stack 6 (1%) 6 (1%) 18 (1%) 8 (1%) Non-Server Application 364 (45%) 384 (38%) 267 (20%) 309 (21%) Server Application 324 (40%) 440 (44%) 771 (59%) 886 (59%) Hardware 14 (2%) 27 (3%) 54 (4%) 43 (3%) Communication Protocol 28 (3%) 22 (2%) 2 (0%) 9 (1%) Encryption Module 4 (0%) 5 (0%) 0 (0%) 6 (0%) Other 5 (1%) 16 (2%) 27 (2%) 5 (0%) 31 -
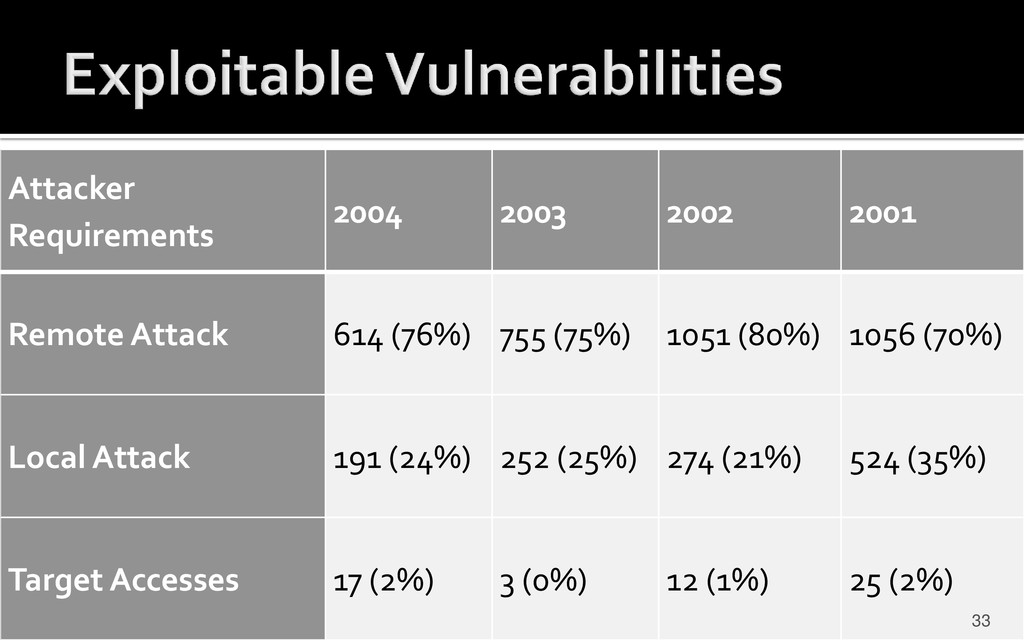
Attacker Requirements 2004 2003 2002 2001 Remote Attack 614 (76%)
755 (75%) 1051 (80%) 1056 (70%) Local Attack 191 (24%) 252 (25%) 274 (21%) 524 (35%) Target Accesses 17 (2%) 3 (0%) 12 (1%) 25 (2%) 33 -
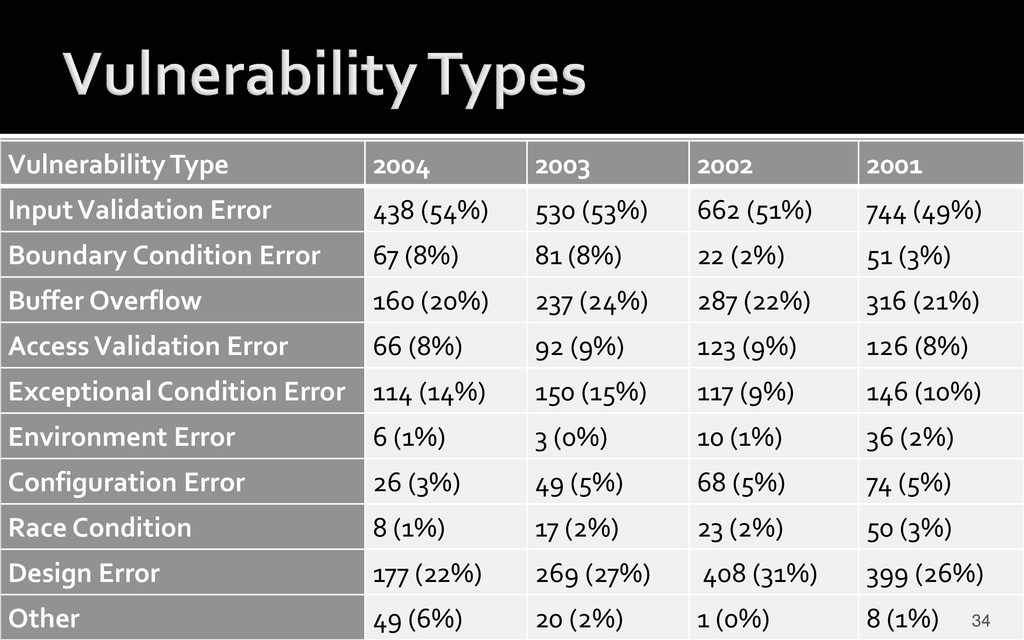
Vulnerability Type 2004 2003 2002 2001 Input Validation Error 438
(54%) 530 (53%) 662 (51%) 744 (49%) Boundary Condition Error 67 (8%) 81 (8%) 22 (2%) 51 (3%) Buffer Overflow 160 (20%) 237 (24%) 287 (22%) 316 (21%) Access Validation Error 66 (8%) 92 (9%) 123 (9%) 126 (8%) Exceptional Condition Error 114 (14%) 150 (15%) 117 (9%) 146 (10%) Environment Error 6 (1%) 3 (0%) 10 (1%) 36 (2%) Configuration Error 26 (3%) 49 (5%) 68 (5%) 74 (5%) Race Condition 8 (1%) 17 (2%) 23 (2%) 50 (3%) Design Error 177 (22%) 269 (27%) 408 (31%) 399 (26%) Other 49 (6%) 20 (2%) 1 (0%) 8 (1%) 34 -
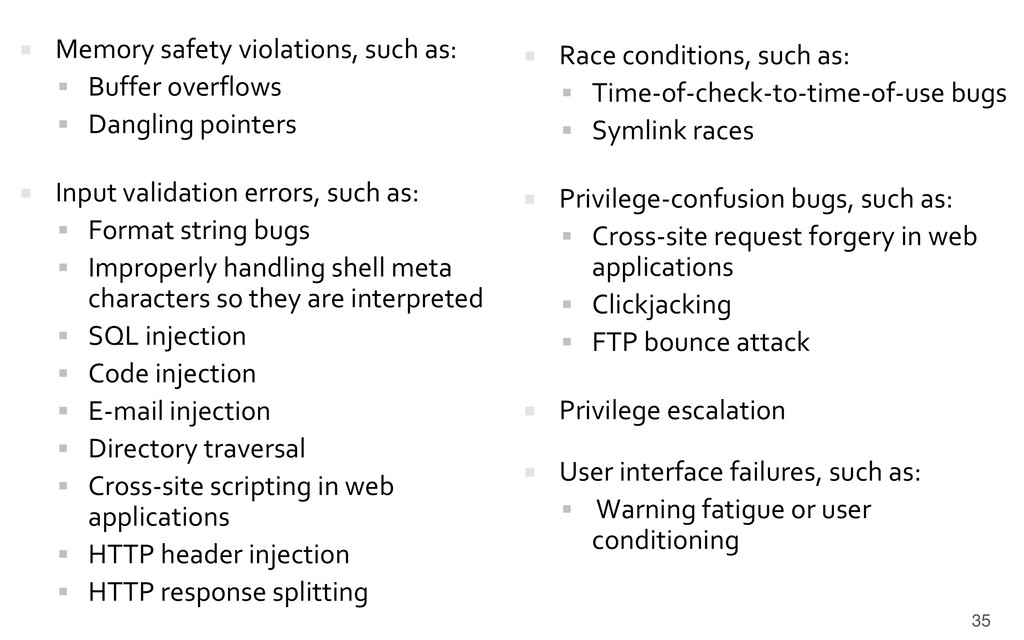
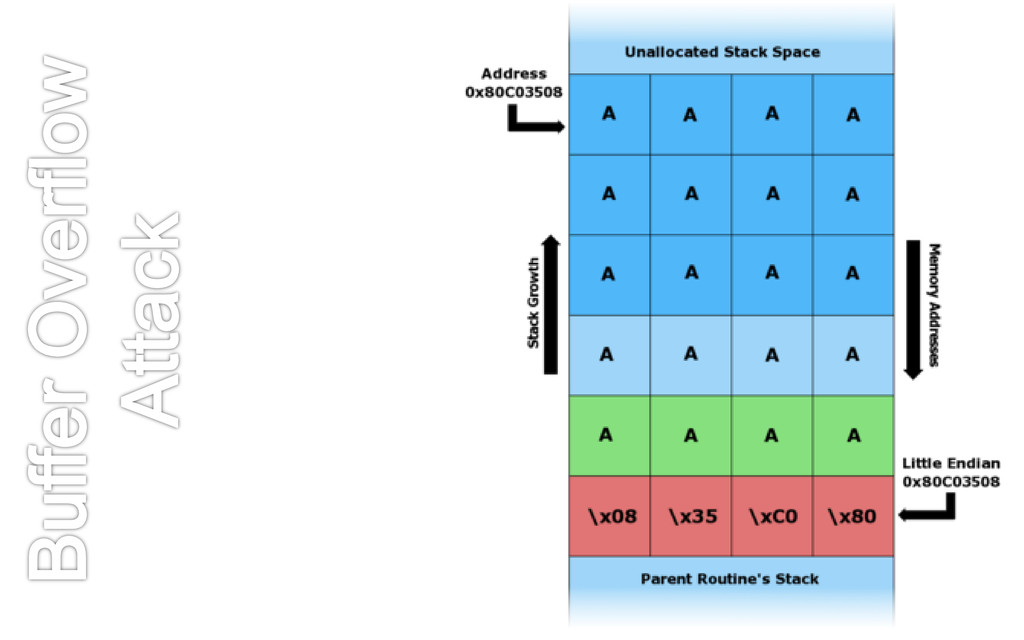
35 Memory safety violations, such as: Buffer overflows
Dangling pointers Input validation errors, such as: Format string bugs Improperly handling shell meta characters so they are interpreted SQL injection Code injection E-mail injection Directory traversal Cross-site scripting in web applications HTTP header injection HTTP response splitting Race conditions, such as: Time-of-check-to-time-of-use bugs Symlink races Privilege-confusion bugs, such as: Cross-site request forgery in web applications Clickjacking FTP bounce attack Privilege escalation User interface failures, such as: Warning fatigue or user conditioning -
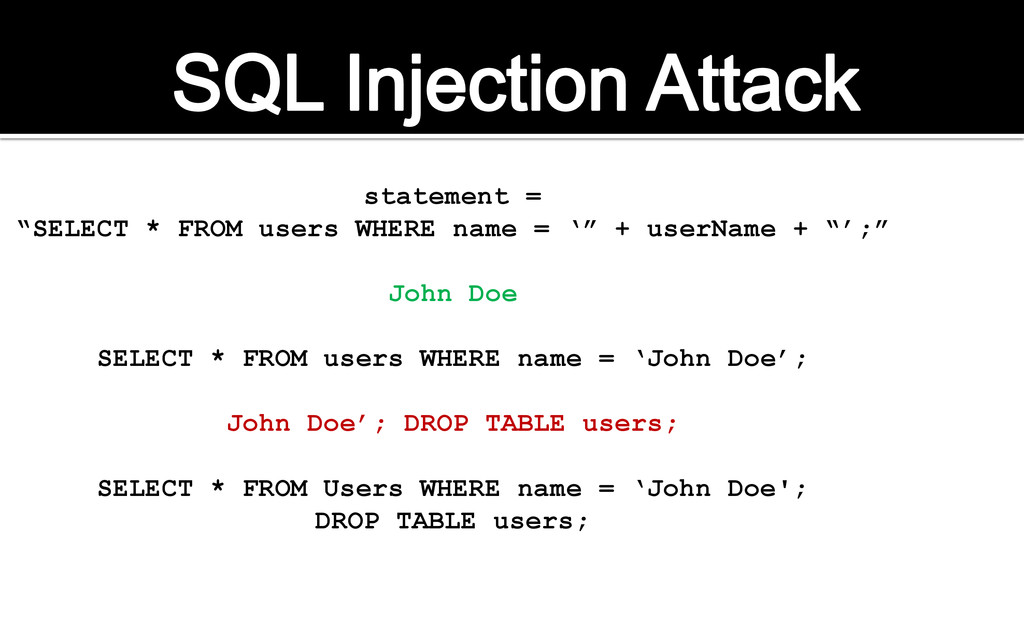
statement = “SELECT * FROM users WHERE name = „”
+ userName + “‟;” John Doe SELECT * FROM users WHERE name = „John Doe‟; John Doe‟; DROP TABLE users; SELECT * FROM Users WHERE name = „John Doe'; DROP TABLE users; -
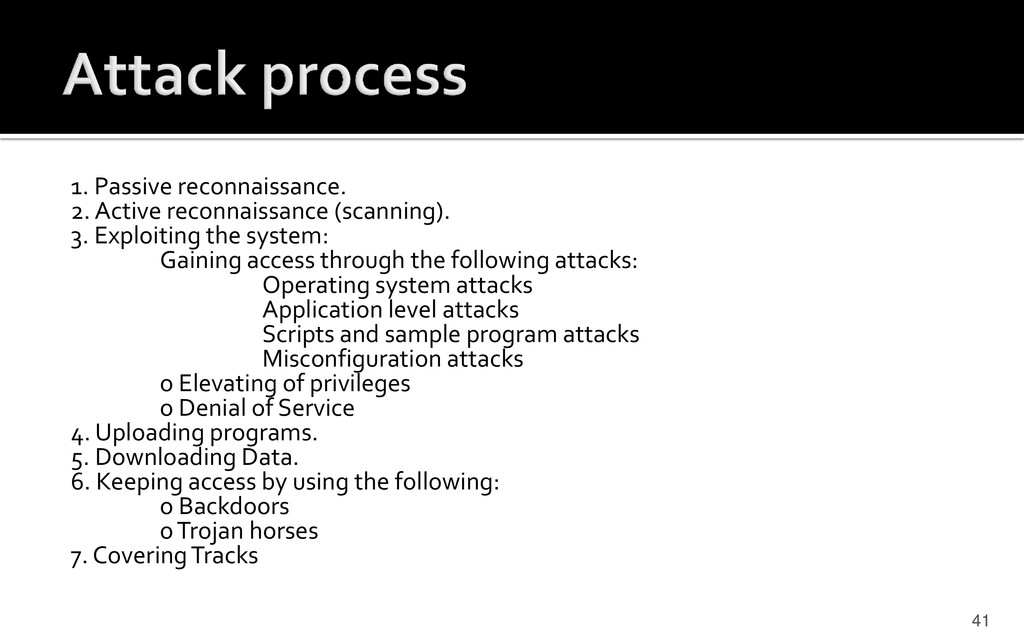
1. Passive reconnaissance. 2. Active reconnaissance (scanning). 3. Exploiting the
system: Gaining access through the following attacks: Operating system attacks Application level attacks Scripts and sample program attacks Misconfiguration attacks o Elevating of privileges o Denial of Service 4. Uploading programs. 5. Downloading Data. 6. Keeping access by using the following: o Backdoors o Trojan horses 7. Covering Tracks 41 -
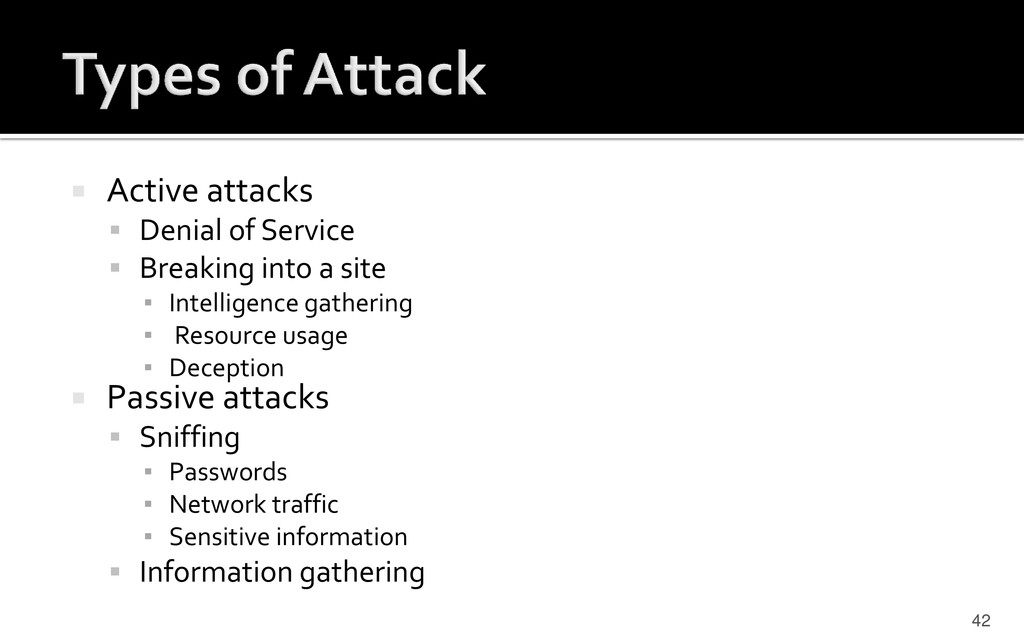
Active attacks Denial of Service Breaking into
a site ▪ Intelligence gathering ▪ Resource usage ▪ Deception Passive attacks Sniffing ▪ Passwords ▪ Network traffic ▪ Sensitive information Information gathering 42 -
Log files File information Additional files
Network traffic 43 -
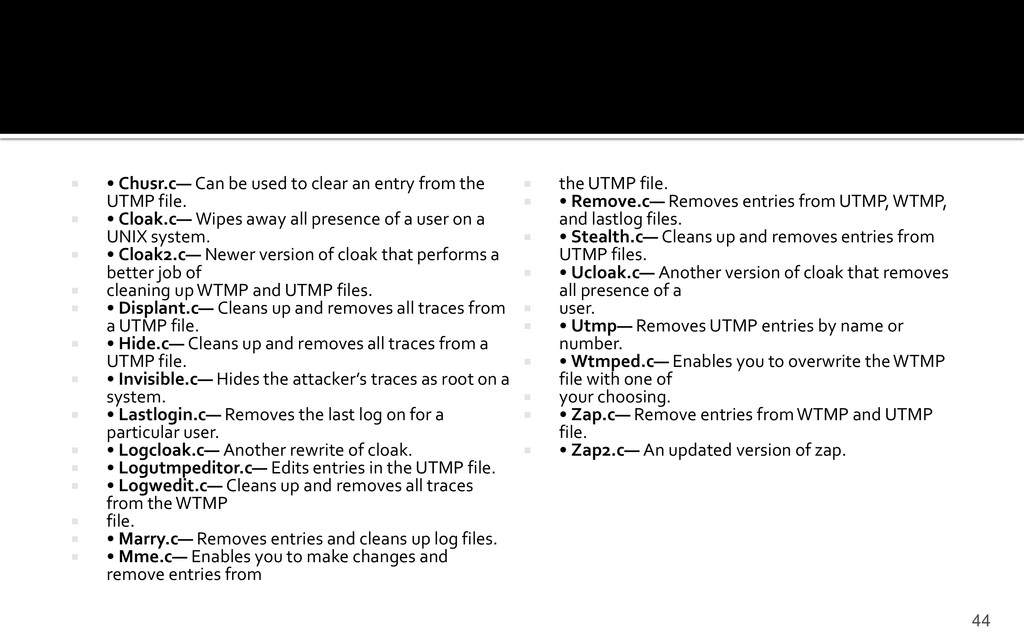
• Chusr.c— Can be used to clear an entry
from the UTMP file. • Cloak.c— Wipes away all presence of a user on a UNIX system. • Cloak2.c— Newer version of cloak that performs a better job of cleaning up WTMP and UTMP files. • Displant.c— Cleans up and removes all traces from a UTMP file. • Hide.c— Cleans up and removes all traces from a UTMP file. • Invisible.c— Hides the attacker’s traces as root on a system. • Lastlogin.c— Removes the last log on for a particular user. • Logcloak.c— Another rewrite of cloak. • Logutmpeditor.c— Edits entries in the UTMP file. • Logwedit.c— Cleans up and removes all traces from the WTMP file. • Marry.c— Removes entries and cleans up log files. • Mme.c— Enables you to make changes and remove entries from the UTMP file. • Remove.c— Removes entries from UTMP, WTMP, and lastlog files. • Stealth.c— Cleans up and removes entries from UTMP files. • Ucloak.c— Another version of cloak that removes all presence of a user. • Utmp— Removes UTMP entries by name or number. • Wtmped.c— Enables you to overwrite the WTMP file with one of your choosing. • Zap.c— Remove entries from WTMP and UTMP file. • Zap2.c— An updated version of zap. 44 -
Operating System Network Protocol Stack Non-Server Application Server Application Hardware
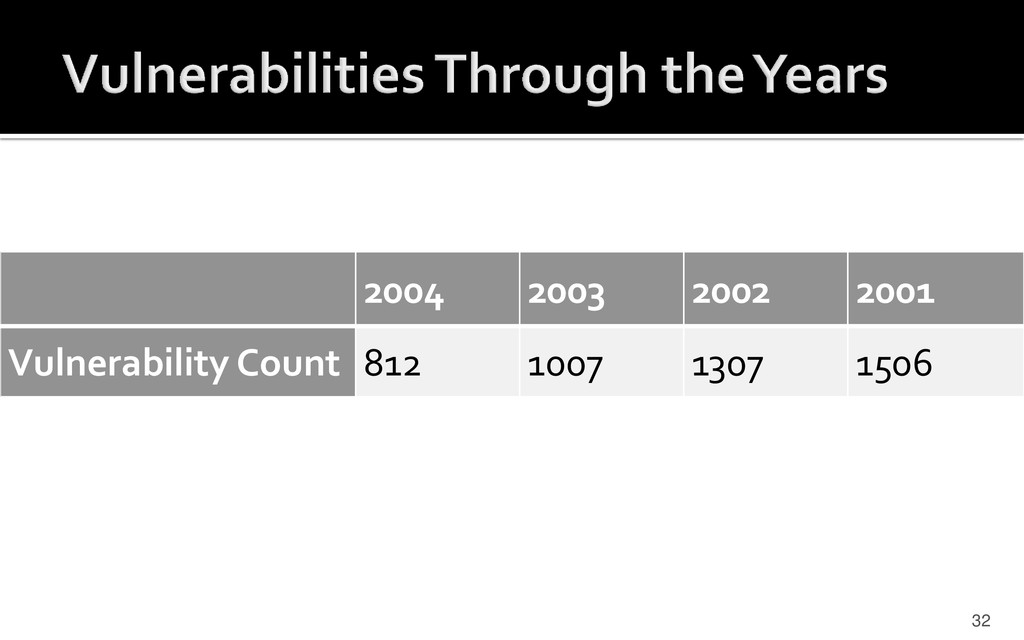
Communicati on Protocol Encryption Module Other 2001 248 8 309 886 43 9 6 5 2002 213 18 267 771 54 2 0 27 2003 163 6 384 440 27 22 5 16 2004 124 6 364 324 14 28 4 5 0 100 200 300 400 500 600 700 800 900 1000 -
Server is: - Host offering services Application,
Authentication, etc -
Knowledge of threat levels gives head start ID
all reducible threats Data, Resources are potential targets due to bugs Bugs become exploits Assessment, mitigation aid understanding shield strength Assumption: - Network servers in an enterprise -
Plan the installation and deployment of the operating system
and other components for the server Install, configure, and secure the underlying operating system as well as the server software For web servers, database servers, and directory servers which host content, ensure that the content is properly secured. -
Planning, Installation & Deployment Cautious Planning, more security
Deficient Planning management controls Fixing security later won’t help ▪ Cumbersome, expensive Detailed Plan should be made and followed Suspicious behavior, deviation from the plan. -
Parameters considered Purpose, Information categories, security requirements, retrieval
Privileges, management, user authentication, protection of data Enforced appropriate access to Information Application meets requirements Vulnerability history, functionality -
Application chooses OS OS restrict activities to authorized
users Data access control Disable unnecessary services Public facing Sensitive Secure environment, physical security -
Post Planning Patching Hardening ▪ Remove disable
unwanted services ▪ User Authentication configuration ▪ Configure server resource requirements Configure Additional Security -
Periodic testing, help ID breaches, measure effectiveness present security
Vulnerability scanning, penetration testing Test identically configured test server Possibility for inconsistencies -
Read, Understand the Software Documentation, see options coming with
software Check vulnerabilities and related patches Never place partially patched server on the Network Such a server will be compromised easily -
Very similar OS installation Install only required services
Anything not necessary should be removed First install software on a dedicated host/guest OS Apply patches and upgrades Create separate partition for server data Remove unnecessary service and unwanted default accounts -
OS provides option to set access rights for files,
resources, devices Distribute access rights to users Sever software has the same option Set Identical permissions for both OS and server software Optimal Access controls Limit server applications access to resources Limit user access through additional controls -
Proper access controls help protect sensitive data. Limit
resource usage Ensure integrity of server logs Distinctive files need access control ▪ Logs, audit files, security mechanisms Individual User or User Groups Identity, restricted access OS should Limit file access by server software processes Enforce service processes, run as user, write to sever content whenever required. -
Sever software uses minimum OS resources Install sever
software different partition Scan upload files before the server reads Limit size of Upload files Store logging information logging server Store locally if feasible Connection timeout configuration -
Additional Authentication and Encryption Maintaining server security
Maintain a test server -
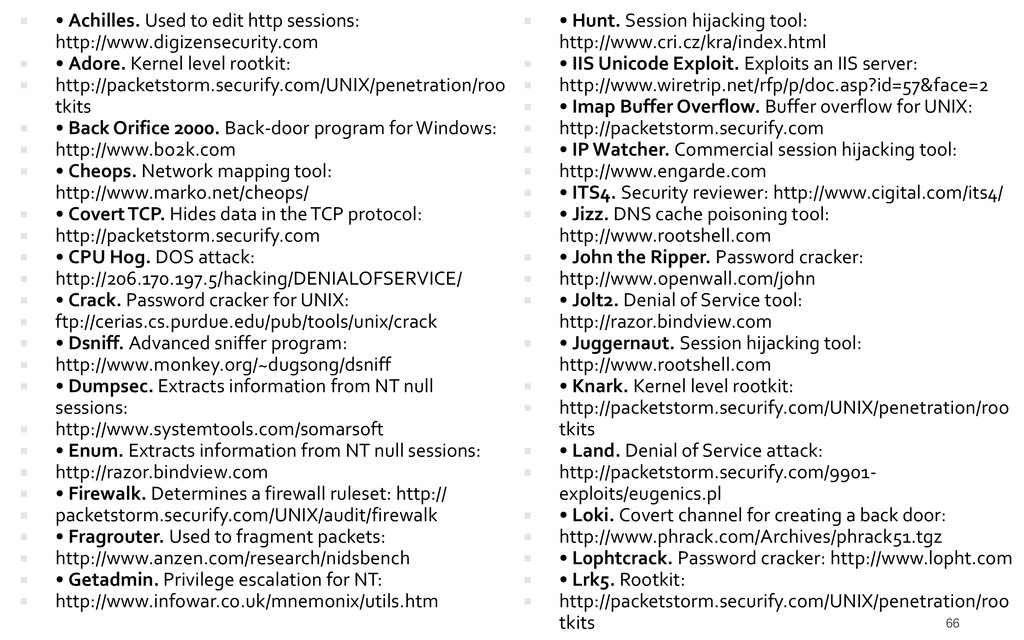
66 • Achilles. Used to edit http sessions: http://www.digizensecurity.com
• Adore. Kernel level rootkit: http://packetstorm.securify.com/UNIX/penetration/roo tkits • Back Orifice 2000. Back-door program for Windows: http://www.bo2k.com • Cheops. Network mapping tool: http://www.marko.net/cheops/ • Covert TCP. Hides data in the TCP protocol: http://packetstorm.securify.com • CPU Hog. DOS attack: http://206.170.197.5/hacking/DENIALOFSERVICE/ • Crack. Password cracker for UNIX: ftp://cerias.cs.purdue.edu/pub/tools/unix/crack • Dsniff. Advanced sniffer program: http://www.monkey.org/~dugsong/dsniff • Dumpsec. Extracts information from NT null sessions: http://www.systemtools.com/somarsoft • Enum. Extracts information from NT null sessions: http://razor.bindview.com • Firewalk. Determines a firewall ruleset: http:// packetstorm.securify.com/UNIX/audit/firewalk • Fragrouter. Used to fragment packets: http://www.anzen.com/research/nidsbench • Getadmin. Privilege escalation for NT: http://www.infowar.co.uk/mnemonix/utils.htm • Hunt. Session hijacking tool: http://www.cri.cz/kra/index.html • IIS Unicode Exploit. Exploits an IIS server: http://www.wiretrip.net/rfp/p/doc.asp?id=57&face=2 • Imap Buffer Overflow. Buffer overflow for UNIX: http://packetstorm.securify.com • IP Watcher. Commercial session hijacking tool: http://www.engarde.com • ITS4. Security reviewer: http://www.cigital.com/its4/ • Jizz. DNS cache poisoning tool: http://www.rootshell.com • John the Ripper. Password cracker: http://www.openwall.com/john • Jolt2. Denial of Service tool: http://razor.bindview.com • Juggernaut. Session hijacking tool: http://www.rootshell.com • Knark. Kernel level rootkit: http://packetstorm.securify.com/UNIX/penetration/roo tkits • Land. Denial of Service attack: http://packetstorm.securify.com/9901- exploits/eugenics.pl • Loki. Covert channel for creating a back door: http://www.phrack.com/Archives/phrack51.tgz • L0phtcrack. Password cracker: http://www.l0pht.com • Lrk5. Rootkit: http://packetstorm.securify.com/UNIX/penetration/roo tkits -
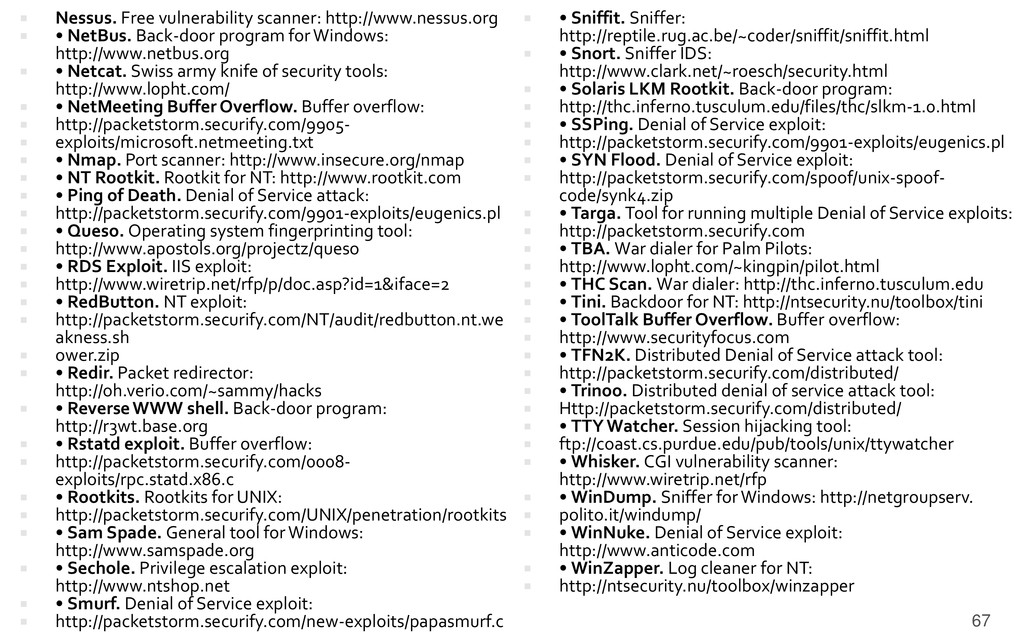
67 Nessus. Free vulnerability scanner: http://www.nessus.org • NetBus.
Back-door program for Windows: http://www.netbus.org • Netcat. Swiss army knife of security tools: http://www.l0pht.com/ • NetMeeting Buffer Overflow. Buffer overflow: http://packetstorm.securify.com/9905- exploits/microsoft.netmeeting.txt • Nmap. Port scanner: http://www.insecure.org/nmap • NT Rootkit. Rootkit for NT: http://www.rootkit.com • Ping of Death. Denial of Service attack: http://packetstorm.securify.com/9901-exploits/eugenics.pl • Queso. Operating system fingerprinting tool: http://www.apostols.org/projectz/queso • RDS Exploit. IIS exploit: http://www.wiretrip.net/rfp/p/doc.asp?id=1&iface=2 • RedButton. NT exploit: http://packetstorm.securify.com/NT/audit/redbutton.nt.we akness.sh ower.zip • Redir. Packet redirector: http://oh.verio.com/~sammy/hacks • Reverse WWW shell. Back-door program: http://r3wt.base.org • Rstatd exploit. Buffer overflow: http://packetstorm.securify.com/0008- exploits/rpc.statd.x86.c • Rootkits. Rootkits for UNIX: http://packetstorm.securify.com/UNIX/penetration/rootkits • Sam Spade. General tool for Windows: http://www.samspade.org • Sechole. Privilege escalation exploit: http://www.ntshop.net • Smurf. Denial of Service exploit: http://packetstorm.securify.com/new-exploits/papasmurf.c • Sniffit. Sniffer: http://reptile.rug.ac.be/~coder/sniffit/sniffit.html • Snort. Sniffer IDS: http://www.clark.net/~roesch/security.html • Solaris LKM Rootkit. Back-door program: http://thc.inferno.tusculum.edu/files/thc/slkm-1.0.html • SSPing. Denial of Service exploit: http://packetstorm.securify.com/9901-exploits/eugenics.pl • SYN Flood. Denial of Service exploit: http://packetstorm.securify.com/spoof/unix-spoof- code/synk4.zip • Targa. Tool for running multiple Denial of Service exploits: http://packetstorm.securify.com • TBA. War dialer for Palm Pilots: http://www.l0pht.com/~kingpin/pilot.html • THC Scan. War dialer: http://thc.inferno.tusculum.edu • Tini. Backdoor for NT: http://ntsecurity.nu/toolbox/tini • ToolTalk Buffer Overflow. Buffer overflow: http://www.securityfocus.com • TFN2K. Distributed Denial of Service attack tool: http://packetstorm.securify.com/distributed/ • Trinoo. Distributed denial of service attack tool: Http://packetstorm.securify.com/distributed/ • TTY Watcher. Session hijacking tool: ftp://coast.cs.purdue.edu/pub/tools/unix/ttywatcher • Whisker. CGI vulnerability scanner: http://www.wiretrip.net/rfp • WinDump. Sniffer for Windows: http://netgroupserv. polito.it/windump/ • WinNuke. Denial of Service exploit: http://www.anticode.com • WinZapper. Log cleaner for NT: http://ntsecurity.nu/toolbox/winzapper
 vg
 ydah
 oidfj
 nealle
 tsukuboshi
 nejumi
 imuta
 takuyay0ne
 csswizardry
 keitah
 sansantech
 sue445
 gokken
 asonas
 marcoroth
 kimpetersen
 kevinliebholz
 stephaniewalter
 ks91
 rkaga
 maggiecrowley
 inesmontani
 speakerdeck