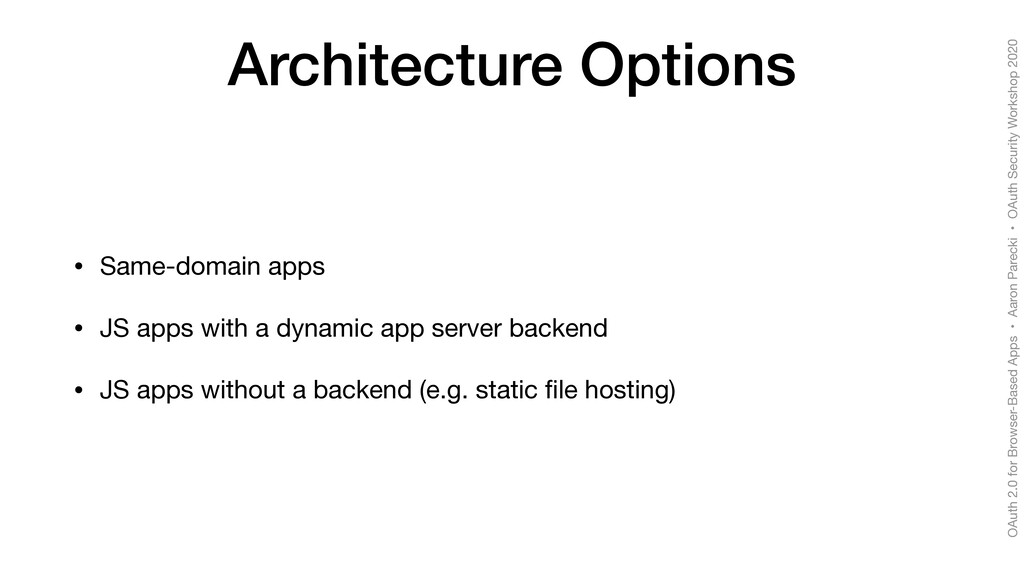
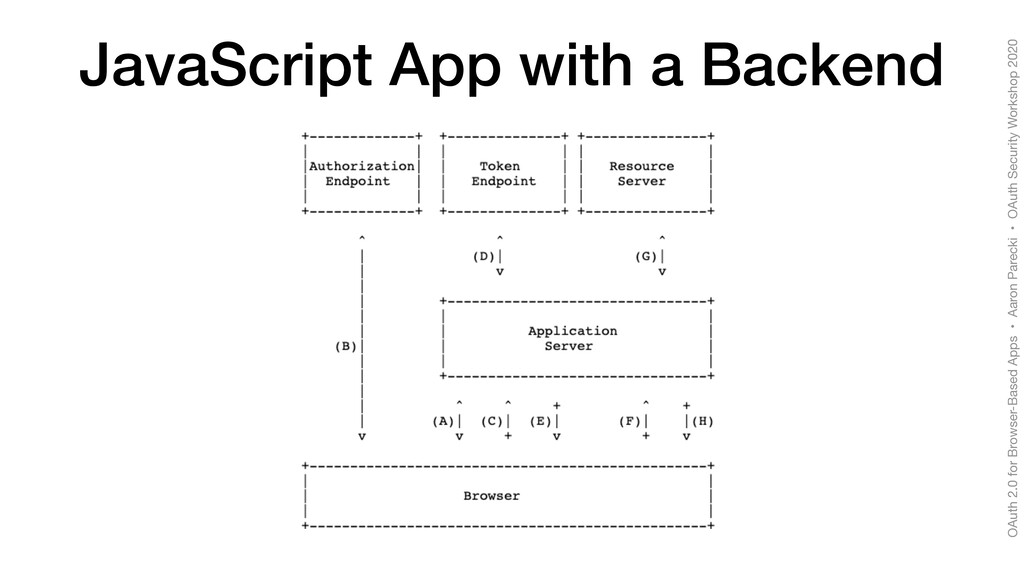
Security Workshop 2020 OAuth 2.0 for Browser-Based Apps • Includes recommendations for implementors building browser-based apps using OAuth 2.0 • "Browser-based apps" are defined as applications running in a browser, aka "SPA" or "single-page apps"
Security Workshop 2020 Recommendations • MUST NOT return access tokens in the front channel (e.g. no Implicit flow) • MUST use only exact registered redirect URIs • The AS MUST require an exact match of the redirect URI • The AS MUST issue one-time-use refresh tokens • The AS MUST either set a max lifetime on refresh tokens or expire if they are not used after some time
Security Workshop 2020 Same-Domain Applications • Details of this section still TBD • There are still benefits of OAuth such as easier MFA, avoiding passwords in apps, etc • Thoughts and opinions welcome
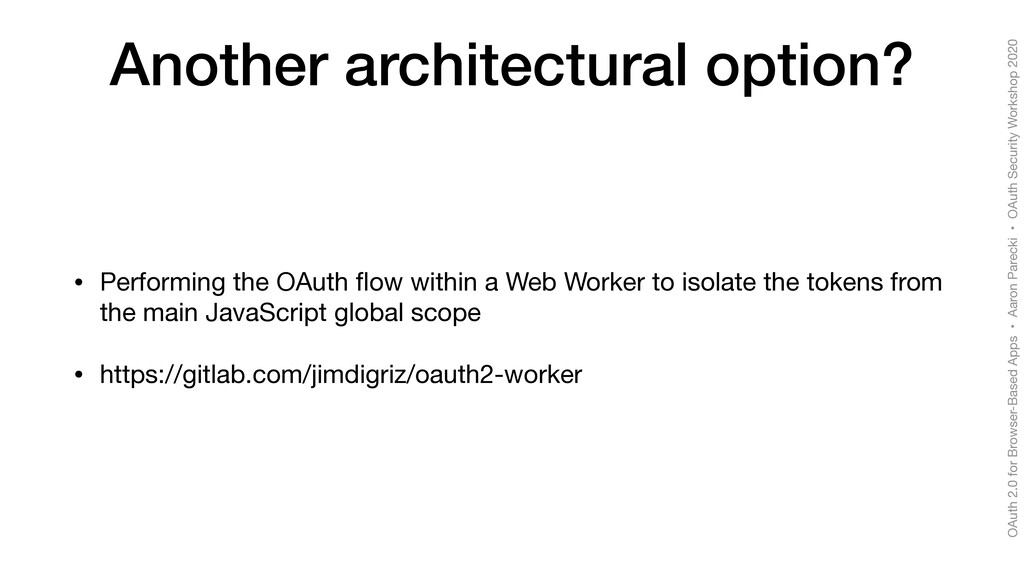
Security Workshop 2020 Another architectural option? • Performing the OAuth flow within a Web Worker to isolate the tokens from the main JavaScript global scope • https://gitlab.com/jimdigriz/oauth2-worker
Security Workshop 2020 Outstanding Work • Collect feedback on the architectural recommendations from people who have deployment experience • Remove details and reference sections that duplicate the Security BCP


 aaronpk
 demaecan
 oidfj
 jacopen
 mikanichinose
 visional_engineering_and_design
 lycorptech_jp
 riyaamemiya
 takuyay0ne
 ryudai
 nejumi
 bengo4com
 jirtosterone
 brad_frost
 katarinadahlin
 addyosmani
 inesmontani
 nonsquared
 konakalab
 szymonslowik
 irinanazarova
 frankvandijk
 techseoconnect
 tenderlove
 aleyda