Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
雑に疎通確認だけしたい...せや!CloudShell使ったろ!
Search
Ryotaro Harada
May 10, 2025
Technology
1k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
雑に疎通確認だけしたい...せや!CloudShell使ったろ!
Ryotaro Harada
May 10, 2025
More Decks by Ryotaro Harada
See All by Ryotaro Harada
あるけみー式LTスライド作成術
alchemy1115
2
230
最高のシステムプロンプトを作るためにフィードバック機能を導入した話
alchemy1115
1
680
凡エンジニアがこの先生きのこるためには。〜TypeScript完全に理解したい〜
alchemy1115
2
480
30代、何を"諦める"か
alchemy1115
1
790
ADOTで始めるサーバレスアーキテクチャのオブザーバビリティ
alchemy1115
3
350
AgentCore RuntimeをVPCにデプロイして 開発ドキュメント作成AIエージェントを作った
alchemy1115
5
1.4k
バズる!アウトプット
alchemy1115
1
620
社外コミュニティと「学び」を考える
alchemy1115
2
250
AWS IoT CoreとRaspberry Piに触れてみた
alchemy1115
0
450
Other Decks in Technology
See All in Technology
作って終わりじゃないサーバーレス 〜9年運用する大規模EC物流API基盤の設計・運用のリアル〜
zozotech
PRO
0
460
AgentCore Runtime上にAgentic Coding基盤を構築・展開する際の設計ポイントと限界点 / Design considerations and limitations when building an agentic coding platform on AgentCore Runtime
har1101
5
690
データ_AIの事業の勝敗をわけるもの
nek0128
1
480
What the customer really needed
kawaguti
PRO
3
220
絵ではじめるKubernetesセキュリティ
aoi1
4
700
積み重なった技術負債への挑戦 〜初手としての全社ゴト化〜
techtekt
PRO
0
1.6k
AIによるクリエイティブ生成を行う上での試行錯誤
plaidtech
PRO
0
180
え、こんなに早く改修できるの?──新人エンジニアとスクラムマスターの2人が語る、AI×アジャイル開発の現場
ysasago
2
670
おい、エージェントを使って終わらせろ
nwiizo
3
870
2026-09-18 gotanda.sre Terraformで複数環境作ったり、複数Stateに分割したりそれとTerragrunt / Terraform multi envs and multi states
masasuzu
4
700
The Knowledge Spine: A Machine-Executable Ontology for Governed Marketing Activation
vananth22
0
120
Kiro Meetup #8 Kiro アップデート (2026/3/21〜2026/9/24)
katzueno
1
140
Featured
See All Featured
YesSQL, Process and Tooling at Scale
rocio
174
15k
Mind Mapping
helmedeiros
1
370
Done Done
chrislema
186
17k
Making Projects Easy
brettharned
120
6.8k
Getting science done with accelerated Python computing platforms
jacobtomlinson
2
480
Fashionably flexible responsive web design (full day workshop)
malarkey
409
67k
Lightning Talk: Beautiful Slides for Beginners
inesmontani
PRO
2
700
What does AI have to do with Human Rights?
axbom
PRO
1
2.4k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Paper Plane
katiecoart
PRO
4
53k
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
19k
Designing for Timeless Needs
cassininazir
1
480
Transcript
雑に疎通確認だけしたい...せや!CloudShell 使ったろ! 2025/5/10 JAWS-UG彩の国埼玉支部 #1 KDDI株式会社 原田涼太郎
自己紹介 名前: 原田 涼太郎@KDDI株式会社 ハンドルネーム: あるけみー 好きなAWSサービス: AWS Certificate Manager(ACM)、AmazonECS
最近は仕事と育児とコミュニティと 資格取得とハンター生活の両立を目指している
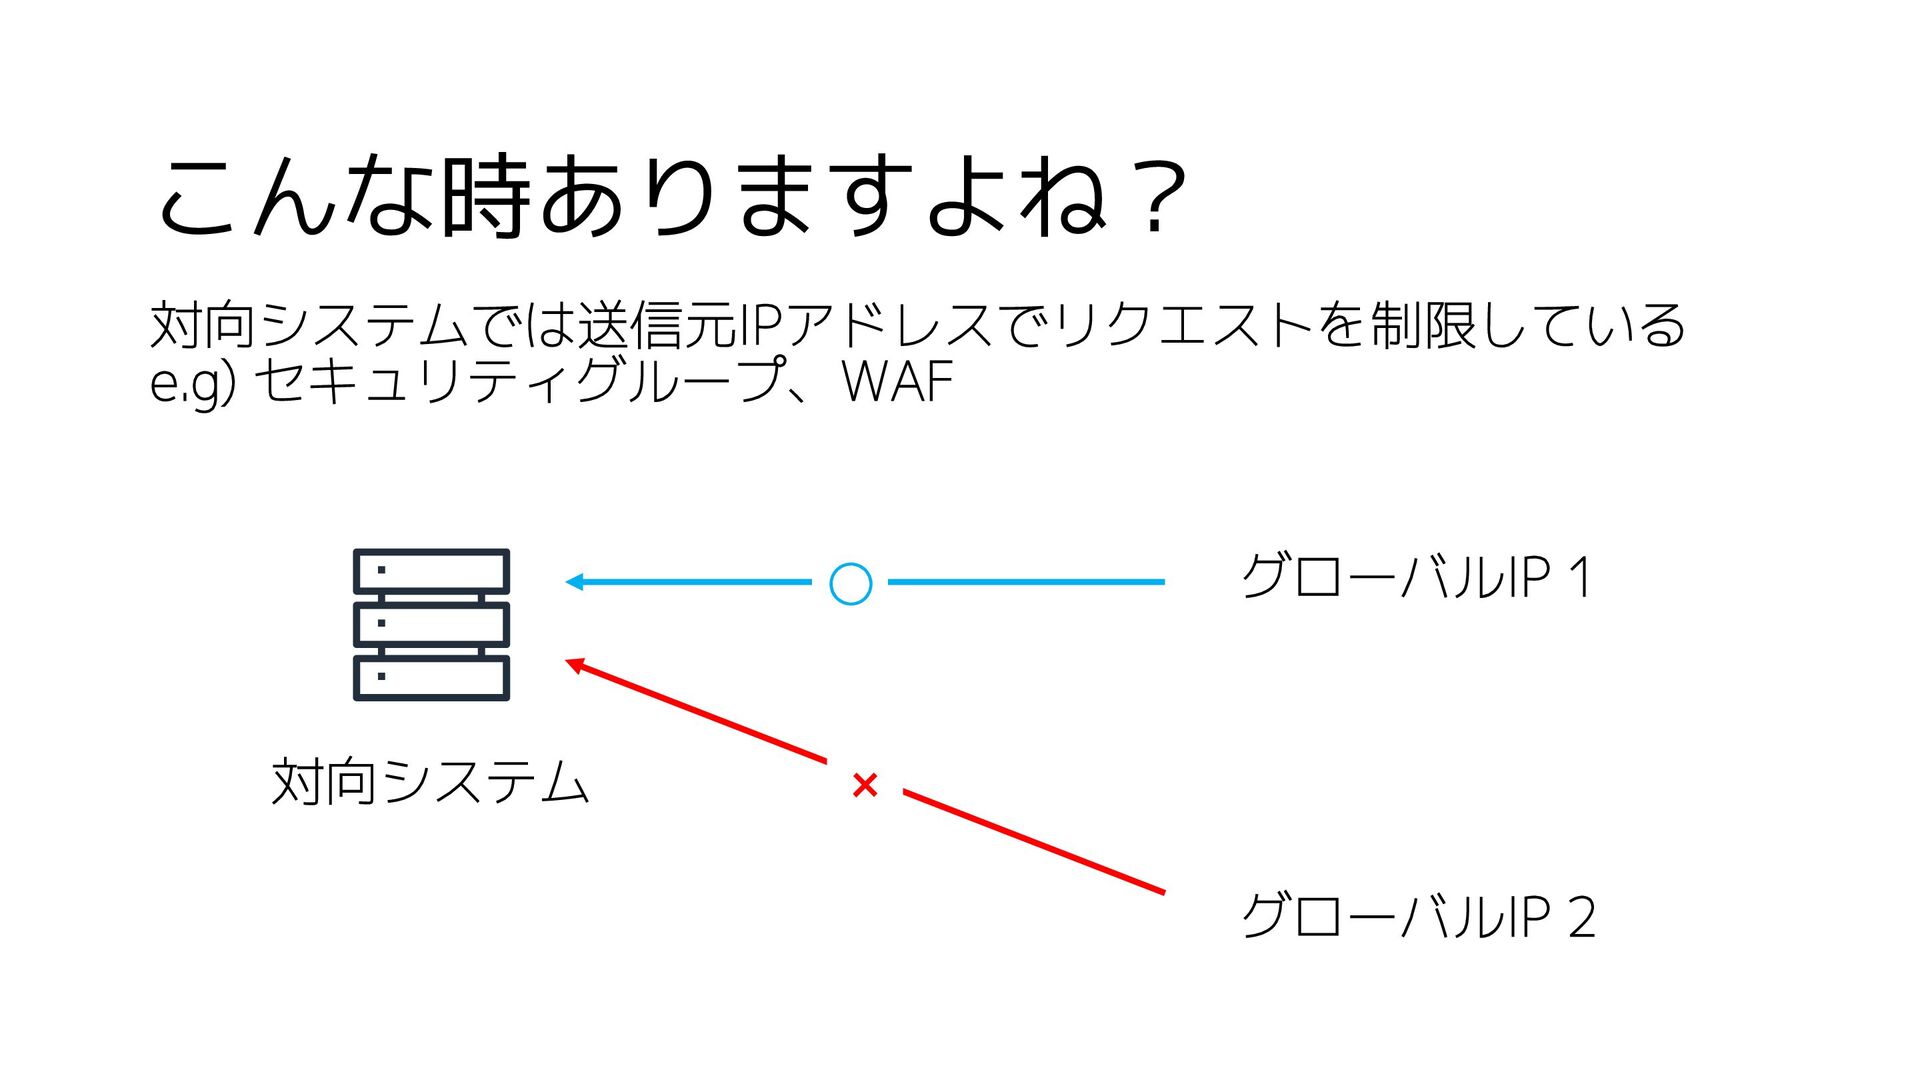
こんな時ありますよね? 対向システムでは送信元IPアドレスでリクエストを制限している e.g) セキュリティグループ、WAF 対向システム グローバルIP 1 ◯ × グローバルIP
2
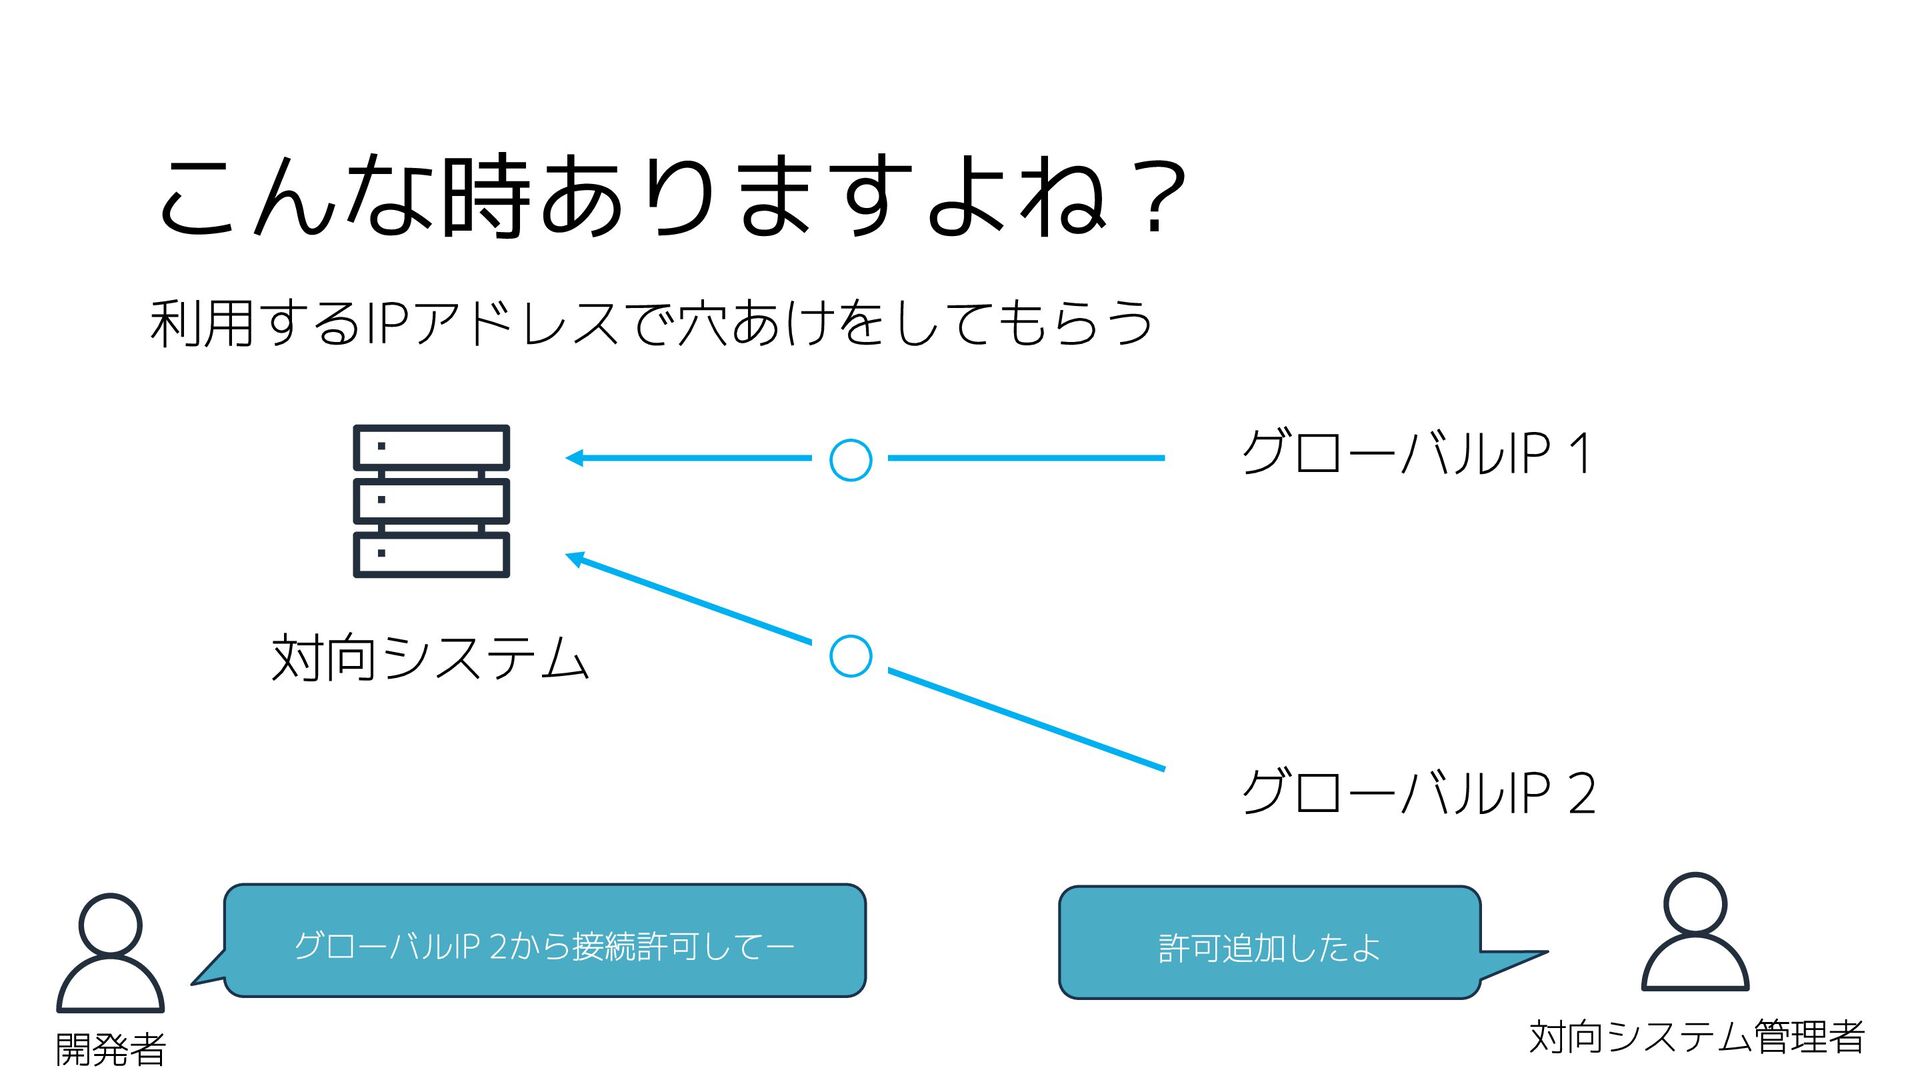
こんな時ありますよね? 利用するIPアドレスで穴あけをしてもらう 対向システム グローバルIP 1 ◯ グローバルIP 2 グローバルIP 2から接続許可してー
対向システム管理者 開発者 許可追加したよ ◯
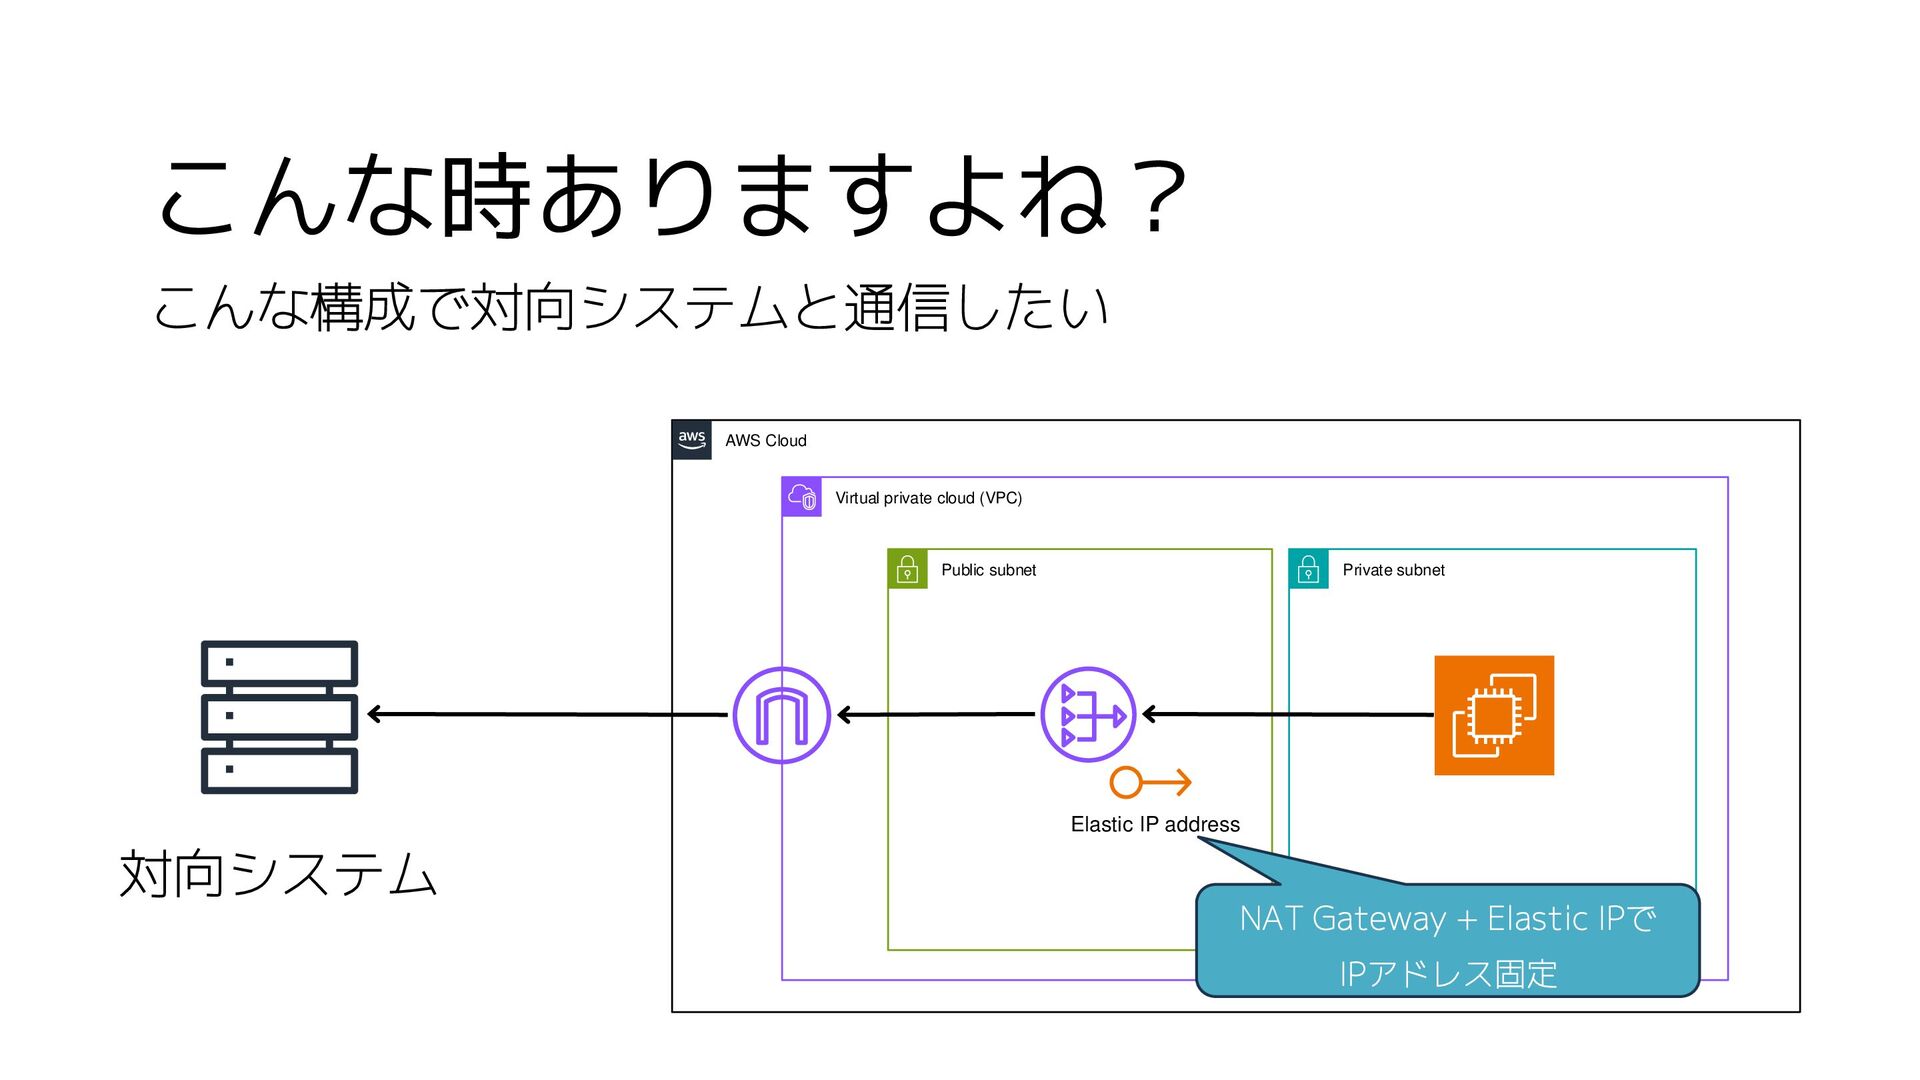
こんな時ありますよね? こんな構成で対向システムと通信したい 対向システム AWS Cloud Virtual private cloud (VPC) Public
subnet Private subnet Elastic IP address NAT Gateway + Elastic IPで IPアドレス固定
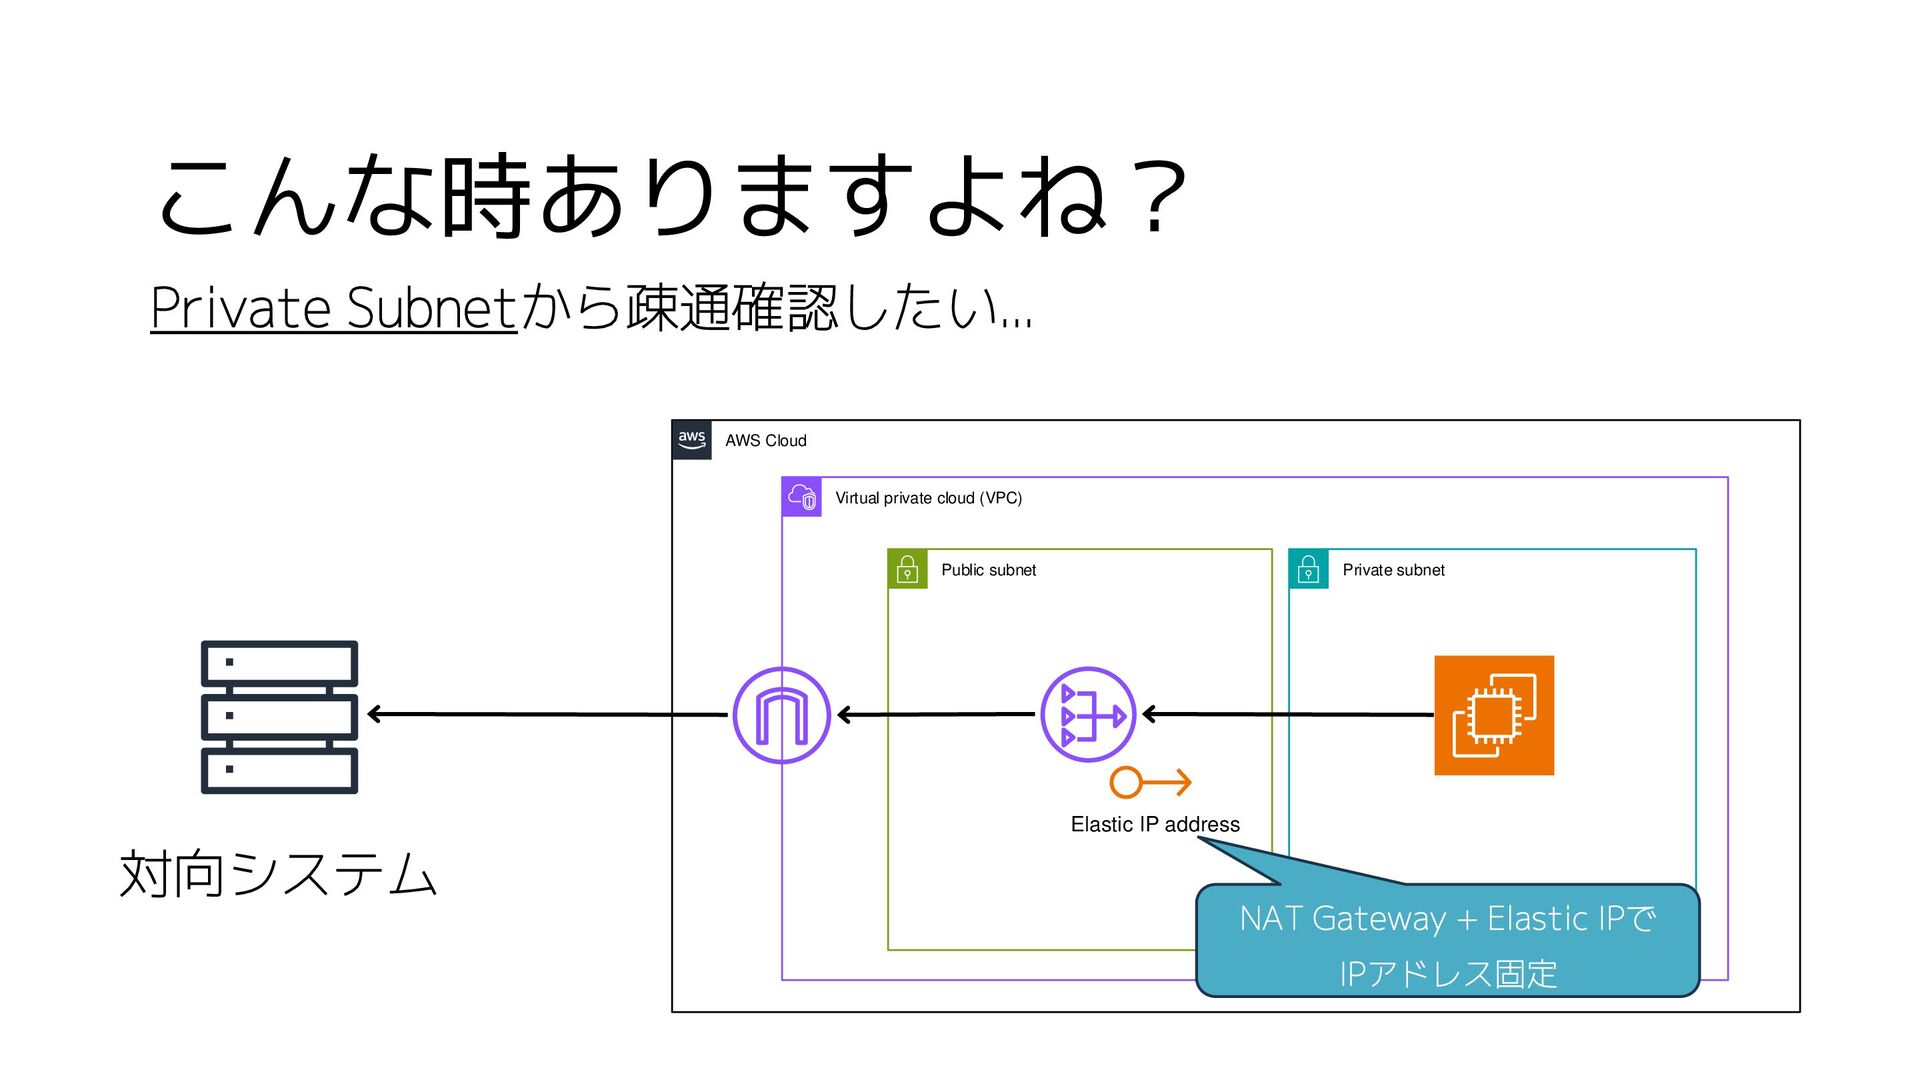
こんな時ありますよね? Private Subnetから疎通確認したい... 対向システム AWS Cloud Virtual private cloud (VPC)
Public subnet Private subnet Elastic IP address NAT Gateway + Elastic IPで IPアドレス固定
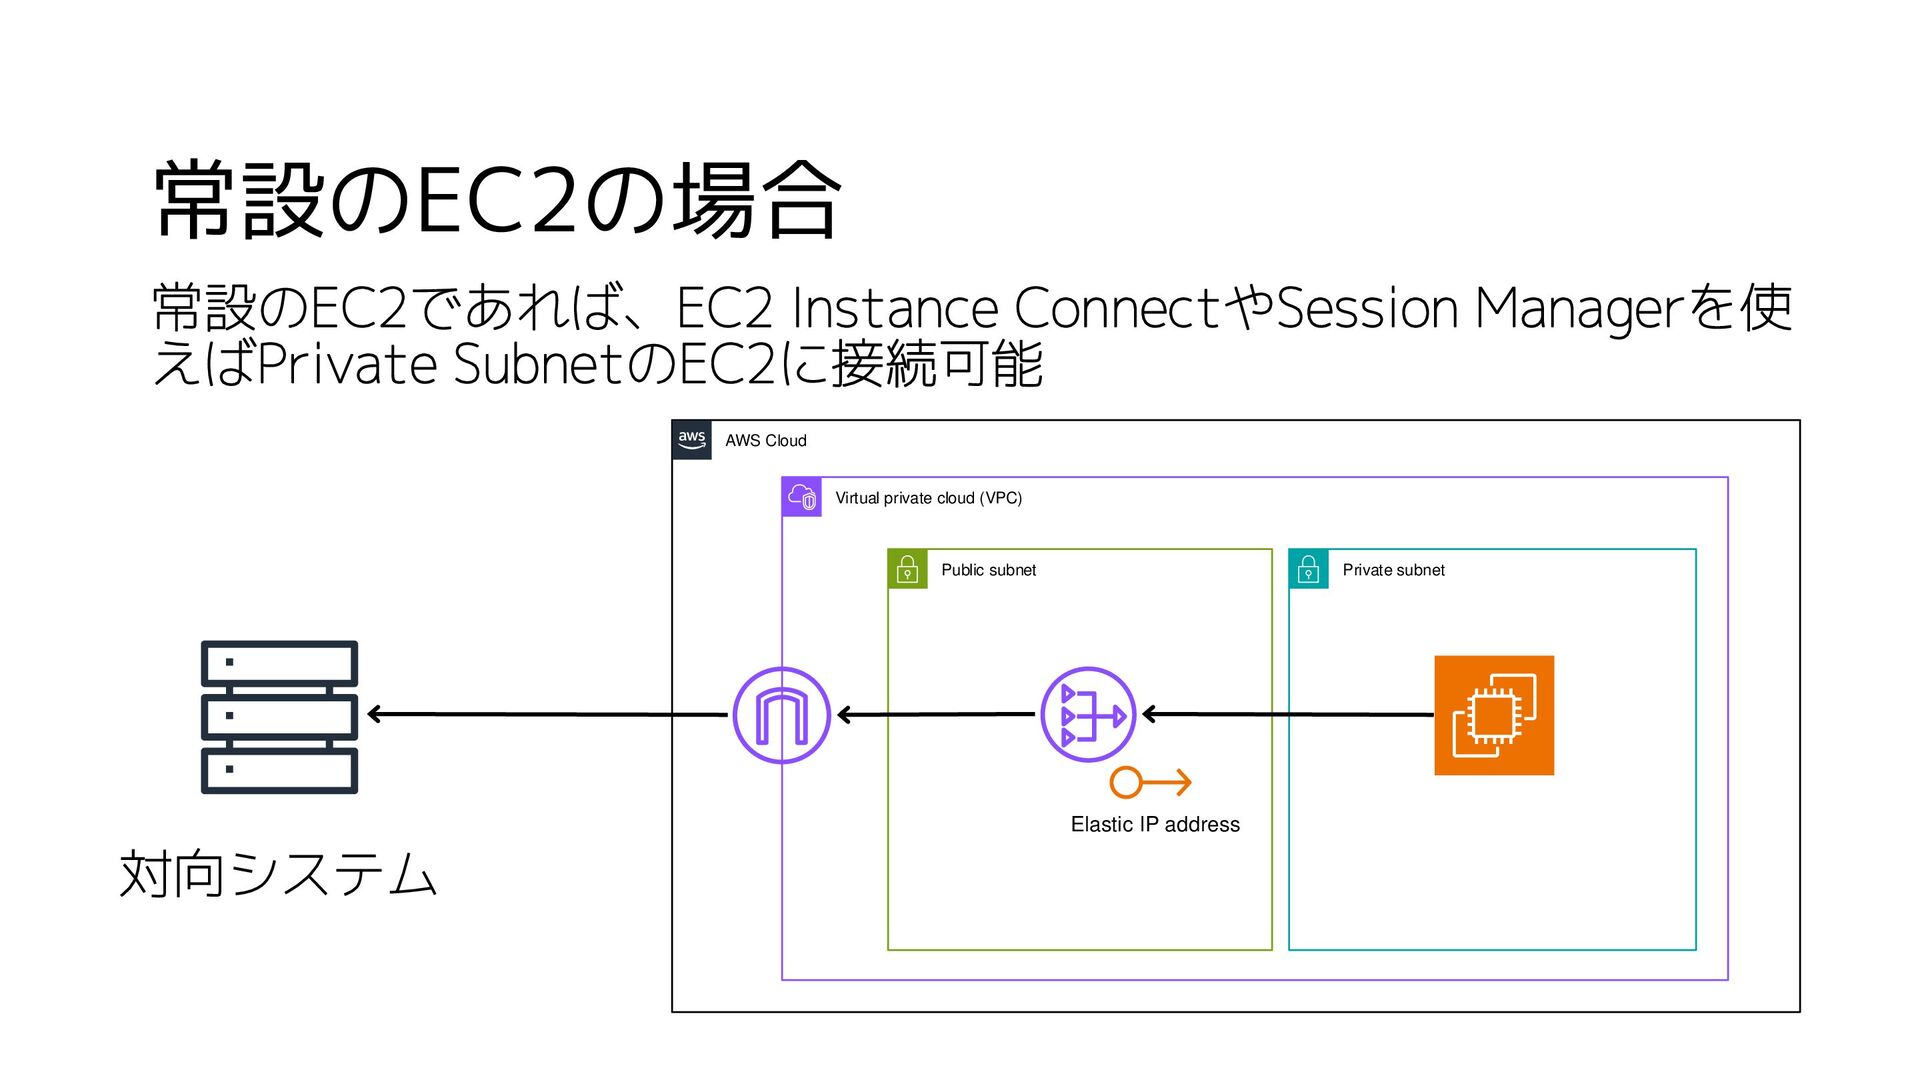
常設のEC2の場合 対向システム AWS Cloud Virtual private cloud (VPC) Public subnet
Private subnet Elastic IP address 常設のEC2であれば、EC2 Instance ConnectやSession Managerを使 えばPrivate SubnetのEC2に接続可能
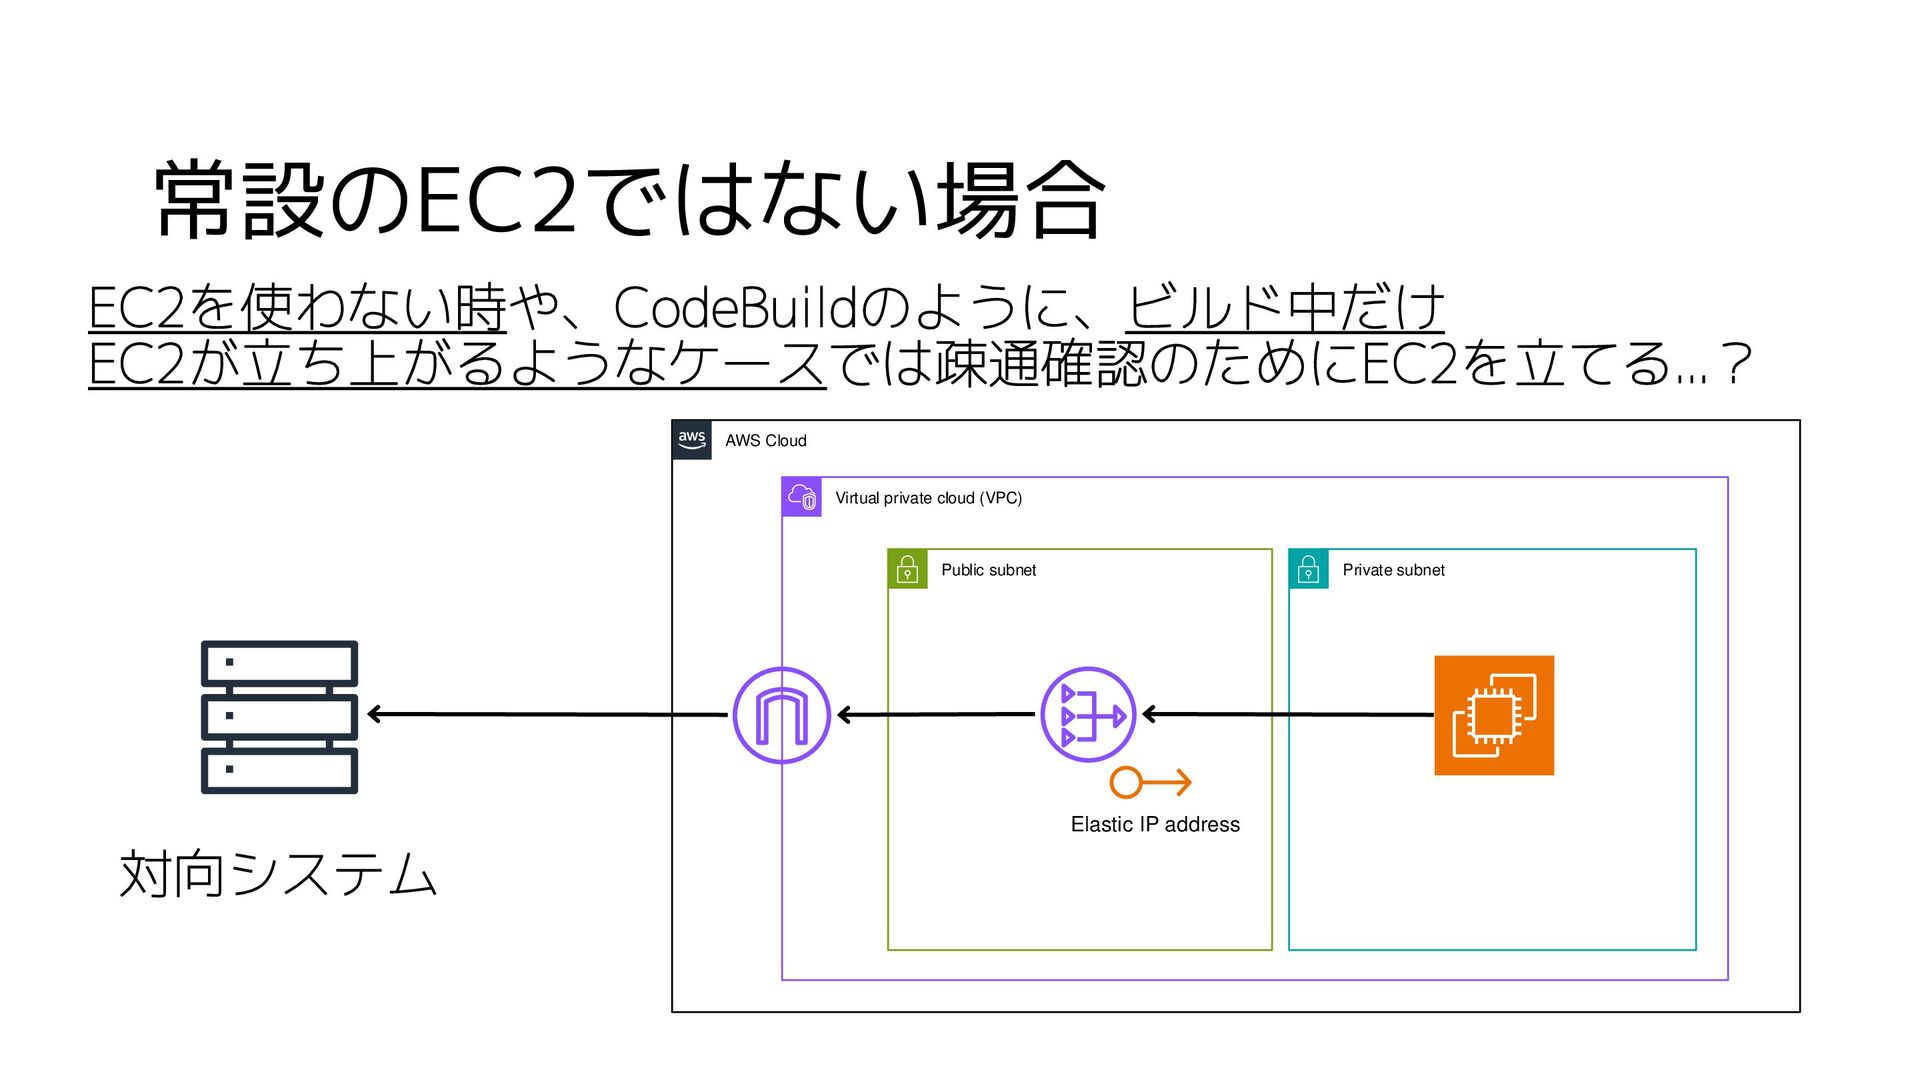
常設のEC2ではない場合 対向システム AWS Cloud Virtual private cloud (VPC) Public subnet
Private subnet Elastic IP address EC2を使わない時や、CodeBuildのように、ビルド中だけ EC2が立ち上がるようなケースでは疎通確認のためにEC2を立てる...?
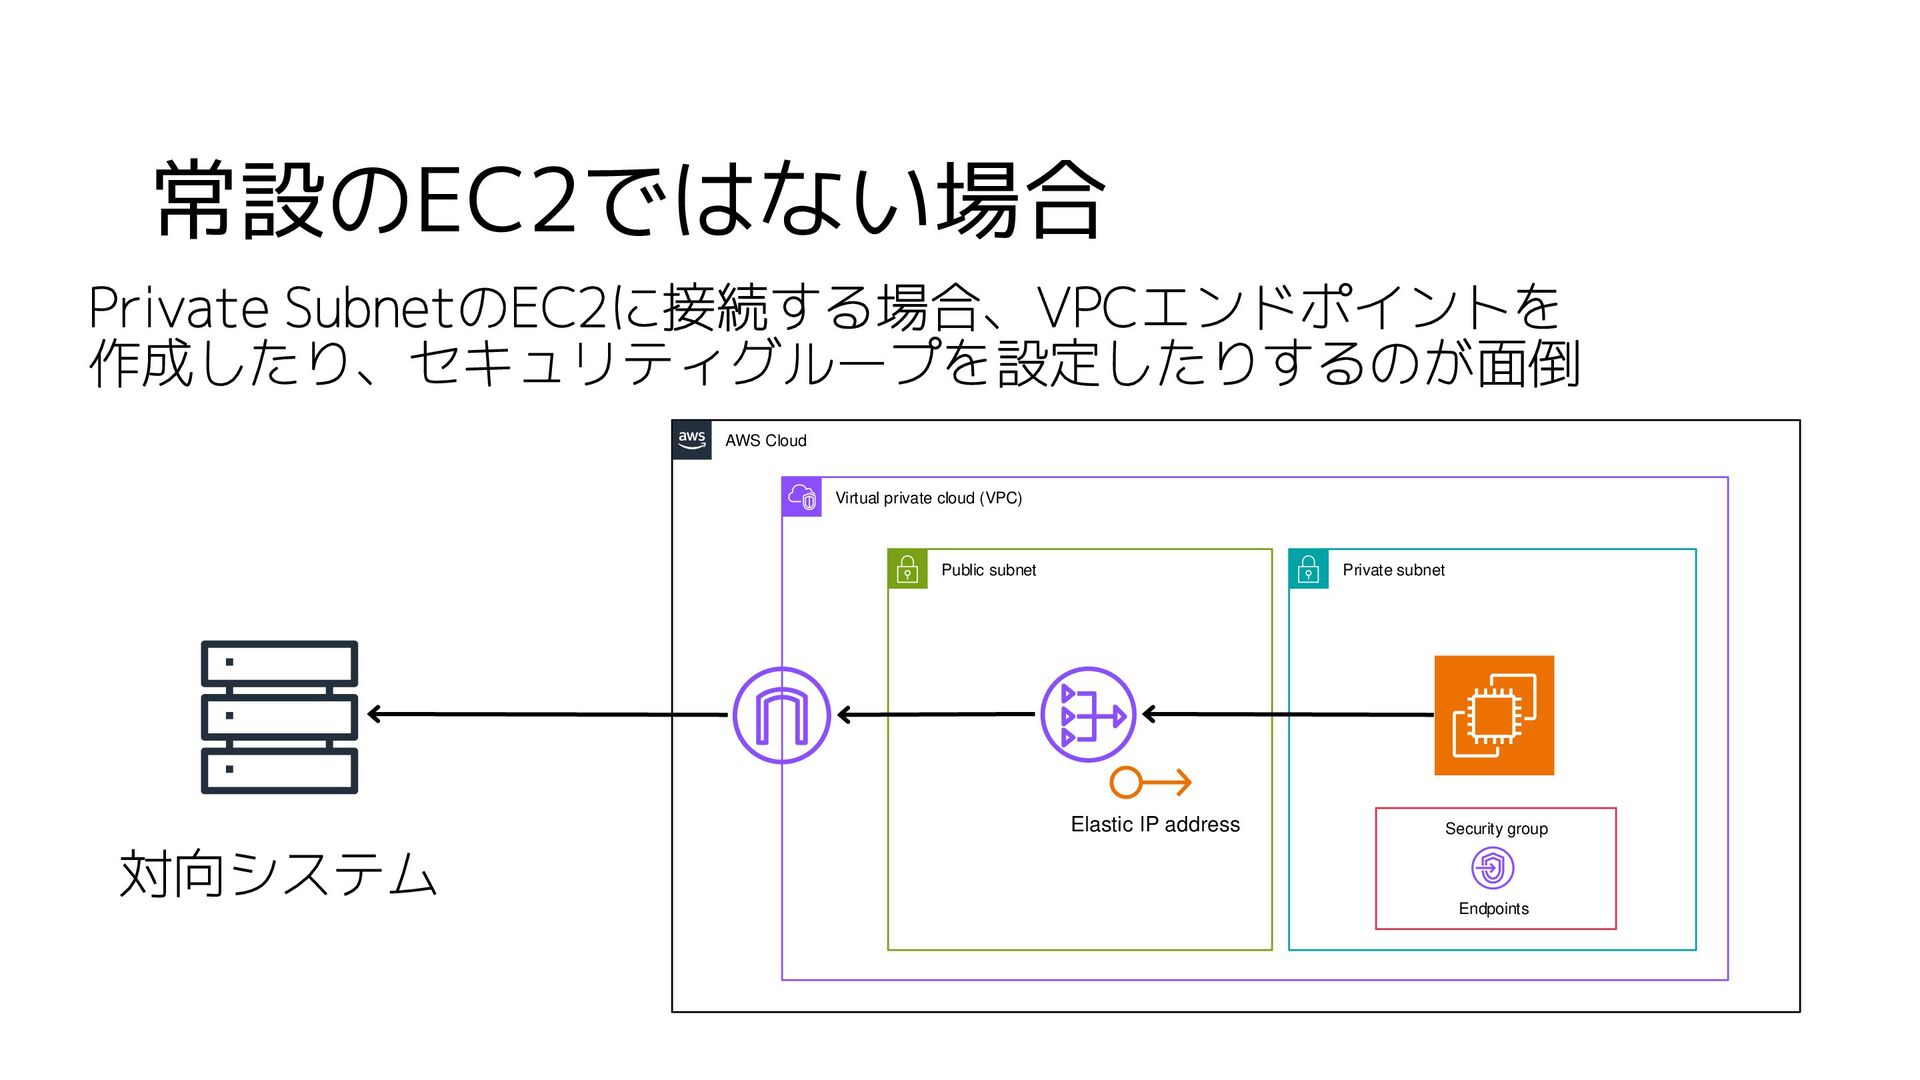
常設のEC2ではない場合 対向システム AWS Cloud Virtual private cloud (VPC) Public subnet
Private subnet Elastic IP address Private SubnetのEC2に接続する場合、VPCエンドポイントを 作成したり、セキュリティグループを設定したりするのが面倒 Endpoints Security group
簡単に疎通確認をする方法はないものか
それ、CloudShellでいけます! やぁ
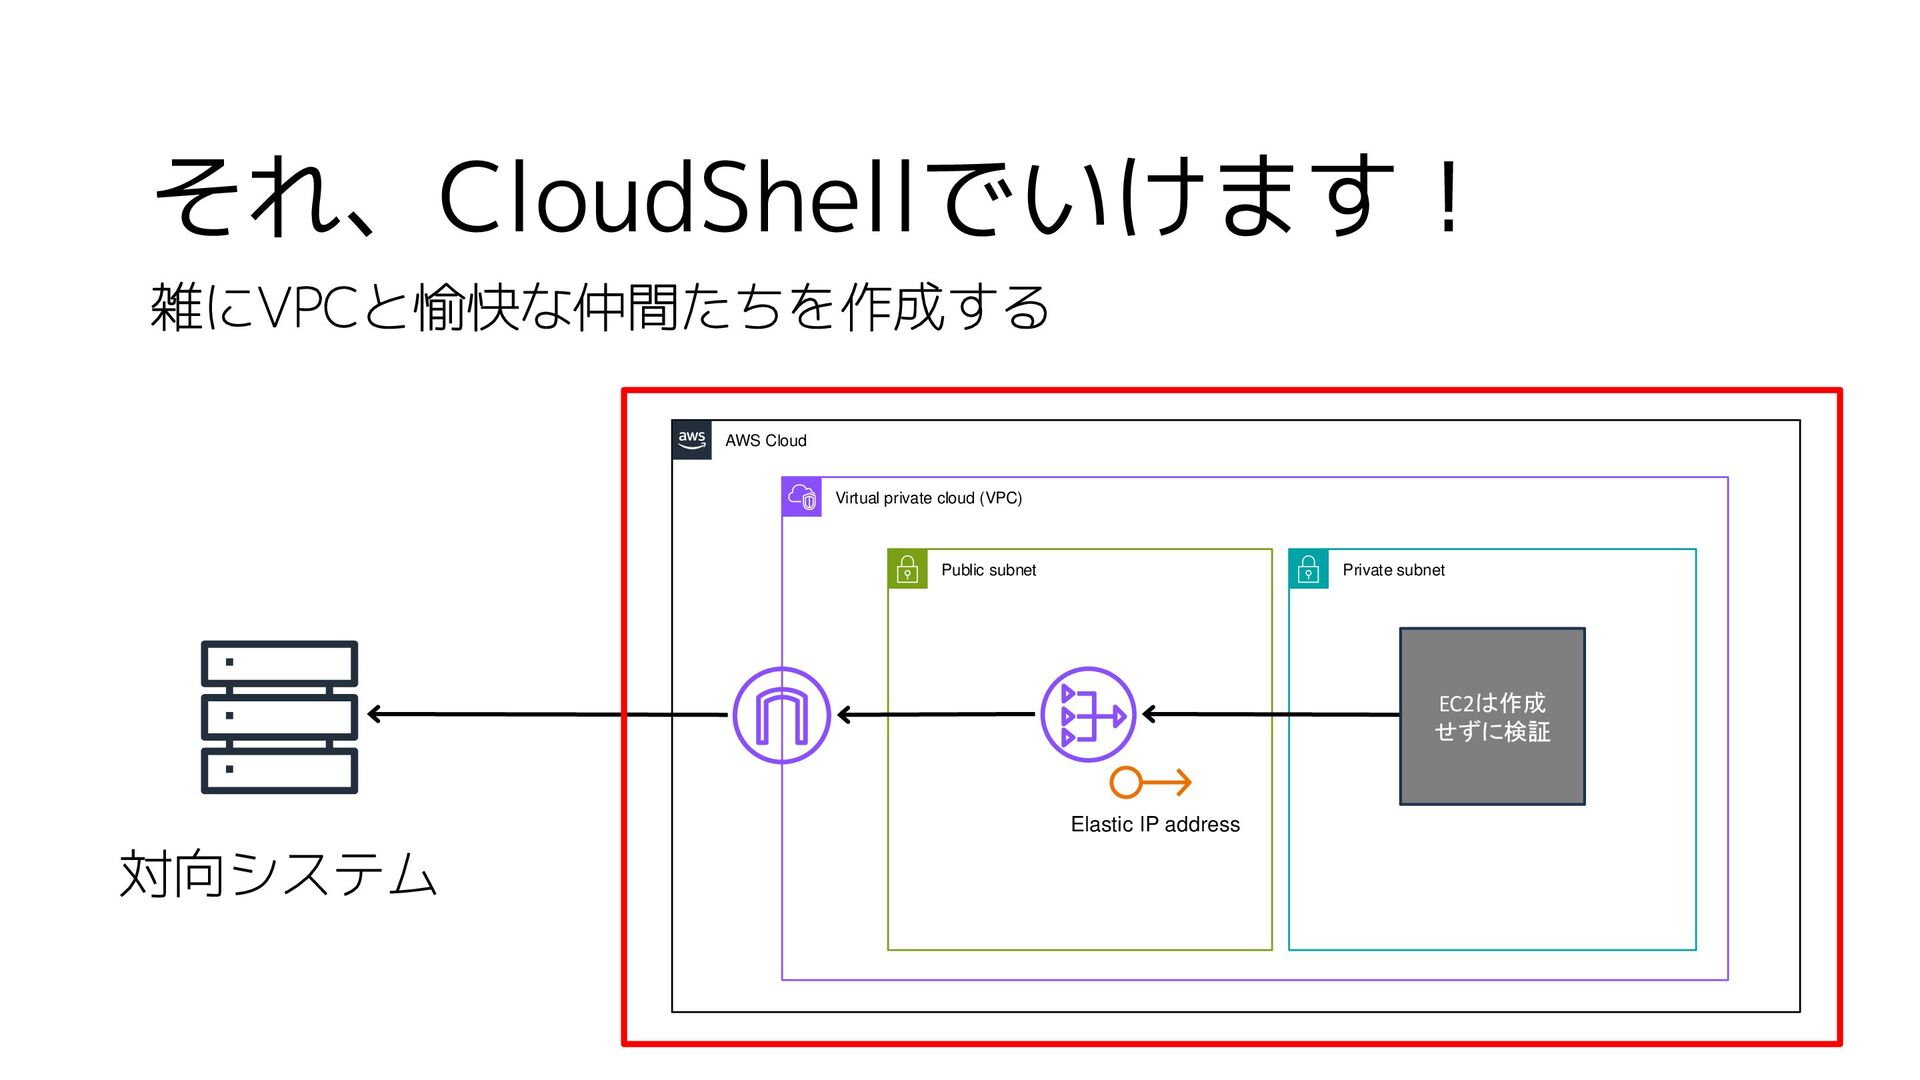
それ、CloudShellでいけます! 対向システム AWS Cloud Virtual private cloud (VPC) Public subnet
Private subnet Elastic IP address 雑にVPCと愉快な仲間たちを作成する EC2は作成 せずに検証
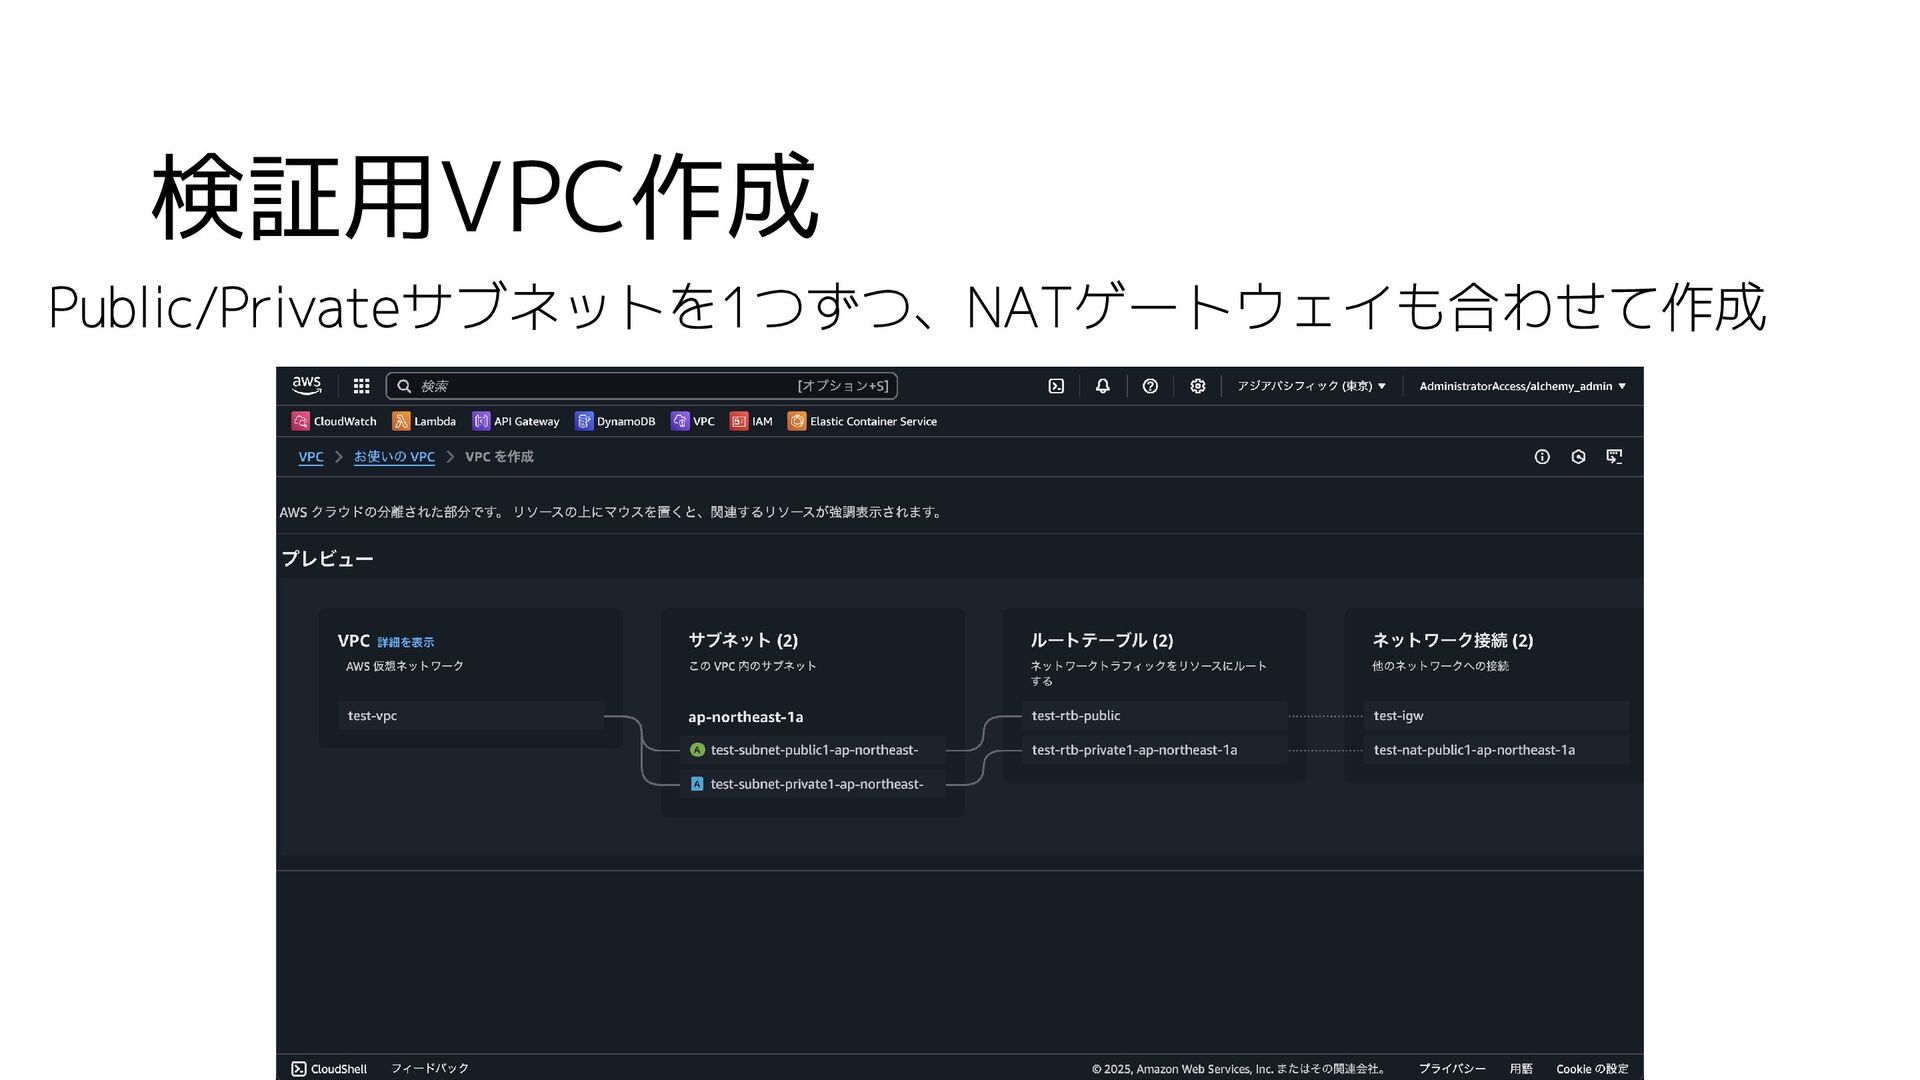
検証用VPC作成 Public/Privateサブネットを1つずつ、NATゲートウェイも合わせて作成
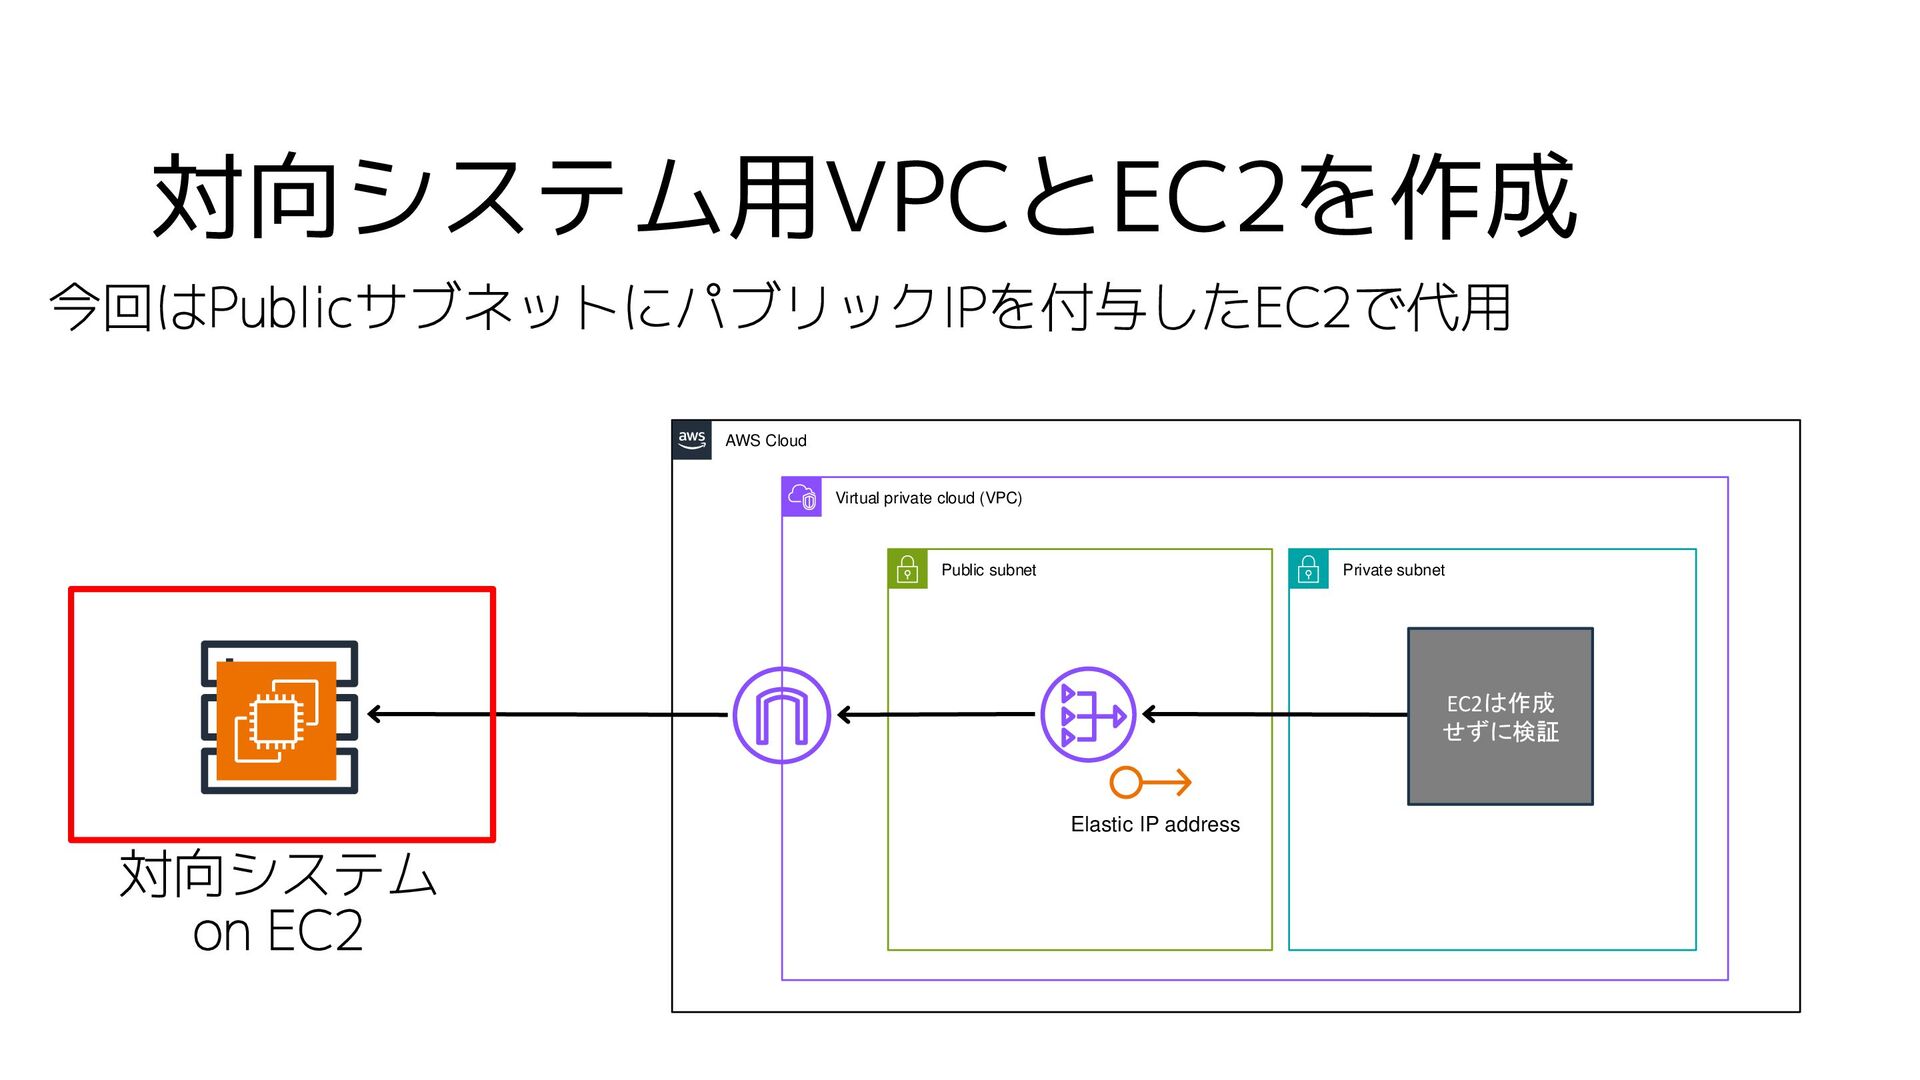
対向システム用VPCとEC2を作成 今回はPublicサブネットにパブリックIPを付与したEC2で代用 対向システム on EC2 AWS Cloud Virtual private cloud
(VPC) Public subnet Private subnet Elastic IP address EC2は作成 せずに検証
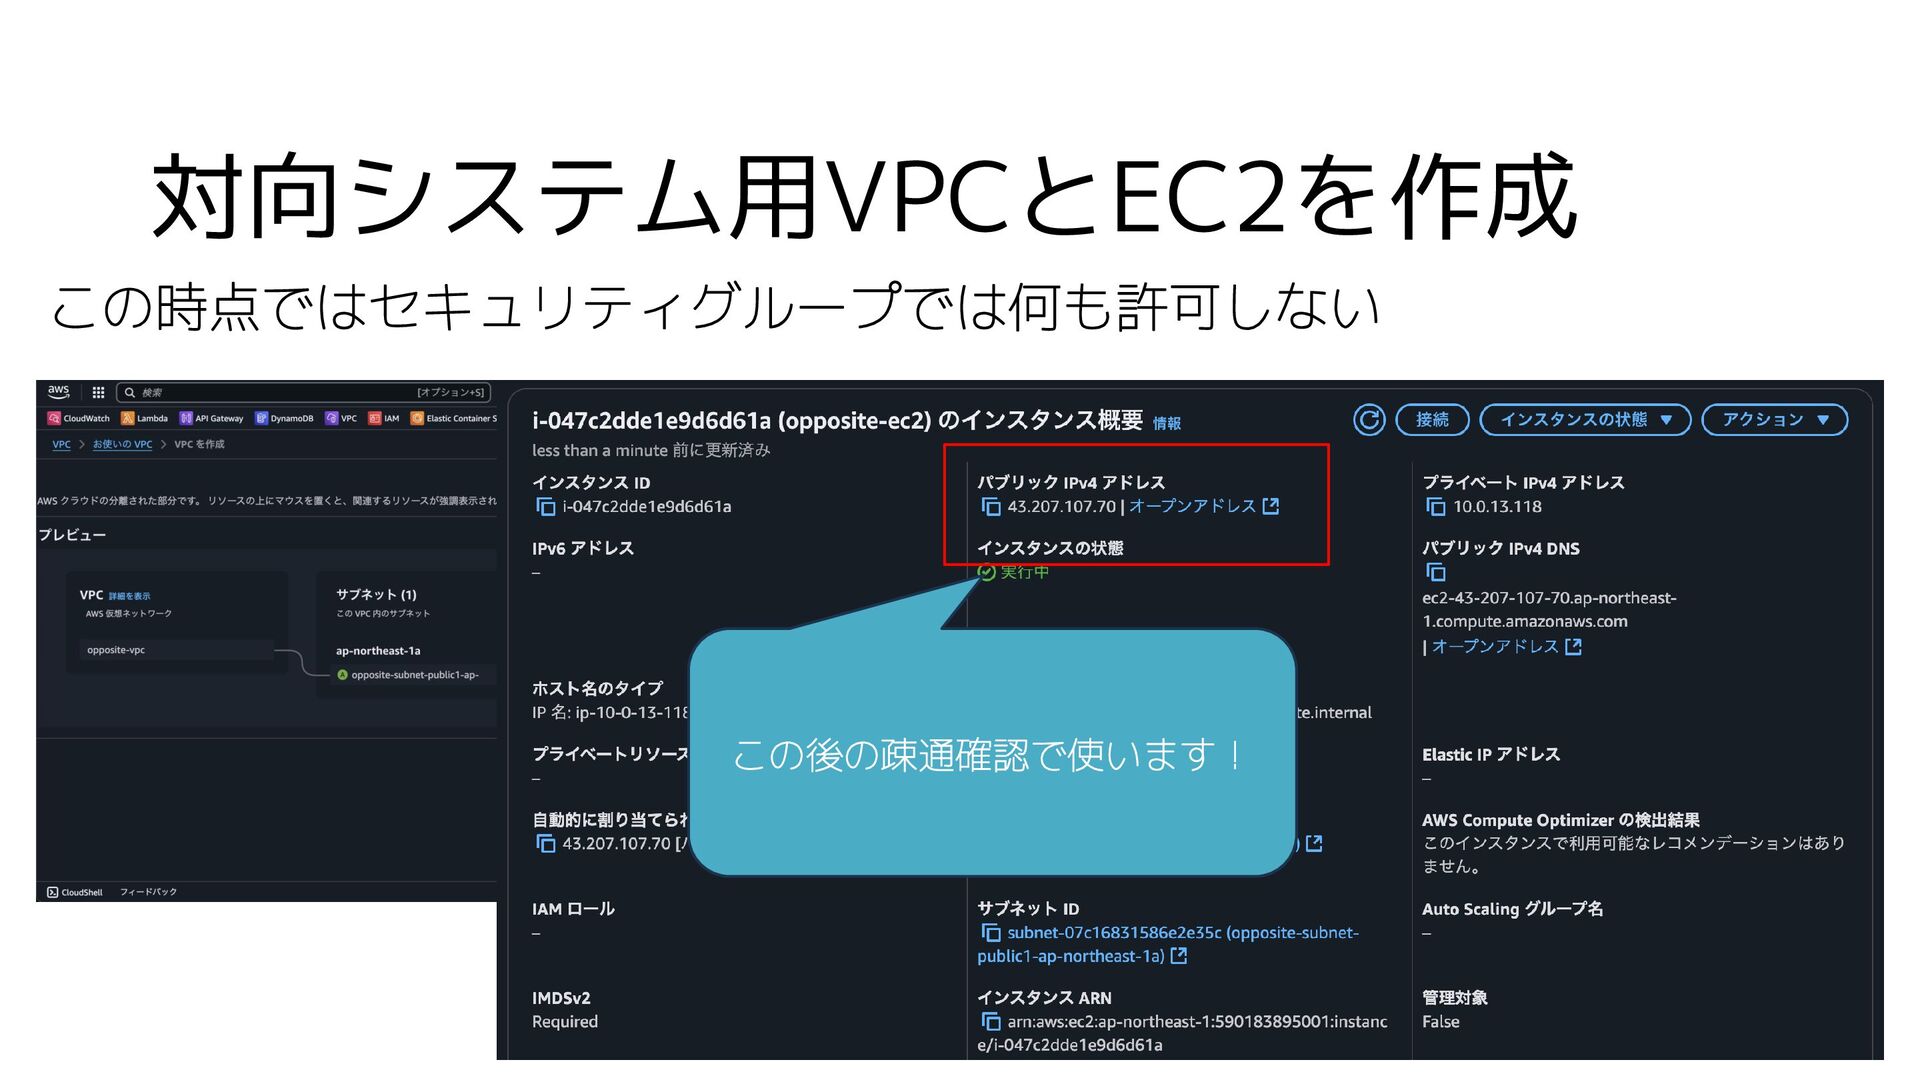
対向システム用VPCとEC2を作成 この時点ではセキュリティグループでは何も許可しない この後の疎通確認で使います!
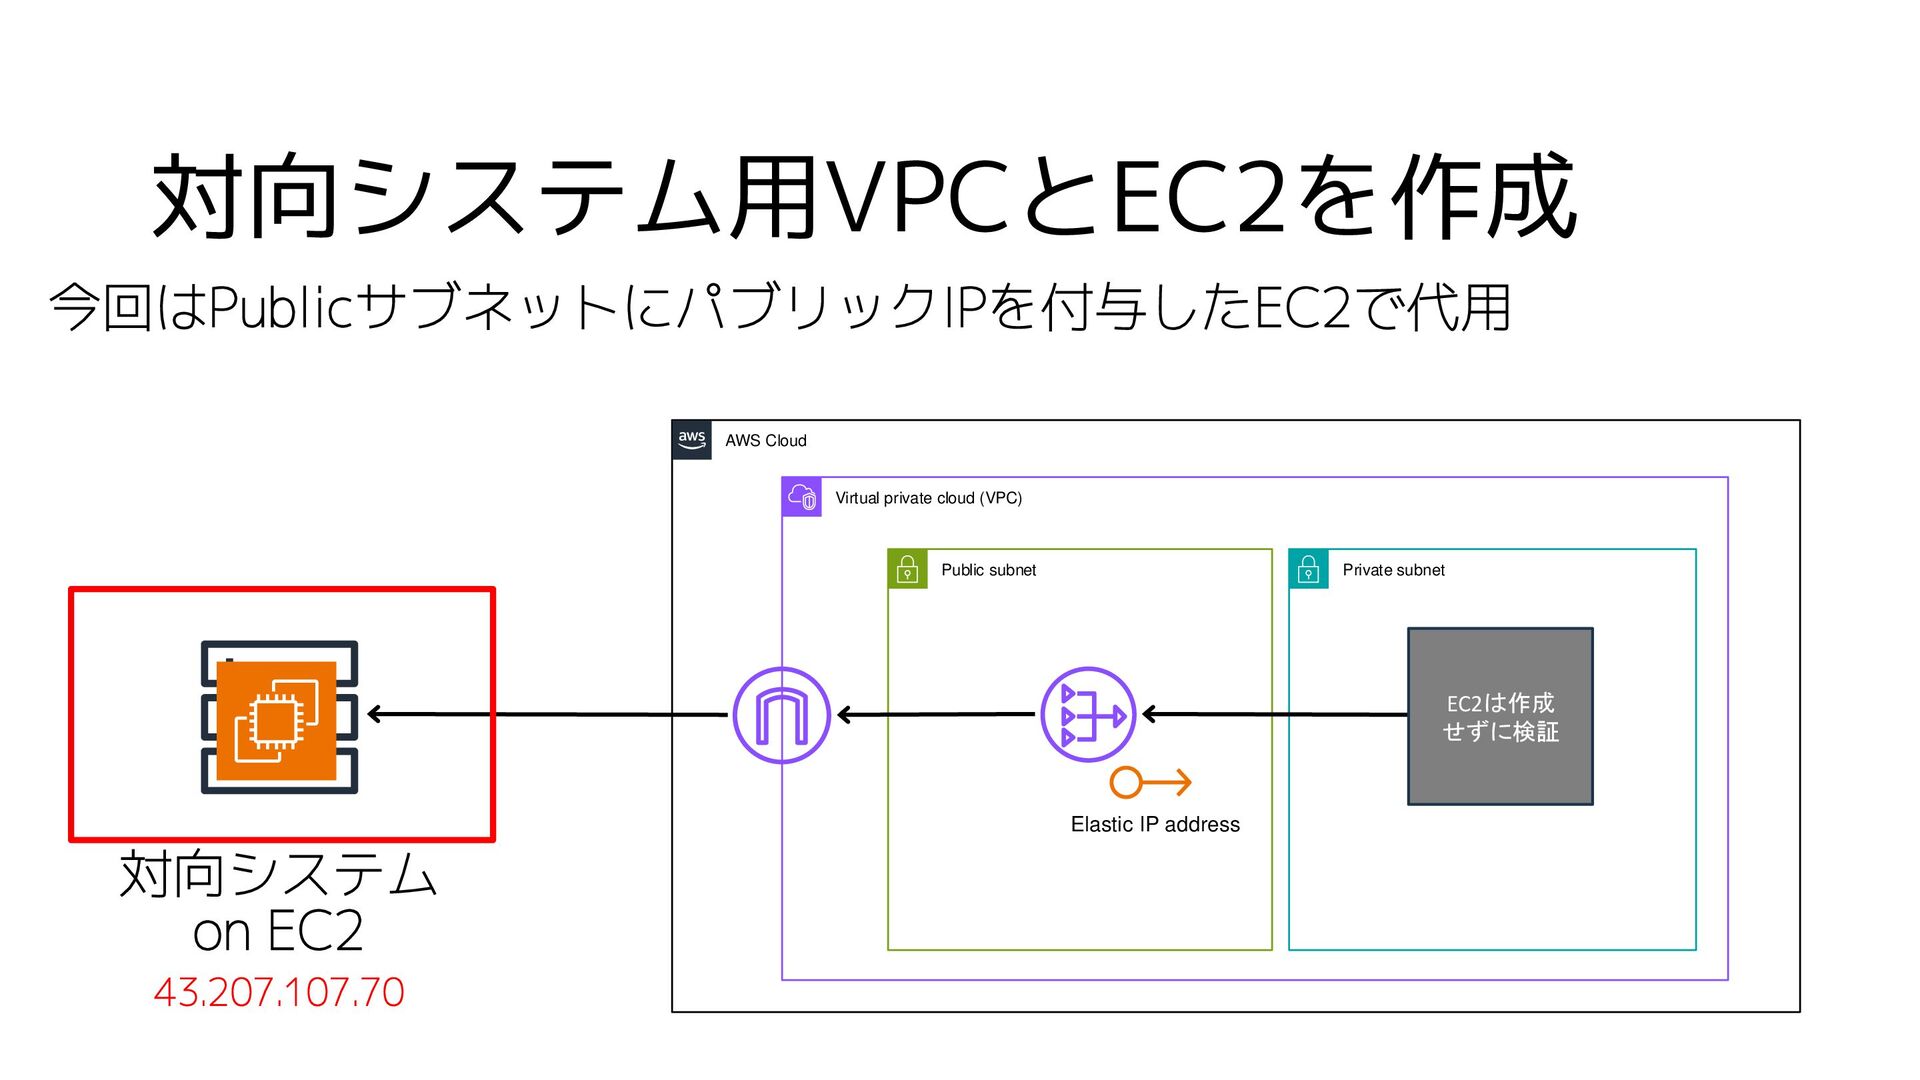
対向システム用VPCとEC2を作成 今回はPublicサブネットにパブリックIPを付与したEC2で代用 対向システム on EC2 43.207.107.70 AWS Cloud Virtual private
cloud (VPC) Public subnet Private subnet Elastic IP address EC2は作成 せずに検証
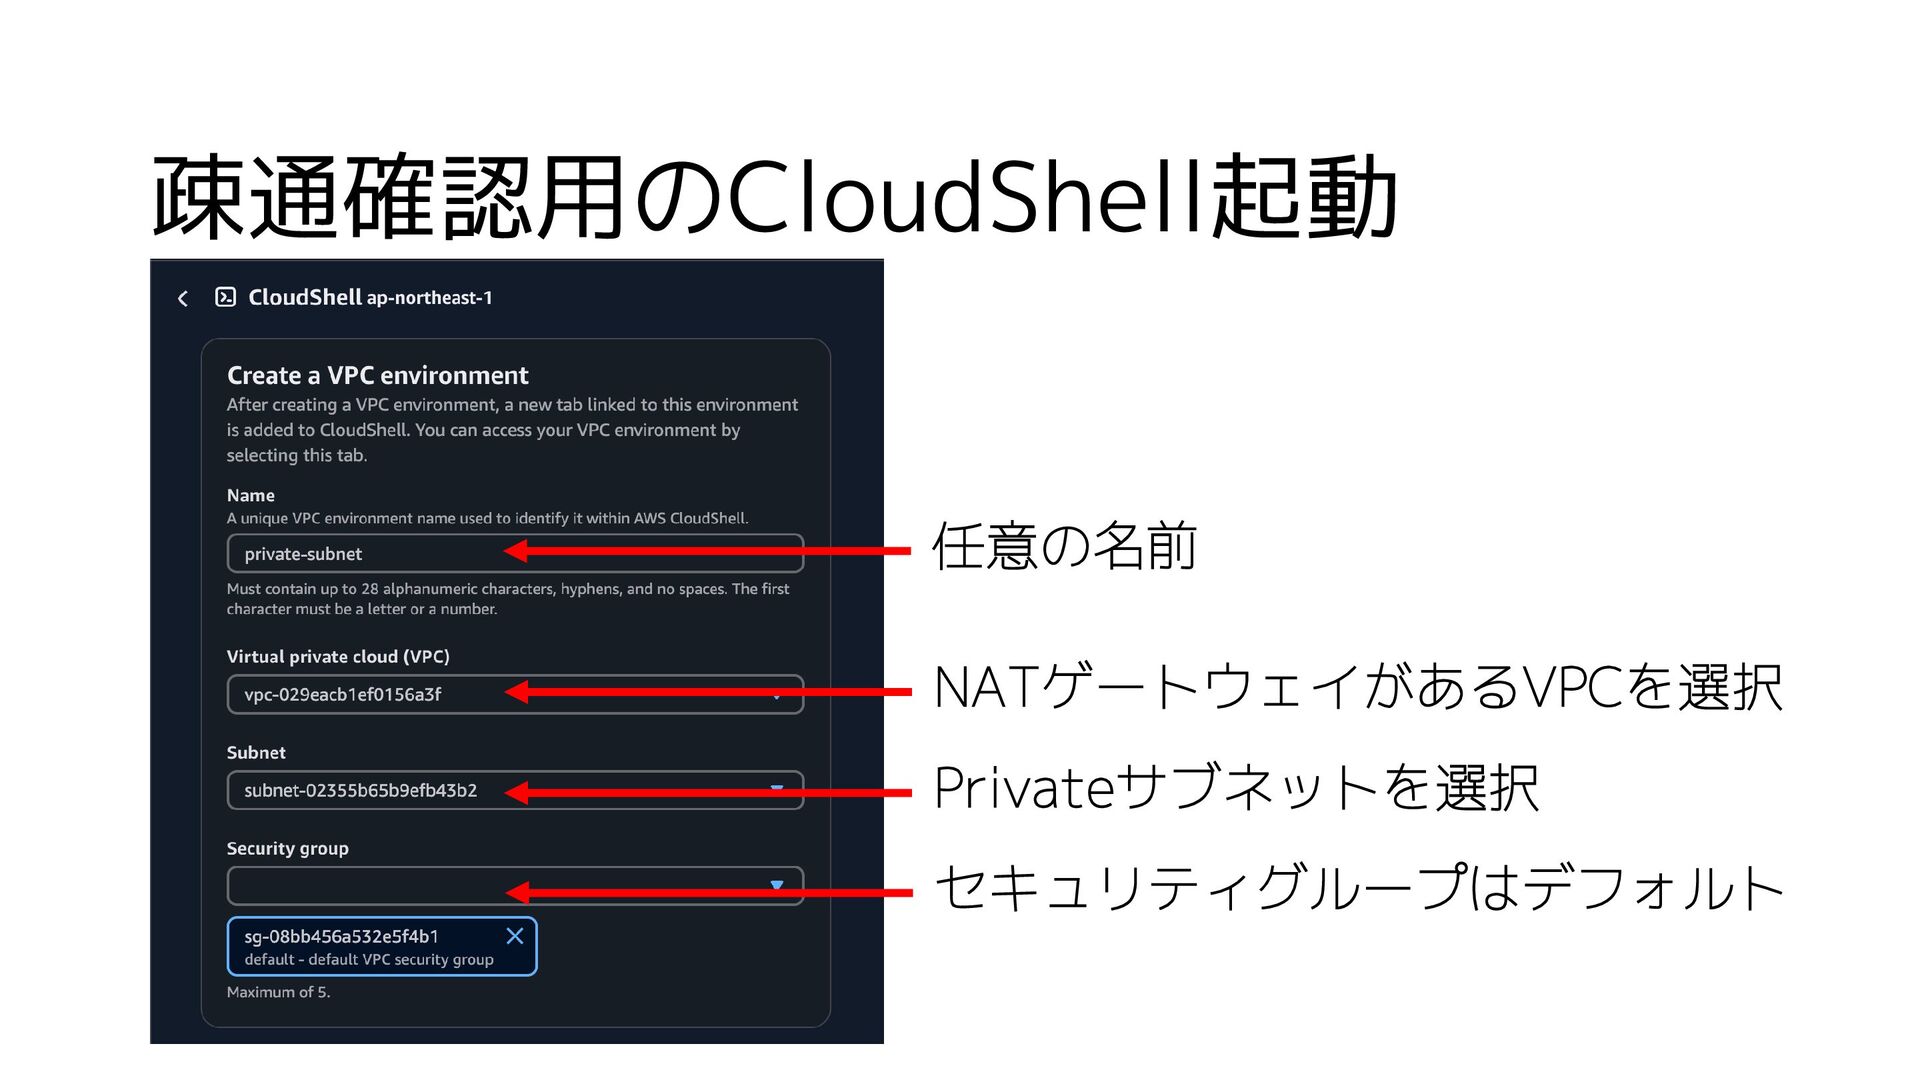
疎通確認用のCloudShell起動 NATゲートウェイがあるVPCを選択 Privateサブネットを選択 セキュリティグループはデフォルト 任意の名前
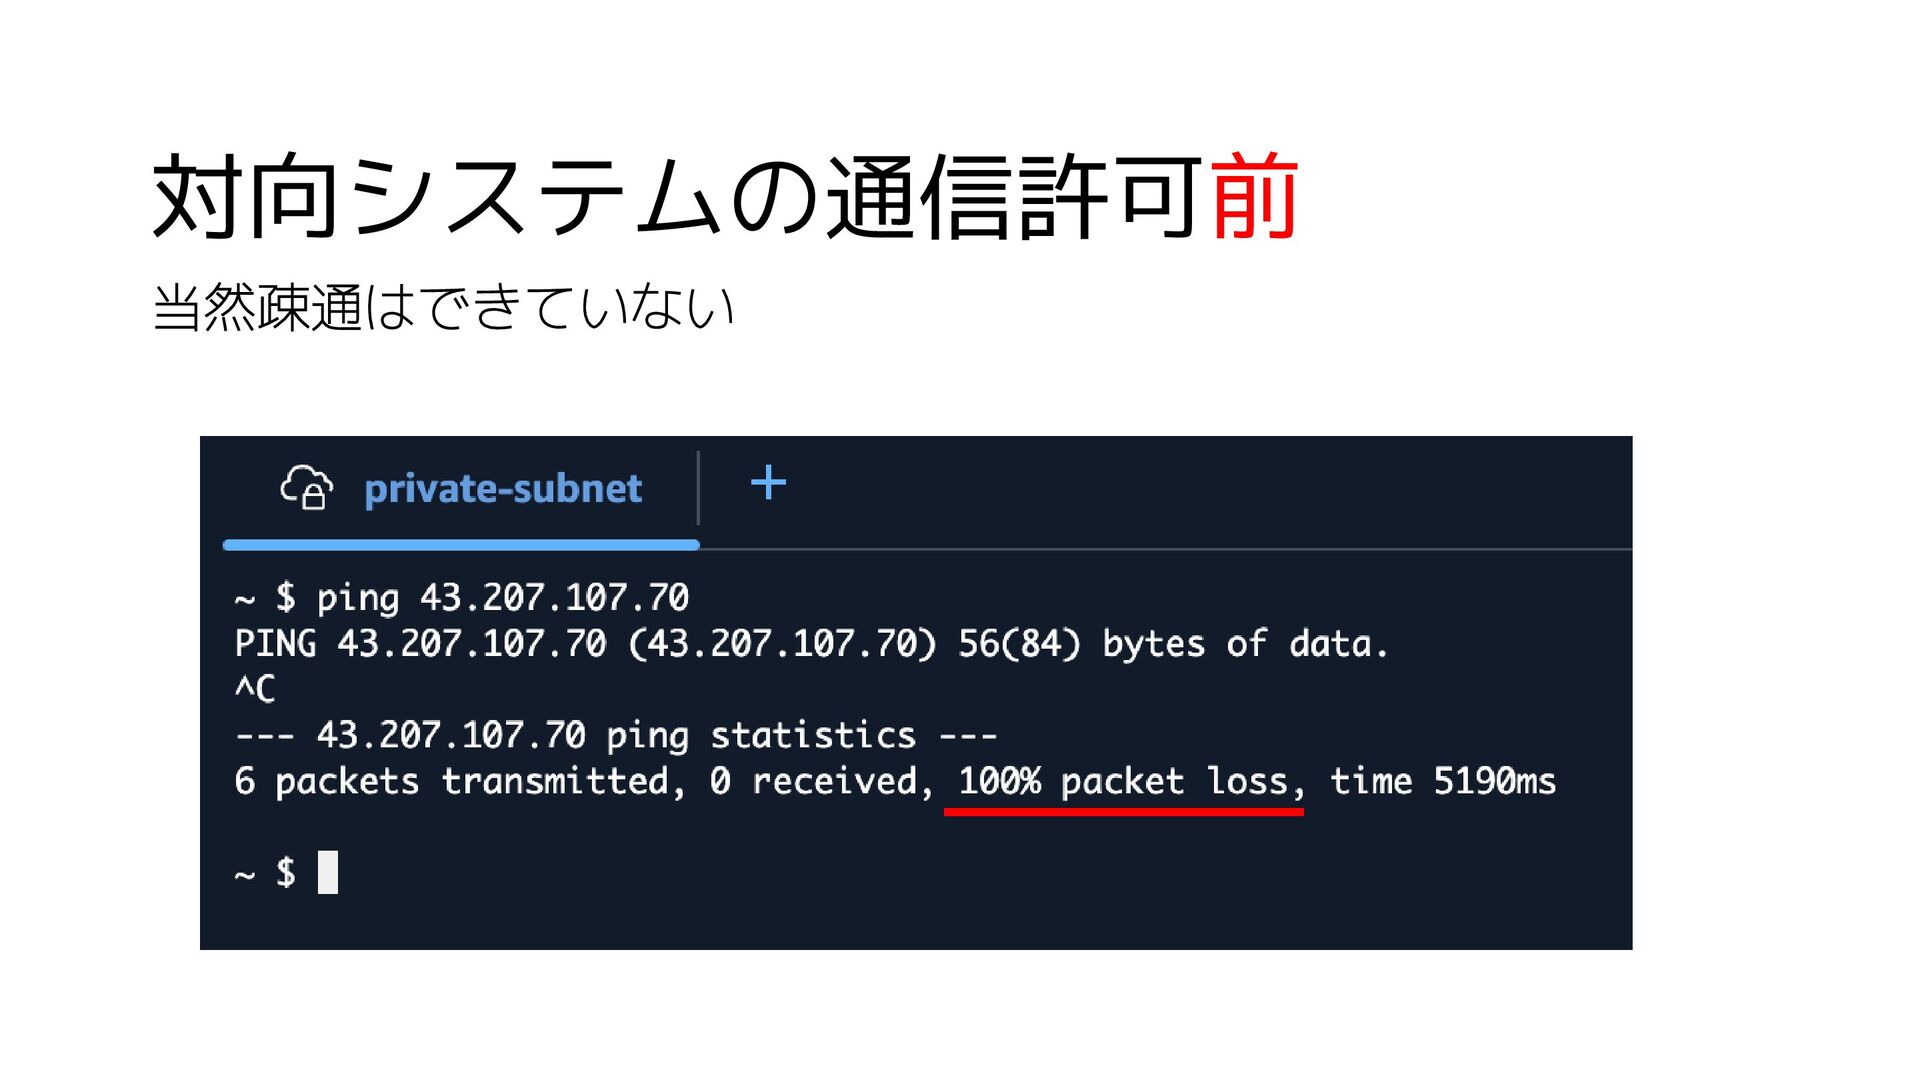
対向システムの通信許可前 当然疎通はできていない
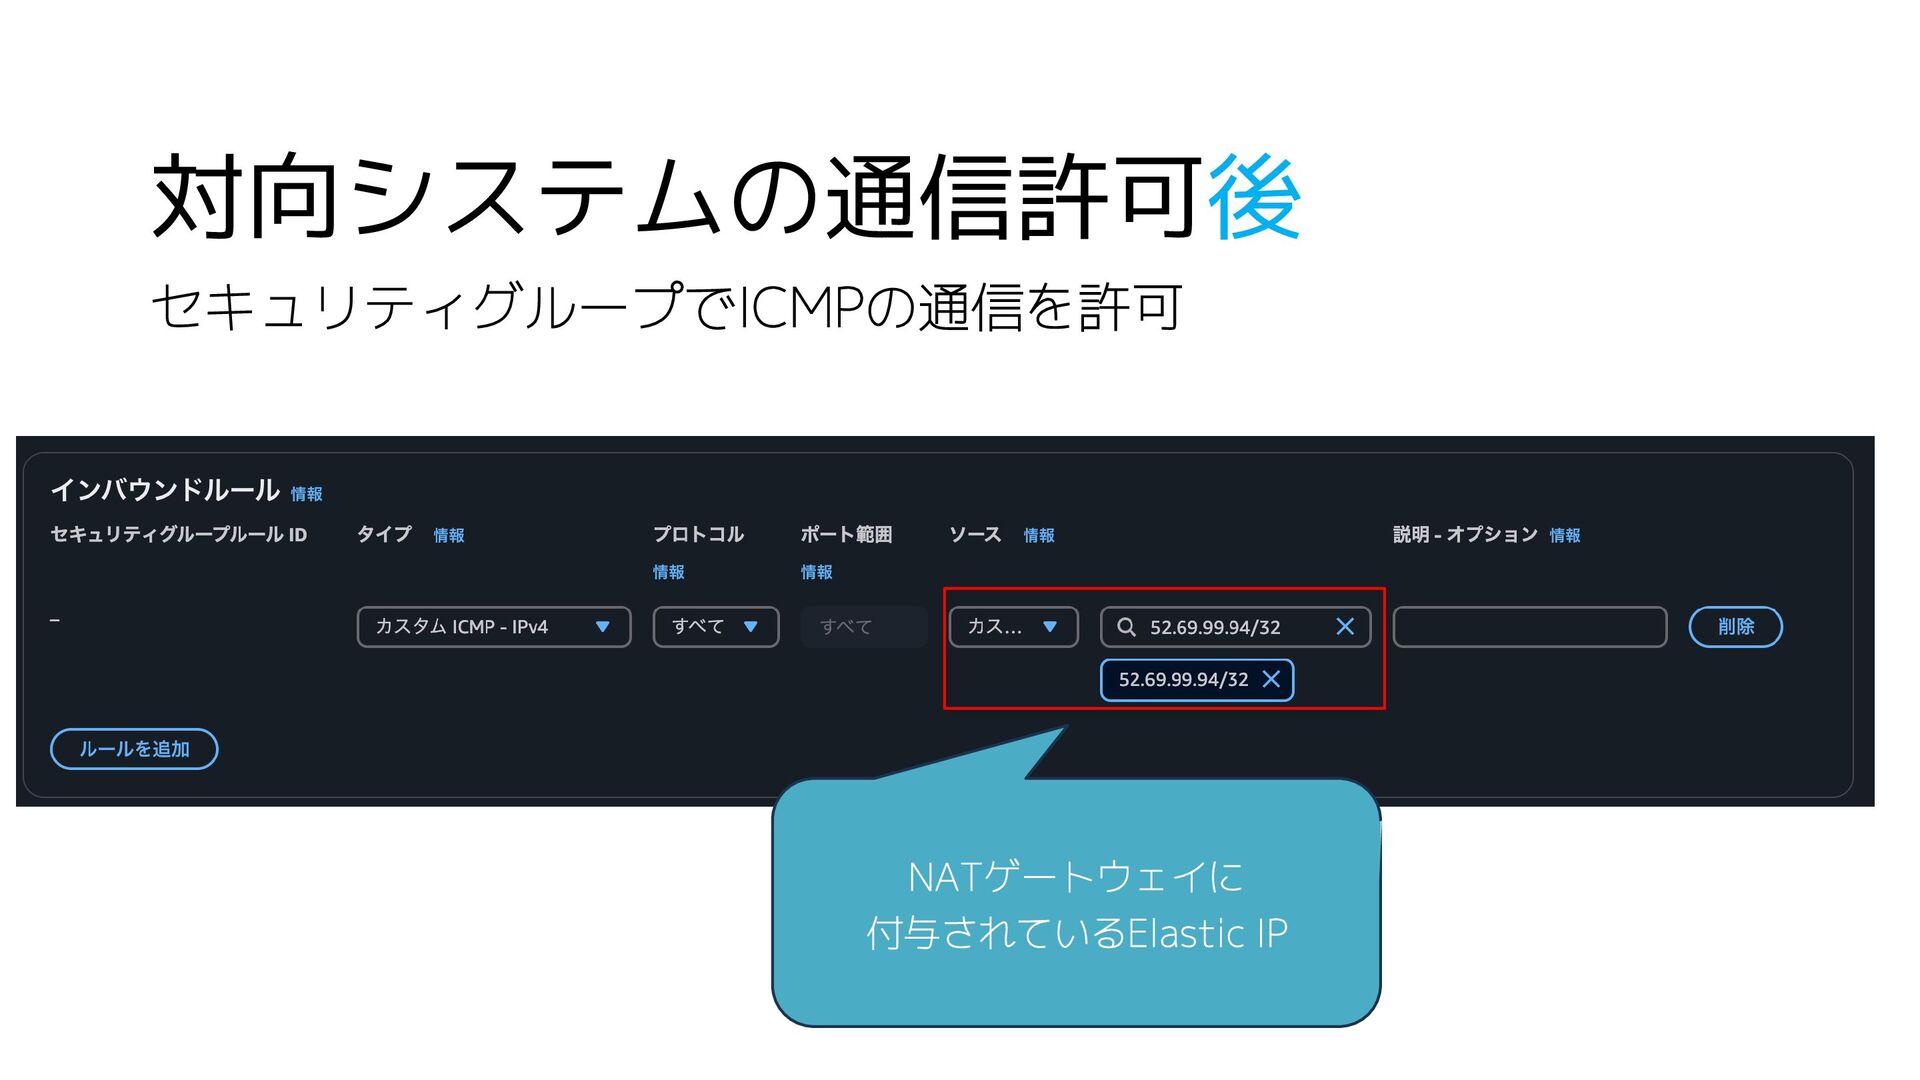
対向システムの通信許可後 セキュリティグループでICMPの通信を許可 NATゲートウェイに 付与されているElastic IP
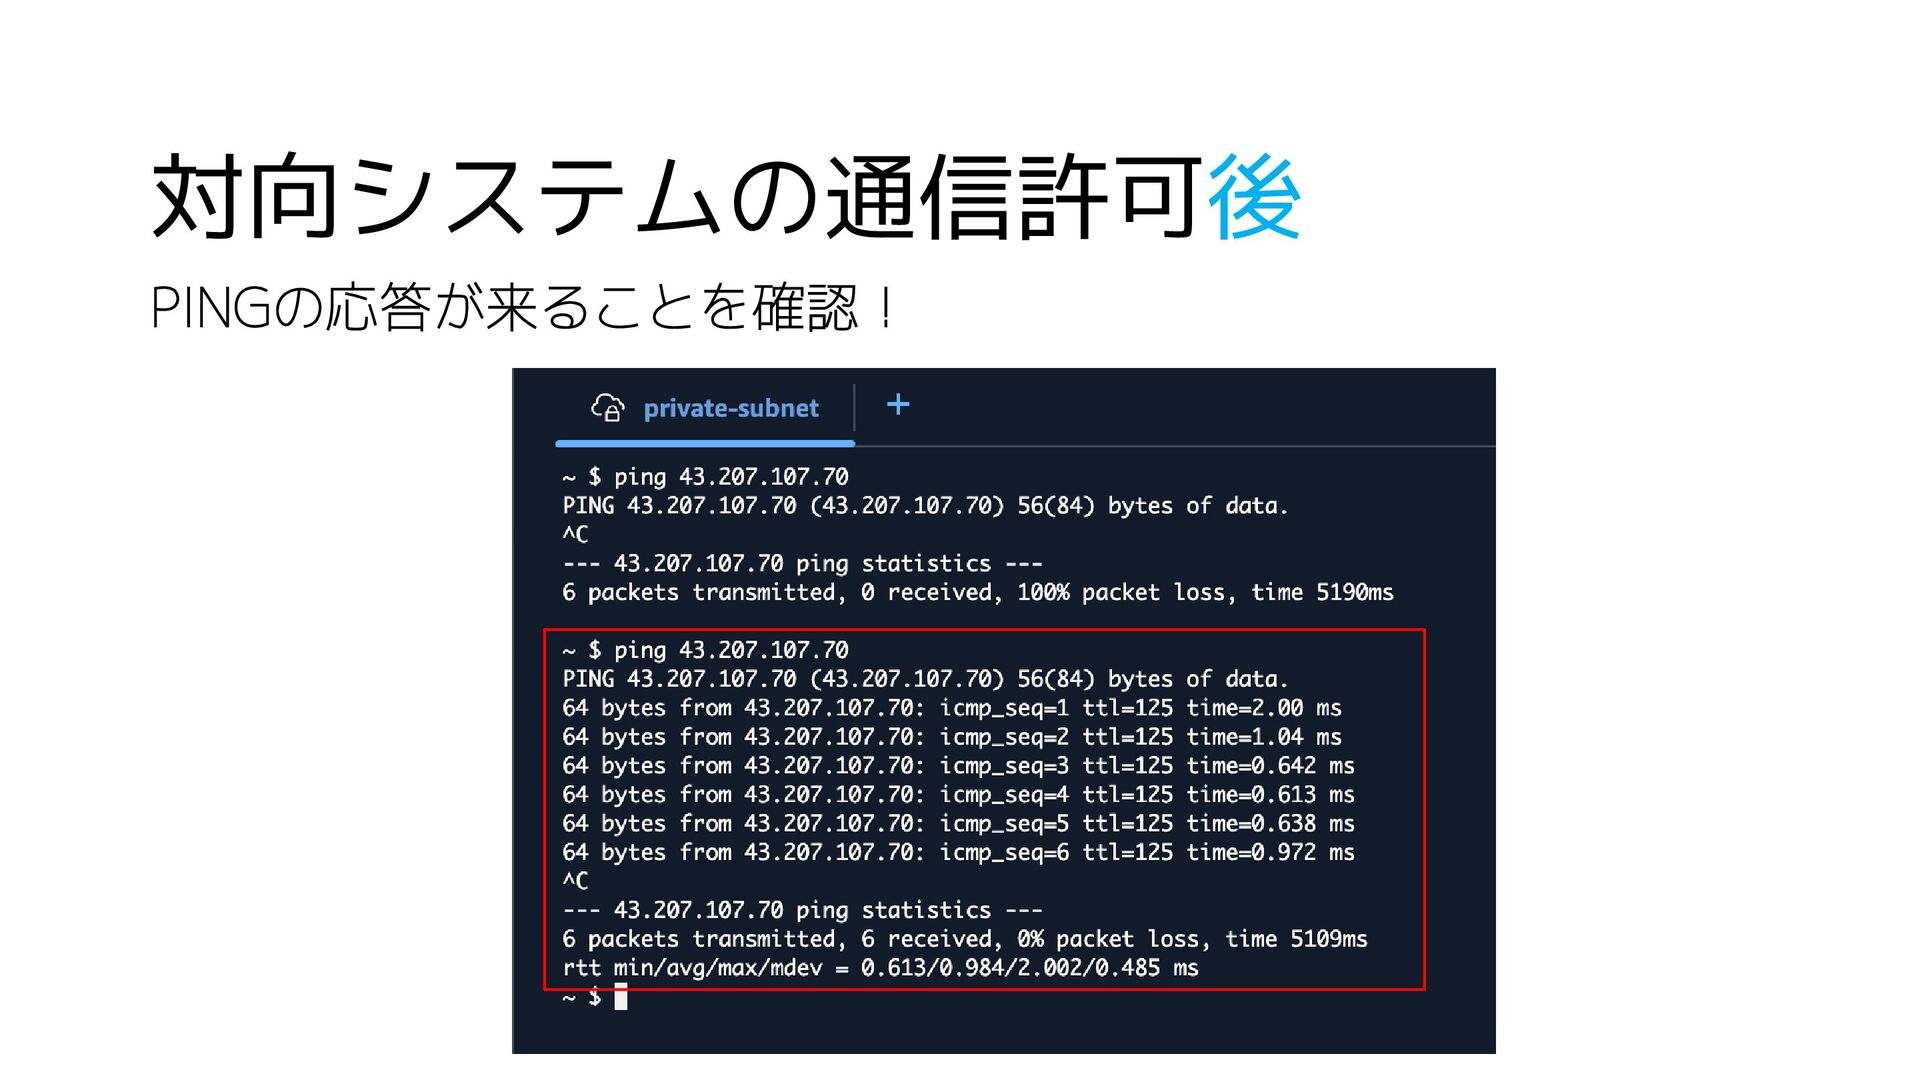
対向システムの通信許可後 PINGの応答が来ることを確認!
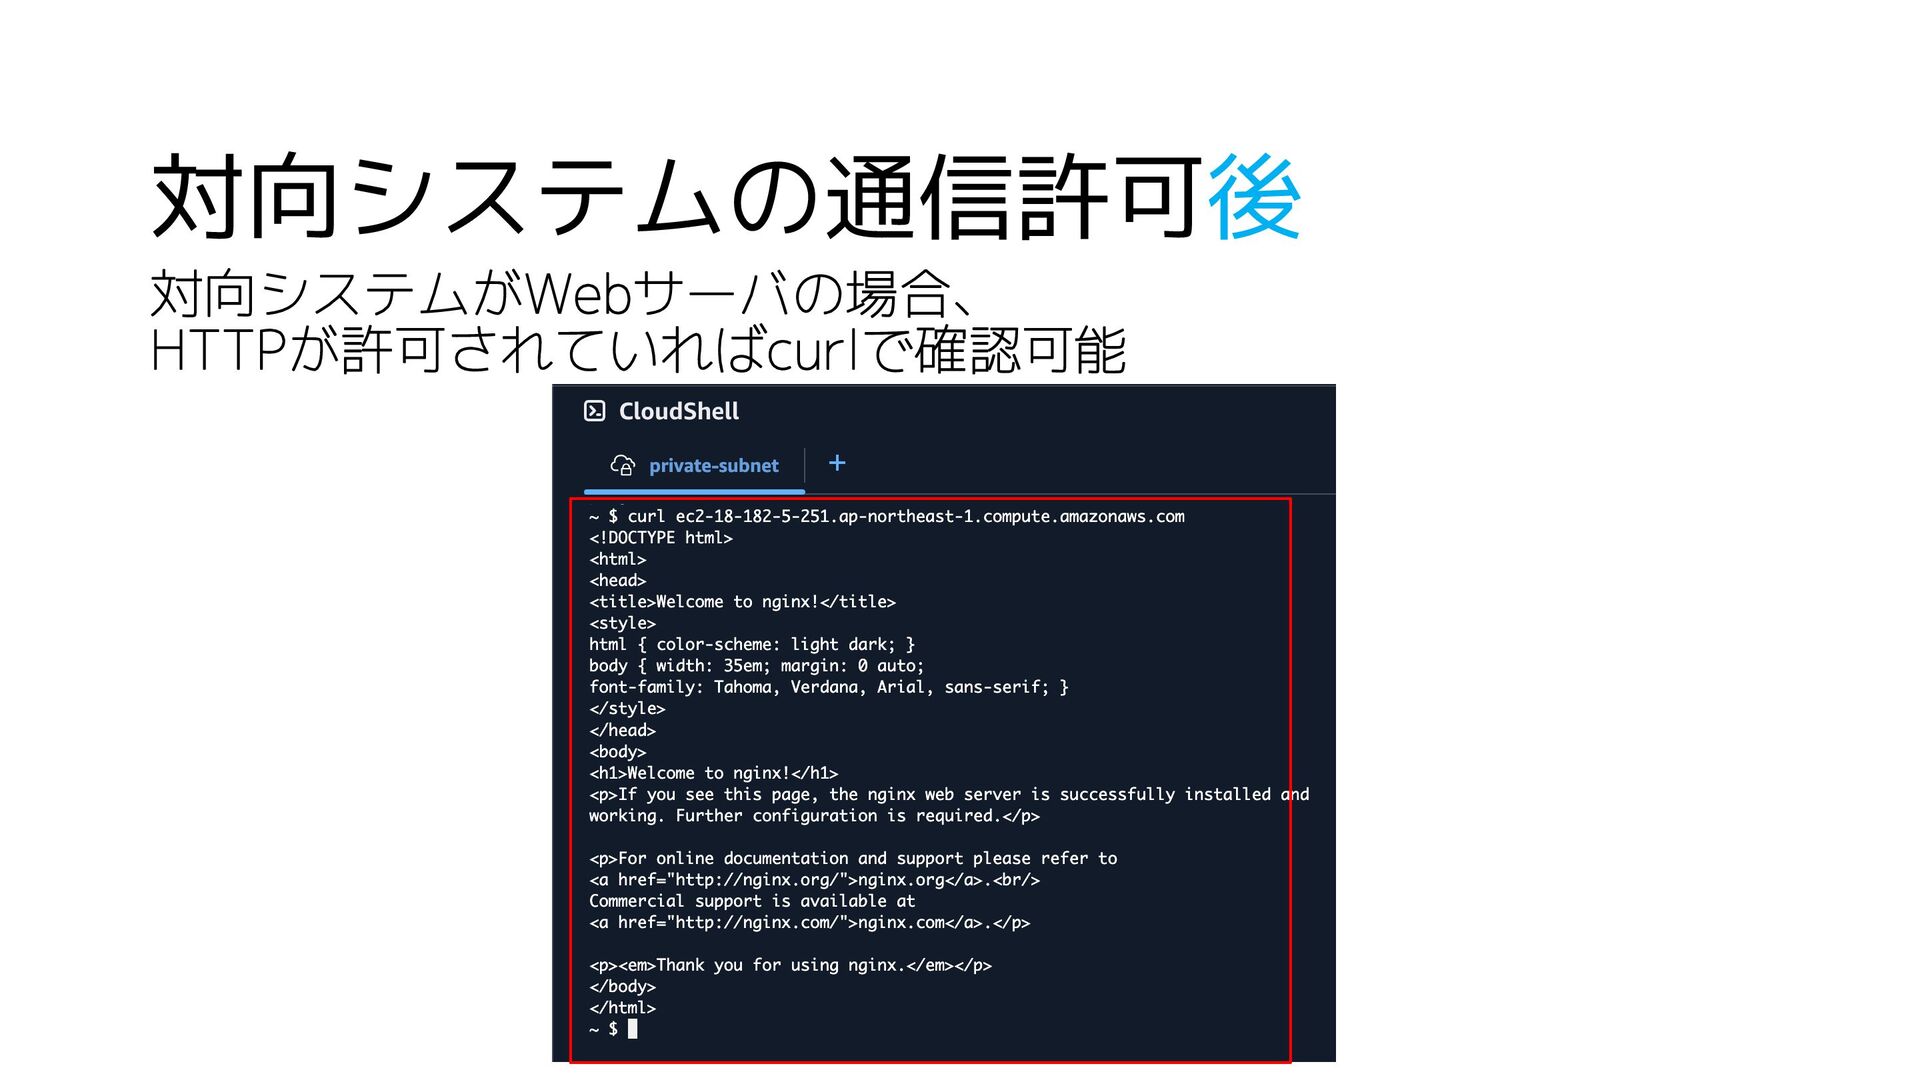
対向システムの通信許可後 対向システムがWebサーバの場合、 HTTPが許可されていればcurlで確認可能
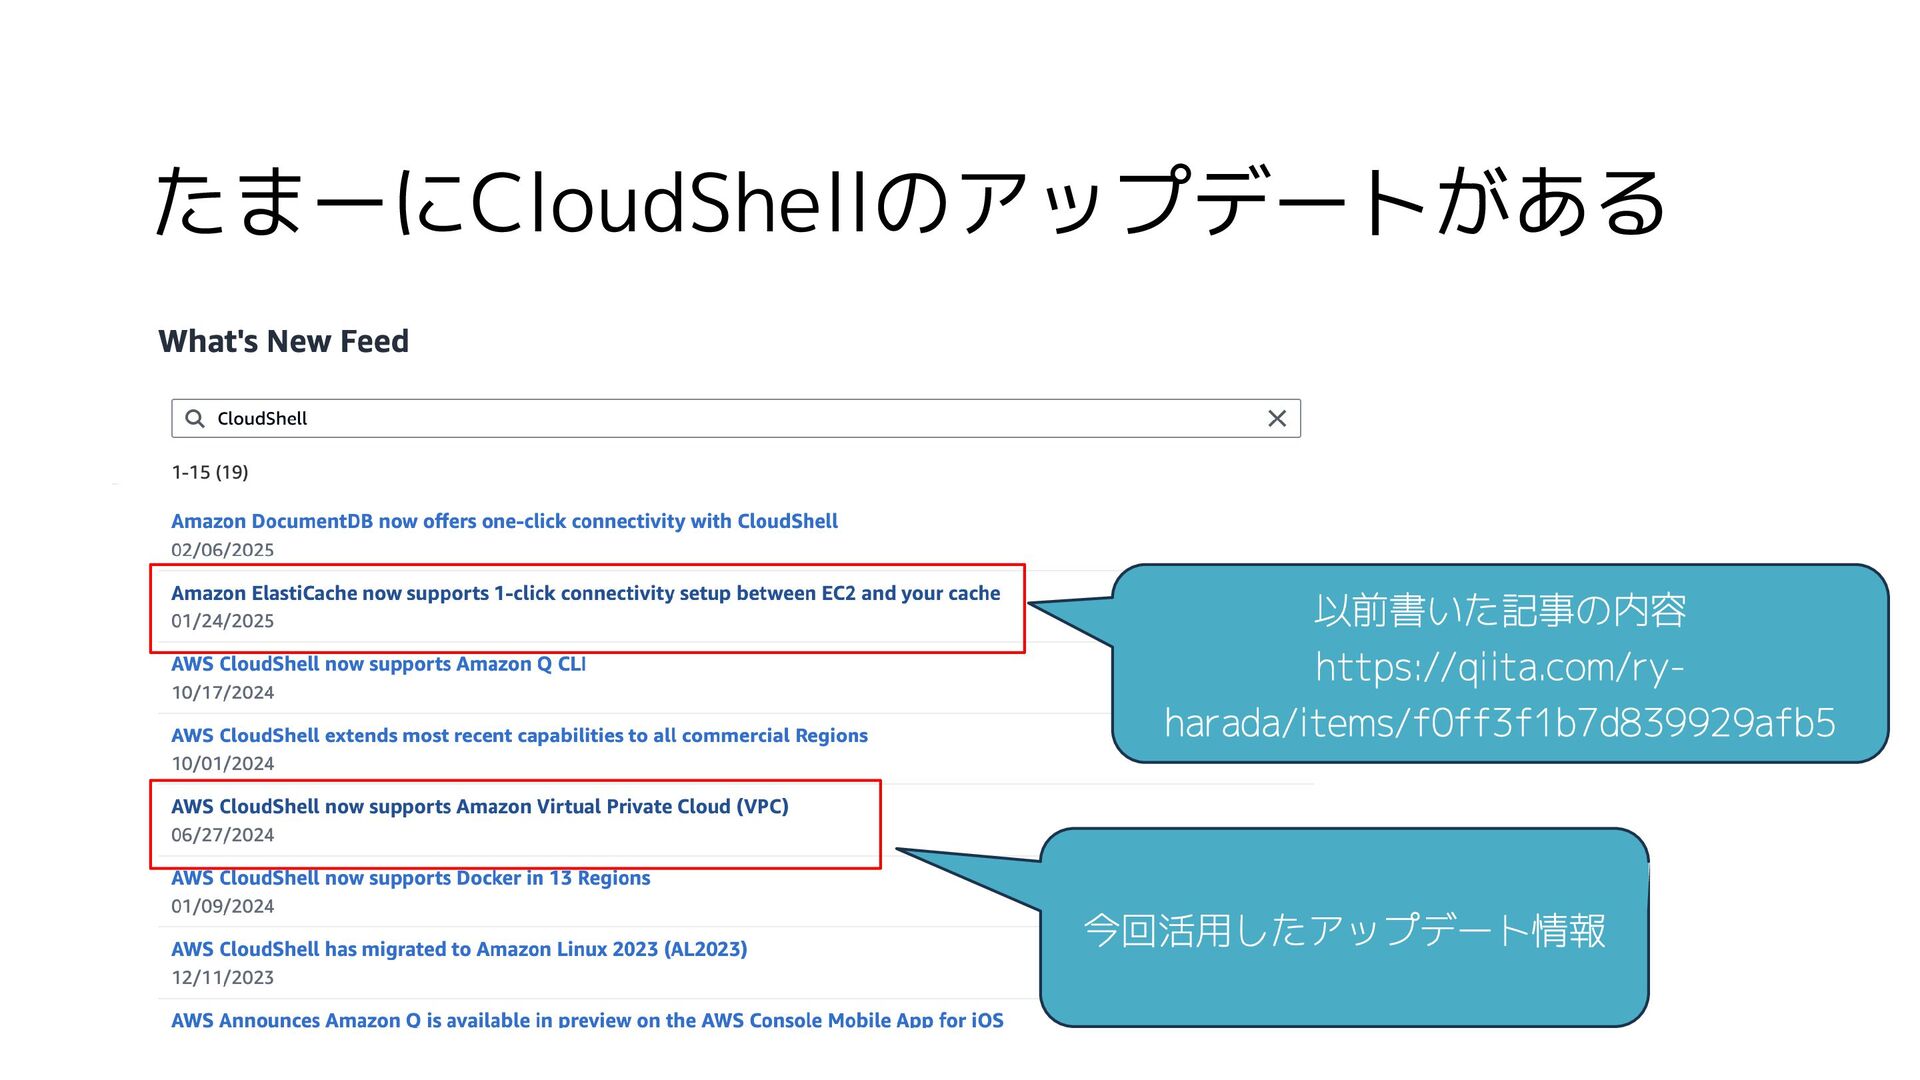
たまーにCloudShellのアップデートがある 今回活用したアップデート情報 以前書いた記事の内容 https://qiita.com/ry- harada/items/f0ff3f1b7d839929afb5
まとめ • 痒いところに手が届くCloudShell • 雑に確認したい時に使おう!
ありがとうございました!


 alchemy1115
 zozotech
 har1101
 nek0128
 kawaguti
 aoi1
 techtekt
 plaidtech
 ysasago
 nwiizo
 masasuzu
 vananth22
 katzueno
 rocio
 helmedeiros
 chrislema
 brettharned
 jacobtomlinson
 malarkey
 inesmontani
 axbom
 aki_iinuma
 katiecoart
 morganepeng
 cassininazir