Share
Embed
Avoiding damage, shame and regrets: data protection for mobile client-server architectures
We will talk a bit about avoiding snake oil, getting rid of cognitive biases when planning application security, and how to avoid becoming cryptography professor when you only need to protect your app.
By Anastasiia Voitova. Original slides: https://speakerdeck.com/vixentael/avoiding-damage-shame-and-regrets-data-protection-for-mobile-client-server-architectures
Powered by http://xebia.com
do{iOS} conference
November 09, 2015
Transcript
65 slides
-
Avoiding damage, shame and regrets data protection for mobile client-server
architectures #doios @vixentael -
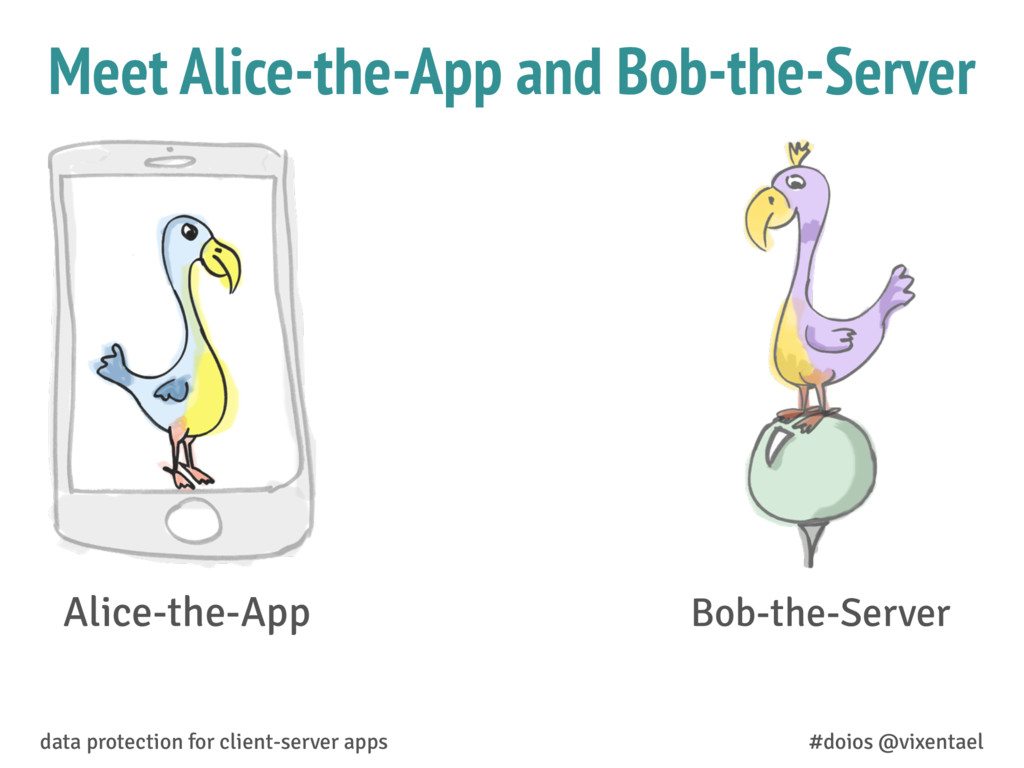
Meet Dodo birds! Alice Bob data protection for client-server apps
#doios @vixentael -
They are chatting together Alice Bob data protection for client-server
apps #doios @vixentael tweet hello -
Here comes Eve.. data protection for client-server apps #doios @vixentael
..the eavesdropping Fennec Fox -
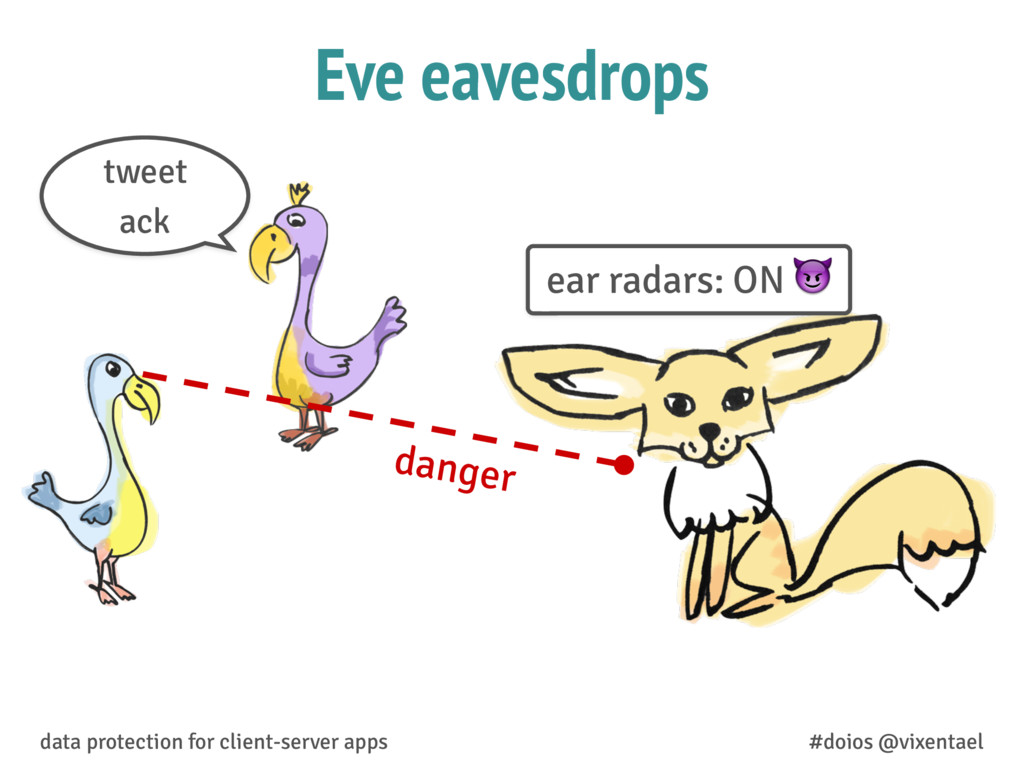
Eve eavesdrops danger data protection for client-server apps #doios @vixentael
tweet ack ear radars: ON -
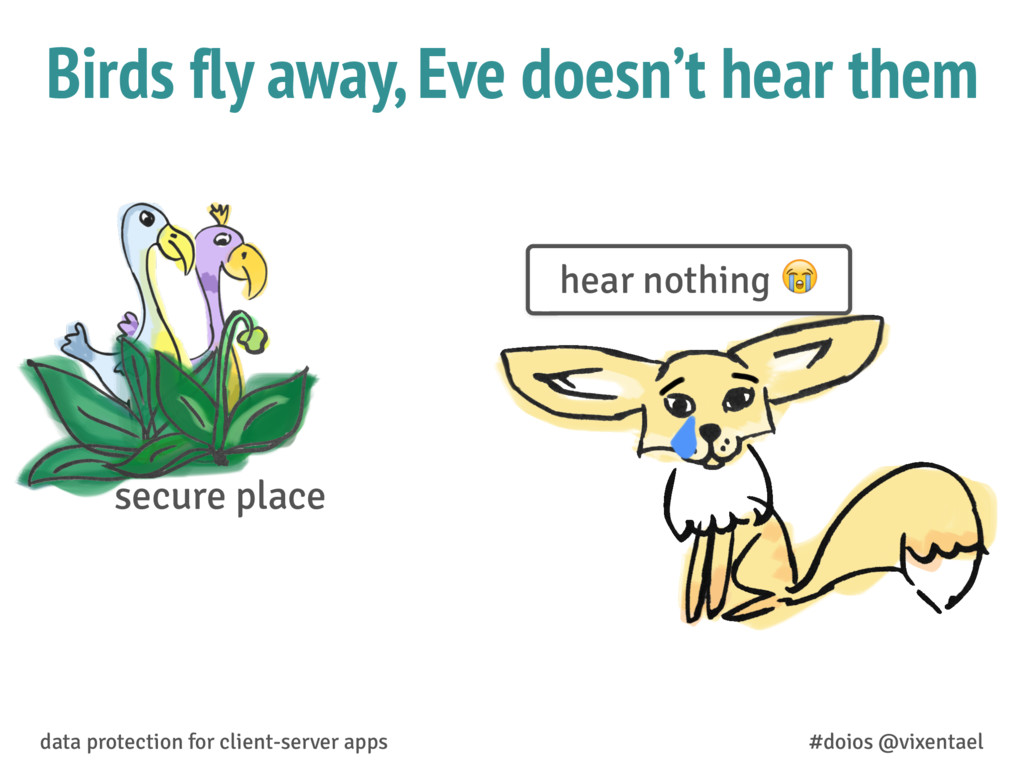
Birds fly away, Eve doesn’t hear them data protection for
client-server apps #doios @vixentael secure place hear nothing -
Risk (threat): Eve hears your secrets Mitigation: physically move away
from Eve Real-world security -
Apple Secure Coding Guide Every program is a potential target.
Your customers’ property and your reputation are at stake. https://developer.apple.com/library/mac/documentation/ Security/Conceptual/SecureCodingGuide/ Introduction.html data protection for client-server apps #doios @vixentael -
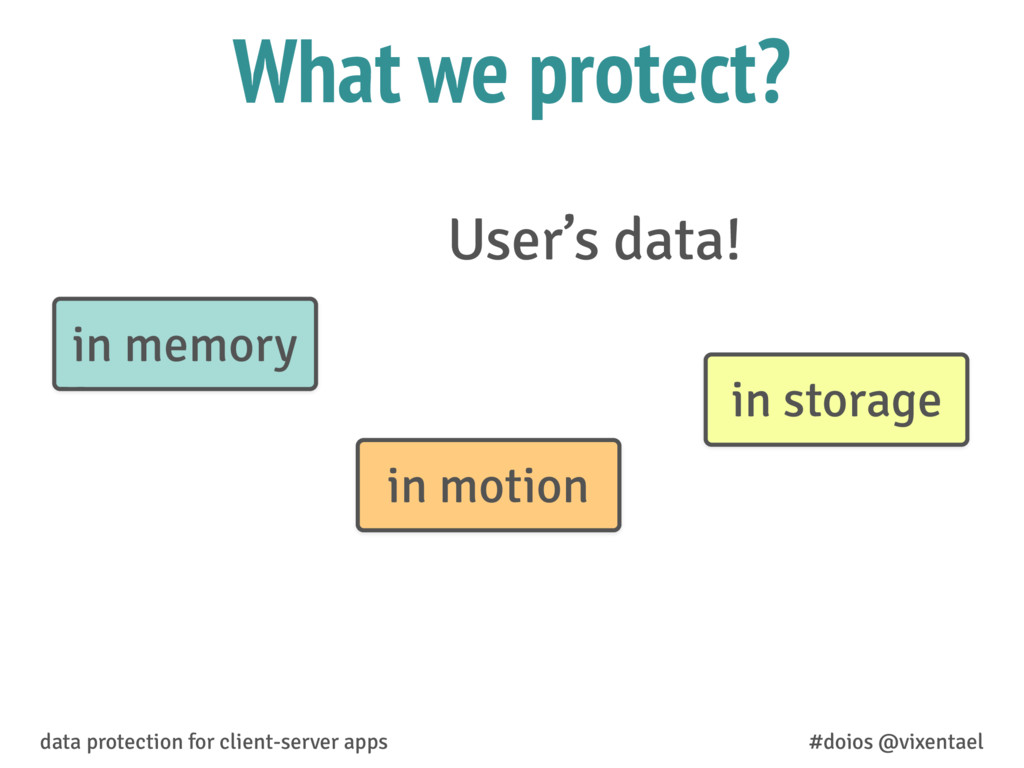
What we protect? User’s data! data protection for client-server apps
#doios @vixentael in storage in motion in memory -
There are hackers.. and threats these hackers exploit.. to create
damage data protection for client-server apps #doios @vixentael Problem: Layer 1 -
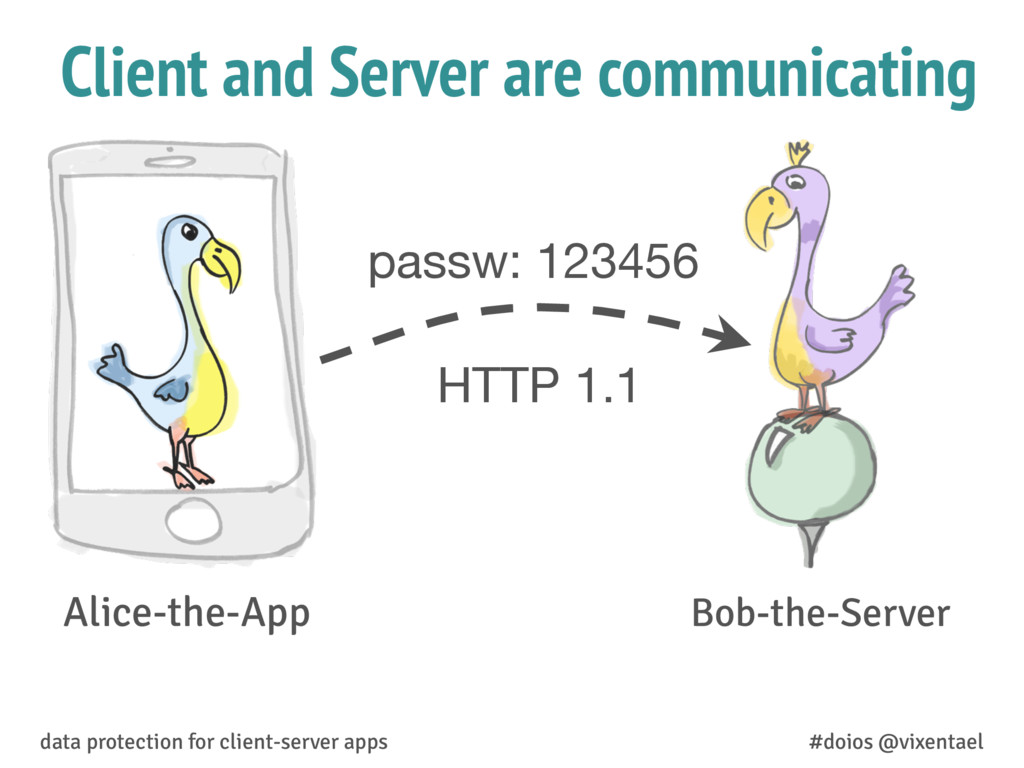
Client and Server are communicating data protection for client-server apps
#doios @vixentael passw: 123456 HTTP 1.1 Alice-the-App Bob-the-Server -
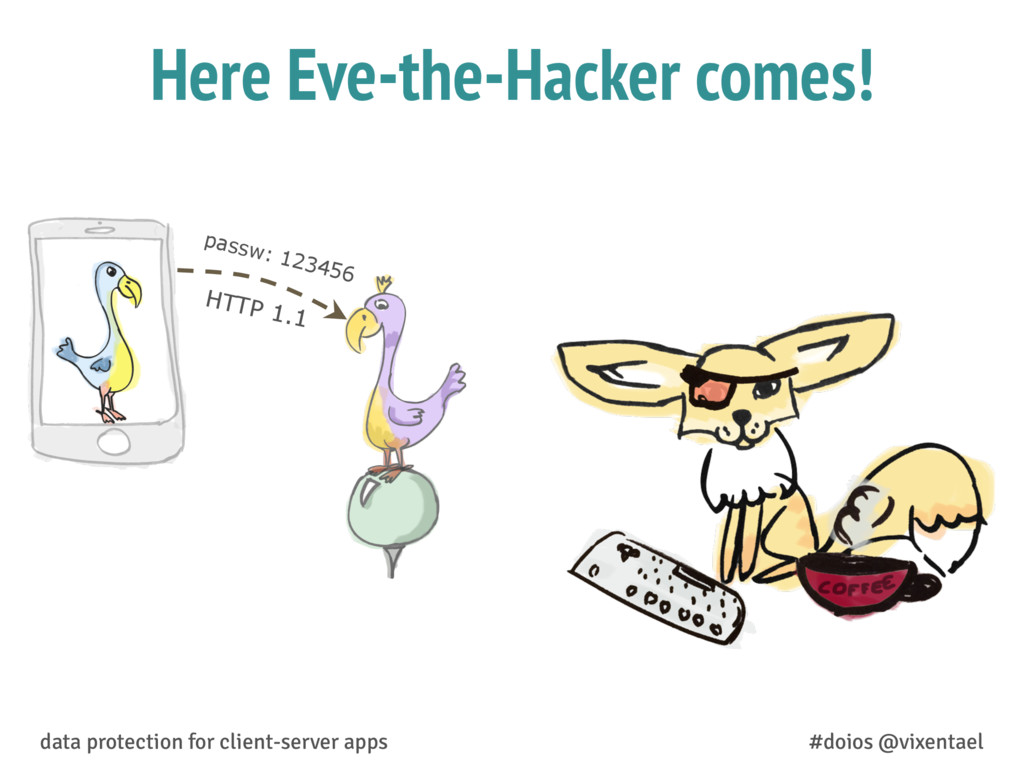
Here Eve-the-Hacker comes! passw: 123456 HTTP 1.1 data protection for
client-server apps #doios @vixentael -
Here Eve-the-Hacker comes! passw: 123456 HTTP 1.1 data protection for
client-server apps #doios @vixentael {“passw”:“123456”} -
Let’s go deeper.. To avoid threats we need secure programming
data protection for client-server apps #doios @vixentael Problem: Layer 2 -
Alice decides to implement security data protection for client-server apps
#doios @vixentael puts on paper hat! -
Bob decides to implement security builds the fence! data protection
for client-server apps #doios @vixentael -
..and they decide to use HTTPS! data protection for client-server
apps #doios @vixentael ****** : ****** HTTPS out of the box -
But it’s not really secure.. ****** : ****** HTTPS out
of the box data protection for client-server apps #doios @vixentael {“passw”:“123456”} -
Intercept traffic using proxy data protection for client-server apps #doios
@vixentael * SSL experimenting with Android Top100 apps http://bit.ly/1NqpheM * Intercepting the App Store's Traffic on iOS http://bit.ly/1H3xMrs -
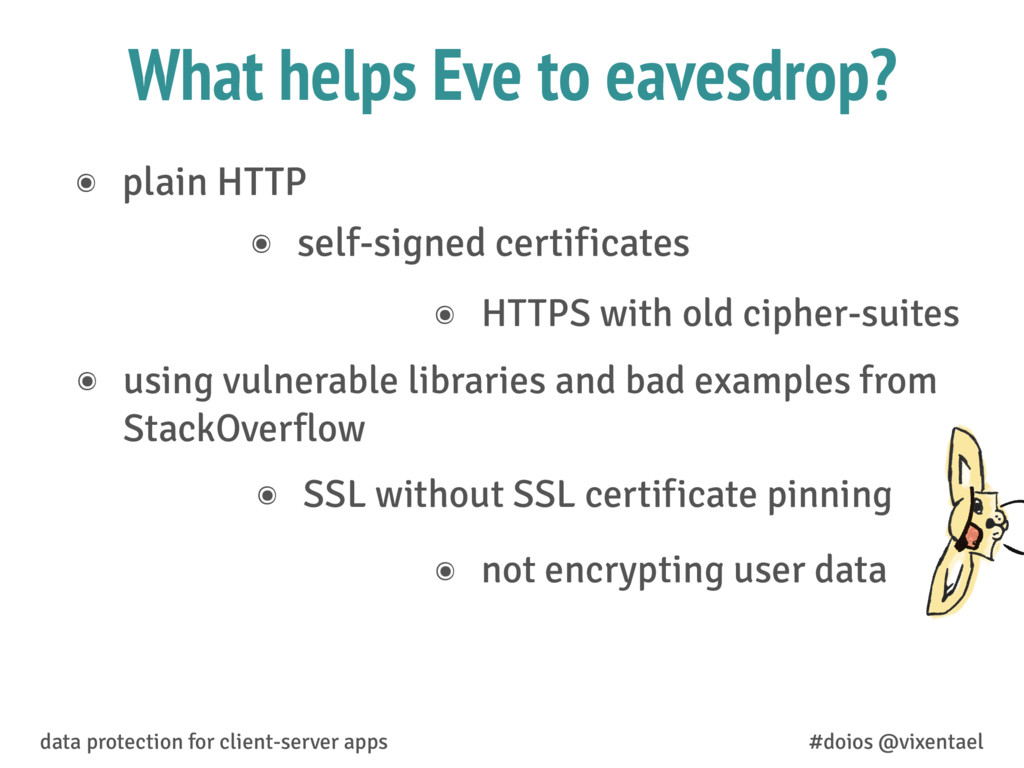
What helps Eve to eavesdrop? ๏ not encrypting user data
data protection for client-server apps #doios @vixentael ๏ plain HTTP ๏ self-signed certificates ๏ HTTPS with old cipher-suites ๏ using vulnerable libraries and bad examples from StackOverflow ๏ SSL without SSL certificate pinning -
data protection for client-server apps #doios @vixentael Problem: Layer 3
As the result, Programming is rarely secure -
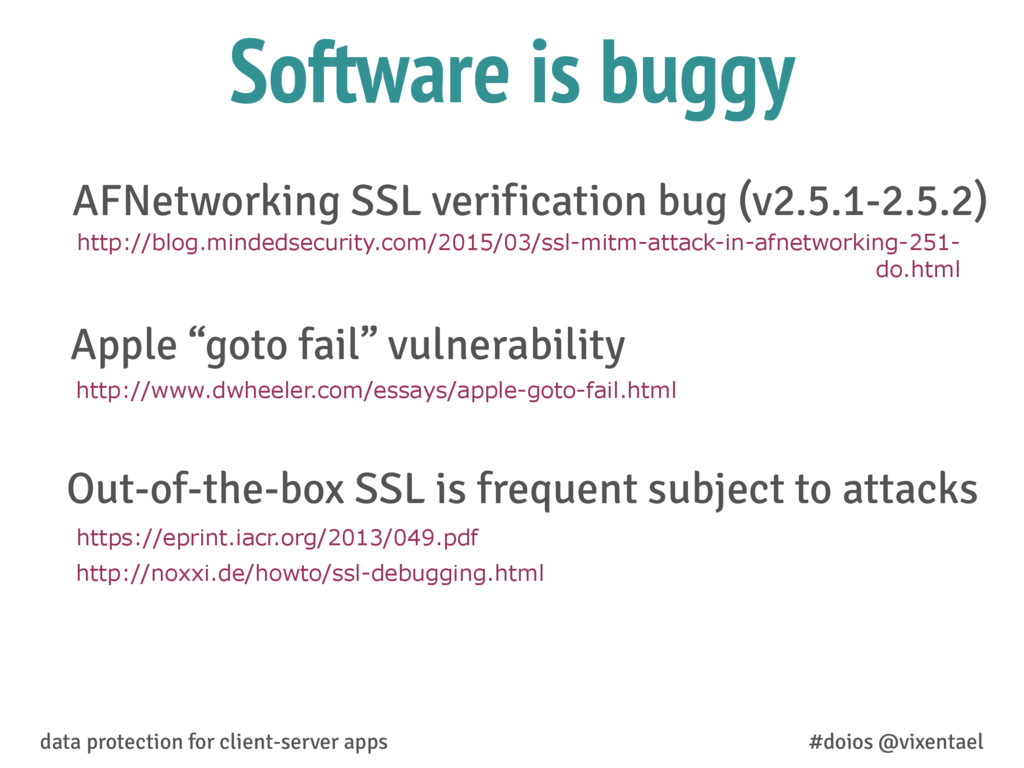
data protection for client-server apps #doios @vixentael Software is buggy
http://blog.mindedsecurity.com/2015/03/ssl-mitm-attack-in-afnetworking-251- do.html AFNetworking SSL verification bug (v2.5.1-2.5.2) https://eprint.iacr.org/2013/049.pdf Out-of-the-box SSL is frequent subject to attacks http://www.dwheeler.com/essays/apple-goto-fail.html Apple “goto fail” vulnerability http://noxxi.de/howto/ssl-debugging.html -
๏ Copying bad code from StackOverflow ๏ Debugging by tearing
security suites apart ๏ Avoiding “complicated” security documentation data protection for client-server apps #doios @vixentael Software is buggy. Why? -
- is easy to f*ck up - is inconvenient to
implement Cyber-world security -
- use good practice and brain - use good tools
- minimize re-inventing the wheel What shall we do? -
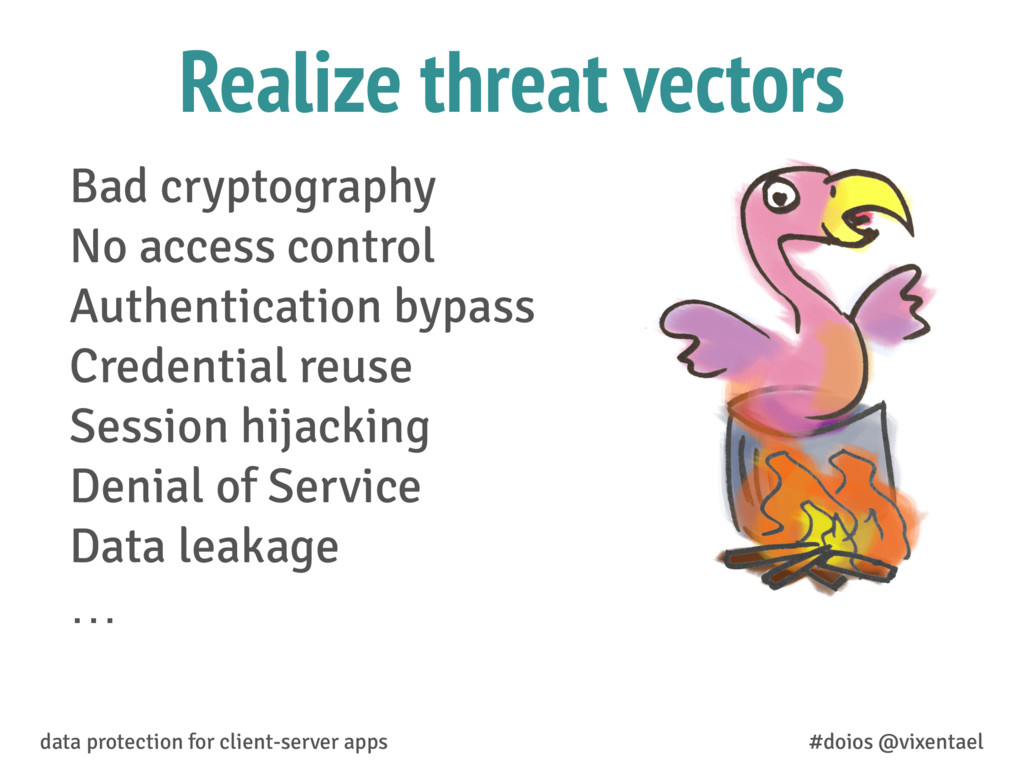
data protection for client-server apps #doios @vixentael Realize threat vectors
Bad cryptography No access control Authentication bypass Credential reuse Session hijacking Denial of Service Data leakage … -
Anyone can invent a security system that he himself cannot
break — Schneier's Law https://www.schneier.com/blog/archives/ 2011/04/schneiers_law.html data protection for client-server apps #doios @vixentael Implementing security tools yourself is a threat -
Use great tools scientific background trust big guys good track
record data protection for client-server apps #doios @vixentael libsodium/NaCL OTRKit RNCryptor MIHCrypto Themis https://github.com/mochtu/libsodium-ios https://github.com/ChatSecure/OTRKit https://github.com/RNCryptor/RNCryptor https://github.com/hohl/MIHCrypto https://github.com/cossacklabs/themis -
Do your SSL/TLS right ๏use long keys ๏disable backward compatibility
๏use strong ciphers (EC vs RSA) ๏pin SSL certificate ๏use cheat sheet https://www.cossacklabs.com/avoid-ssl-for-your- next-app.html SSL has a lot of problems To survive you need to: data protection for client-server apps #doios @vixentael https://www.owasp.org/index.php/ Transport_Layer_Protection_Cheat_Sheet -
Do you pin SSL certificate? data protection for client-server apps
#doios @vixentael -
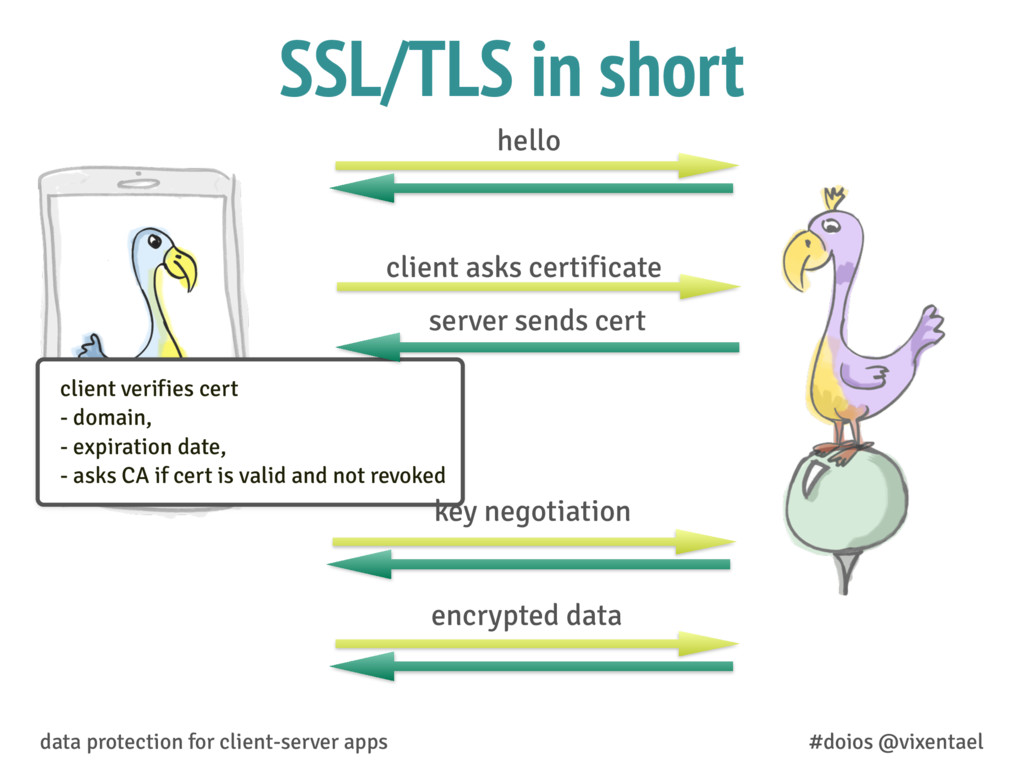
SSL/TLS in short data protection for client-server apps #doios @vixentael
hello client asks certificate server sends cert encrypted data client verifies cert - domain, - expiration date, - asks CA if cert is valid and not revoked key negotiation -
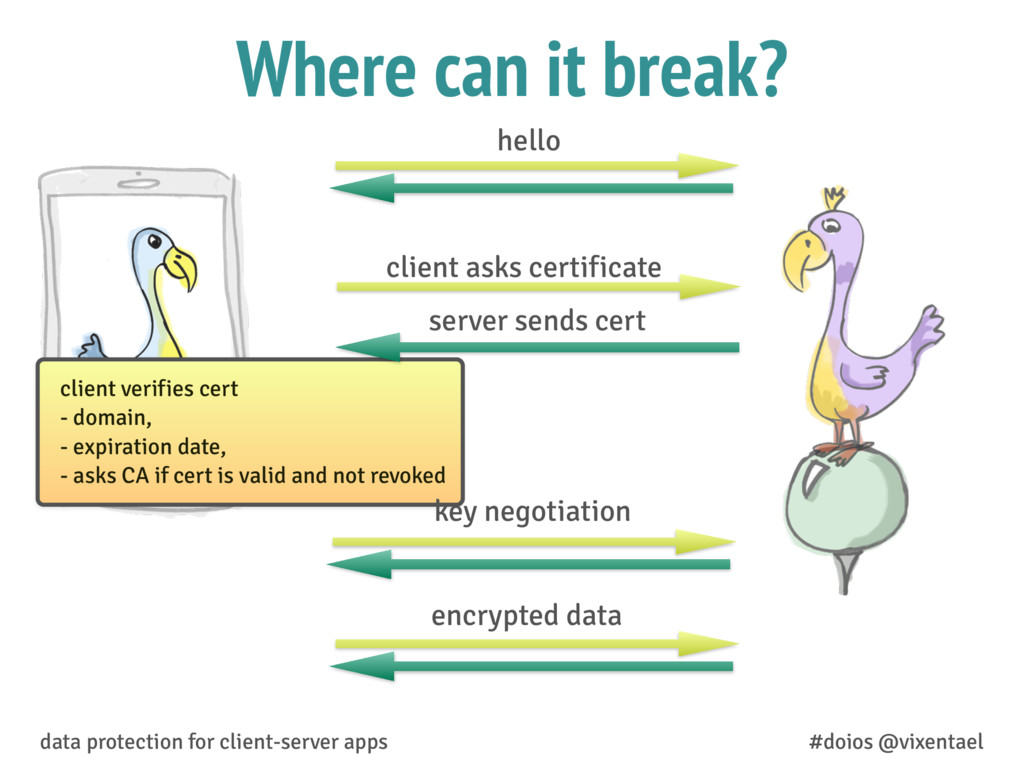
Where can it break? data protection for client-server apps #doios
@vixentael hello client asks certificate server sends cert encrypted data client verifies cert - domain, - expiration date, - asks CA if cert is valid and not revoked key negotiation -
SSL pinning data protection for client-server apps #doios @vixentael hello
client asks certificate server sends cert encrypted data client verifies cert - compares cert against pinned cert key negotiation -
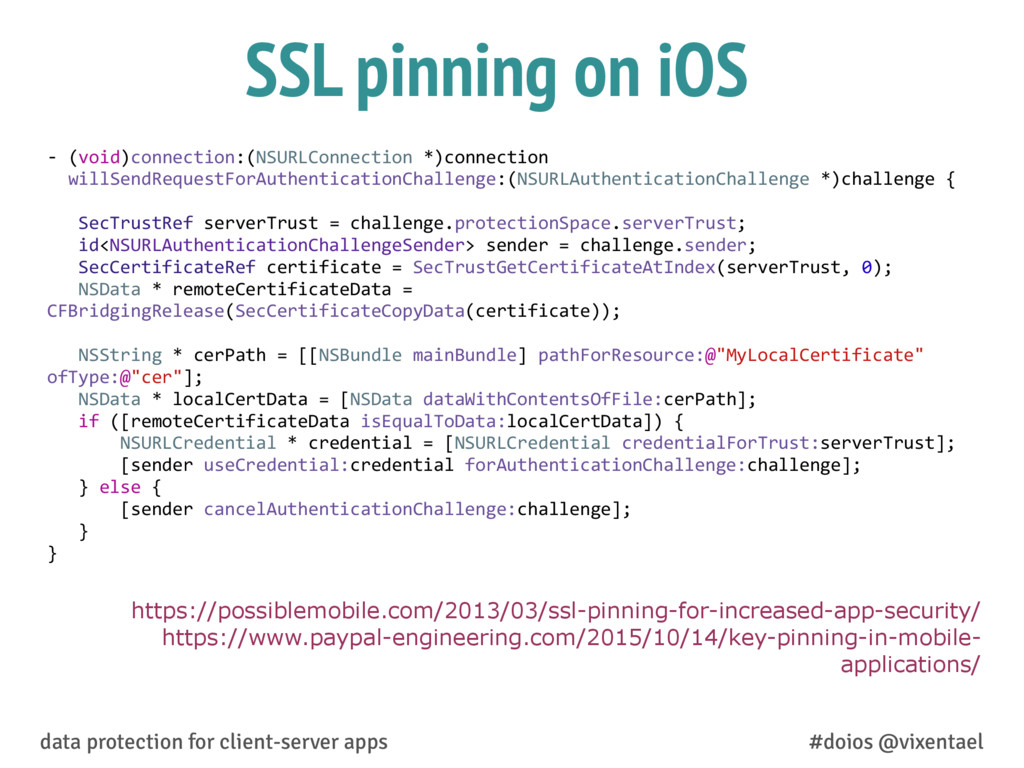
SSL pinning on iOS https://possiblemobile.com/2013/03/ssl-pinning-for-increased-app-security/ https://www.paypal-engineering.com/2015/10/14/key-pinning-in-mobile- applications/ -‐ (void)connection:(NSURLConnection *)connection
willSendRequestForAuthenticationChallenge:(NSURLAuthenticationChallenge *)challenge { SecTrustRef serverTrust = challenge.protectionSpace.serverTrust; id<NSURLAuthenticationChallengeSender> sender = challenge.sender; SecCertificateRef certificate = SecTrustGetCertificateAtIndex(serverTrust, 0); NSData * remoteCertificateData = CFBridgingRelease(SecCertificateCopyData(certificate)); NSString * cerPath = [[NSBundle mainBundle] pathForResource:@"MyLocalCertificate" ofType:@"cer"]; NSData * localCertData = [NSData dataWithContentsOfFile:cerPath]; if ([remoteCertificateData isEqualToData:localCertData]) { NSURLCredential * credential = [NSURLCredential credentialForTrust:serverTrust]; [sender useCredential:credential forAuthenticationChallenge:challenge]; } else { [sender cancelAuthenticationChallenge:challenge]; } } data protection for client-server apps #doios @vixentael -
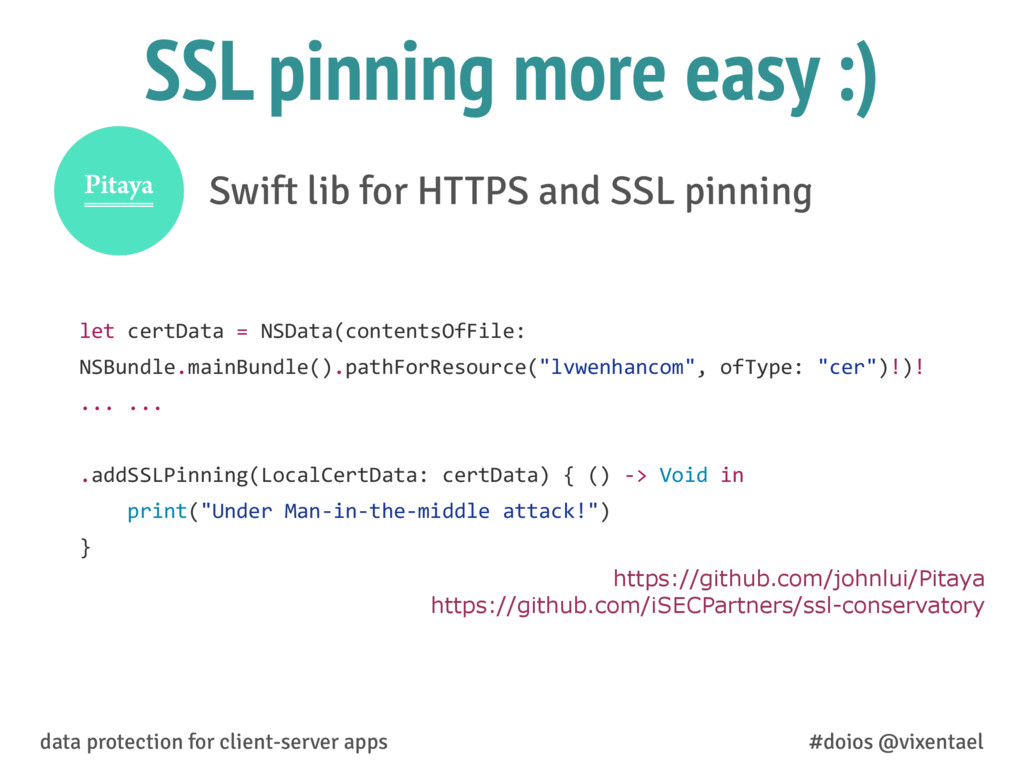
SSL pinning more easy :) let certData = NSData(contentsOfFile:
NSBundle.mainBundle().pathForResource("lvwenhancom", ofType: "cer")!)! ... ... .addSSLPinning(LocalCertData: certData) { () -‐> Void in print("Under Man-‐in-‐the-‐middle attack!") } data protection for client-server apps #doios @vixentael Swift lib for HTTPS and SSL pinning https://github.com/johnlui/Pitaya https://github.com/iSECPartners/ssl-conservatory -
Forward Secrecy: Threat Eve records encrypted traffic New crypto vulnerability
allows to exact keys Eve physically extracts keys from one of the birds Eve decrypts all encrypted traffic data protection for client-server apps #doios @vixentael -
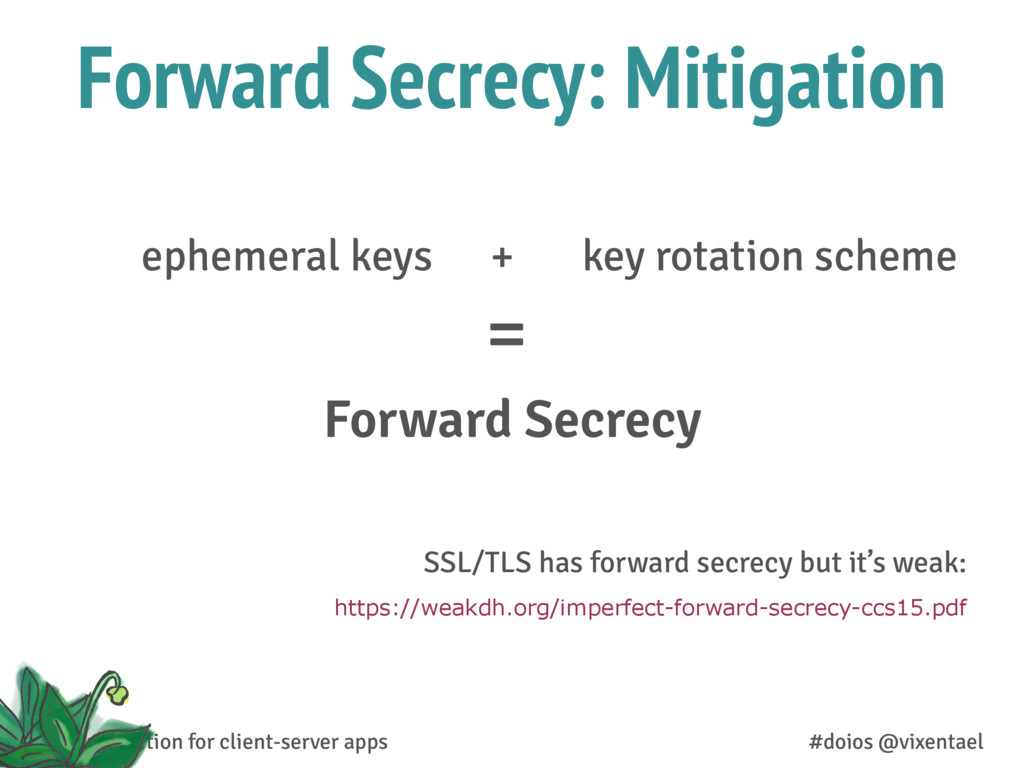
Forward Secrecy: Mitigation Forward Secrecy ephemeral keys + key rotation
scheme data protection for client-server apps #doios @vixentael https://weakdh.org/imperfect-forward-secrecy-ccs15.pdf SSL/TLS has forward secrecy but it’s weak: = -
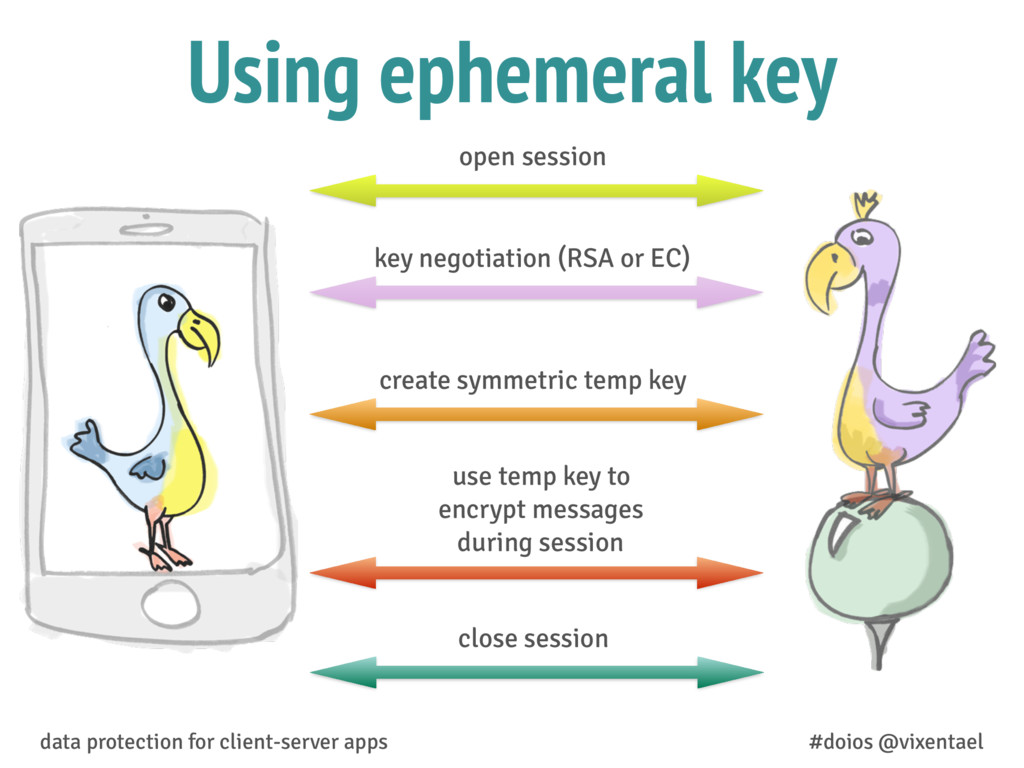
Using ephemeral key data protection for client-server apps #doios @vixentael
key negotiation (RSA or EC) create symmetric temp key use temp key to encrypt messages during session close session open session -
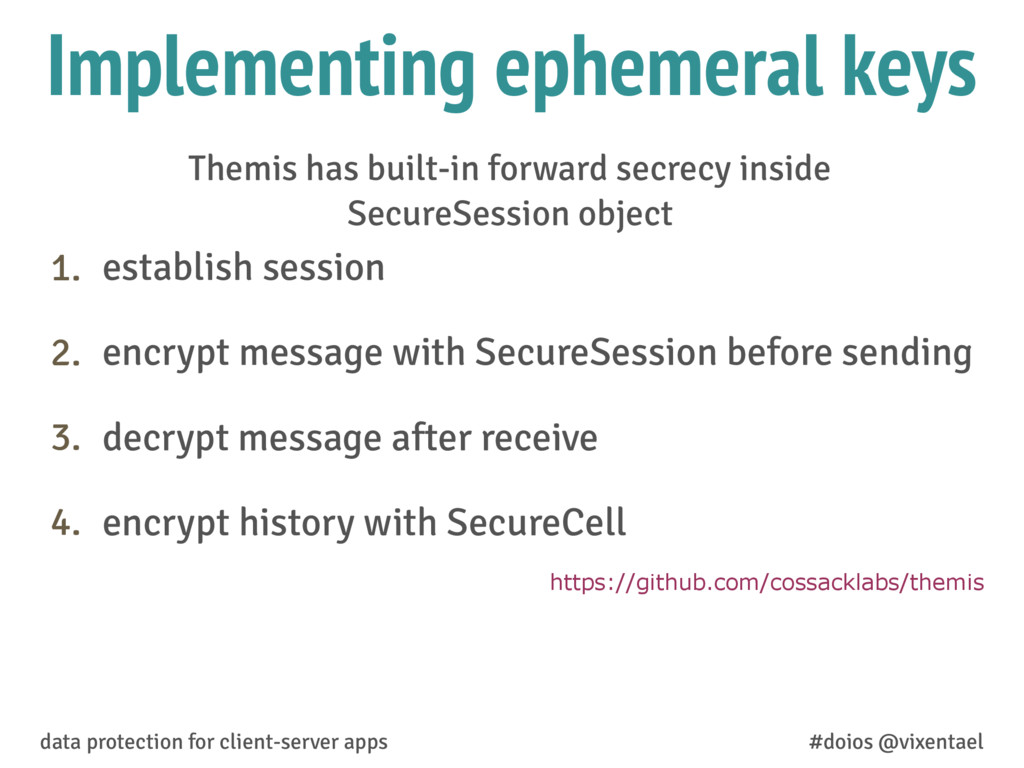
Implementing ephemeral keys 1. establish session 2. encrypt message with
SecureSession before sending 3. decrypt message after receive 4. encrypt history with SecureCell data protection for client-server apps #doios @vixentael https://github.com/cossacklabs/themis Themis has built-in forward secrecy inside SecureSession object -
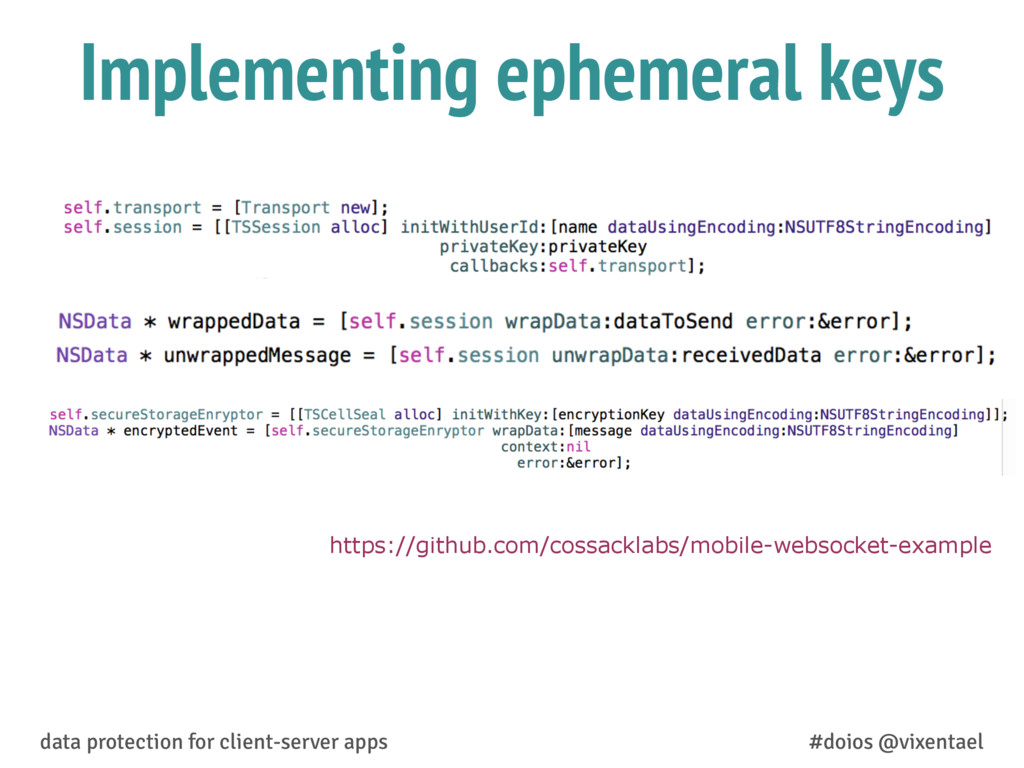
Implementing ephemeral keys data protection for client-server apps #doios @vixentael
https://github.com/cossacklabs/mobile-websocket-example -
What we need to do 1. Choose good storage library
with efficient crypto 2. Embed it on read/write 3. Store keys safely data protection for client-server apps #doios @vixentael -
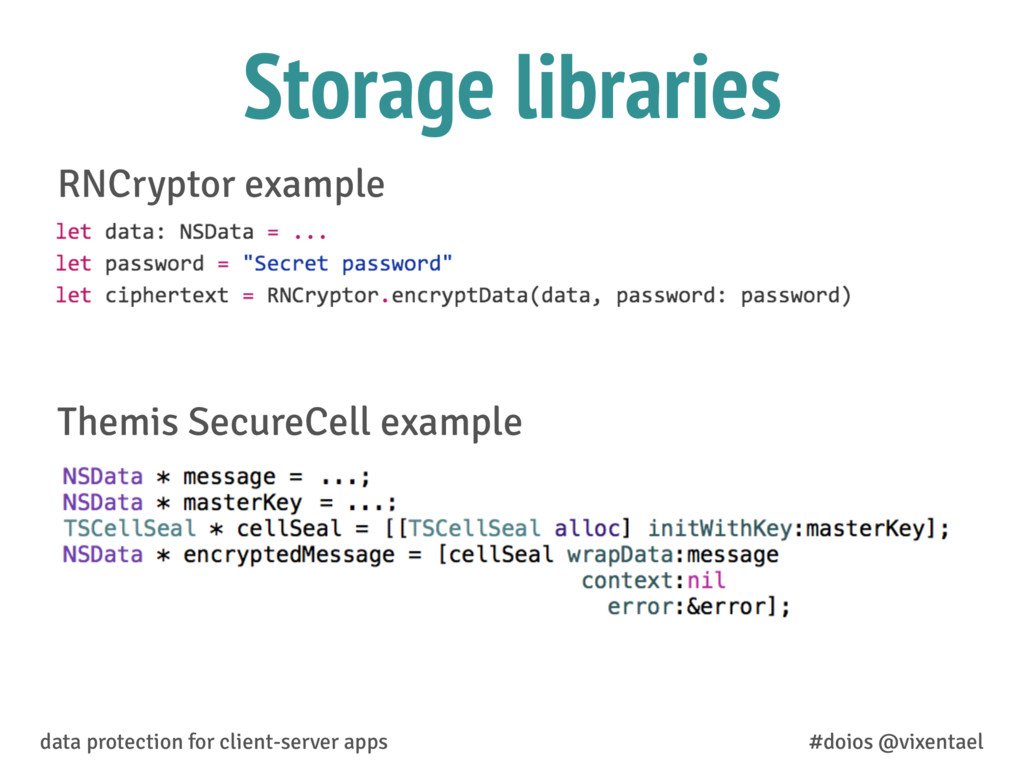
RNCryptor example Themis SecureCell example data protection for client-server apps
#doios @vixentael Storage libraries -
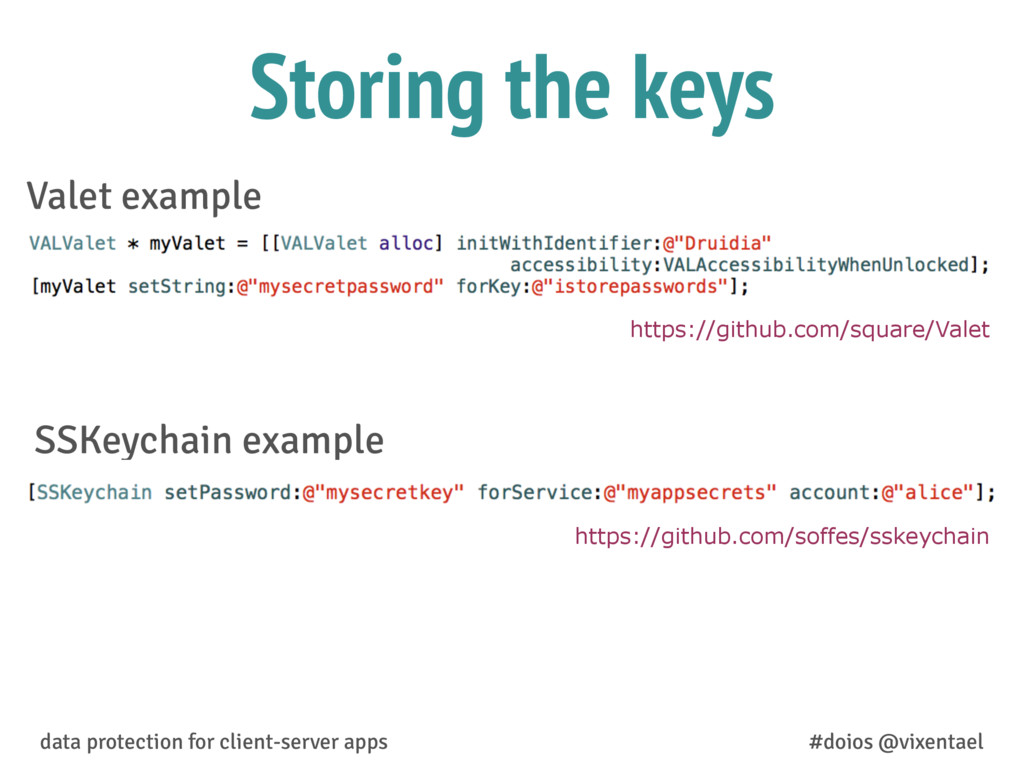
data protection for client-server apps #doios @vixentael Storing the keys
SSKeychain example Valet example https://github.com/square/Valet https://github.com/soffes/sskeychain -
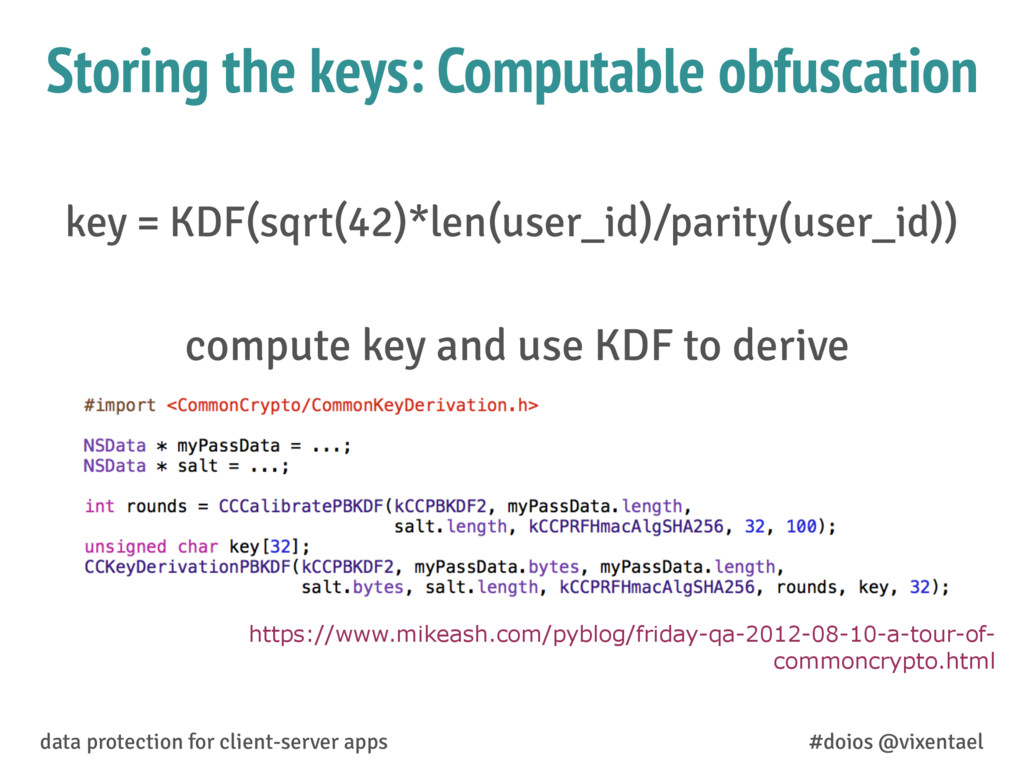
compute key and use KDF to derive data protection for
client-server apps #doios @vixentael Storing the keys: Computable obfuscation https://www.mikeash.com/pyblog/friday-qa-2012-08-10-a-tour-of- commoncrypto.html key = KDF(sqrt(42)*len(user_id)/parity(user_id)) -
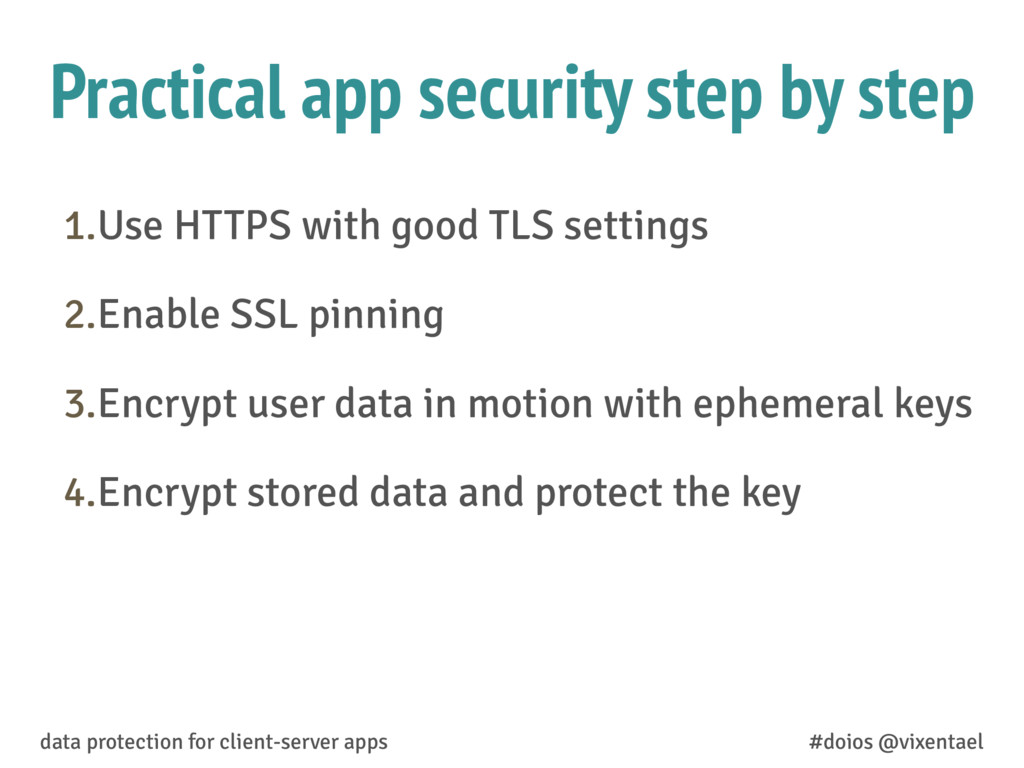
Practical app security step by step 1.Use HTTPS with good
TLS settings 2.Enable SSL pinning 3.Encrypt user data in motion with ephemeral keys 4.Encrypt stored data and protect the key data protection for client-server apps #doios @vixentael -
Alice is more secure now data protection for client-server apps
#doios @vixentael SSL pinning encrypted storage data ephemeral keys -
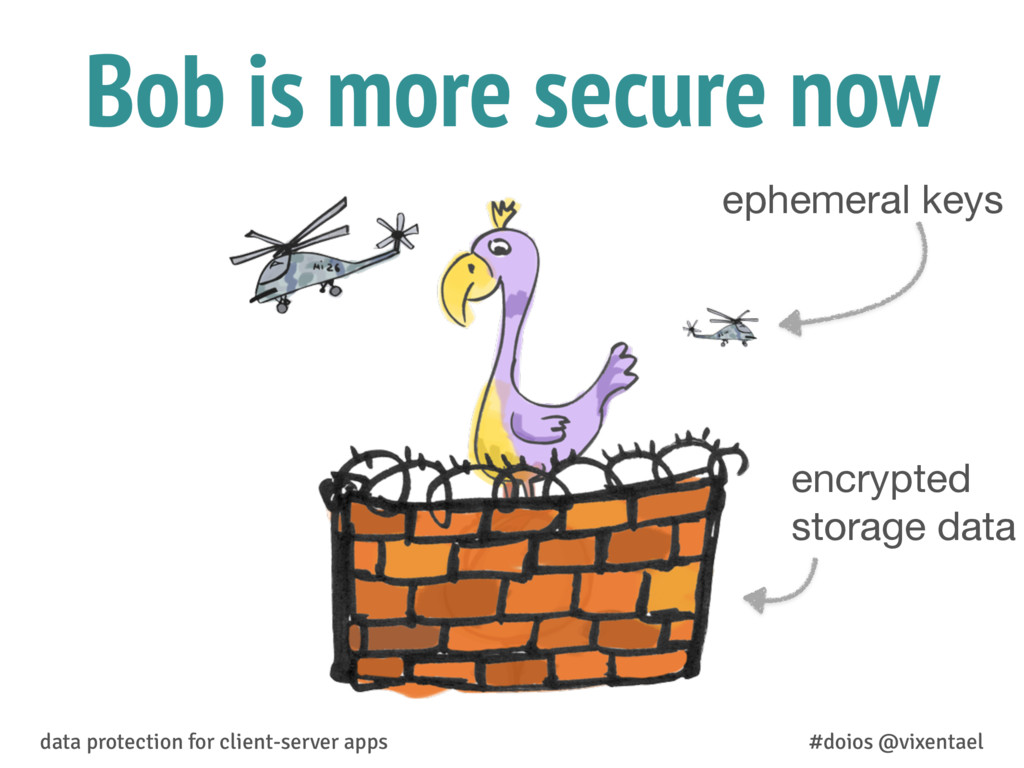
Bob is more secure now data protection for client-server apps
#doios @vixentael encrypted storage data ephemeral keys -
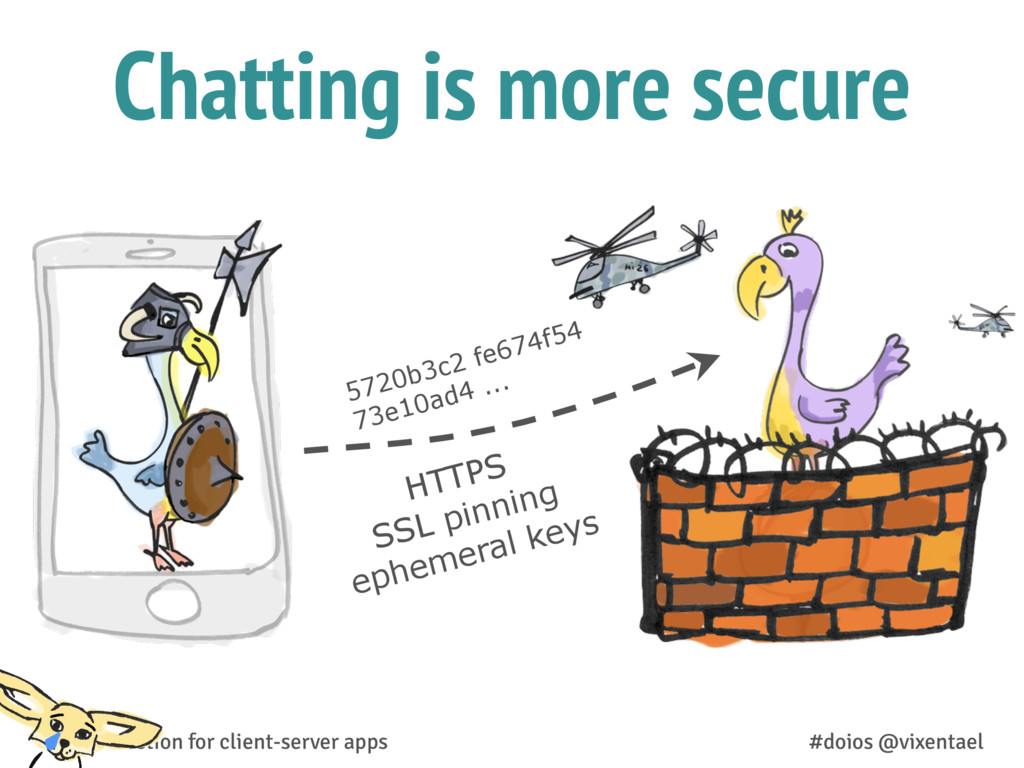
Chatting is more secure 5720b3c2 fe674f54 73e10ad4 ... HTTPS SSL
pinning ephemeral keys data protection for client-server apps #doios @vixentael -
Security is full of adventures and discoveries. And fun. and
shiny metal birds! -
The last slide @vixentael iOS developer at stanfy.com [creating awesome
mobile and IoT apps] data protection for client-server apps #doios @vixentael take care! -
More to read ★ The Mobile Application Hacker's Handbook https://books.google.com.ua/books?id=UgVhBgAAQBAJ
★ Designing Secure User Interfaces https://developer.apple.com/library/ios/documentation/Security/ Conceptual/SecureCodingGuide/Articles/AppInterfaces.html#//apple_ref/ doc/uid/TP40002862-SW1 ★ CryptoCat iOS app security audit https://nabla-c0d3.github.io/documents/iSEC_Cryptocat_iOS.pdf ★ Storing secret keys http://www.splinter.com.au/2014/09/16/storing-secret-keys/ -
More to watch ★ All talks of Moxie Marlinspike https://www.youtube.com/watch?v=ibF36Yyeehw
https://www.youtube.com/watch?v=8N4sb-SEpcg https://www.youtube.com/watch?v=tOMiAeRwpPA