Share
Embed
The nightmare behind the cross platform mobile apps dream
Black Hat Asia 15

Marco Grassi
March 27, 2015
Transcript
67 slides
-
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style The nightmare behind the cross platform mobile apps dream Marco Grassi @marcograss [email protected] Sebastián Guerrero @0xroot [email protected] -
Agenda •Background introduction •What Cross-‐platform Frameworks are out there?
•Concerns •The uniform attack surface •Code formats and code retrieval •Runtime manipulation and dynamic analysis •Some examples of vulnerabilities in the frameworks •Conclusions -
Who are we? Marco Grassi Mobile Security Researcher
NowSecure Sebas Guerrero Mobile Security Researcher NowSecure -
Warning! Part of those slides were made while drinking alcohol
in international flights! -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Background intro -
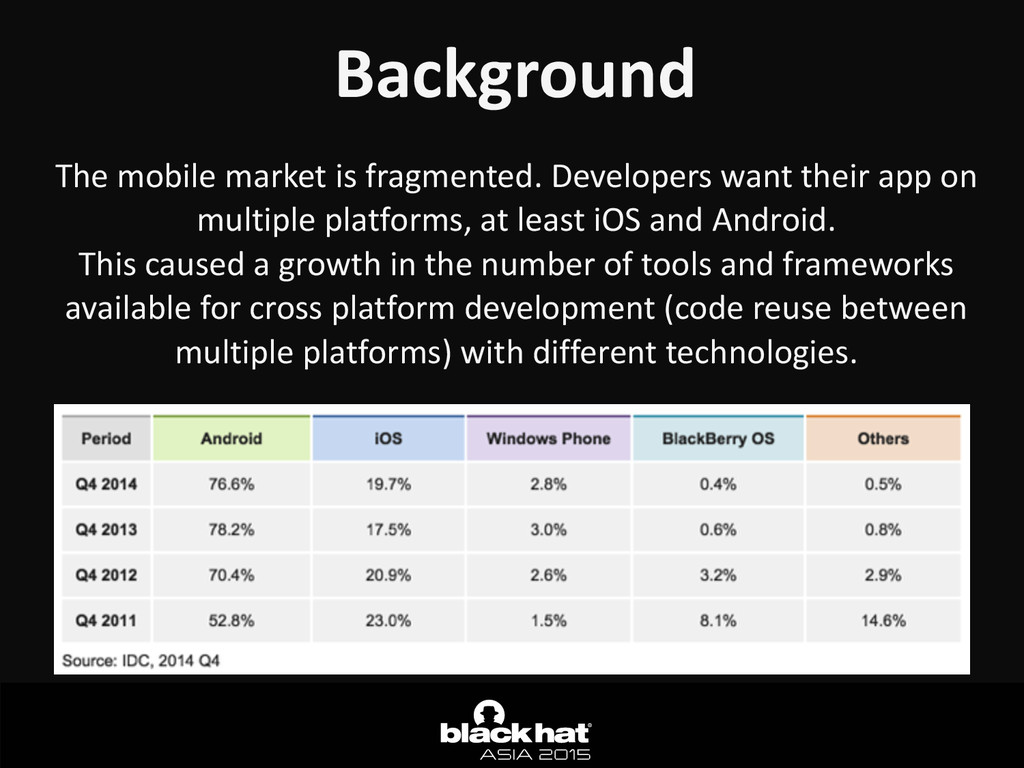
Background The mobile market is fragmented. Developers want their app
on multiple platforms, at least iOS and Android. This caused a growth in the number of tools and frameworks available for cross platform development (code reuse between multiple platforms) with different technologies. -
Background Those frameworks usually achieve code portability by leveraging
HTML5 technology or interpreters with bindings on the native code platform, to expose the API of the underlying system in a way as platform independent as possible. The result is that lot of code, if not all, can be reused. -
Background So far everything seems great, we can code once
and run in every platform! But how is the quality of the code of these frameworks? Do they introduce security vulnerabilities if we use them? Are those vulnerabilities shared by all the applications using the same framework? -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style What Cross-‐platform Frameworks Are Out There? -
Cordova / PhoneGap •Mobile development framework to write Mobile
applications using web technologies such as HTML5, Javascript and CSS3. •Cordova is the Opensource core, PhoneGap is owned by Adobe which leverages Cordova. •Cordova leverages a “bridge” between javascript and native code, to invoke native methods from javascript code. •OpenSource -‐ https://cordova.apache.org/ -
Cordova / PhoneGap •Some history of known vulnerabilities and CVEs
•Great job by David Kaplan and Roee Hay of IBM Security Systems •CVE-‐2014-‐3500, CVE-‐2014-‐3501, CVE-‐2014-‐3502, all related to Android Intents somehow “mistrusted” leading to XAS, bypasses and leak of data. -
•Cross platform game creation system, including the major mobile
platforms. •You can develop the game with Mono, so in .NET •http://unity3d.com/ -
Adobe AIR •Very popular cross platform runtime, not only on
mobile but also on desktop. Used both in apps and games. •You can develop your project with Adobe Flash or ActionScript. -
Adobe AIR •Lot of CVE, maybe mainly because they are
shared with Adobe Flash Player for Desktop browsers •In this context (cross platform application), those vulns are less relevant because you don’t run remote/untrusted code like in the browser, you just execute code shipped within your application. (if you don’t do strange things) -
Titanium Appcelerator •Open source -‐ http://www.appcelerator.com/ •You can develop
your native mobile application in javascript •The javascript runs on a interpreter and uses native UI and functionalities •The IDE is Eclipse based -
•SDK to develop 2d games and apps •You
write Lua code using bindings to C++ and OpenGL -
Kony Framework •Platform to develop cross platform applications. •Native
Mobile Applications can be written in Lua or Javascript. -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Concerns -
Concerns •Code reuse implies uniform attack surface between apps
using the same framework. •Vulnerabilities and attacks can be reused among different apps. •The code is stored in high level languages or byte code. This makes reverse engineering process easier or non-‐existent as we will see soon. -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Code Format: Some Examples On How To Retrieve The Code -
With great portability… … often comes great meta
datas and easy reverse engineering. -
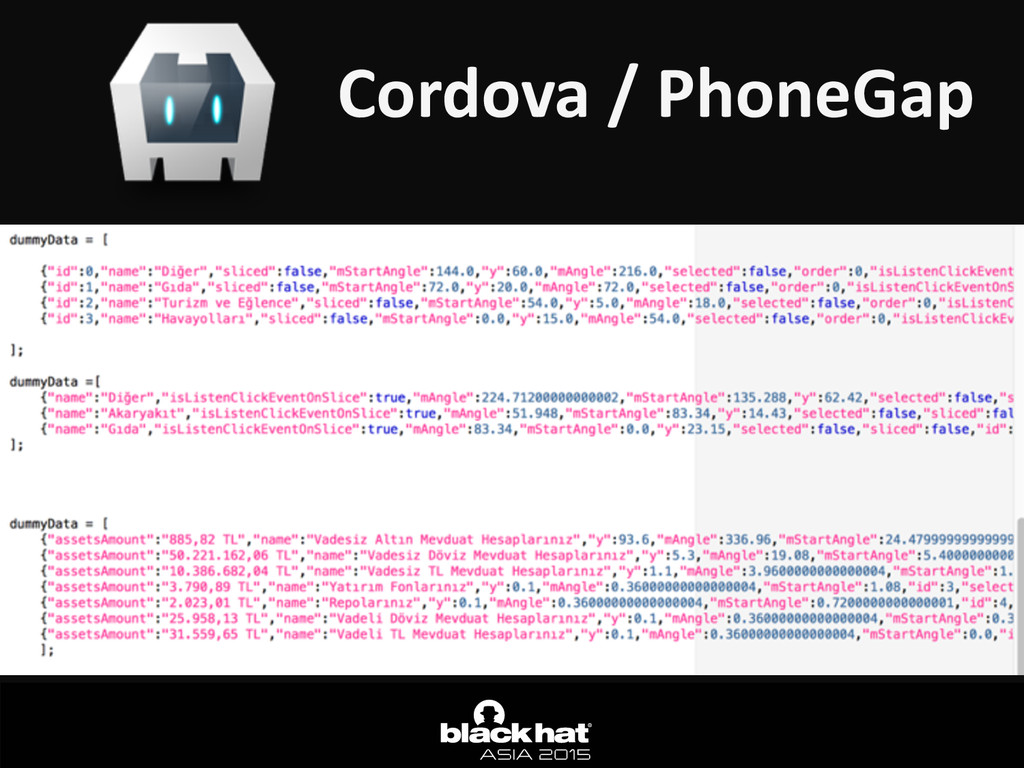
Cordova / PhoneGap •Almost all the code is written in
javascript, the UI is developed in HTML5 and CSS3. •The code by default it’s just bundled in plain text inside of the mobile app, so retrieving it and reversing is trivial -
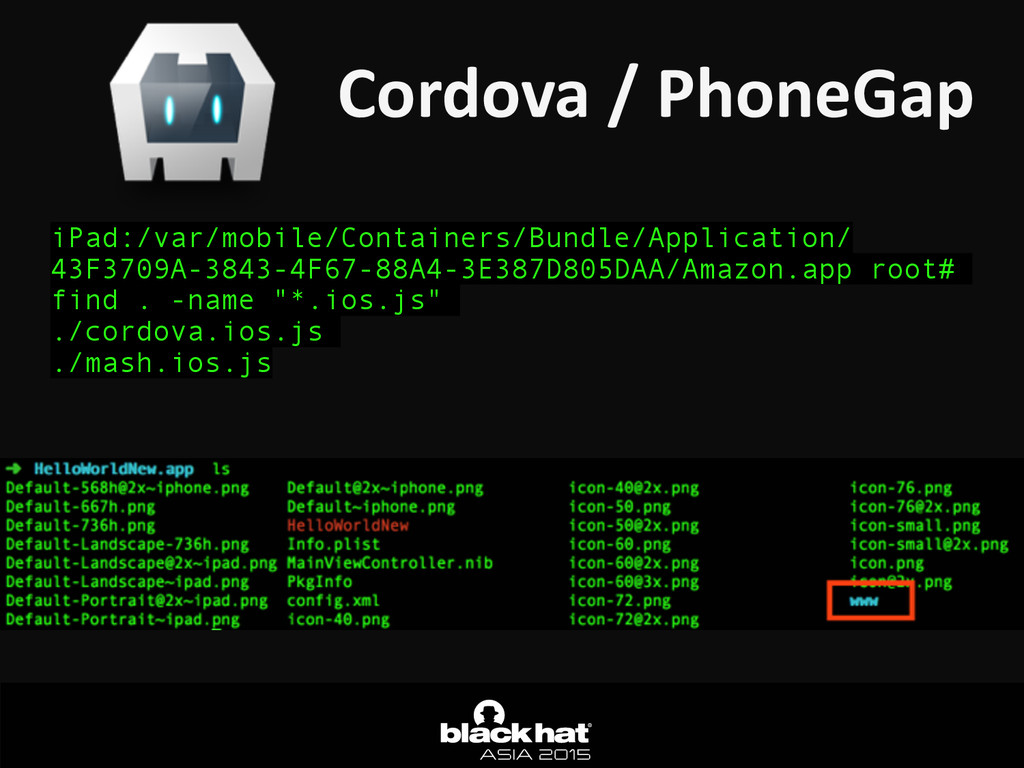
Cordova / PhoneGap •On iOS the Cordova code is bundled
as a resources, or in a www/ subfolder of the app bundle •On Android it’s usually bundled in the assets/ folder of the apk -
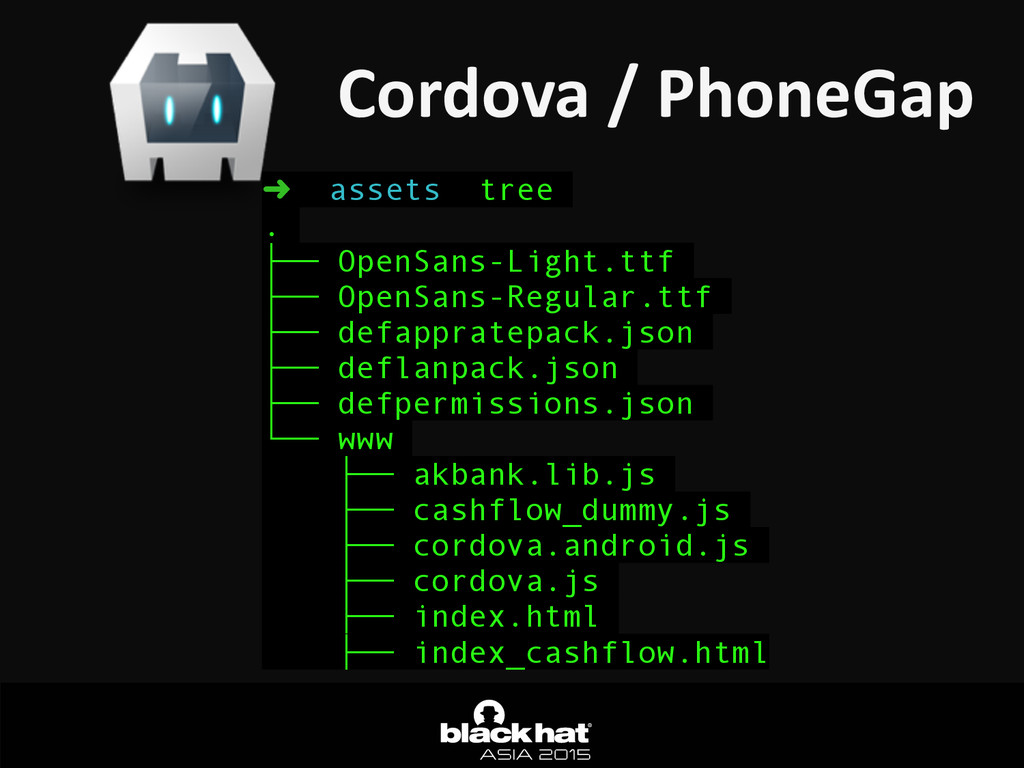
Cordova / PhoneGap ➜ assets tree . ├── OpenSans-Light.ttf ├──
OpenSans-Regular.ttf ├── defappratepack.json ├── deflanpack.json ├── defpermissions.json └── www ├── akbank.lib.js ├── cashflow_dummy.js ├── cordova.android.js ├── cordova.js ├── index.html ├── index_cashflow.html -
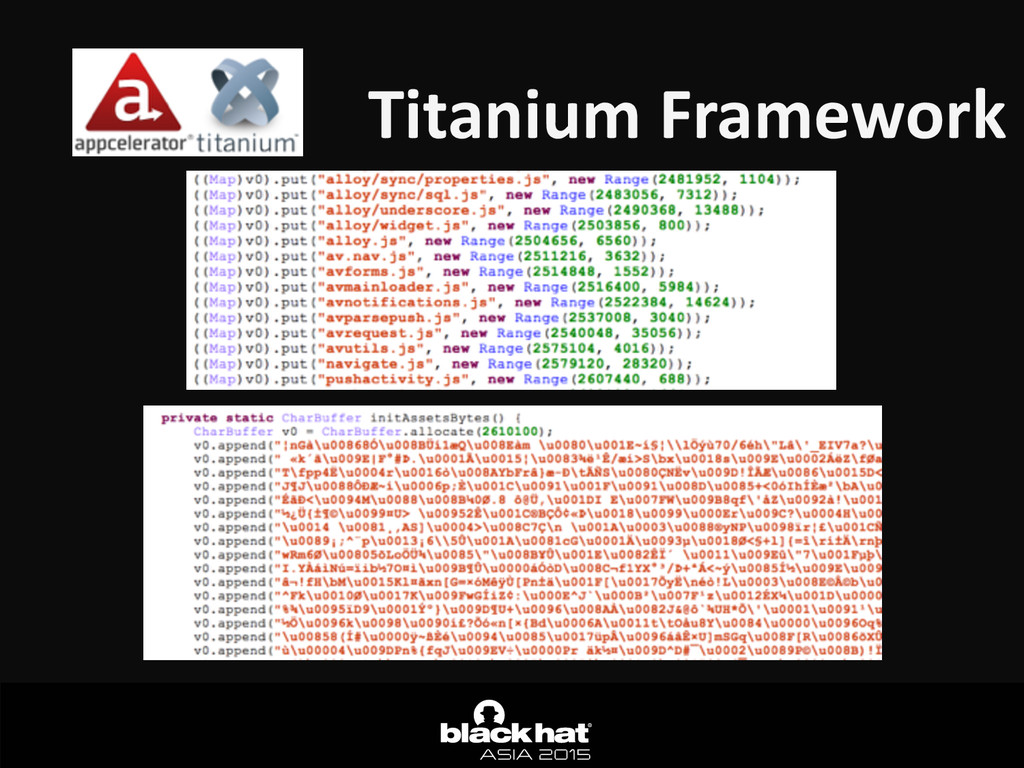
Titanium Framework •Real code is written in JavaScript. •Load
asset data at runtime through the AssetCryptImpl class. •Assets range are defined in a HashMap within the initAssets class. •Assets bytes are contained in a CharBuffer defined in the initAssetsBytes. -
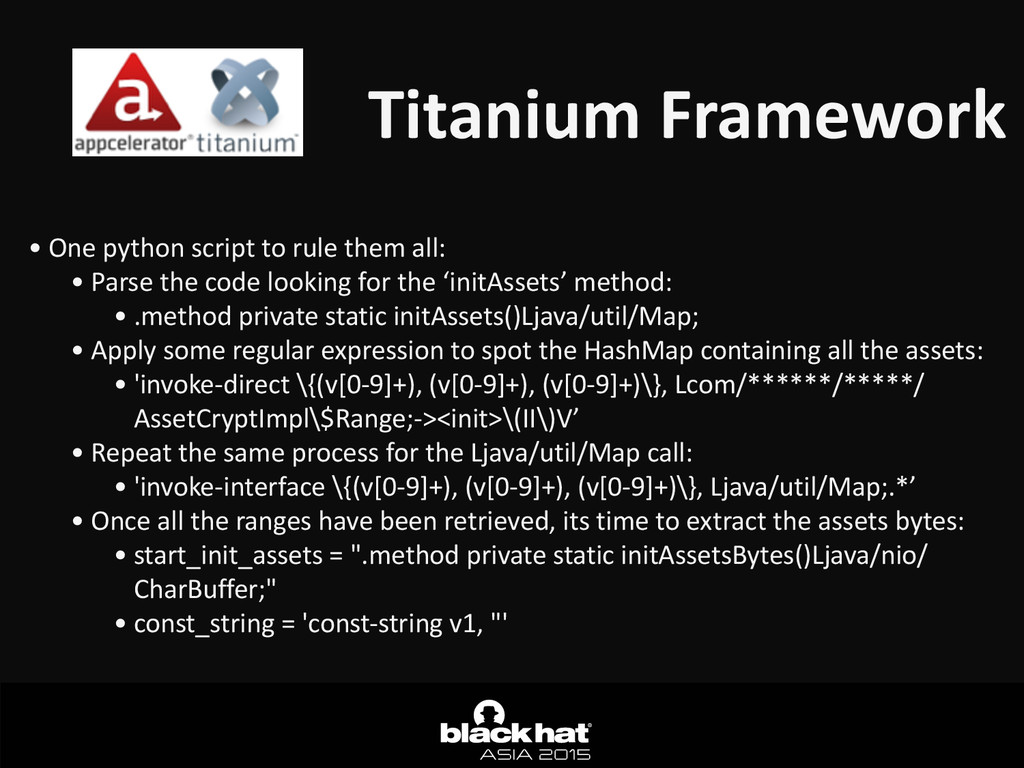
Titanium Framework • One python script to rule them all:
• Parse the code looking for the ‘initAssets’ method: • .method private static initAssets()Ljava/util/Map; • Apply some regular expression to spot the HashMap containing all the assets: • 'invoke-‐direct \{(v[0-‐9]+), (v[0-‐9]+), (v[0-‐9]+)\}, Lcom/******/*****/ AssetCryptImpl\$Range;-‐><init>\(II\)V’ • Repeat the same process for the Ljava/util/Map call: • 'invoke-‐interface \{(v[0-‐9]+), (v[0-‐9]+), (v[0-‐9]+)\}, Ljava/util/Map;.*’ • Once all the ranges have been retrieved, its time to extract the assets bytes: • start_init_assets = ".method private static initAssetsBytes()Ljava/nio/ CharBuffer;" • const_string = 'const-‐string v1, "' -
Titanium Framework • But the assets are encrypted… NO PROBLEM,
DO YOU EVEN REVERSE ENGINEERING, BRO?!? • The crypto is described in the JNI function ‘Java_org_appcelerator_titanium_TiVerify_filterDataInRange’ in ‘libtiverify.so’ byte[] filterDataInRange(byte[] bytes, int offset, int count) { SecretKeySpec key = new SecretKeySpec(bytes, bytes.length -‐ 0x10, 0x10, "AES"); Cipher cipher = Cipher.getInstance("AES"); cipher.init(Cipher.DECRYPT_MODE, key); return cipher.doFinal(bytes, offset, count); } -
Titanium Framework •Yeah, OK, enough theory, show me some real
sh*t. [+] Extracting "xxx/ui/checkDeposit/DepositLandingPage.js" [+] Extracting "xxx/ui/transfers/TransferApprovedPage.js" [+] Extracting “shared/xxx/gbapi/checkDepositHistoryResponse.js" … ./xxx/modules: total 40 -‐rw-‐r-‐-‐r-‐-‐ 1 sebas staff 1560 Mar 9 03:09 BalanceHelper.js -‐rw-‐r-‐-‐r-‐-‐ 1 sebas staff 1618 Mar 9 03:09 StepUpServiceWrapper.js -‐rw-‐r-‐-‐r-‐-‐ 1 sebas staff 5675 Mar 9 03:09 UserContext.js -‐rw-‐r-‐-‐r-‐-‐ 1 sebas staff 1703 Mar 9 03:09 events.mod.js -
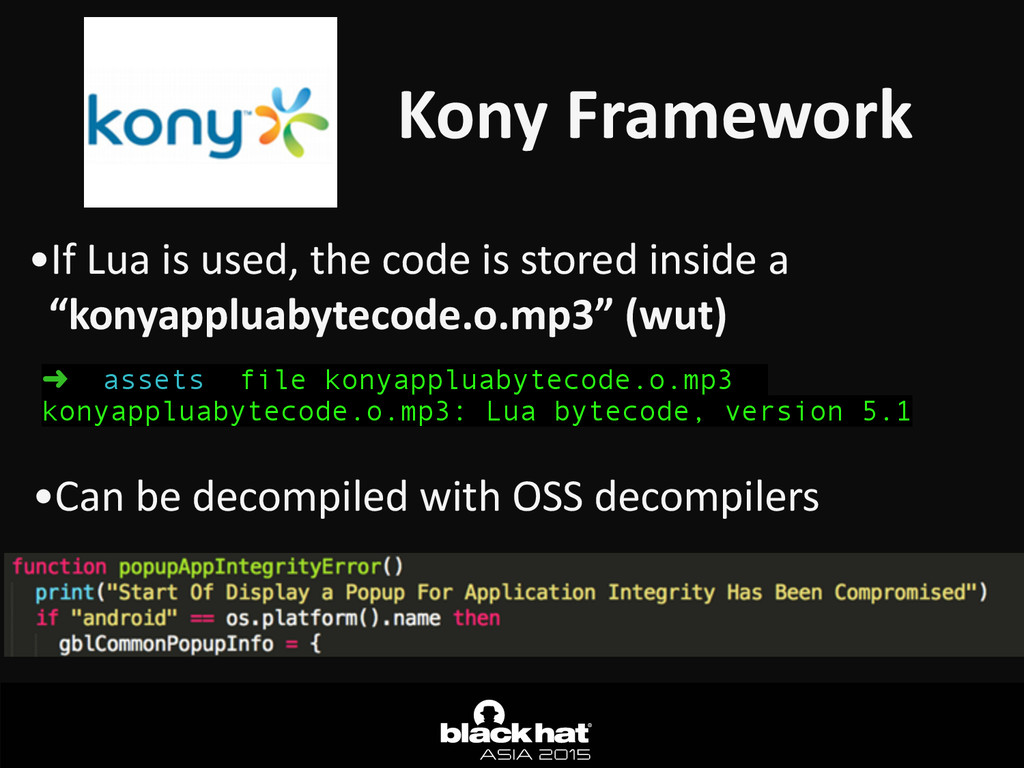
•If Lua is used, the code is stored inside a
“konyappluabytecode.o.mp3” (wut) Kony Framework ➜ assets file konyappluabytecode.o.mp3 konyappluabytecode.o.mp3: Lua bytecode, version 5.1 •Can be decompiled with OSS decompilers -
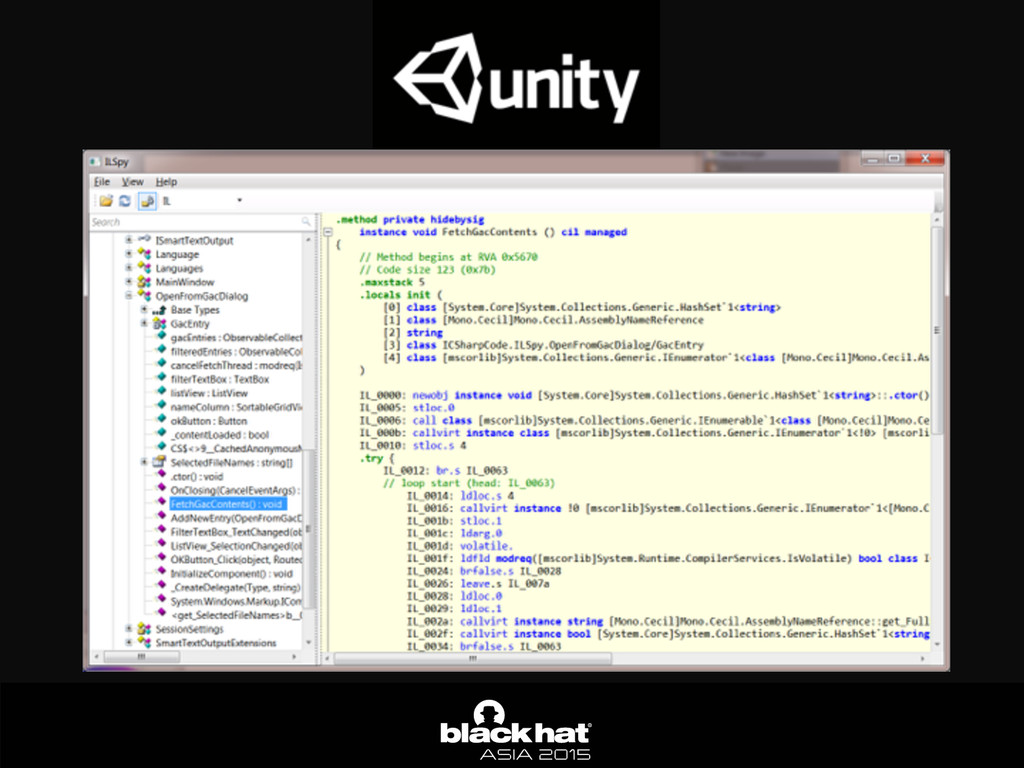
•.NET code, trivial to reverse if not obfuscated, lot
of good quality decompilers out there, like ILSPY. •You can find the code in the assets/ folder in Android for example. -
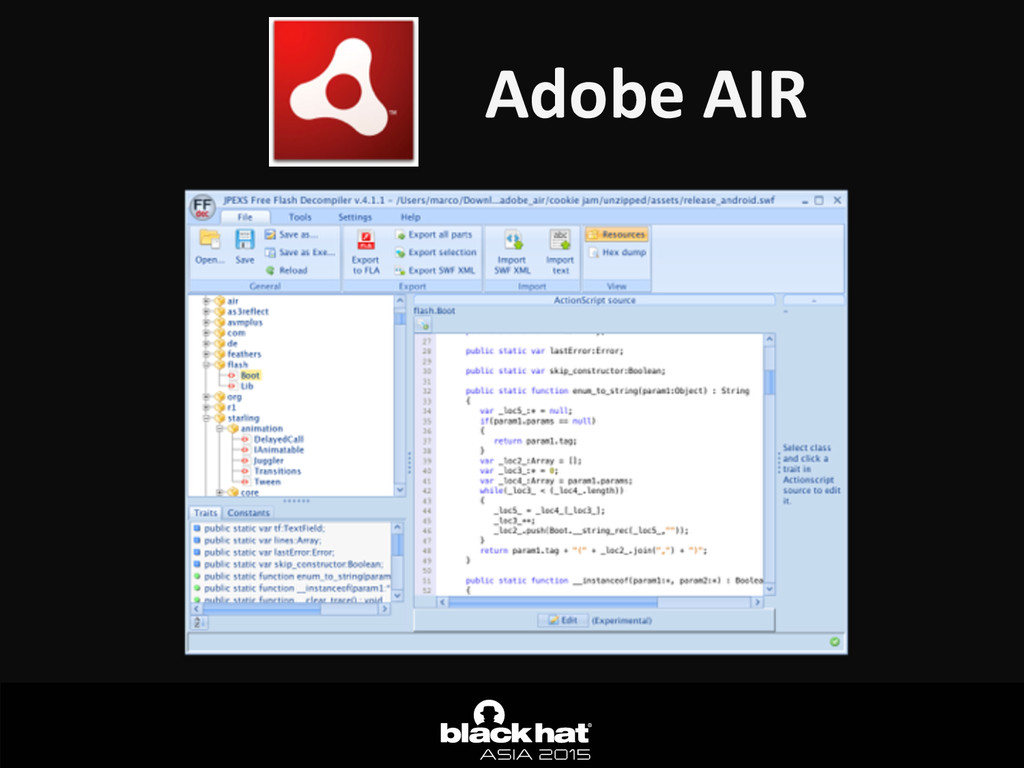
Adobe AIR •You can find the .swf file in the
assets/ folder on Android •Trivial to reverse if not obfuscated, some decompilers available -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Enough with static analysis attacks.. What about dynamic? Runtime Manipulation -
Runtime attacks, leveraging the shared codebase •Like we said
before, apps using those frameworks share most of the code. •This fact comes handy also for runtime attacks. We can deploy a runtime attack and use it against all applications that leverage the same framework with little or without any change! -
Can I have it for free Adobe? In App
items for free! 1. Reverse engineer the Adobe AIR code 2. Spot implementation of in app purchases on Android 3. Verify it’s shared between multiple apps 4. Develop a runtime attack to make the purchases appear legitimate when they are not 5. ??? 6. PROFIT! -
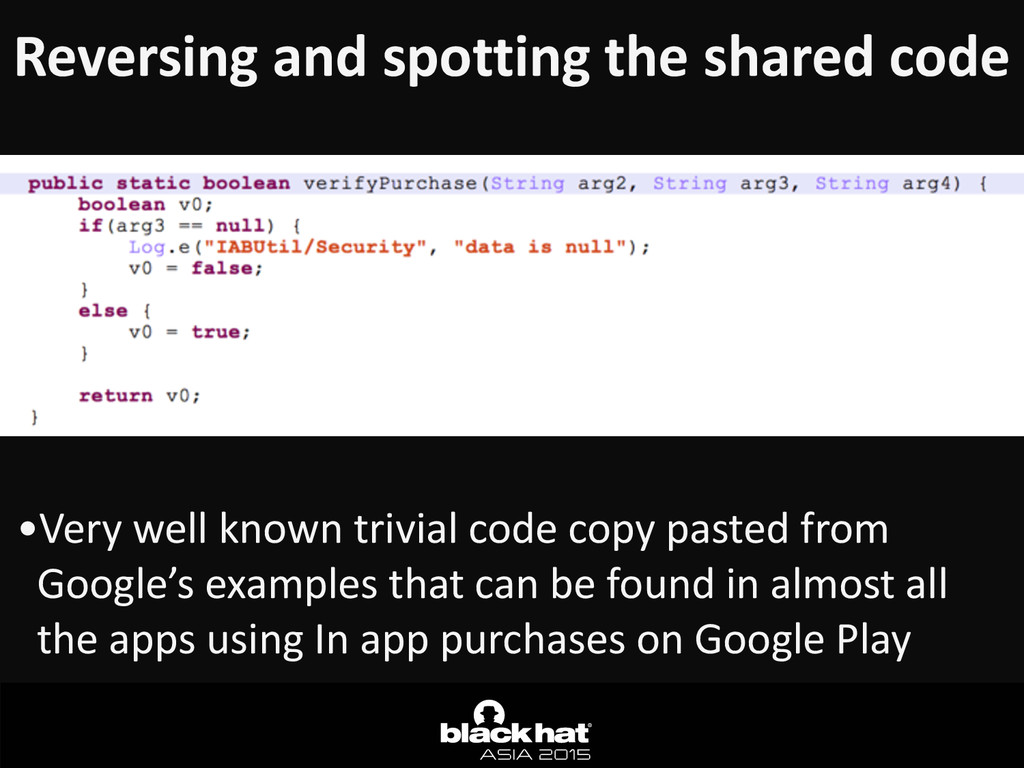
Reversing and spotting the shared code •Very well known trivial
code copy pasted from Google’s examples that can be found in almost all the apps using In app purchases on Google Play -
Develop a runtime attack • Leverage a framework to patch
verifyPurchase to return always true and other small mods (with Xposed framework for example) • if the app doesn’t check signatures server side for the purchase (which almost none do) we are done • For more informations on runtime attacks on iOS or Android: ZeroNights ’14 -‐ Steroids For Your App Security Assessment -‐ https:// speakerdeck.com/marcograss/steroids-‐for-‐your-‐ app-‐security-‐assessment -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Some examples of vulnerabilities in the frameworks -
A tale about chained vulns in Cordova • CVE-‐2014-‐3500 XAS
via Android Intent URLs. • CVE-‐2014-‐3501 Whitelist Bypass for Non-‐HTTP URLs. • CVE-‐2014-‐3502 Apps can leak data to other apps via URL Loading. -
CVE-‐2014-‐3500 • Cordova-‐based applications use a WebView to renders the
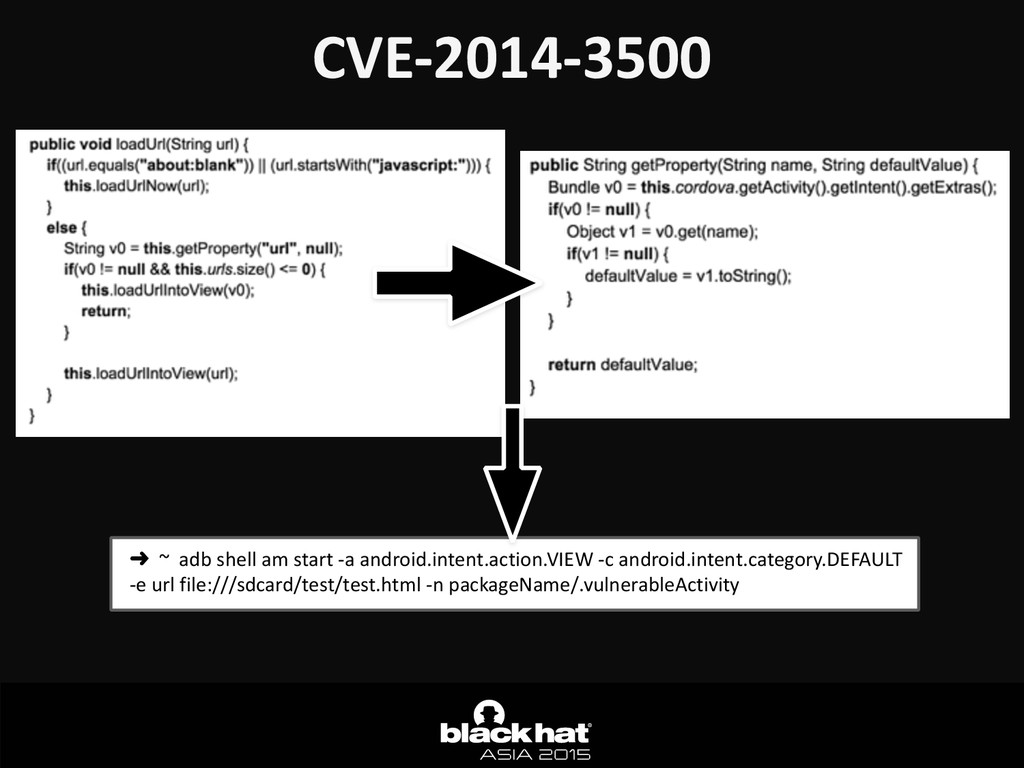
website requested, via the ‘CordovaWebView’ activity, through the ‘loadUrl()’ function. • If the url provided is ‘ about:blank' or ‘javascript’ it will be loaded via ‘loadUrlNow(url)’ method. Otherwise the register v0 will triggered after a call to ‘getProperty(“url”, null)’. • In such case, the ‘url’ parameter is taken from ‘getIntent().getExtra()’, which can be provided externally. -
CVE-‐2014-‐3500 ➜ ~ adb shell am start -‐a
android.intent.action.VIEW -‐c android.intent.category.DEFAULT -‐e url file:///sdcard/test/test.html -‐n packageName/.vulnerableActivity -
CVE-‐2014-‐3500 • Pretty similar to the previous one, the ‘errorurl’
parameter can be passed via Intent extras in ‘CordovaActivity’. • The ‘errorurl’ will be rendered by the WebView when a network request fails. • The parameter’s content must either be in the whitelist or be part of URI scheme file. Otherwise it will not be triggered. -
CVE-‐2014-‐3501 • The framework overrides Android’s ‘shouldInterceptRequest()’ method,
to ensure that the WebView only allows requests to URLs in the configured whitelist. • The mechanism is only configured for HTTP/S or the file URI, being possible to bypass it through other protocols like WS/S -
CVE-‐2014-‐3502 • Cordova overrides ‘shouldOverrideUrlLoading()’. If the scheme is
not handled by the function will be launched in the default viewer. • If an attacker calls the WebView to load a new URL (location.href), ‘shouldOverrideUrlLoading()’ will be called. Independently of the whitelist validation. • It’s possible to force Cordova to launch a URL using the default viewer. -
Adobe AIR’s EncryptedLocalStorage API “The EncryptedLocalStore class (ELS) provides
an encrypted local storage mechanism that you can be use as a small cache for an application's private data. ELS data cannot be shared between applications. The intent of ELS is to allow an application to store easily recreated items such as login credentials and other private information.” -‐ Adobe documentation -
Adobe AIR WTF On Android, the data stored by
the EncryptedLocalStorage class are not encrypted. Adobe basically rely on the fact that application private folder are not accessible by an attacker thanks to Android uid/gid separation between apps. As we will see this assumption is not valid. So basically a developer expects to store data encrypted but…. -
Adobe AIR WTF Instead the implementation of the
“EncryptedStorage” is just a Base64 Encoding! Probably lot of others platform specific quirks around the code base… -
Small parenthesis… adb backups • Functionality introduced in Android 4.0.
• If you have physical access to the phone and you can activate usb debugging, you can backup to your computer the content of the private application folder that have the flag “allowBackup” set to true in their AndroidManifest.xml • If the flag is omitted, the default value is true. -
Adobe AIR WTF The Adobe AIR applications by default
have the flag allowBackup unset, so the default value of true kicks in. This allows an attacker without root to backup the content of the private folder of the Adobe application with adb backup and retrieve those unencrypted supposedly private informations. -
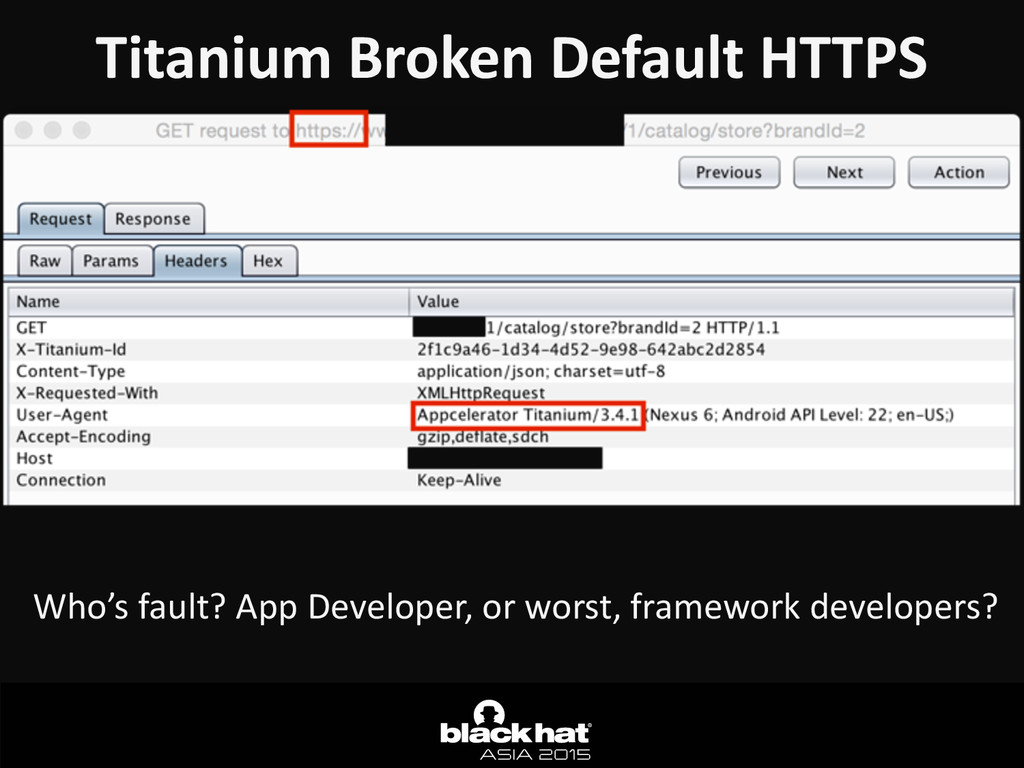
Titanium Broken Default HTTPS Who’s fault? App Developer, or worst,
framework developers? -
Titanium Broken Default HTTPS So the applications developed by this
framework are often vulnerable by MiTM. Why? By default the framework doesn’t validate the certificate on Android! -
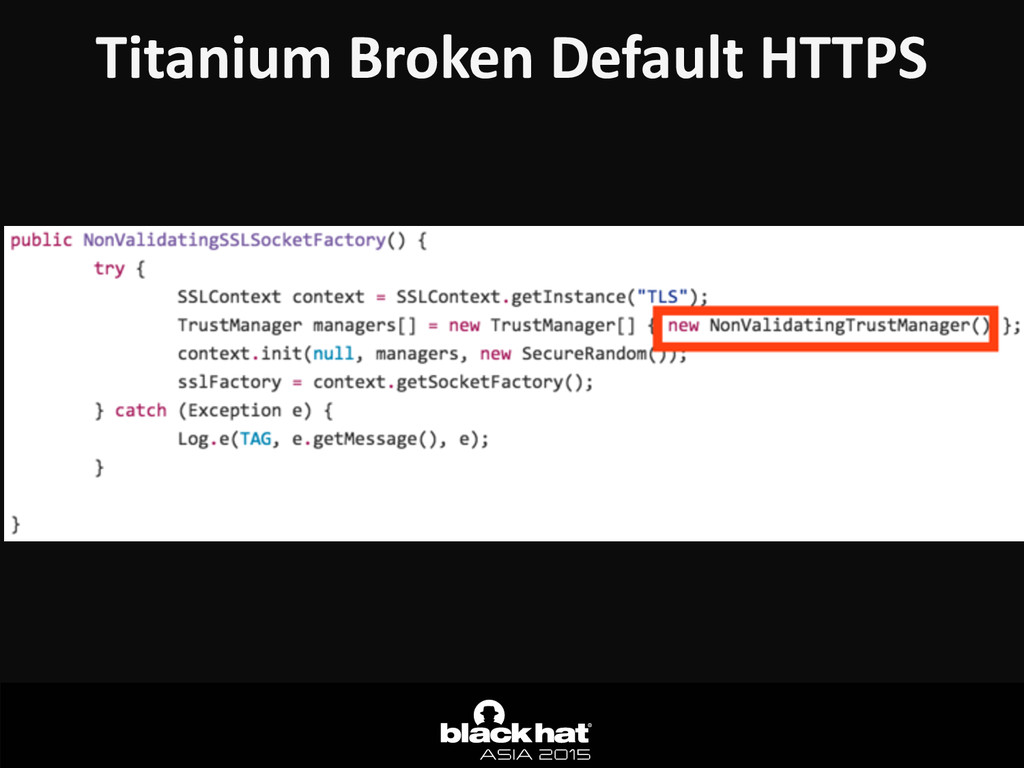
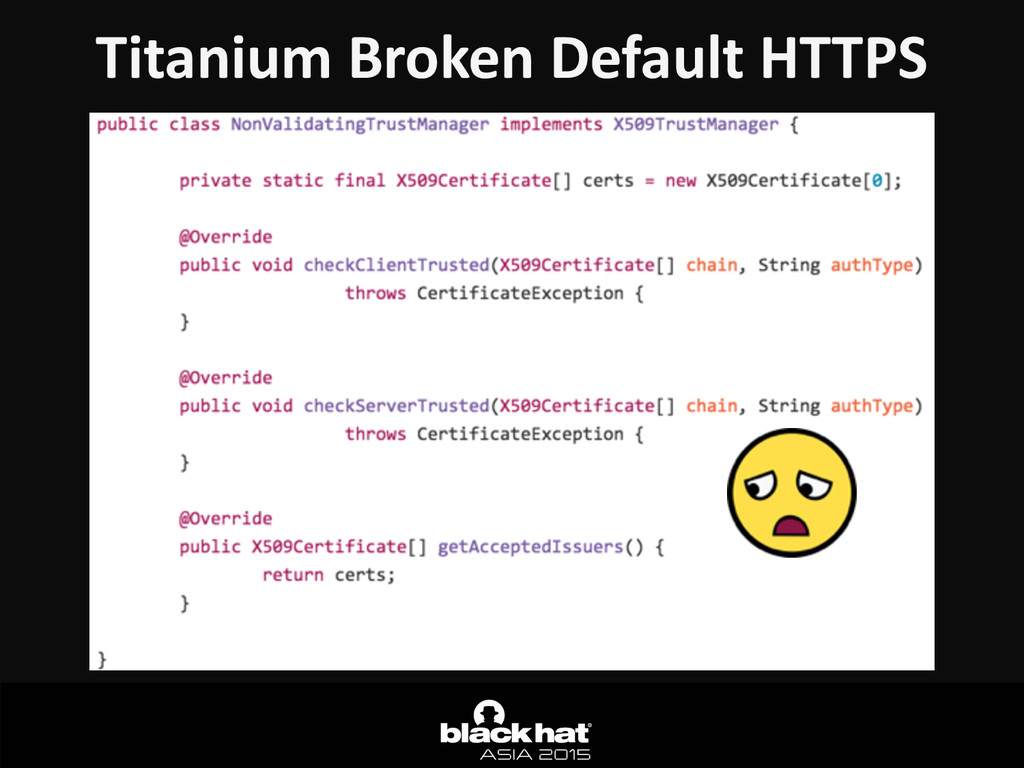
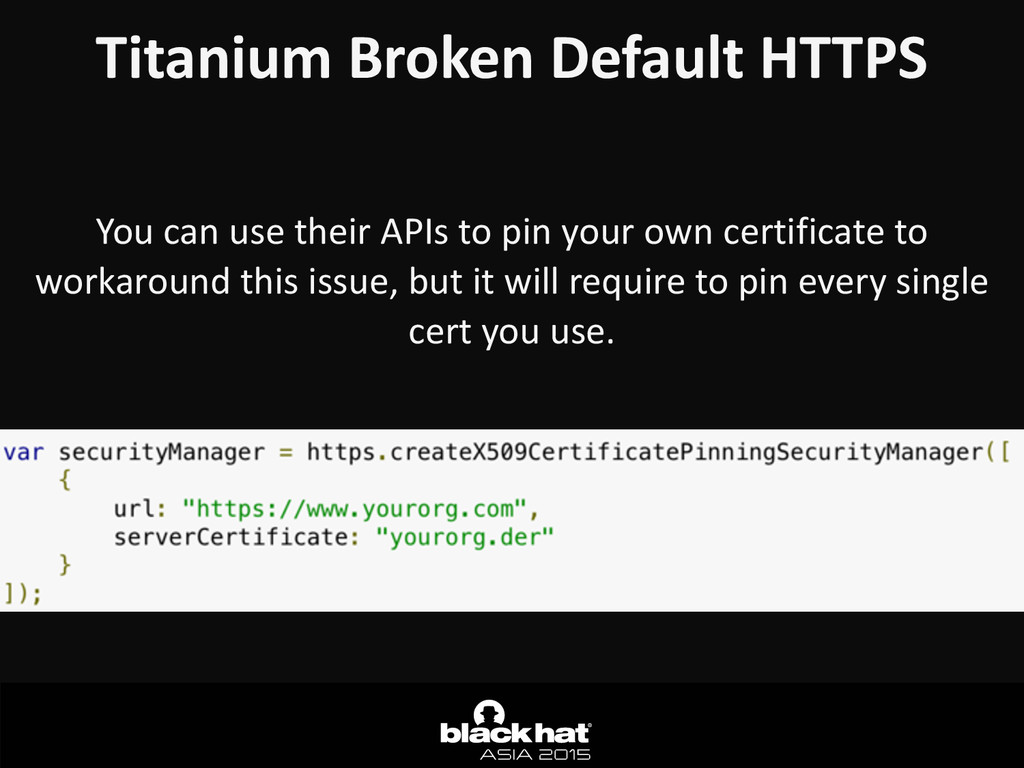
Titanium Broken Default HTTPS If the developer doesn’t specify a
pinning for his certificate, the framework simply leverage dummy classes called “NonValidatingSSLSocketFactory / NonValidatingTrustManager” and so on. So the result is that if you rely on the defaults (which pretty much everyone does), the SSL validation is completely skipped, allowing an attacker to MiTM traffic even without a trusted certificate! -
Titanium Broken Default HTTPS You can use their APIs to
pin your own certificate to workaround this issue, but it will require to pin every single cert you use. -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Conclusions -
Conclusions • Security is not taken too much seriously.
• Mechanisms used to protect the application’s assets are not good enough. (so your IP is at risk!) • Few hours and some minion bottles of vodka were necessary to find these issues. What could possibly go wrong if we dedicate more time? -
• Click to edit Master text styles — Second
level • Third level — Fourth level » Fifth level Click to edit Master title style Next Steps -
To the infinity and beyond • Automatic framework recognition
and develop instrumentation to trace also interpreted execution. • Merge all the code extractors in one unique utility. • Find more vulnerabilities in the framework cores. • Suggestions? -
WE ARE HIRING! https://www.nowsecure.com/careers/ OR… SAY HI TO US AND
WE WILL GRAB A DRINK AND TALK!
 marcograss
 xspa2012
 s_mizuki_nlp
 takaomurakami
 analokmaus
 resolutionfoundation
 nzw0301
 godel
 institutdelelevage
 mikimhk
 ept
 eileencodes
 katarinadahlin
 jnunemaker
 codingconduct
 sabderemane
 danielanewman
 badams
 destraynor
 mraible
 mfonobong
 honnibal
 lara