Share
Embed
Transcript
54 slides
-
→ Who are you? ➡ Authentication → Are you allowed
(to do that)? ➡ Authorization -
The Game Plan → authentication concepts → authorization concepts →
how they're used in a framework project Example Project https://github.com/ocrampete16/symfony-security- demystified-talk -
btw, who dis? ! Marco Petersen " Software Developer @
SensioLabs # @ocrampete16 $ [email protected] -
User Providers load a user from a source $userProvider =
new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd', 'roles' => ['ROLE_USER'], ], ]); $user = $userProvider->loadUserByUsername('marco'); -
User Providers load a user from a source $userProvider =
new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd', 'roles' => ['ROLE_USER'], ], ]); $user = $userProvider->loadUserByUsername('marco'); -
The User Checker ensures that the user meets certain requirements
$userChecker = new UserChecker(); $userChecker->checkPreAuth($user); // authenticate user here $userChecker->checkPostAuth($user); -
The User Checker ensures that the user meets certain requirements
$userChecker = new UserChecker(); $userChecker->checkPreAuth($user); // authenticate user here $userChecker->checkPostAuth($user); -
The User Checker ensures that the user meets certain requirements
$userChecker = new UserChecker(); $userChecker->checkPreAuth($user); // authenticate user here $userChecker->checkPostAuth($user); -
The User Checker ensures that the user meets certain requirements
$userChecker = new UserChecker(); $userChecker->checkPreAuth($user); // authenticate user here $userChecker->checkPostAuth($user); -
What does the default User Checker do? The User Checker
does not do anything by default. Implement your own to check for things like: → disabled accounts → accounts past the trial period → expired credentials -
Password Encoders encode passwords $encoderFactory = new EncoderFactory([ User::class =>
new PlaintextPasswordEncoder(), ]); $encoder = $encoderFactory->getEncoder($user); $hash = $encoder->encodePassword($plaintext, $salt); -
Password Encoders encode passwords $encoderFactory = new EncoderFactory([ User::class =>
new PlaintextPasswordEncoder(), ]); $encoder = $encoderFactory->getEncoder($user); $hash = $encoder->encodePassword($plaintext, $salt); -
const PROVIDER_KEY = 'default'; $unauthenticatedToken = new UsernamePasswordToken('marco', 'p4$$w0rd', PROVIDER_KEY);
$authenticationManager = new AuthenticationProviderManager([ new DaoAuthenticationProvider( $userProvider, $userChecker, PROVIDER_KEY, $encoderFactory ), ]); $authenticatedToken = $authenticationManager->authenticate($unauthenticatedToken); -
const PROVIDER_KEY = 'default'; $unauthenticatedToken = new UsernamePasswordToken('marco', 'p4$$w0rd', PROVIDER_KEY);
$authenticationManager = new AuthenticationProviderManager([ new DaoAuthenticationProvider( $userProvider, $userChecker, PROVIDER_KEY, $encoderFactory ), ]); $authenticatedToken = $authenticationManager->authenticate($unauthenticatedToken); -
const PROVIDER_KEY = 'default'; $unauthenticatedToken = new UsernamePasswordToken('marco', 'p4$$w0rd', PROVIDER_KEY);
$authenticationManager = new AuthenticationProviderManager([ new DaoAuthenticationProvider( $userProvider, $userChecker, PROVIDER_KEY, $encoderFactory ), ]); $authenticatedToken = $authenticationManager->authenticate($unauthenticatedToken); -
const PROVIDER_KEY = 'default'; $unauthenticatedToken = new UsernamePasswordToken('marco', 'p4$$w0rd', PROVIDER_KEY);
$authenticationManager = new AuthenticationProviderManager([ new DaoAuthenticationProvider( $userProvider, $userChecker, PROVIDER_KEY, $encoderFactory ), ]); $authenticatedToken = $authenticationManager->authenticate($unauthenticatedToken); -
const PROVIDER_KEY = 'default'; $unauthenticatedToken = new UsernamePasswordToken('marco', 'p4$$w0rd', PROVIDER_KEY);
$authenticationManager = new AuthenticationProviderManager([ new DaoAuthenticationProvider( $userProvider, $userChecker, PROVIDER_KEY, $encoderFactory ), ]); $authenticatedToken = $authenticationManager->authenticate($unauthenticatedToken); -
Symfony uses the same class for authenticated and unauthenticated tokens
// UserPasswordToken.php public function __construct( $user, $credentials, string $providerKey, array $roles = [] ) { // ... parent::setAuthenticated(\count($roles) > 0); } -
Symfony uses the same class for authenticated and unauthenticated tokens
// UserPasswordToken.php public function __construct( $user, $credentials, string $providerKey, array $roles = [] ) { // ... parent::setAuthenticated(\count($roles) > 0); } -
$userProvider = new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd',
'roles' => ['ROLE_USER'], ], ]); -
$userProvider = new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd',
'roles' => ['ROLE_USER'], ], ]); -
$userProvider = new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd',
'roles' => [], ], ]); // ... // $token is unauthenticated! $token = $authenticationManager->authenticate($unauthenticatedToken); -
$userProvider = new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd',
'roles' => [], ], ]); // ... // $token is unauthenticated! $token = $authenticationManager->authenticate($unauthenticatedToken); -
$userProvider = new InMemoryUserProvider([ 'marco' => [ 'password' => 'p4$$w0rd',
'roles' => [], ], ]); // ... // $token is unauthenticated! $token = $authenticationManager->authenticate($unauthenticatedToken); -
Security voters vote whether an authenticated user can perform an
action on a subject $voter = new BlogPostVoter(); // returns VoterInterface::ACCESS_GRANTED, // VoterInterface::ACCESS_ABSTAIN or VoterInterface::ACCESS_DENIED $vote = $voter->vote($token, $blogPost, ['edit']); -
Security voters vote whether an authenticated user can perform an
action on a subject $voter = new BlogPostVoter(); // returns VoterInterface::ACCESS_GRANTED, // VoterInterface::ACCESS_ABSTAIN or VoterInterface::ACCESS_DENIED $vote = $voter->vote($token, $blogPost, ['edit']); -
The framework also uses Security Voters to check for roles
and authentication states $roleVoter = new RoleVoter('ROLE_'); $authenticatedVoter = new AuthenticatedVoter( $authenticationTrustResolver ); // Does the user have the role `ROLE_USER`? $roleVoter->vote($token, null, ['ROLE_USER']); // Is the user logged in? $authenticatedVoter->vote($token, null, ['IS_AUTHENTICATED_FULLY']); -
The framework also uses Security Voters to check for roles
and authentication states $roleVoter = new RoleVoter('ROLE_'); $authenticatedVoter = new AuthenticatedVoter( $authenticationTrustResolver ); // Does the user have the role `ROLE_USER`? $roleVoter->vote($token, null, ['ROLE_USER']); // Is the user logged in? $authenticatedVoter->vote($token, null, ['IS_AUTHENTICATED_FULLY']); -
The framework also uses Security Voters to check for roles
and authentication states $roleVoter = new RoleVoter('ROLE_'); $authenticatedVoter = new AuthenticatedVoter( $authenticationTrustResolver ); // Does the user have the role `ROLE_USER`? $roleVoter->vote($token, null, ['ROLE_USER']); // Is the user logged in? $authenticatedVoter->vote($token, null, ['IS_AUTHENTICATED_FULLY']); -
Putting it all together $accessDecisionManager = new AccessDecisionManager([ new RoleVoter(),
new BlogPostVoter(), ]); $hasRole = $accessDecisionManager->decide( $authenticatedToken, ['ROLE_USER'] ); $canEditBlogPost = $accessDecisionManager->decide( $authenticatedToken, ['edit'], $blogPost ); -
Putting it all together $accessDecisionManager = new AccessDecisionManager([ new RoleVoter(),
new BlogPostVoter(), ]); $hasRole = $accessDecisionManager->decide( $authenticatedToken, ['ROLE_USER'] ); $canEditBlogPost = $accessDecisionManager->decide( $authenticatedToken, ['edit'], $blogPost ); -
Putting it all together $accessDecisionManager = new AccessDecisionManager([ new RoleVoter(),
new BlogPostVoter(), ]); $hasRole = $accessDecisionManager->decide( $authenticatedToken, ['ROLE_USER'] ); $canEditBlogPost = $accessDecisionManager->decide( $authenticatedToken, ['edit'], $blogPost ); -
Putting it all together $accessDecisionManager = new AccessDecisionManager([ new RoleVoter(),
new BlogPostVoter(), ]); $hasRole = $accessDecisionManager->decide( $authenticatedToken, ['ROLE_USER'] ); $canEditBlogPost = $accessDecisionManager->decide( $authenticatedToken, ['edit'], $blogPost ); -
A simple security configuration security: providers: database_users: entity: { class:
App\Entity\User, property: username } encoders: App\Entity\User: 'bcrypt' firewalls: main: anonymous: true form_login: true access_control: - { path: ^/profile, roles: ROLE_USER } -
framework providers: database_users: entity: { class: App\Entity\User, property: username }
standalone $userProvider = new EntityUserProvider( $registry, App\Entity\User::class, 'username' ); -
framework encoders: App\Entity\User: 'bcrypt' standalone $encoderFactory = new EncoderFactory([ App\Entity\User::class
=> new BCryptPasswordEncoder($cost), ]); -
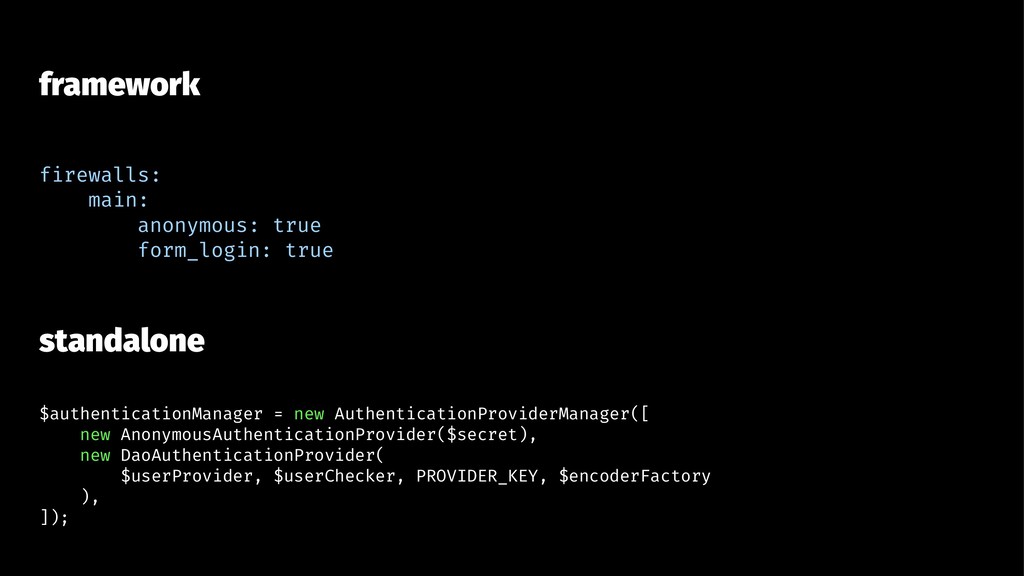
framework firewalls: main: anonymous: true form_login: true standalone $authenticationManager =
new AuthenticationProviderManager([ new AnonymousAuthenticationProvider($secret), new DaoAuthenticationProvider( $userProvider, $userChecker, PROVIDER_KEY, $encoderFactory ), ]); -
framework access_control: - { path: ^/profile, roles: ROLE_USER } standalone
$accessDecisionManager = new AccessDecisionManager([ new RoleVoter(), ]); // if request matches ^/profile $granted = $accessDecisionManager->decide( $authenticatedToken, ['ROLE_USER'] ); -
The security workflow is comprised of two phases. Authentication asks
"Who are you?" Authorization asks "Are you allowed to do that?" -
User providers load users from a source. User checkers check
loaded users. Password encoders encode passwords. -
Security voters vote to grant or deny access (or abstain).
Symfony uses Security Voters to check roles and authentication states.