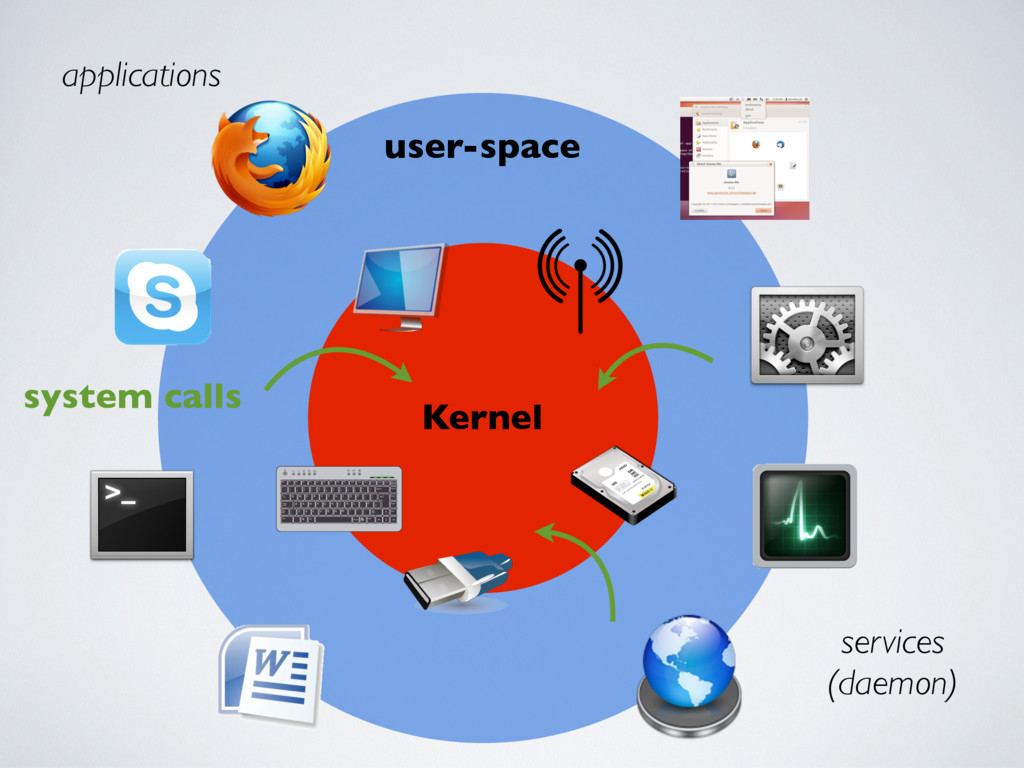
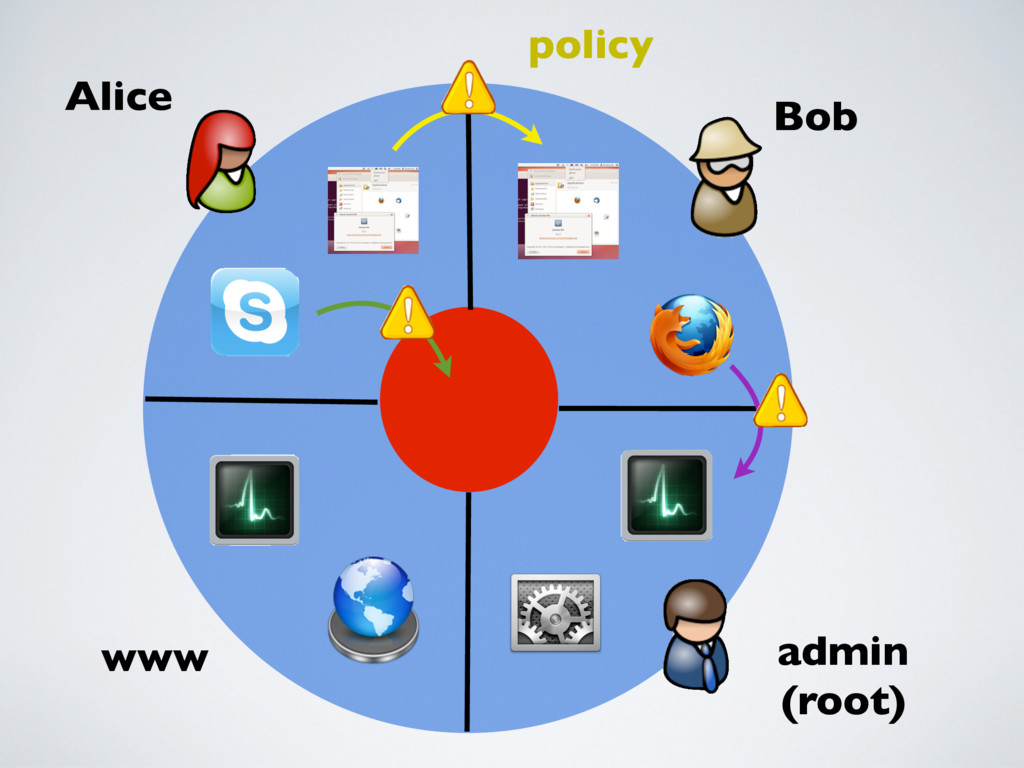
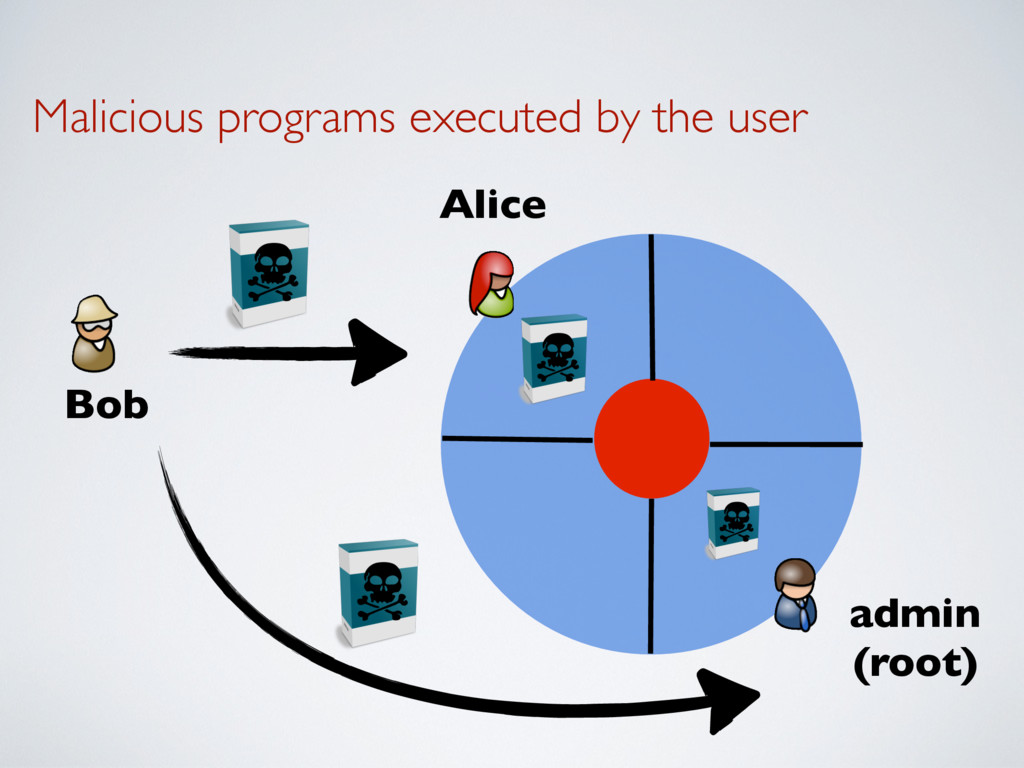
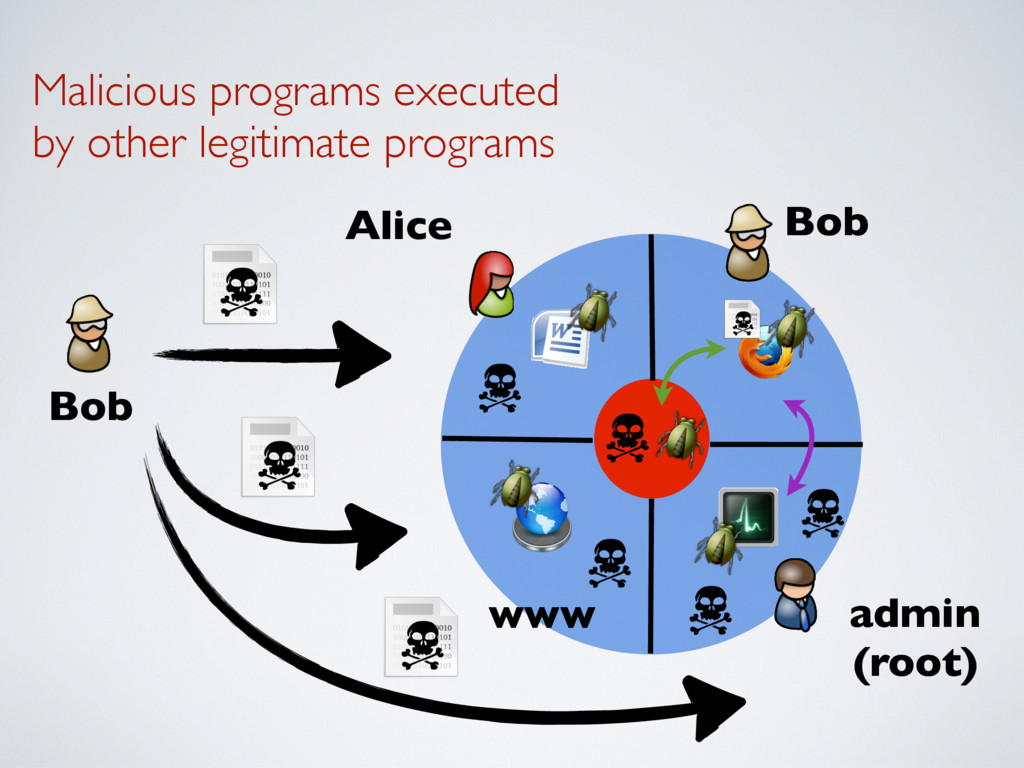
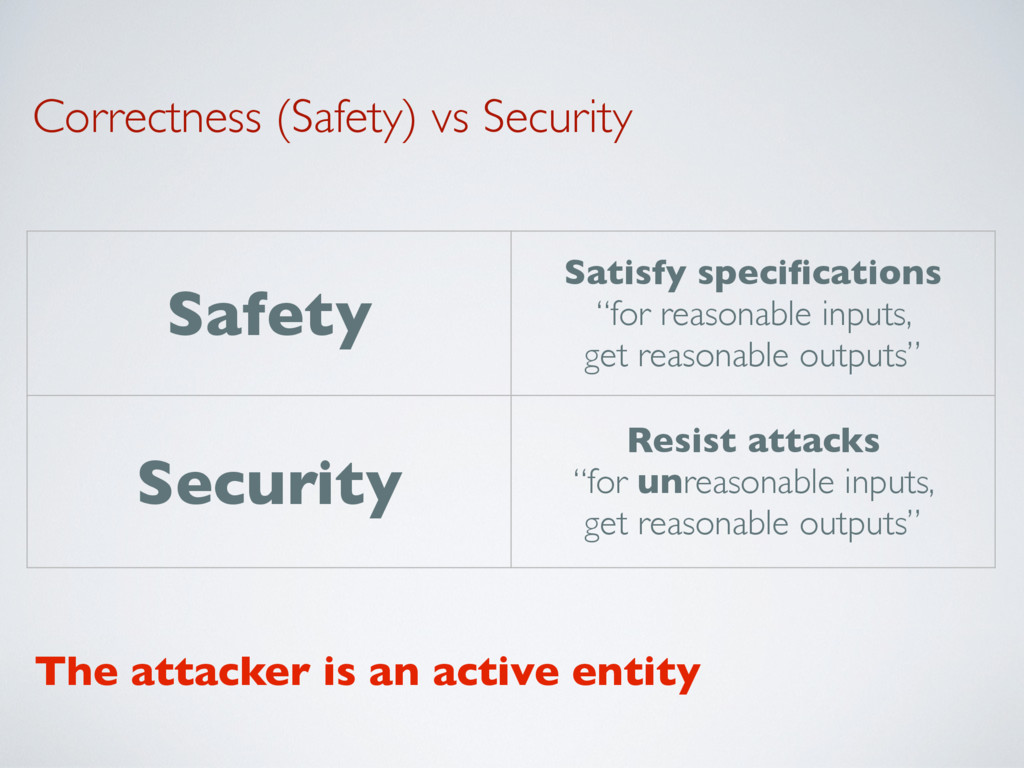
➡ Resources are accessed through programs (authorization) ➡ Every access is checked by the system (complete mediation) ✓ Everything is “secured” as long as long as the system is well configured and the programs behave as expected ๏ But ...
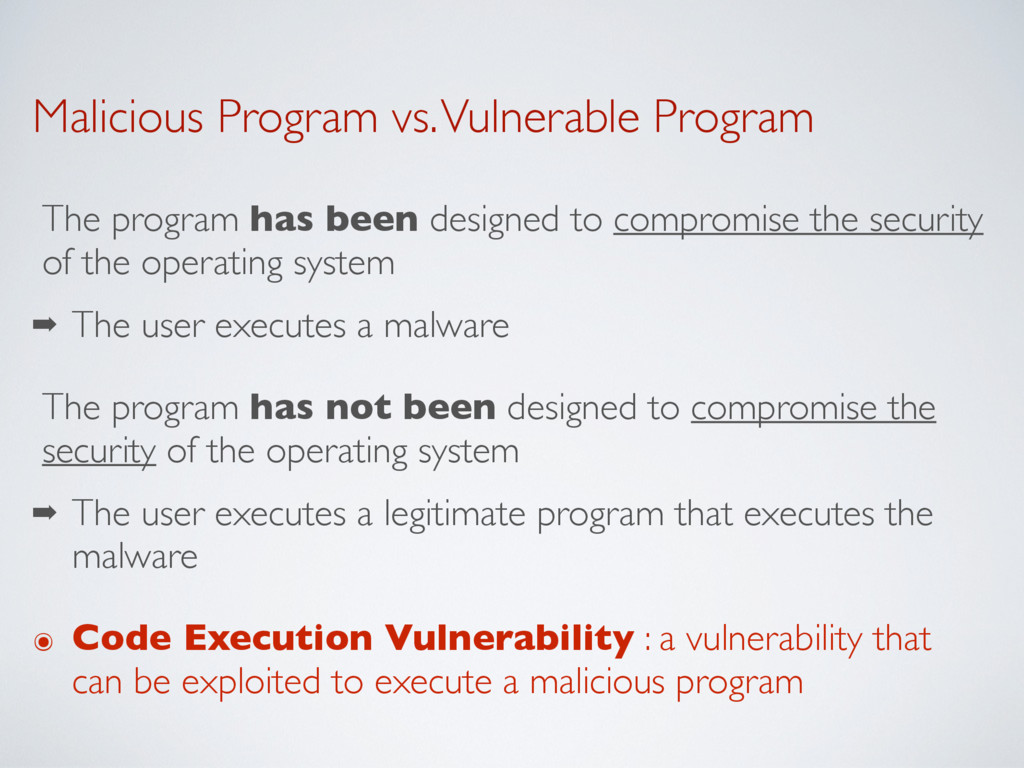
to compromise the security of the operating system ➡ The user executes a malware The program has not been designed to compromise the security of the operating system ➡ The user executes a legitimate program that executes the malware ๏ Code Execution Vulnerability : a vulnerability that can be exploited to execute a malicious program
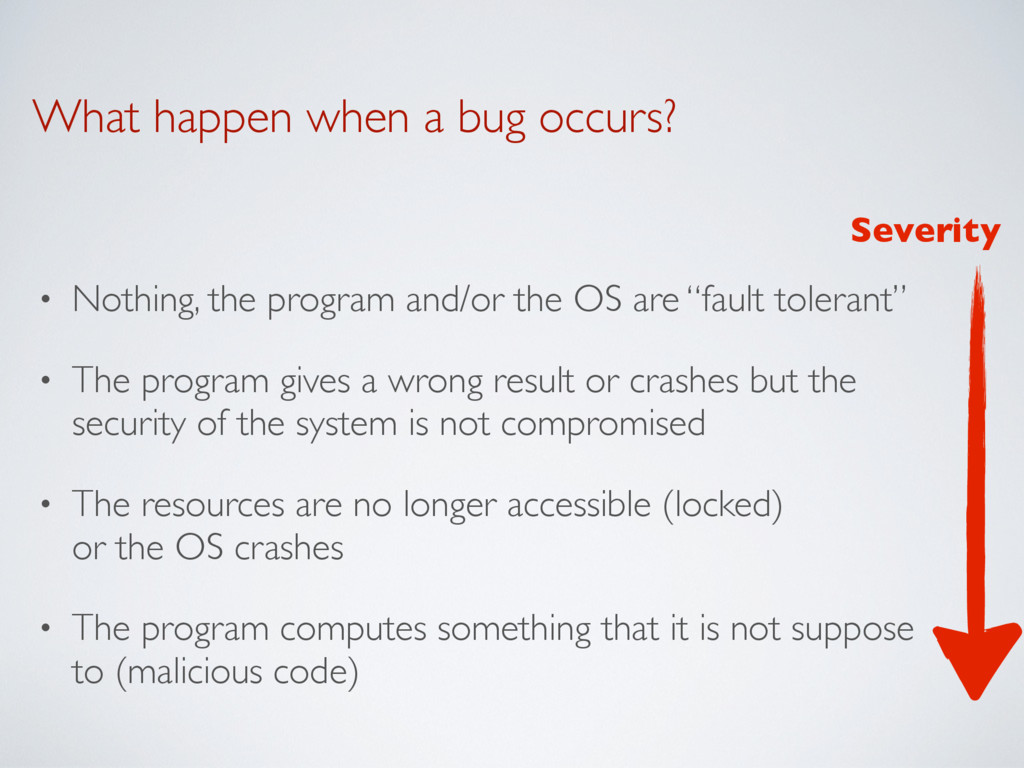
and/or the OS are “fault tolerant” • The program gives a wrong result or crashes but the security of the system is not compromised • The resources are no longer accessible (locked) or the OS crashes • The program computes something that it is not suppose to (malicious code) Severity
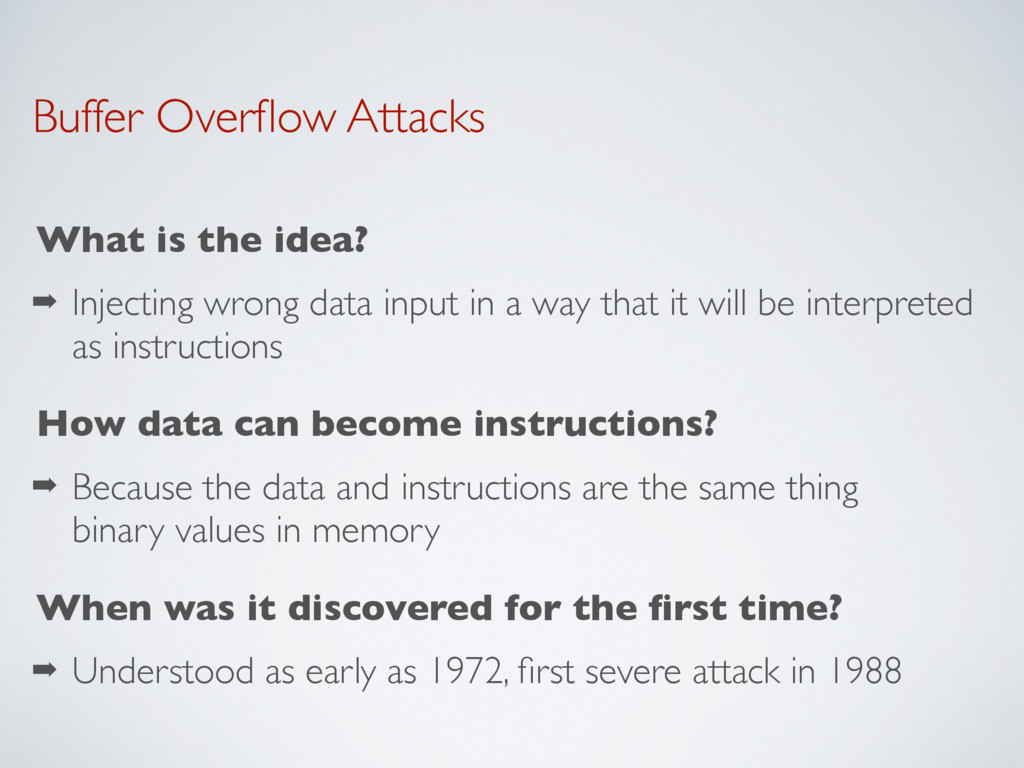
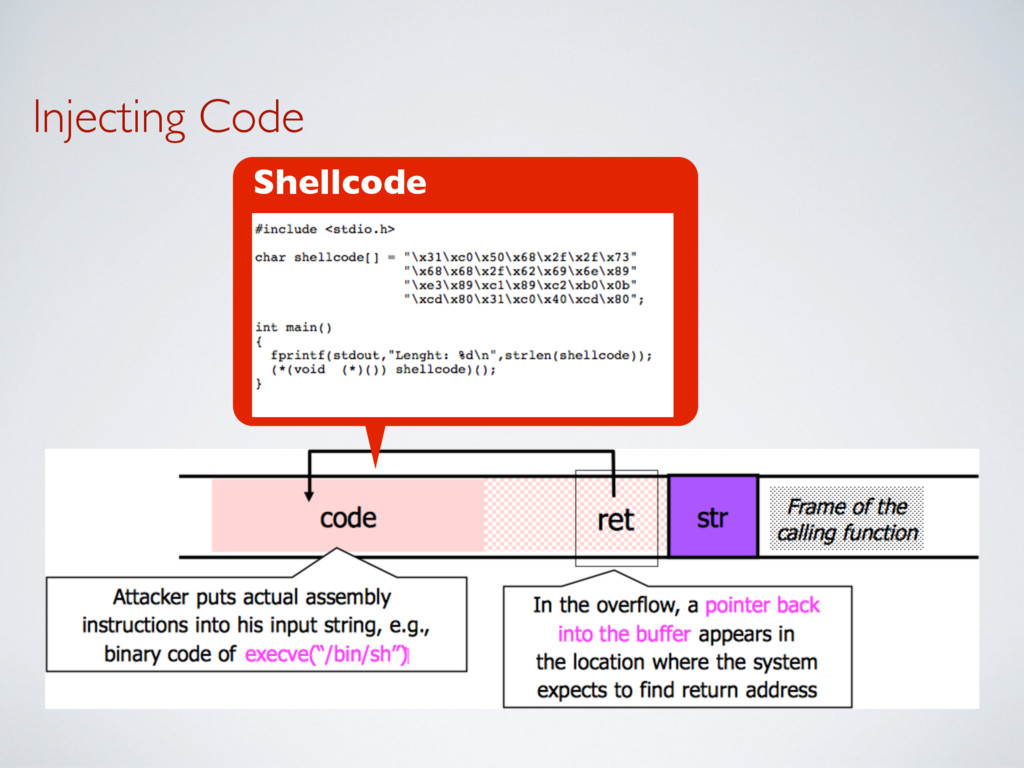
data input in a way that it will be interpreted as instructions How data can become instructions? ➡ Because the data and instructions are the same thing binary values in memory When was it discovered for the first time? ➡ Understood as early as 1972, first severe attack in 1988
familiar with assembly code • understand the runtime stack and data encoding • know how systems calls are performed • understand the exec() system call
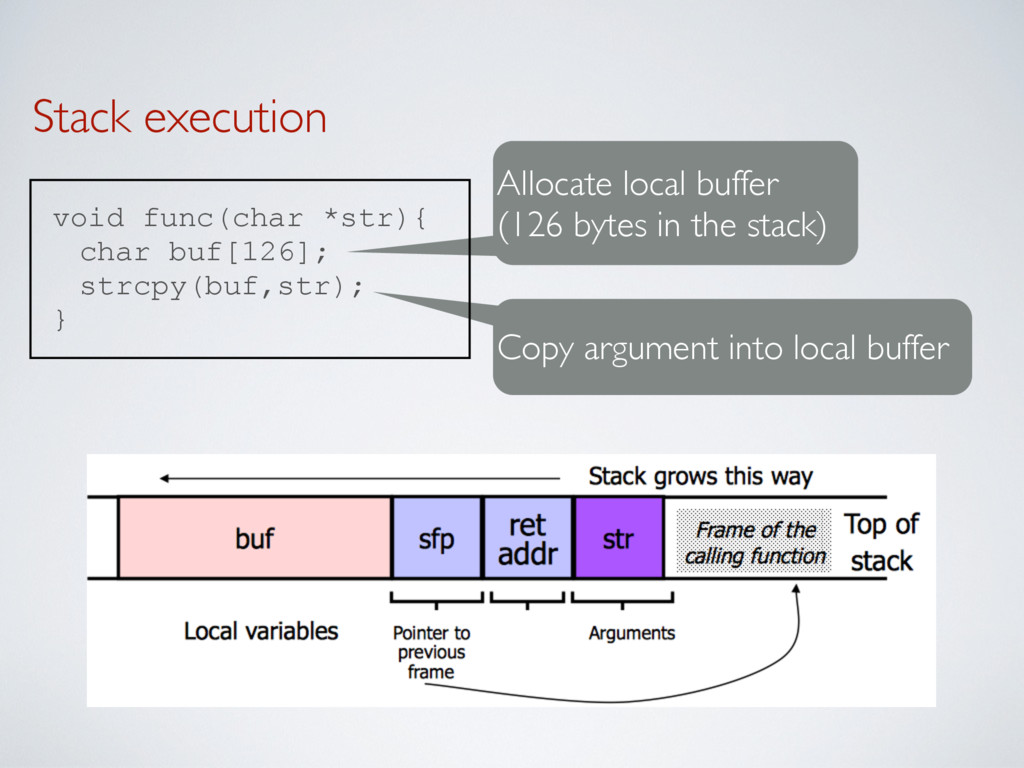
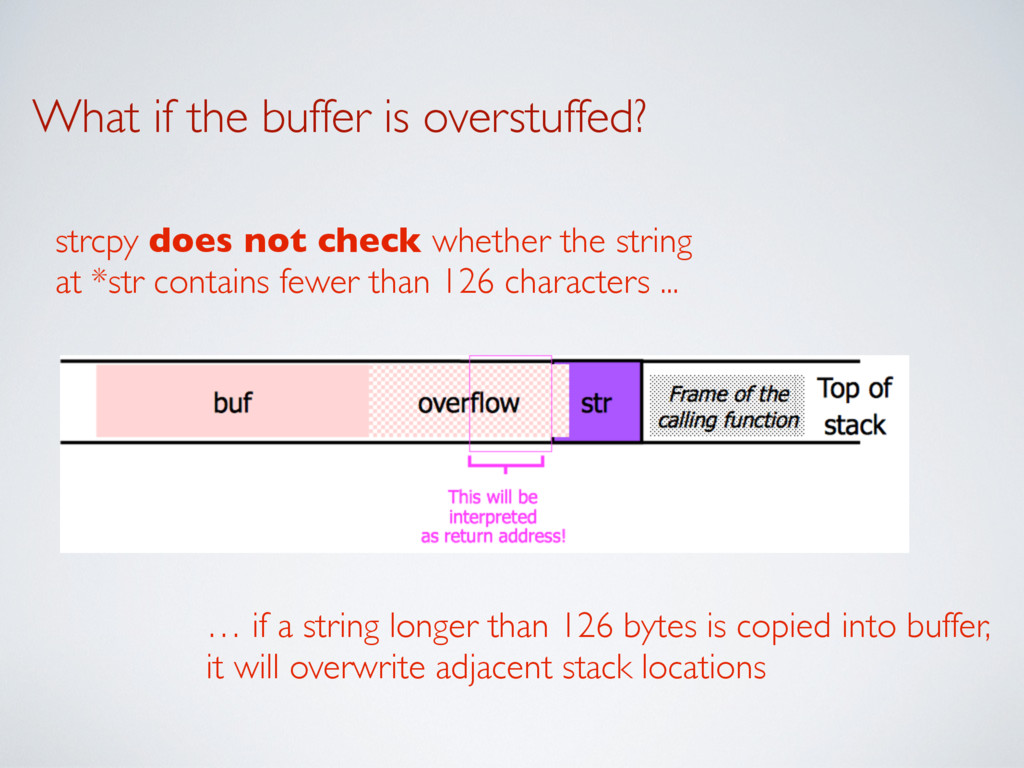
whether the string at *str contains fewer than 126 characters ... … if a string longer than 126 bytes is copied into buffer, it will overwrite adjacent stack locations
written in assembly code or C are subject to buffer overflow attacks? ➡ Because C has primitives to manipulate the memory directly (pointers ect ...) If other programming languages are “memory safe”, why are we not using them instead? • Because C and assembly code are used when a program requires high performances (audio, graphics, calculus …) or when dealing with hardware directly (OS, drivers ….)
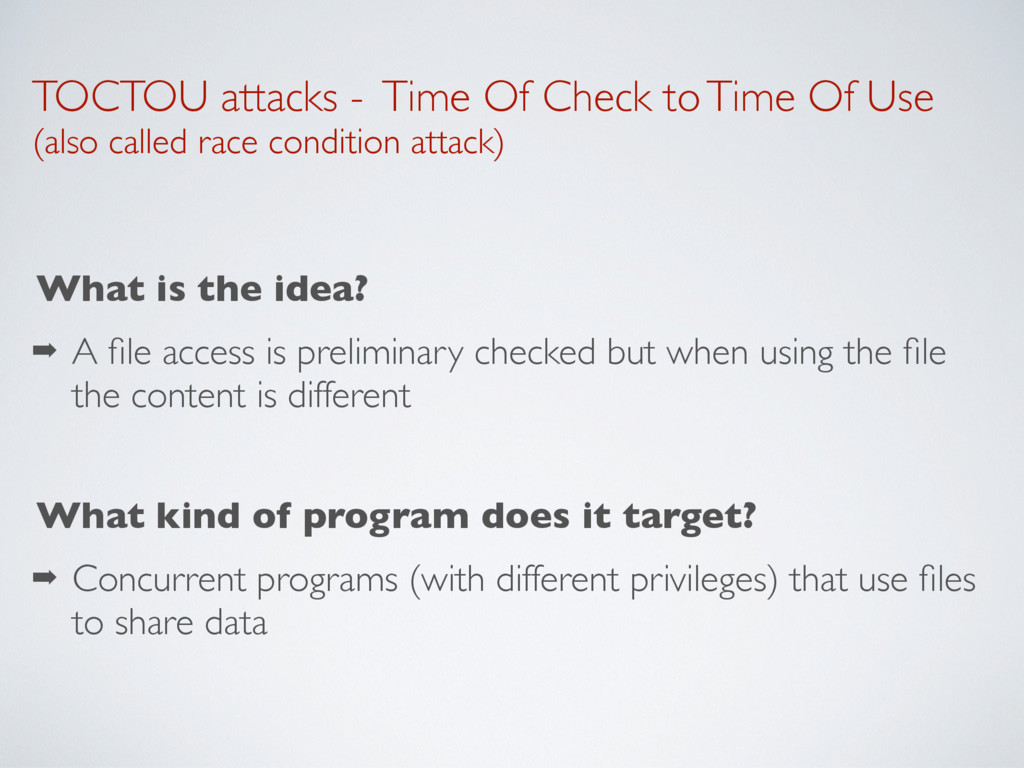
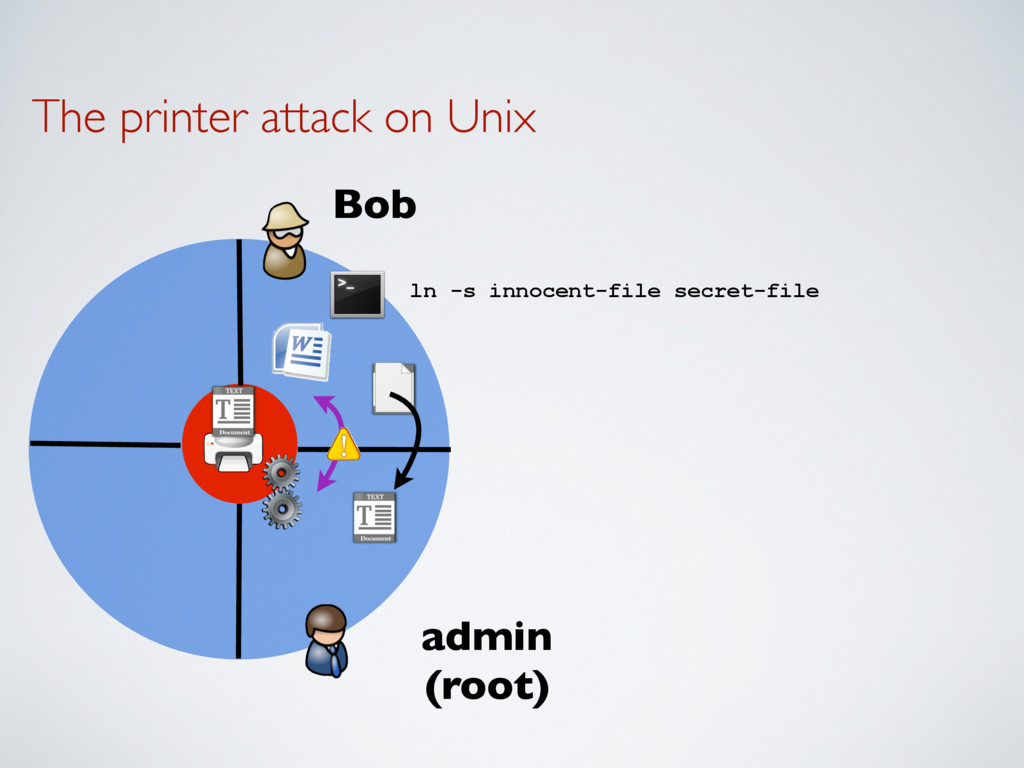
(also called race condition attack) What is the idea? ➡ A file access is preliminary checked but when using the file the content is different What kind of program does it target? ➡ Concurrent programs (with different privileges) that use files to share data
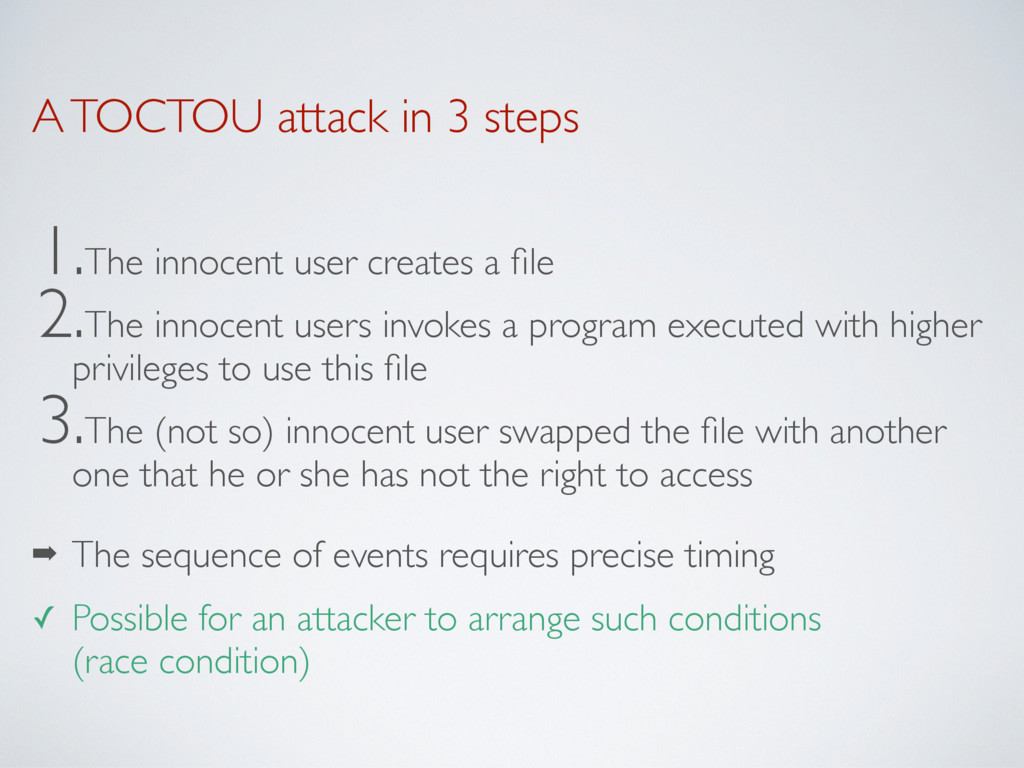
a file 2.The innocent users invokes a program executed with higher privileges to use this file 3.The (not so) innocent user swapped the file with another one that he or she has not the right to access ➡ The sequence of events requires precise timing ✓ Possible for an attacker to arrange such conditions (race condition)
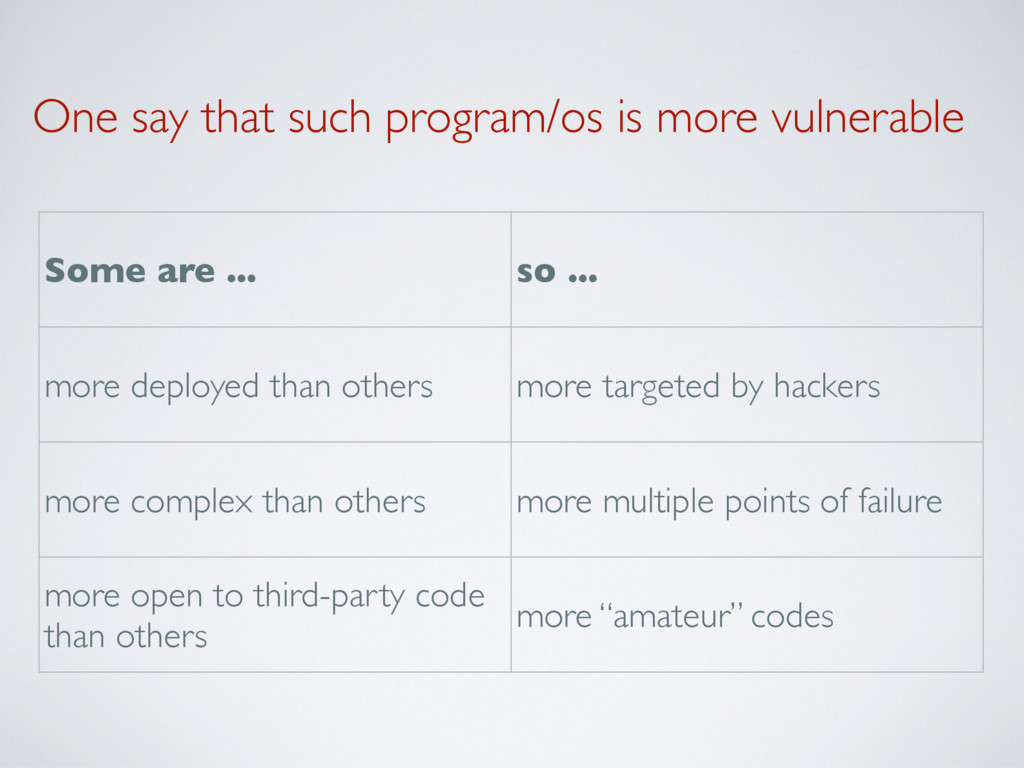
... so ... more deployed than others more targeted by hackers more complex than others more multiple points of failure more open to third-party code than others more “amateur” codes
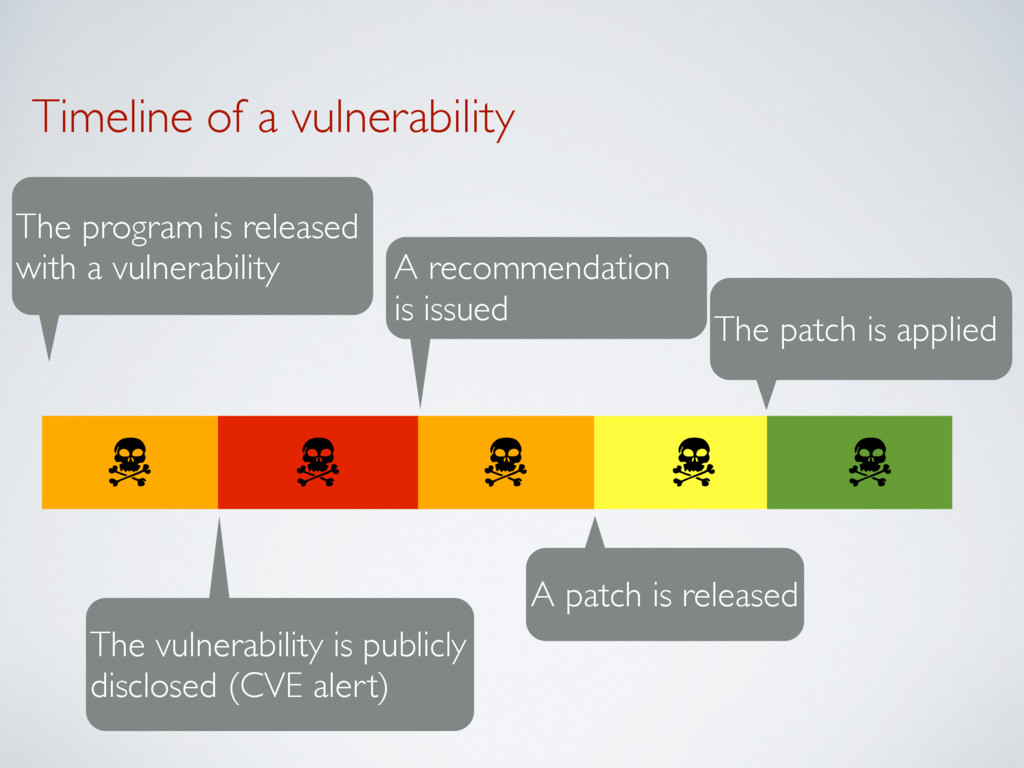
• Some bugs are directly exploitable • Others requires the user to “cooperate” • Exposure Window • How long are users exposed to the vulnerability? • Complete Disclosure • Do vendors always disclose vulnerabilities found internally?
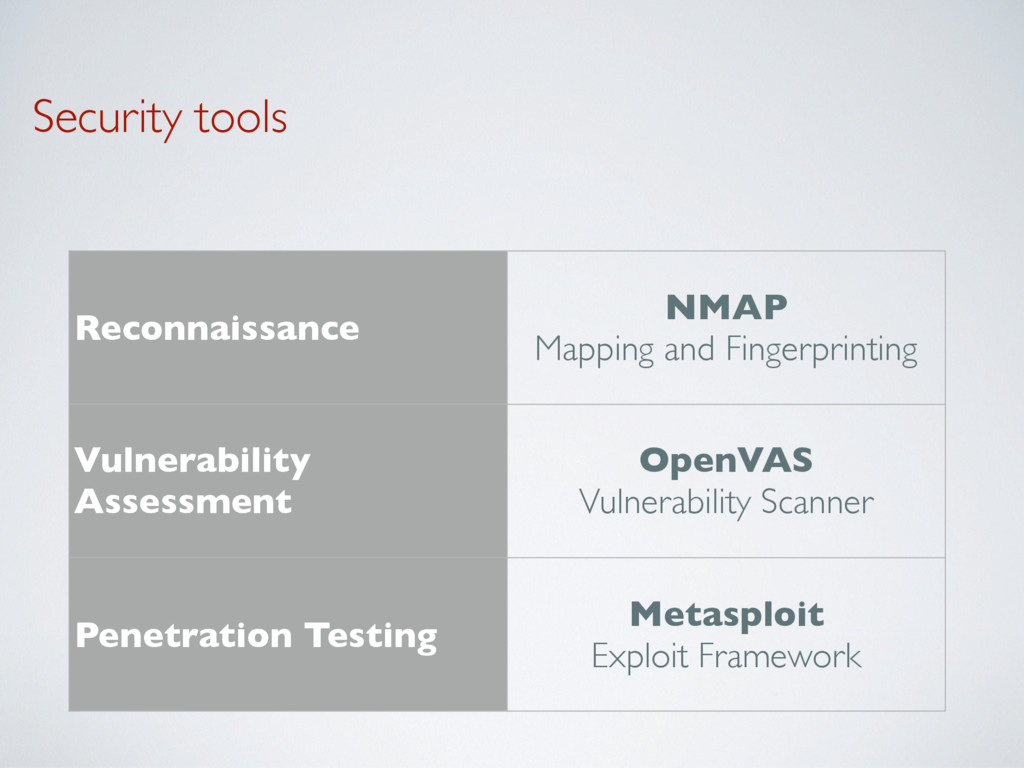
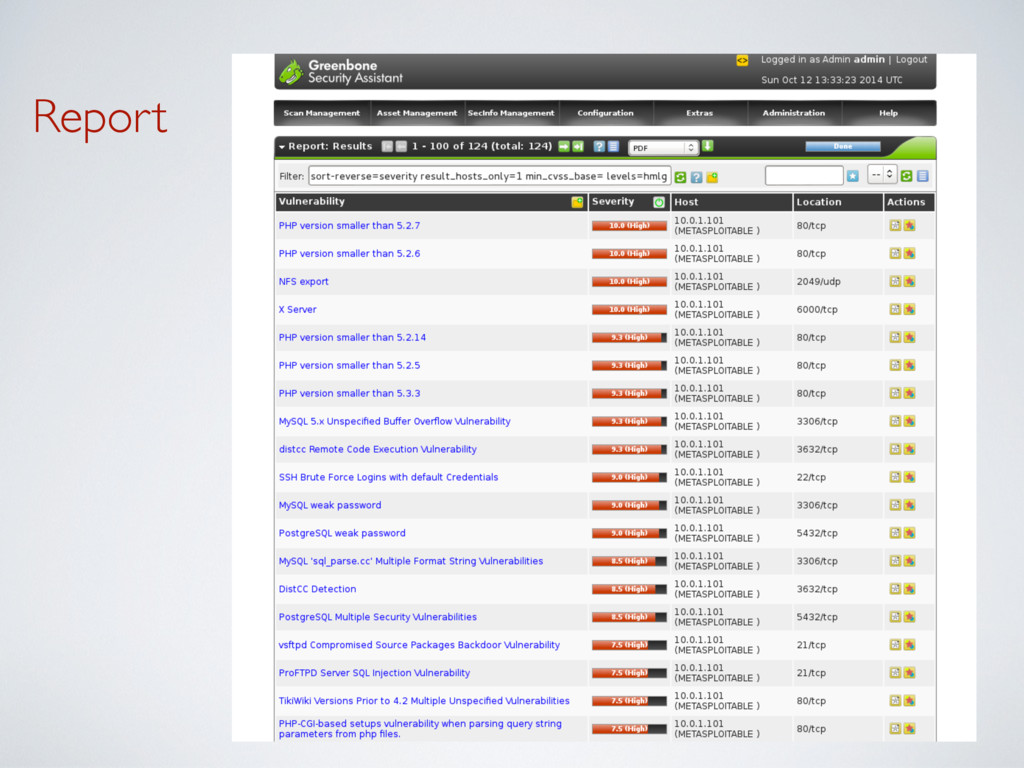
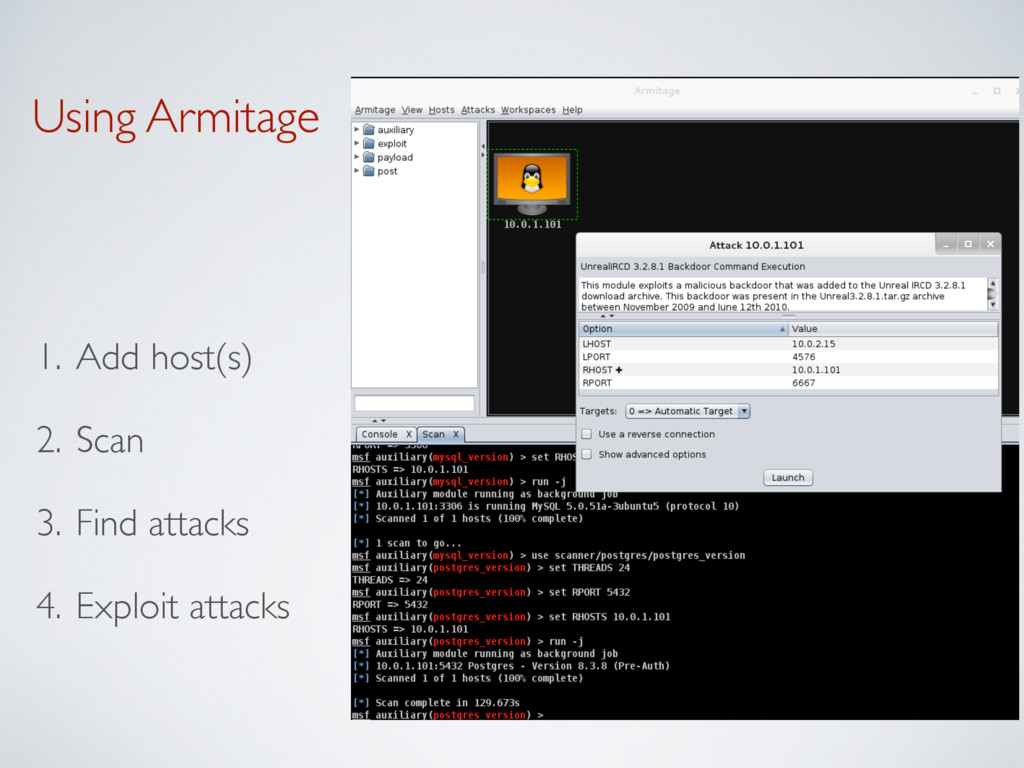
quantify the vulnerabilities of a system http://www.sans.org/reading-room/whitepapers/basics/vulnerability-assessment-421 Penetration testing (a.k.a pentest) ➡ Deliberate attack of a system with the intention of finding security weaknesses http://www.sans.org/reading-room/whitepapers/analyst/penetration-testing-assessing-security-attackers-34635
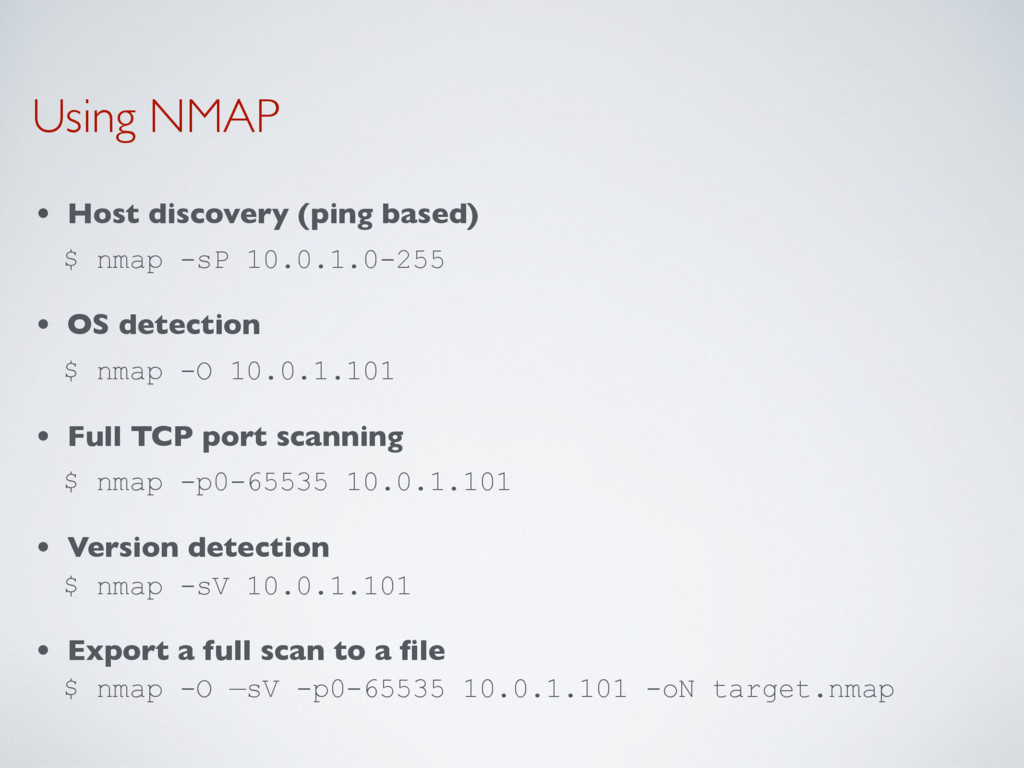
10.0.1.0-255 • OS detection $ nmap -O 10.0.1.101 • Full TCP port scanning $ nmap -p0-65535 10.0.1.101 • Version detection $ nmap -sV 10.0.1.101 • Export a full scan to a file $ nmap -O —sV -p0-65535 10.0.1.101 -oN target.nmap
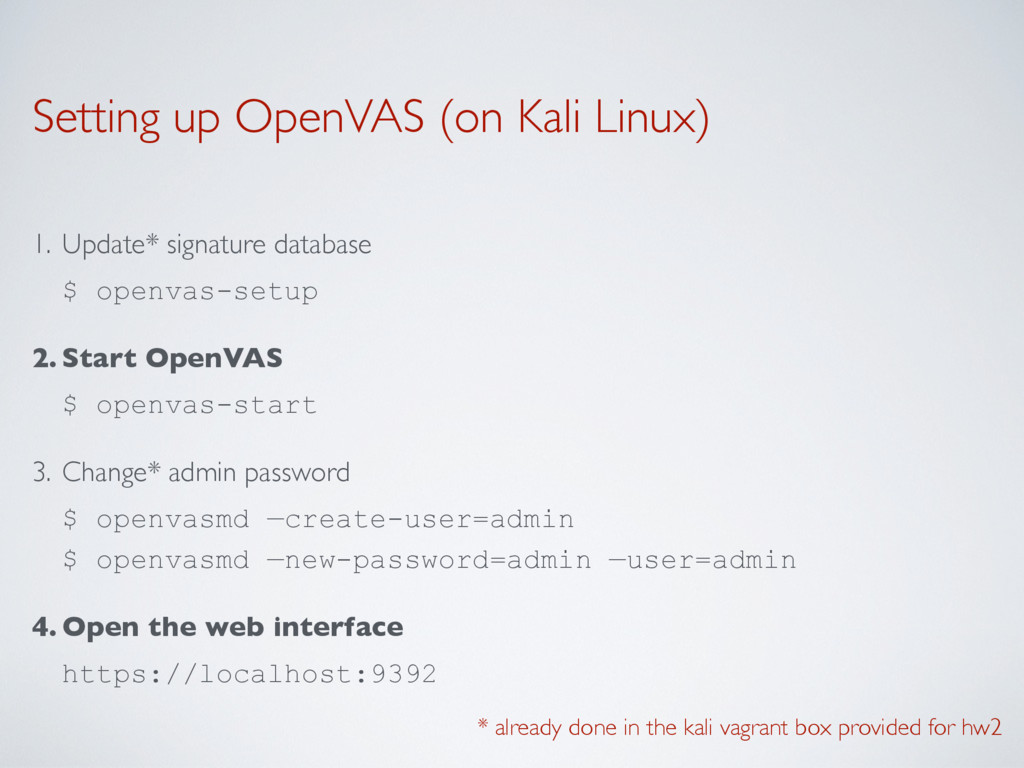
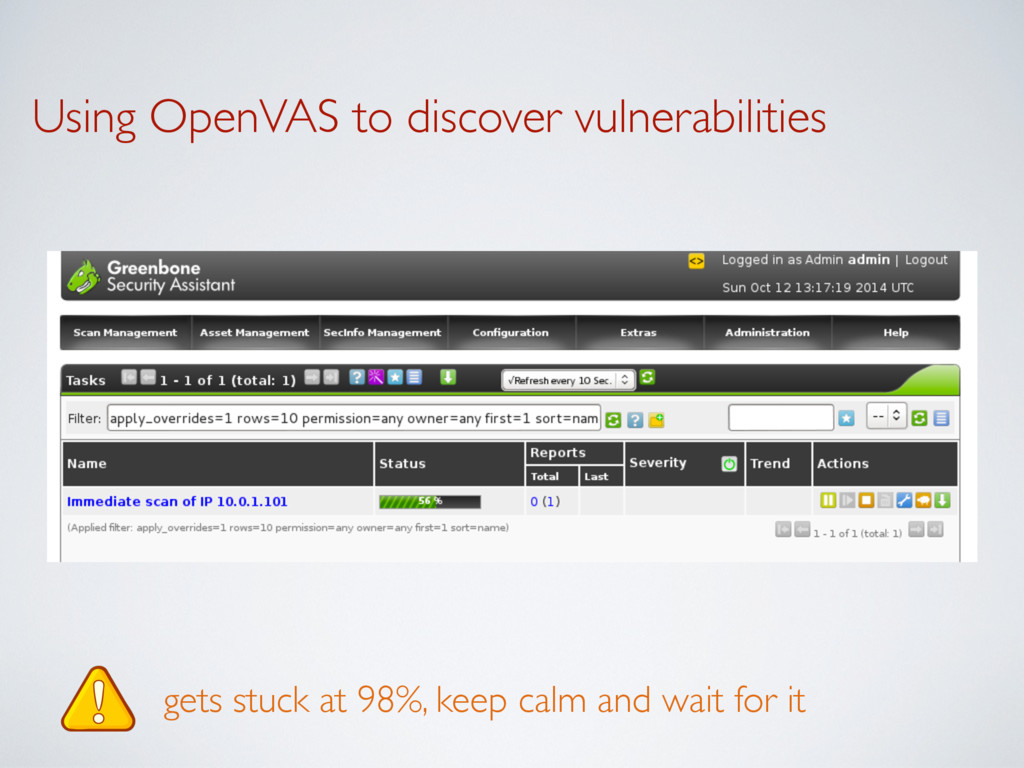
$ openvas-setup 2. Start OpenVAS $ openvas-start 3. Change* admin password $ openvasmd —create-user=admin $ openvasmd —new-password=admin —user=admin 4. Open the web interface https://localhost:9392 * already done in the kali vagrant box provided for hw2
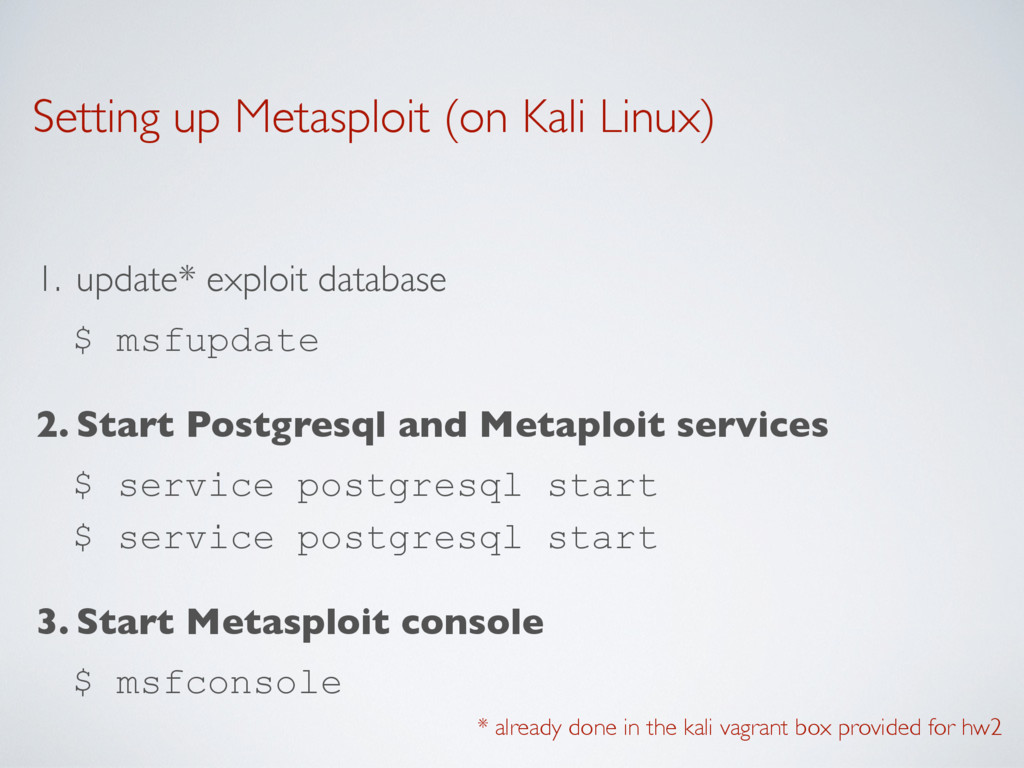
$ msfupdate 2. Start Postgresql and Metaploit services $ service postgresql start $ service postgresql start 3. Start Metasploit console $ msfconsole * already done in the kali vagrant box provided for hw2


 thierrysans
 chriscoyier
 eitanlees
 erikaheidi
 mraible
 auna
 twada
 nikkihalliwell
 paigeccino
 lcolladotor
 cromwellryan
 jonoalderson
 signer