Share
Embed
Introduction to SELinux
Wait! Don't turn off the SELinux too quickly.
Let's get what is access control and what is SELinux.
bighead
September 03, 2019
Transcript
58 slides
-
Copyright 2017 ITRI ⼯工業技術研究院 About Me 王禹軒 (Bighead) • 中央⼤大學
Advanced Defense Lab • 打胖 • ⼯工研院 Intern • Whitelist 1.0 PoC • Hypervisor-based Whitelist (page verification) • SELinux • HITCON 101 Sharing -
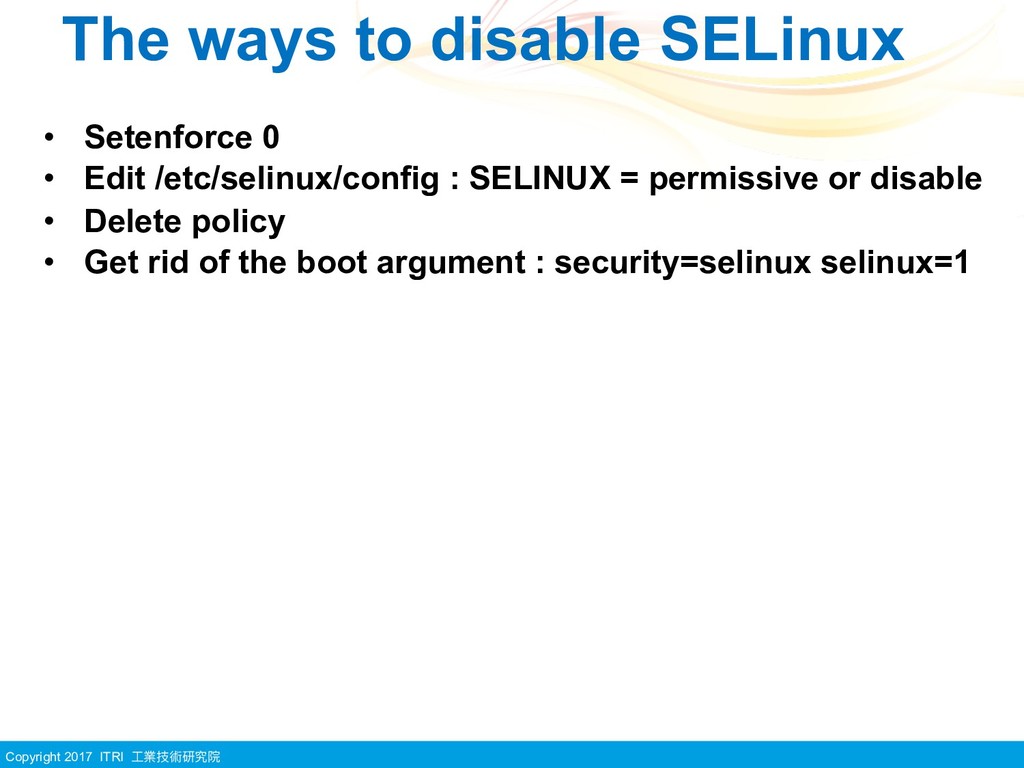
Copyright 2017 ITRI ⼯工業技術研究院 The ways to disable SELinux •
Setenforce 0 • Edit /etc/selinux/config : SELINUX = permissive or disable • Delete policy • Get rid of the boot argument : security=selinux selinux=1 -
Copyright 2017 ITRI ⼯工業技術研究院 The ways to disable SELinux •
Setenforce 0 • Edit /etc/selinux/config : SELINUX = permissive or disable • Delete policy • Get rid of the boot argument : security=selinux selinux=1 • Do NOT use default SELinux-enabled distro (CentOS) -
Copyright 2017 ITRI ⼯工業技術研究院 The ways to disable SELinux •
Setenforce 0 • Edit /etc/selinux/config : SELINUX = permissive or disable • Delete policy • Get rid of the boot argument : security=selinux selinux=1 • Do NOT use default SELinux-enabled distro (CentOS) SELinux gives you the power to close it -
Copyright 2017 ITRI ⼯工業技術研究院 Don’t be Afraid of SELinux •
60 page survey paper • 400 page SELinux Notebook • Makefile survey • Policy Set survey • Powerful mentor -
Copyright 2017 ITRI ⼯工業技術研究院 Don’t be Afraid of SELinux •
60 page survey paper • 400 page SELinux Notebook • Makefile survey • Policy Set survey • Powerful mentor Don’t be afraid! It is not scary -
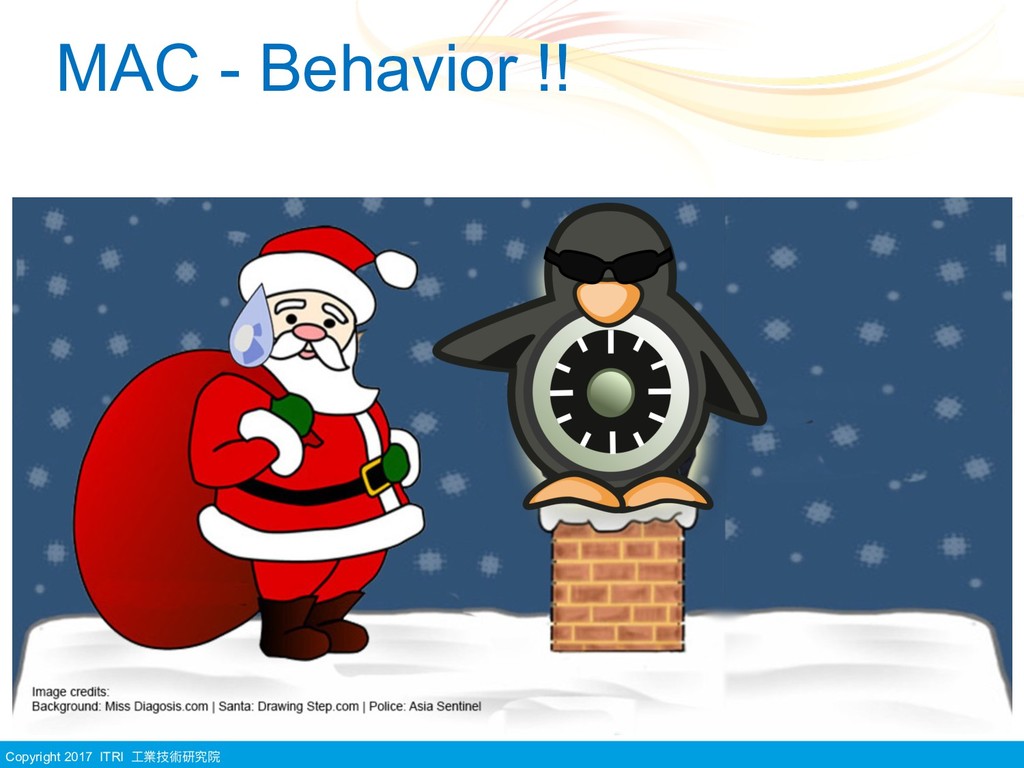
Copyright 2017 ITRI ⼯工業技術研究院 Trust Lovely Santa Claus Reference :
Santa Claus PNG Transparent Image - PngPix -
Copyright 2017 ITRI ⼯工業技術研究院 Trust Evil Santa Claus !? Futurama
: Robot Santa Claus -
Copyright 2017 ITRI ⼯工業技術研究院 Why Access Control ? • Goal:
Protect data and resources from unauthorized use ◦ Confidentiality (or secrecy) : Related to disclosure of information ◦ Integrity : Related to modification of information ◦ Availability : Related to denial of access to information Reference: Security Awareness Posters -
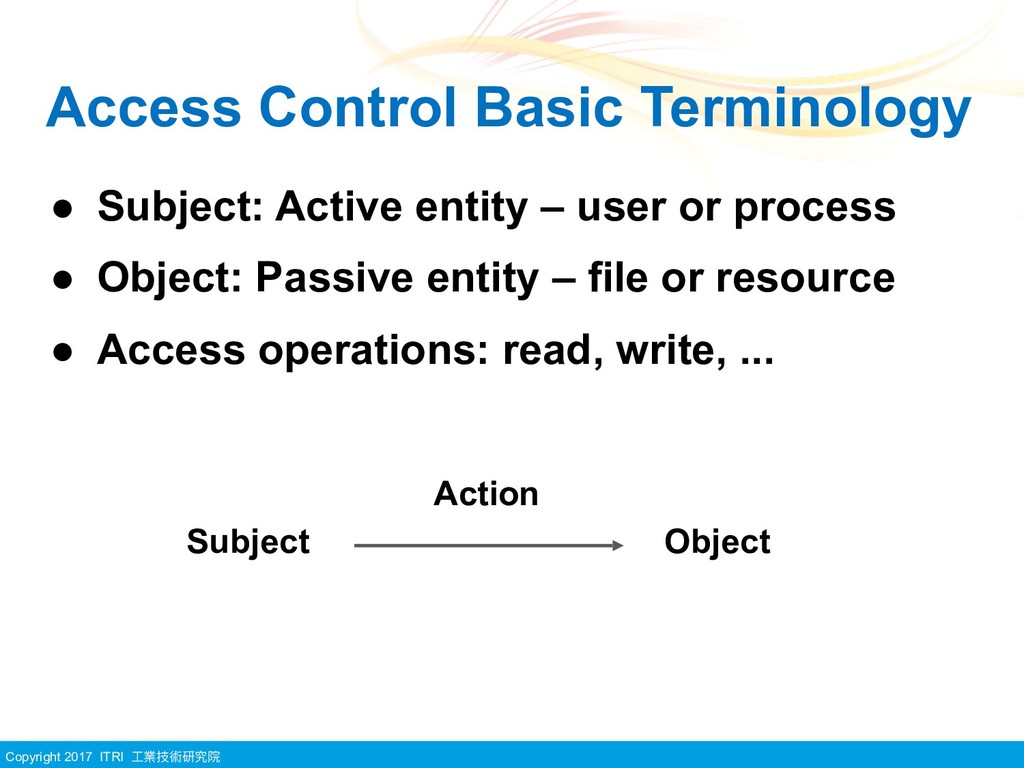
Copyright 2017 ITRI ⼯工業技術研究院 Access Control Basic Terminology • Subject:
Active entity – user or process • Object: Passive entity – file or resource • Access operations: read, write, ... Subject Object Action -
Copyright 2017 ITRI ⼯工業技術研究院 Access Control is Hard Because •
Access control requirements are domain-specific • Generic approaches over-generalize • Access control requirements can change • Anyone could be an administrator Reference : https://profile.cheezburger.com/imaguid/ -
Copyright 2017 ITRI ⼯工業技術研究院 Basic Concepts of Different Access Control
Policies • Discretionary (DAC): (authorization-based) policies control access based on the identity of the requestor and on access rules stating what requestors are (or are not) allowed to do. • Mandatory (MAC): policies control access based on mandated regulations determined by a central authority. -
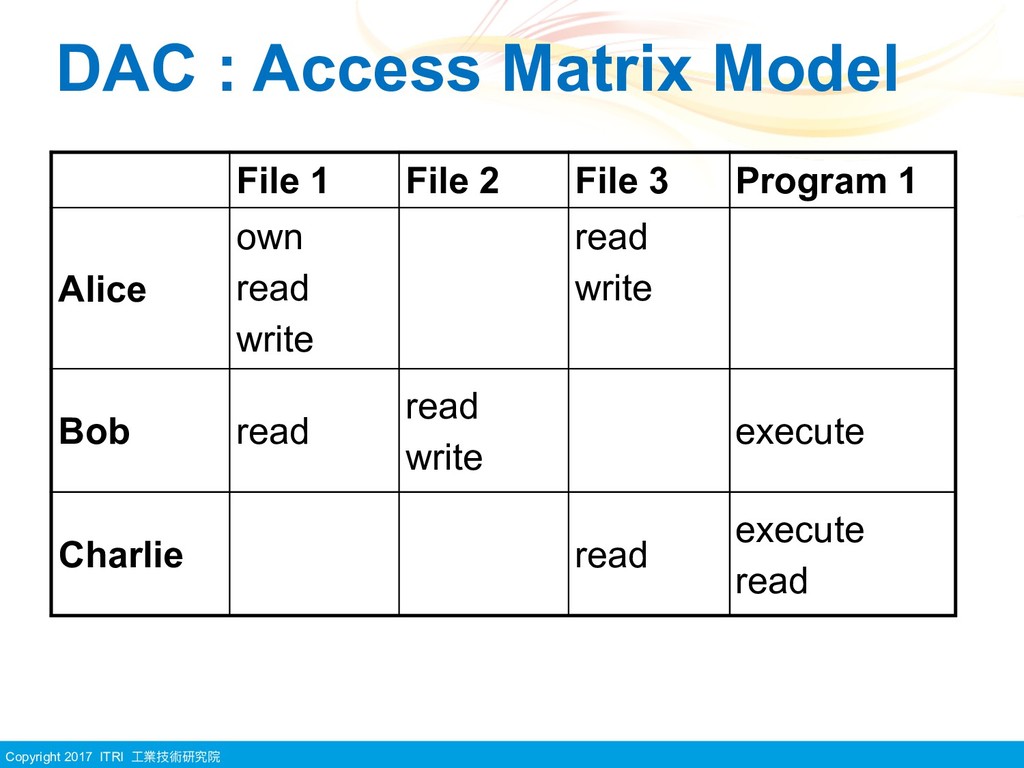
Copyright 2017 ITRI ⼯工業技術研究院 DAC : Access Matrix Model File
1 File 2 File 3 Program 1 Alice own read write read write Bob read read write execute Charlie read execute read -
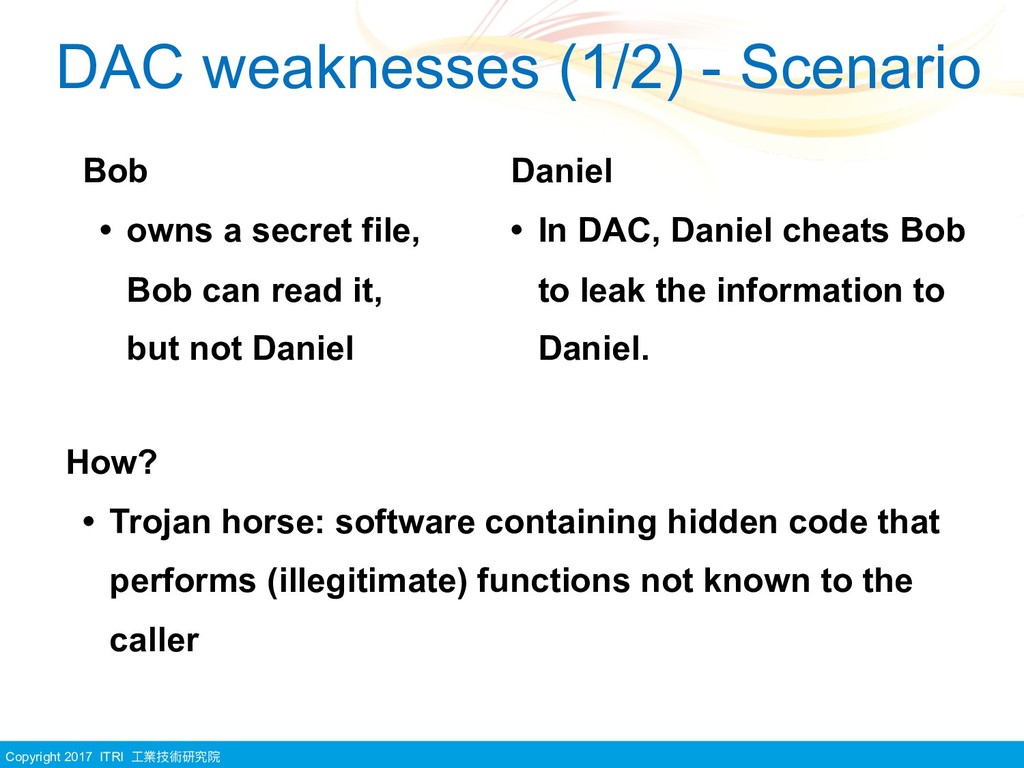
Copyright 2017 ITRI ⼯工業技術研究院 DAC weaknesses (1/2) - Scenario Bob
• owns a secret file, Bob can read it, but not Daniel How? • Trojan horse: software containing hidden code that performs (illegitimate) functions not known to the caller Daniel • In DAC, Daniel cheats Bob to leak the information to Daniel. -
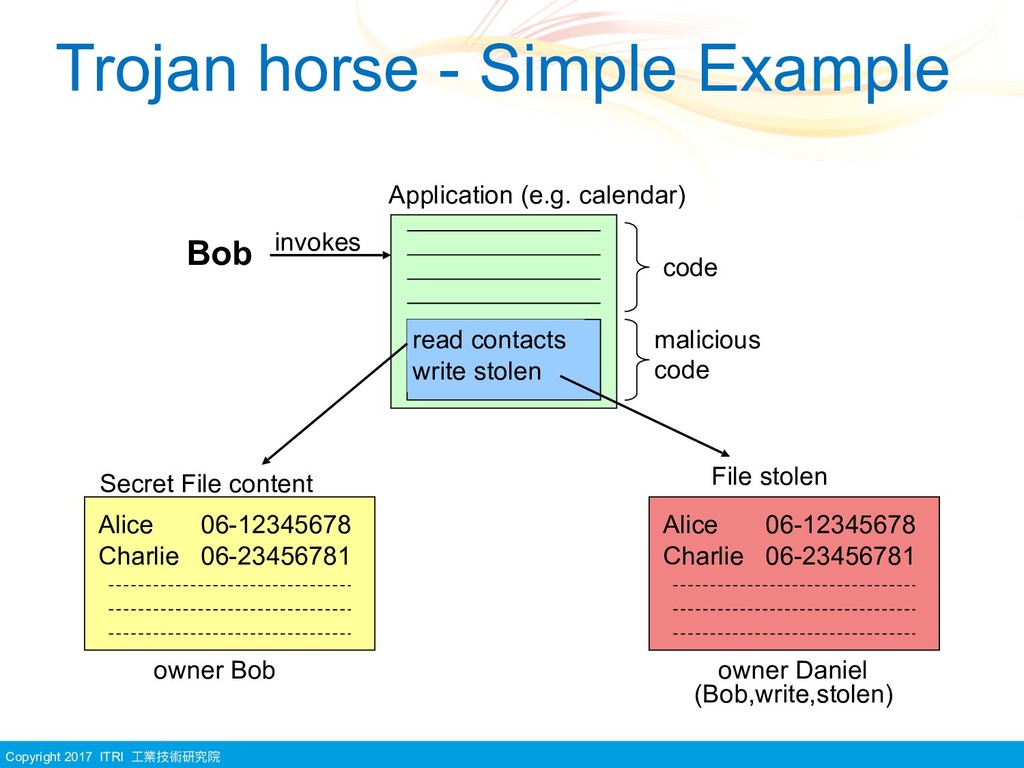
Copyright 2017 ITRI ⼯工業技術研究院 Trojan horse - Simple Example Bob
invokes Application (e.g. calendar) read contacts write stolen code malicious code Secret File content owner Bob Alice 06-12345678 Charlie 06-23456781 File stolen owner Daniel Alice 06-12345678 Charlie 06-23456781 (Bob,write,stolen) -
Copyright 2017 ITRI ⼯工業技術研究院 DAC weaknesses (2/2) • DAC constraints
only identity, no control on what happens to information during execution. • No separation of User identity and execution instance. • Trojan Horses exploit access privileges of calling subjects identity. -
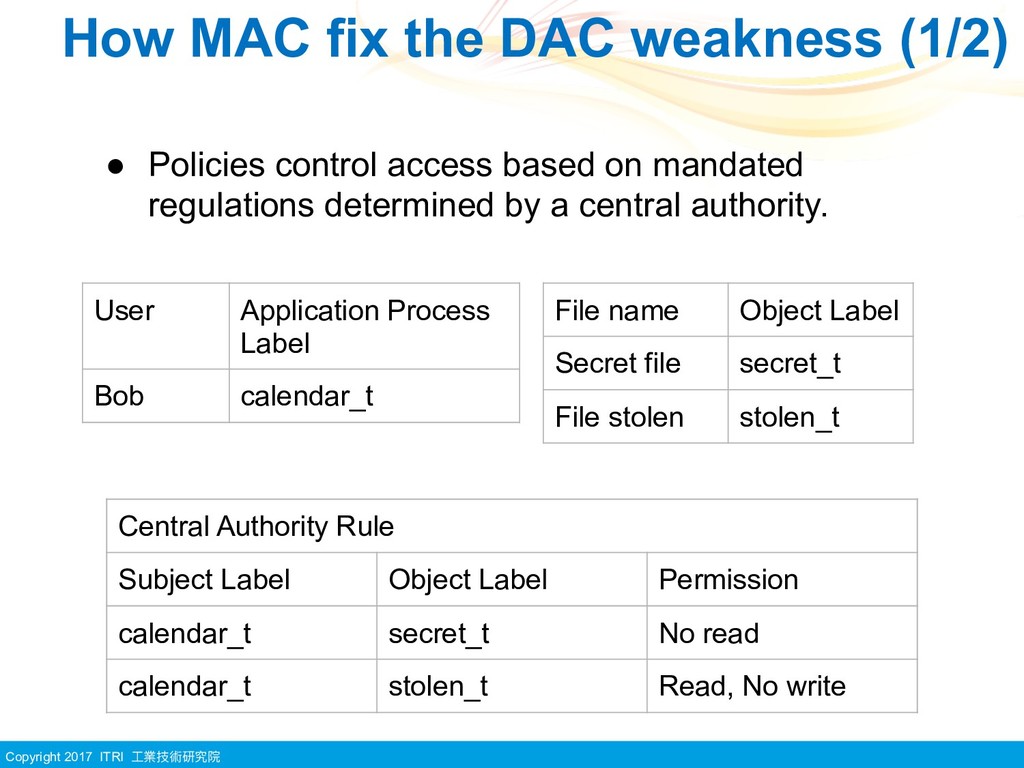
Copyright 2017 ITRI ⼯工業技術研究院 • Policies control access based on
mandated regulations determined by a central authority. User Application Process Label Bob calendar_t Central Authority Rule Subject Label Object Label Permission calendar_t secret_t No read calendar_t stolen_t Read, No write File name Object Label Secret file secret_t File stolen stolen_t How MAC fix the DAC weakness (1/2) -
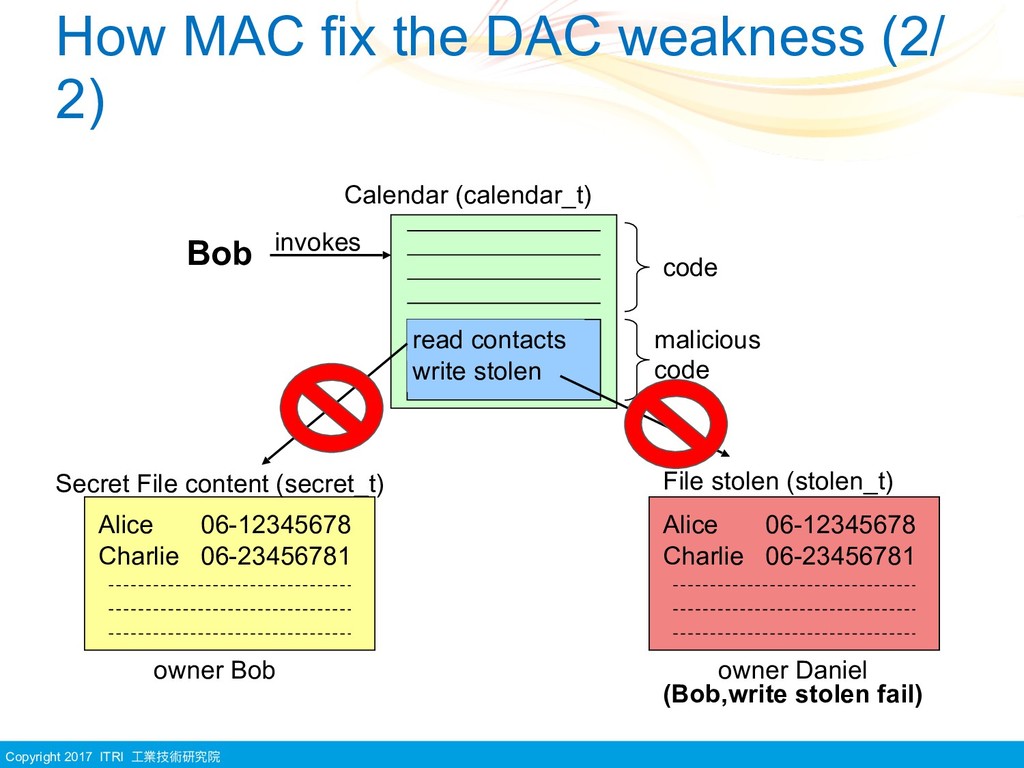
Copyright 2017 ITRI ⼯工業技術研究院 How MAC fix the DAC weakness
(2/ 2) Bob invokes Calendar (calendar_t) read contacts write stolen code malicious code Secret File content (secret_t) owner Bob Alice 06-12345678 Charlie 06-23456781 File stolen (stolen_t) owner Daniel Alice 06-12345678 Charlie 06-23456781 (Bob,write stolen fail) -
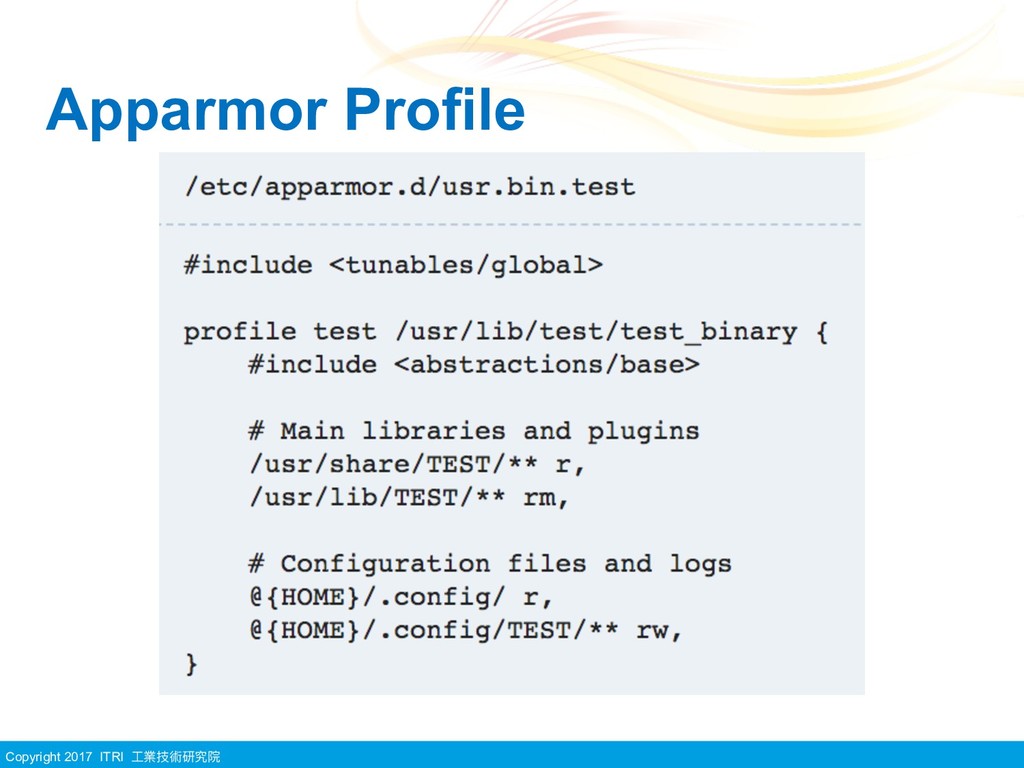
Copyright 2017 ITRI ⼯工業技術研究院 Apparmor • Path-based system : filesystem
no need to support extended attribute • Per-program profile : describe what program can do. • Concept of Different Subject Domain : If you want a different Subject Domain, you should create a hard link & rename the program & create a new profile for it. -
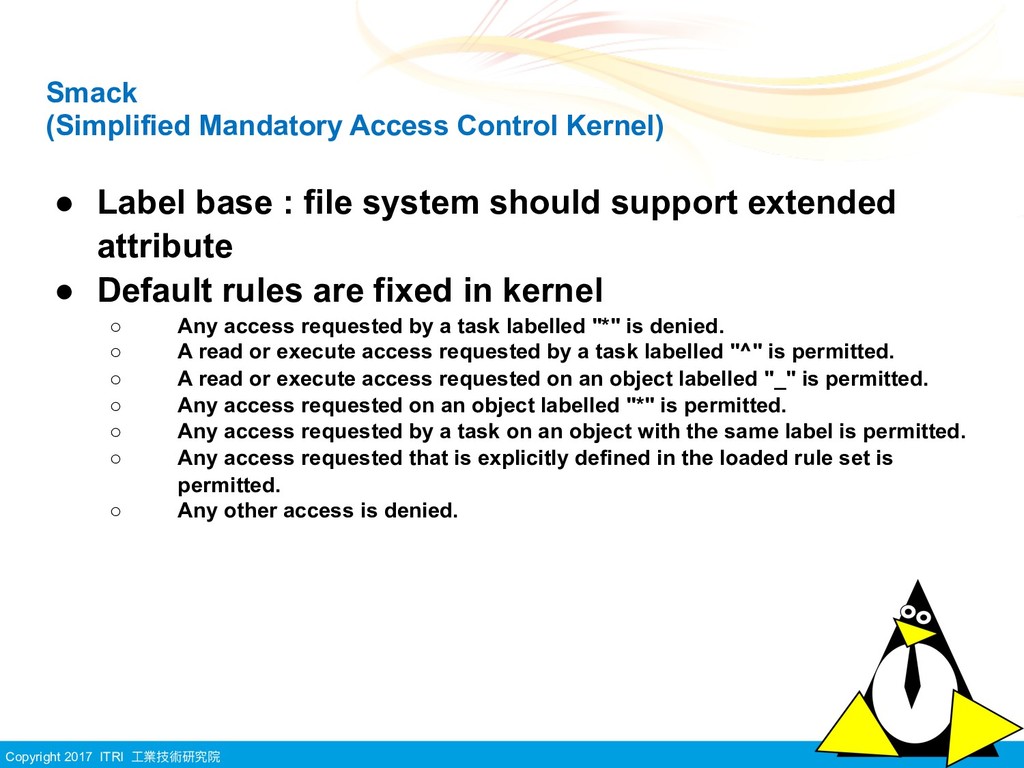
Copyright 2017 ITRI ⼯工業技術研究院 Smack (Simplified Mandatory Access Control Kernel)
• Label base : file system should support extended attribute • Default rules are fixed in kernel ◦ Any access requested by a task labelled "*" is denied. ◦ A read or execute access requested by a task labelled "^" is permitted. ◦ A read or execute access requested on an object labelled "_" is permitted. ◦ Any access requested on an object labelled "*" is permitted. ◦ Any access requested by a task on an object with the same label is permitted. ◦ Any access requested that is explicitly defined in the loaded rule set is permitted. ◦ Any other access is denied. -
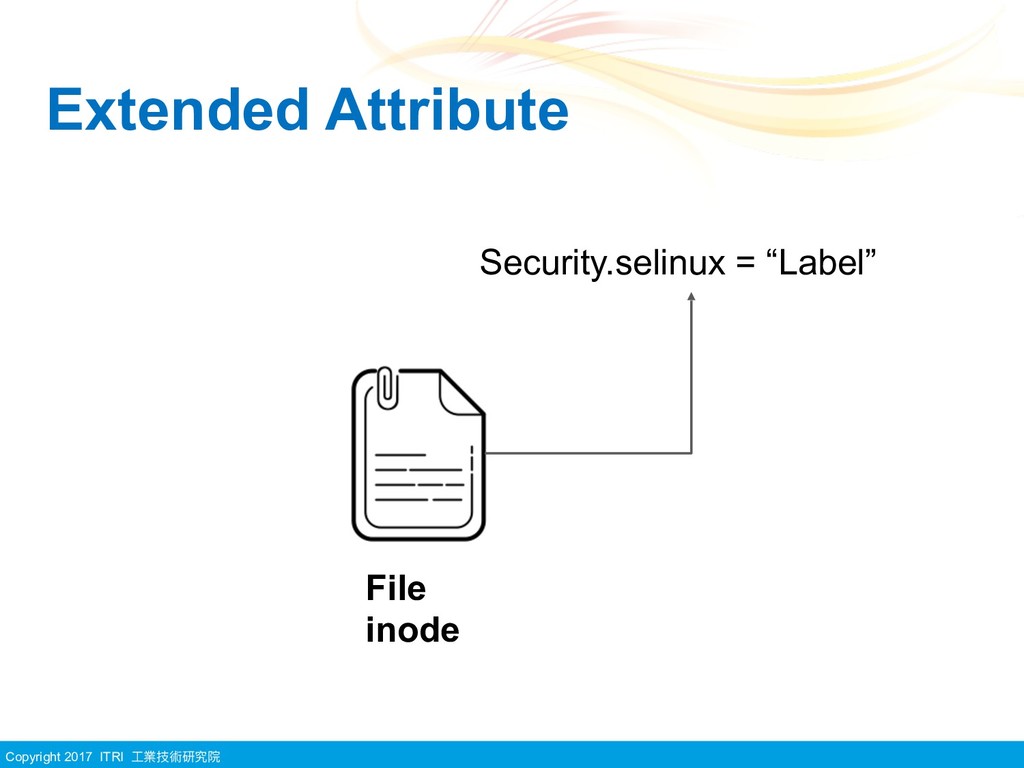
Copyright 2017 ITRI ⼯工業技術研究院 SELinux • Label base : file
system should support extended attribute • Finer granularity : • Different MAC model support : Type Enforcement, MCS, MLS, RBAC • Hard to learn Subject Object:Class Action -
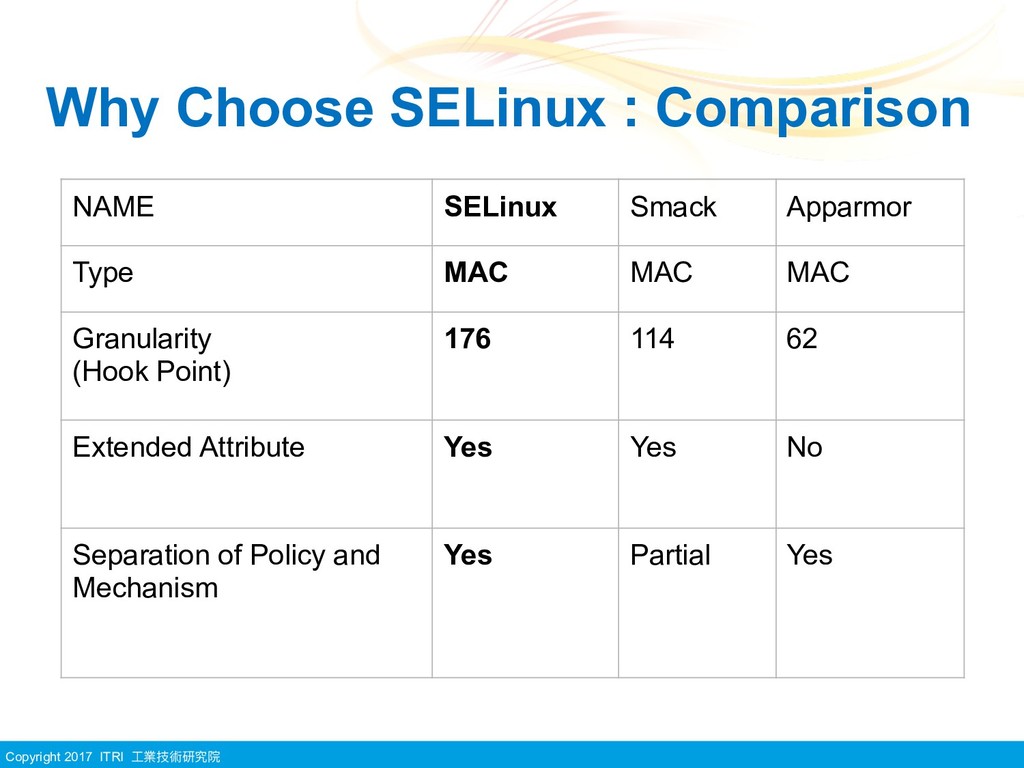
Copyright 2017 ITRI ⼯工業技術研究院 Why Choose SELinux : Comparison NAME
SELinux Smack Apparmor Type MAC MAC MAC Granularity (Hook Point) 176 114 62 Extended Attribute Yes Yes No Separation of Policy and Mechanism Yes Partial Yes -
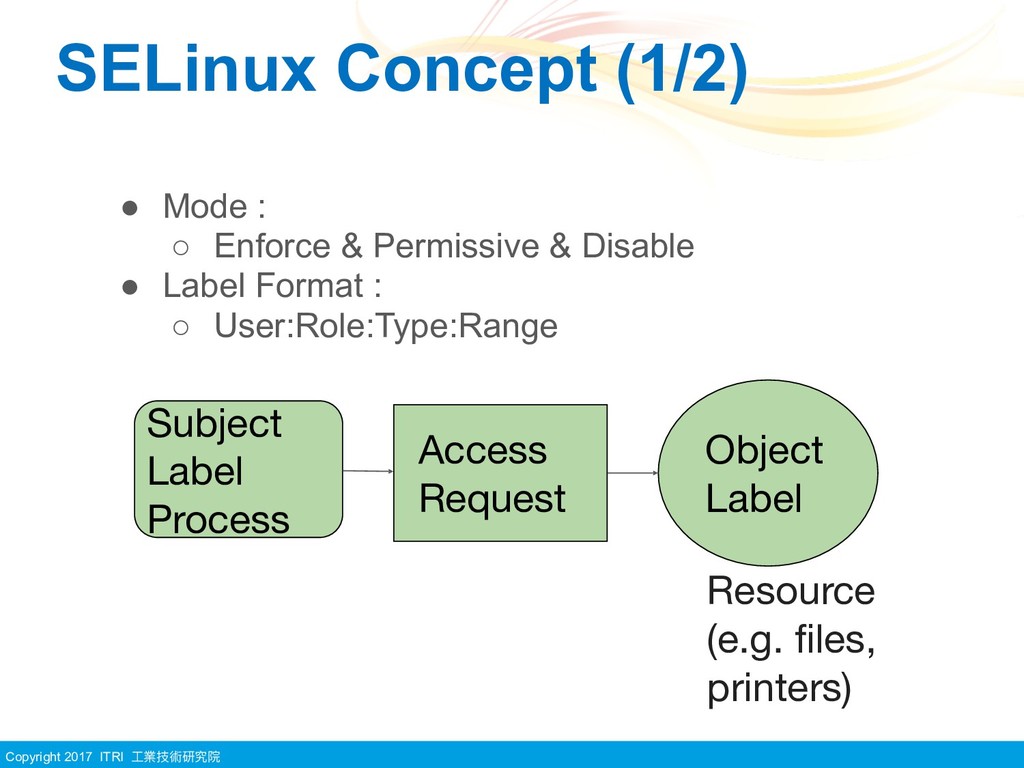
Copyright 2017 ITRI ⼯工業技術研究院 SELinux Concept (1/2) Object Label Resource
(e.g. files, printers) Access Request Subject Label Process • Mode : ◦ Enforce & Permissive & Disable • Label Format : ◦ User:Role:Type:Range -
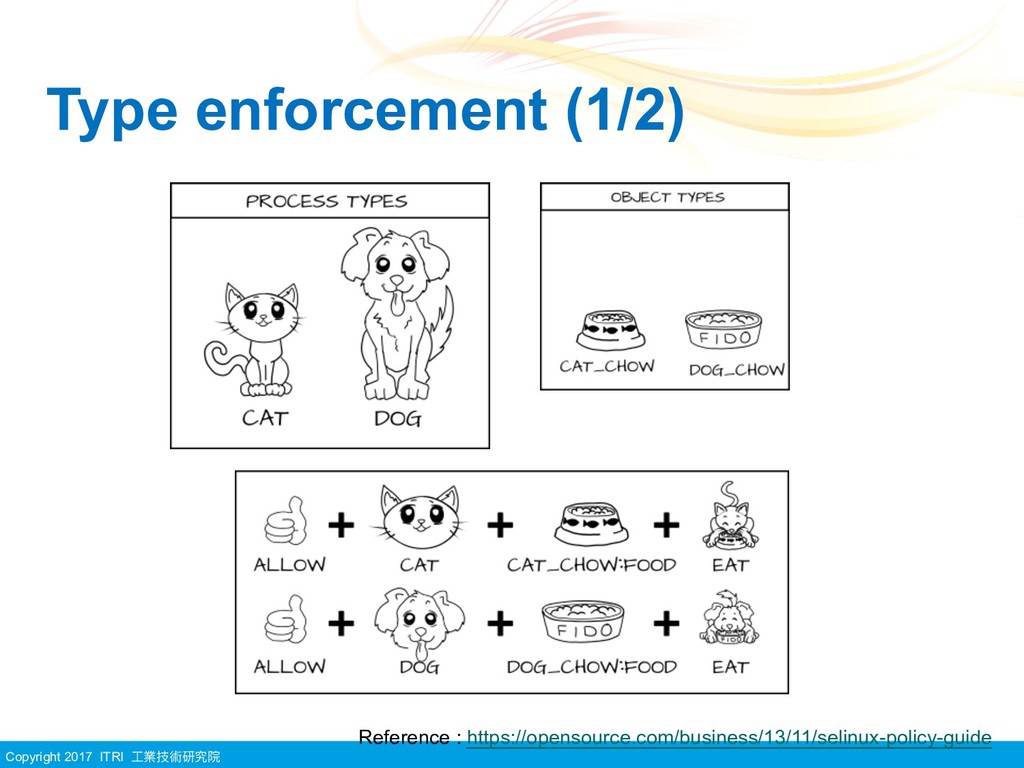
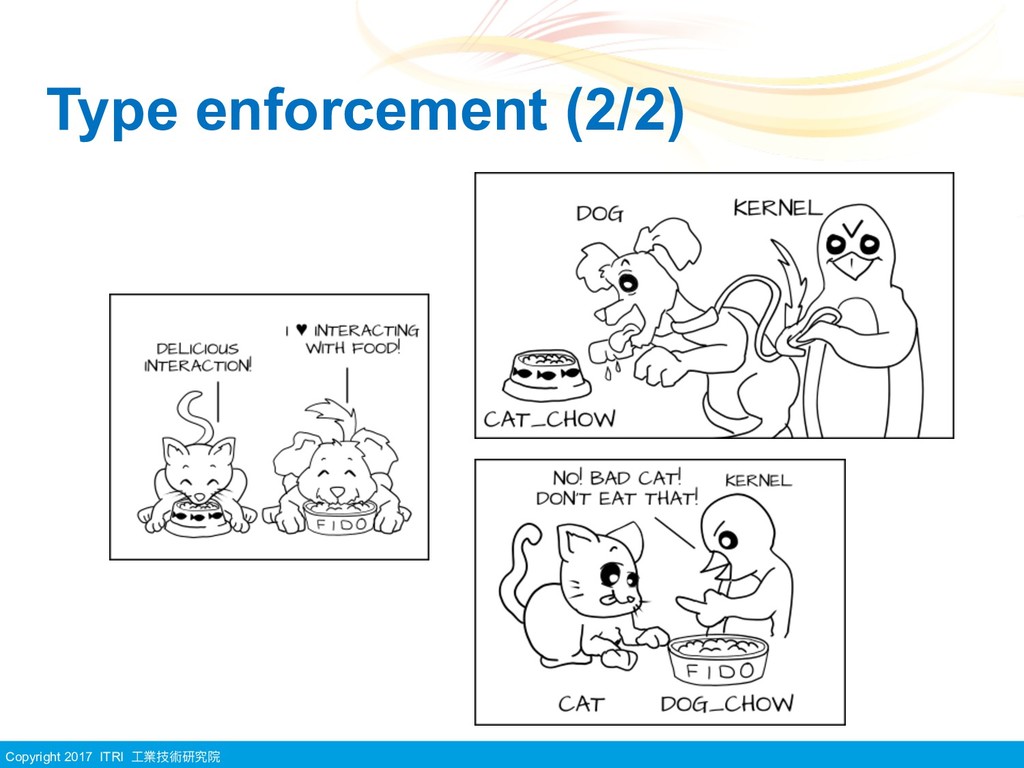
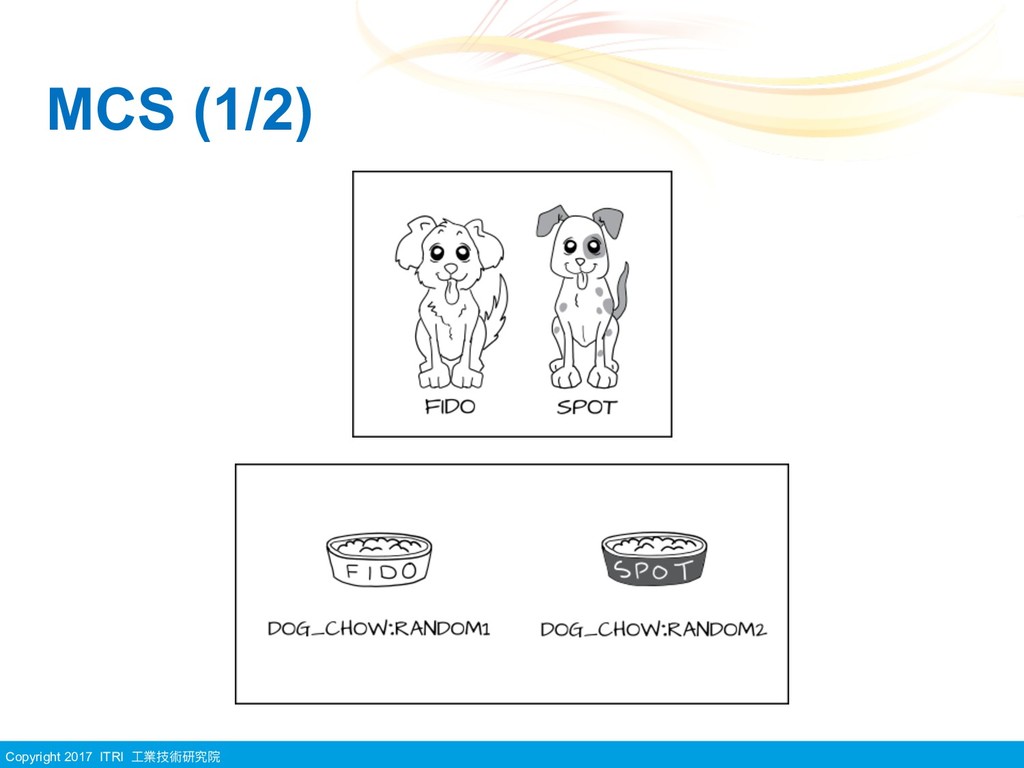
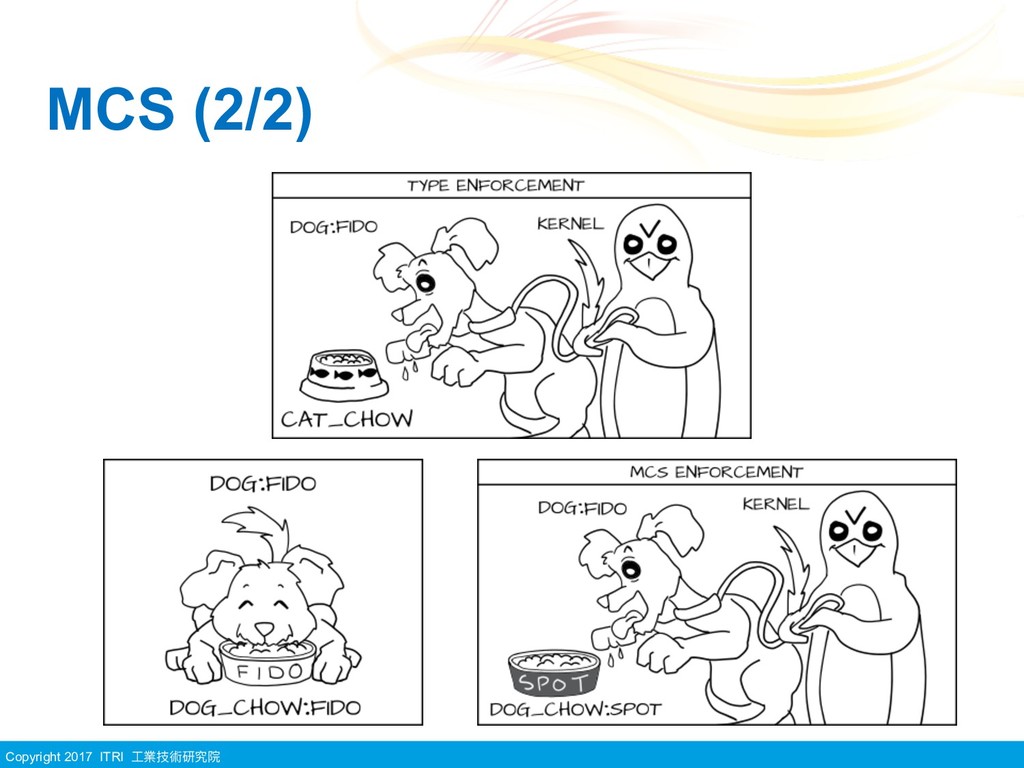
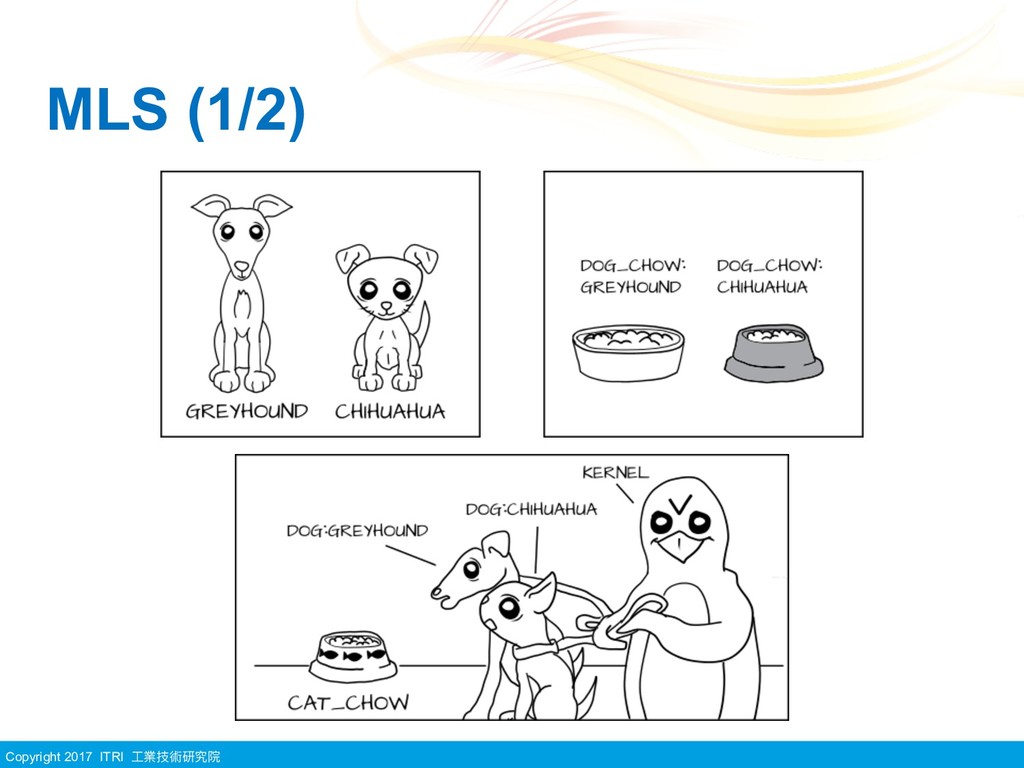
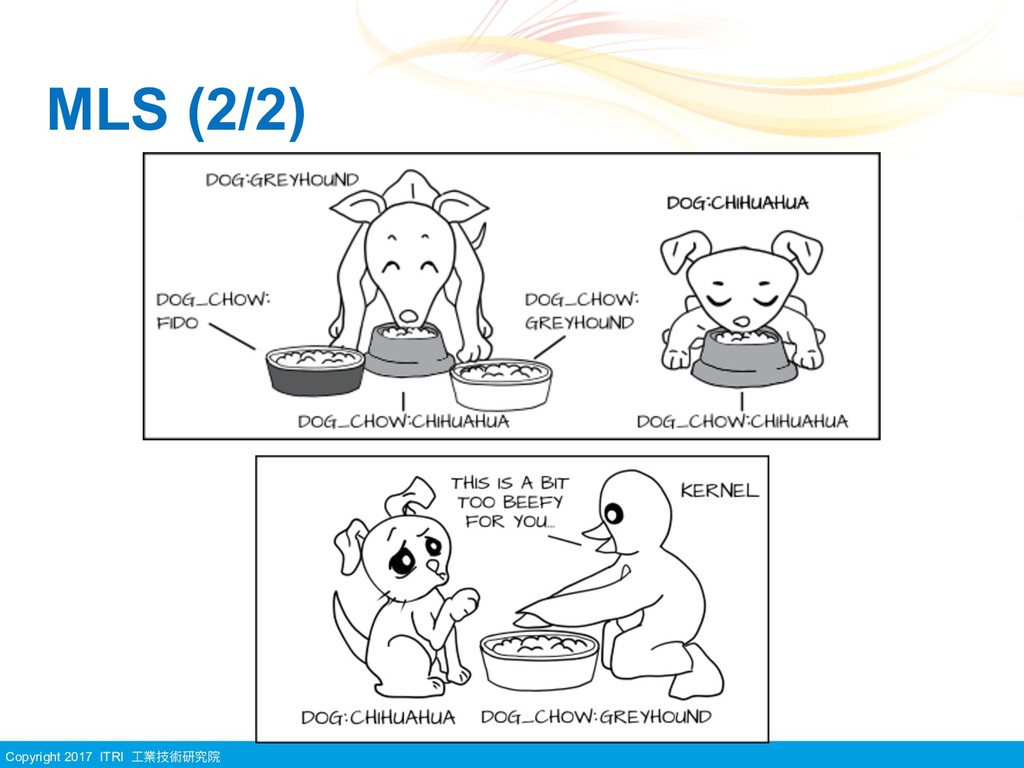
Copyright 2017 ITRI ⼯工業技術研究院 SELinux Concept Outline (2/2) • Type
Enforcement (TE): Type Enforcement is the primary mechanism of access control used in the targeted policy • Multi-Category Security(MCS): An extension of Multi- Level Security. • Multi-Level Security (MLS): Not commonly used and often hidden in the default targeted policy. -
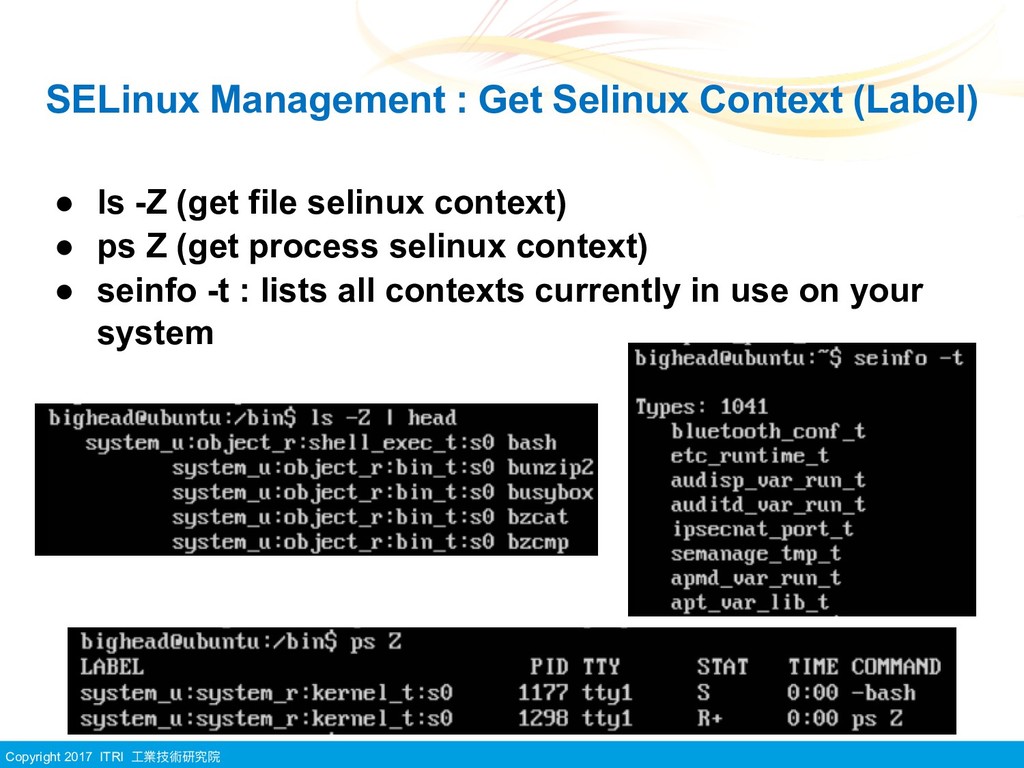
Copyright 2017 ITRI ⼯工業技術研究院 SELinux Management : Get Selinux Context
(Label) • ls -Z (get file selinux context) • ps Z (get process selinux context) • seinfo -t : lists all contexts currently in use on your system -
Copyright 2017 ITRI ⼯工業技術研究院 SELinux Management : 2 Step Used
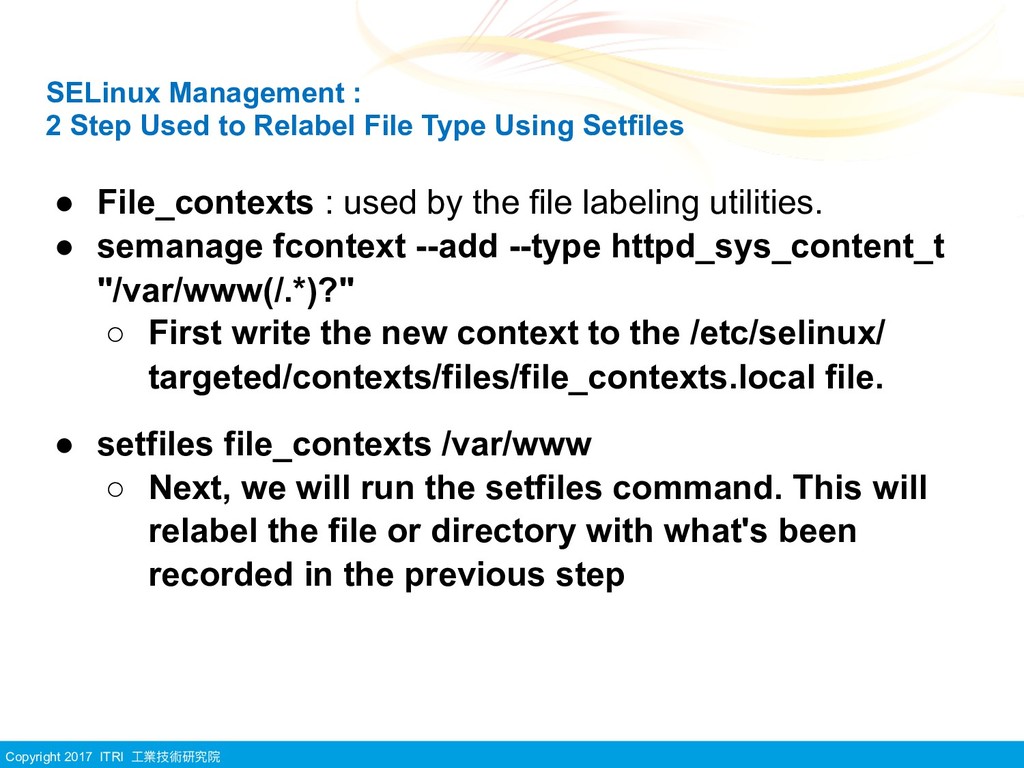
to Relabel File Type Using Setfiles • File_contexts : used by the file labeling utilities. • semanage fcontext --add --type httpd_sys_content_t "/var/www(/.*)?" ◦ First write the new context to the /etc/selinux/ targeted/contexts/files/file_contexts.local file. • setfiles file_contexts /var/www ◦ Next, we will run the setfiles command. This will relabel the file or directory with what's been recorded in the previous step -
Copyright 2017 ITRI ⼯工業技術研究院 SELinux Management : Command to Change
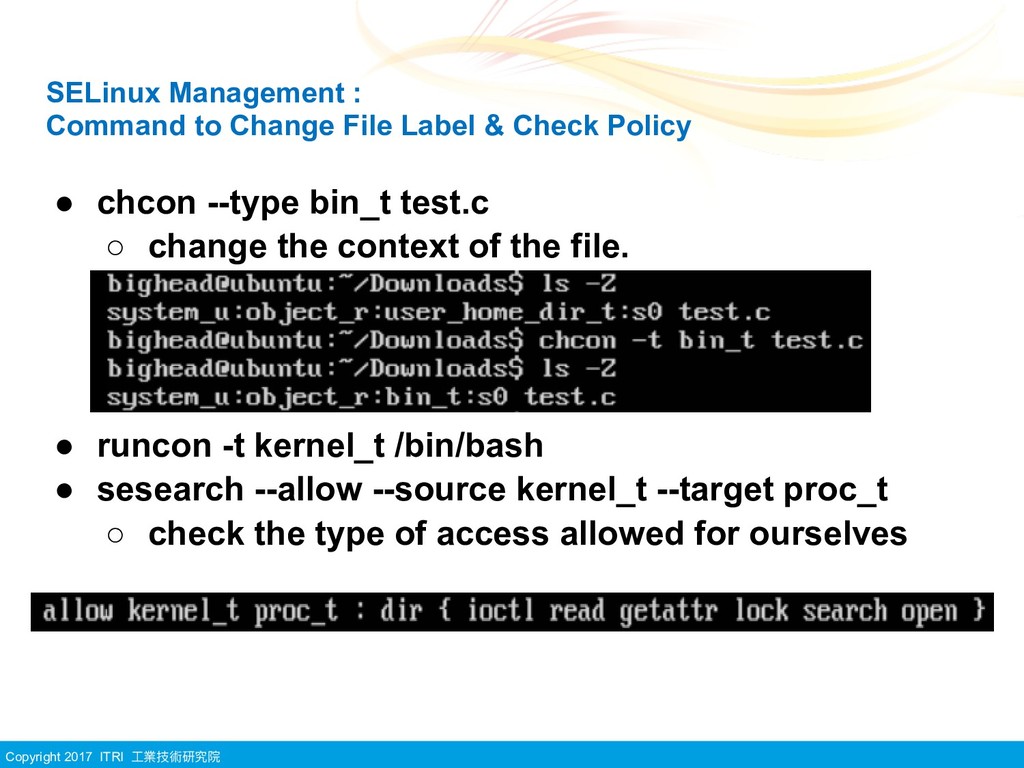
File Label & Check Policy • chcon --type bin_t test.c ◦ change the context of the file. • runcon -t kernel_t /bin/bash • sesearch --allow --source kernel_t --target proc_t ◦ check the type of access allowed for ourselves -
Copyright 2017 ITRI ⼯工業技術研究院 SELinux Management : Boolean • List
Boolean : ◦ getsebool -a • Set Boolean : ◦ setsebool BooleanName (1 or 0) -
Copyright 2017 ITRI ⼯工業技術研究院 Troubleshoot : Audit Message (1/2) •
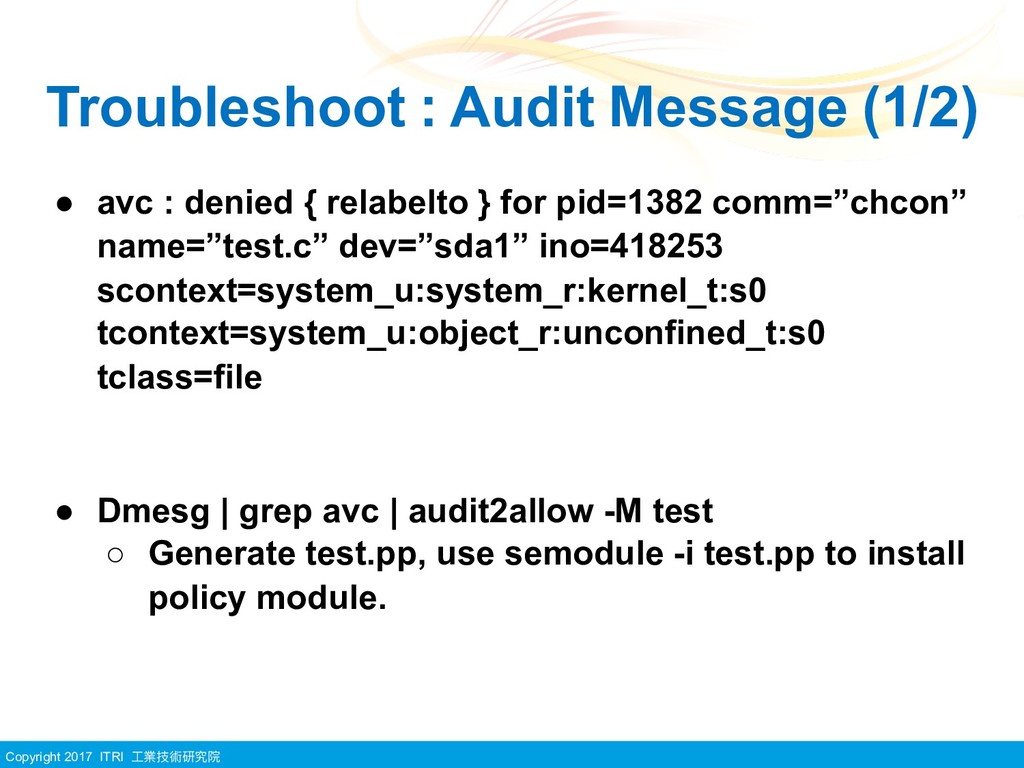
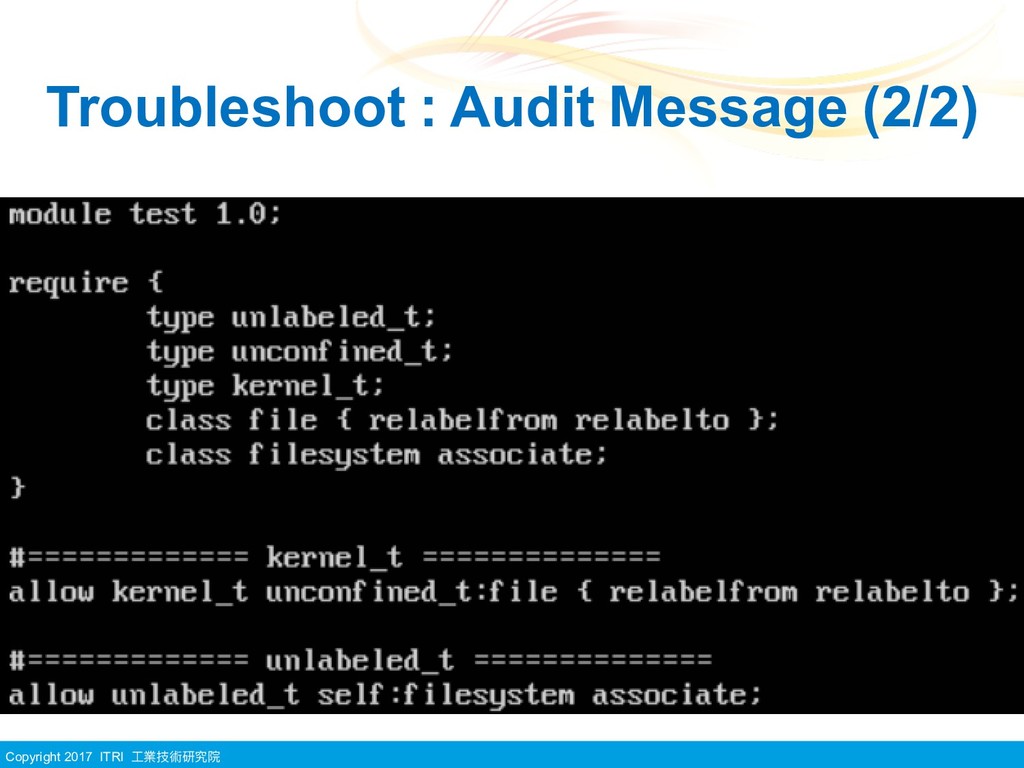
avc : denied { relabelto } for pid=1382 comm=”chcon” name=”test.c” dev=”sda1” ino=418253 scontext=system_u:system_r:kernel_t:s0 tcontext=system_u:object_r:unconfined_t:s0 tclass=file • Dmesg | grep avc | audit2allow -M test ◦ Generate test.pp, use semodule -i test.pp to install policy module. -
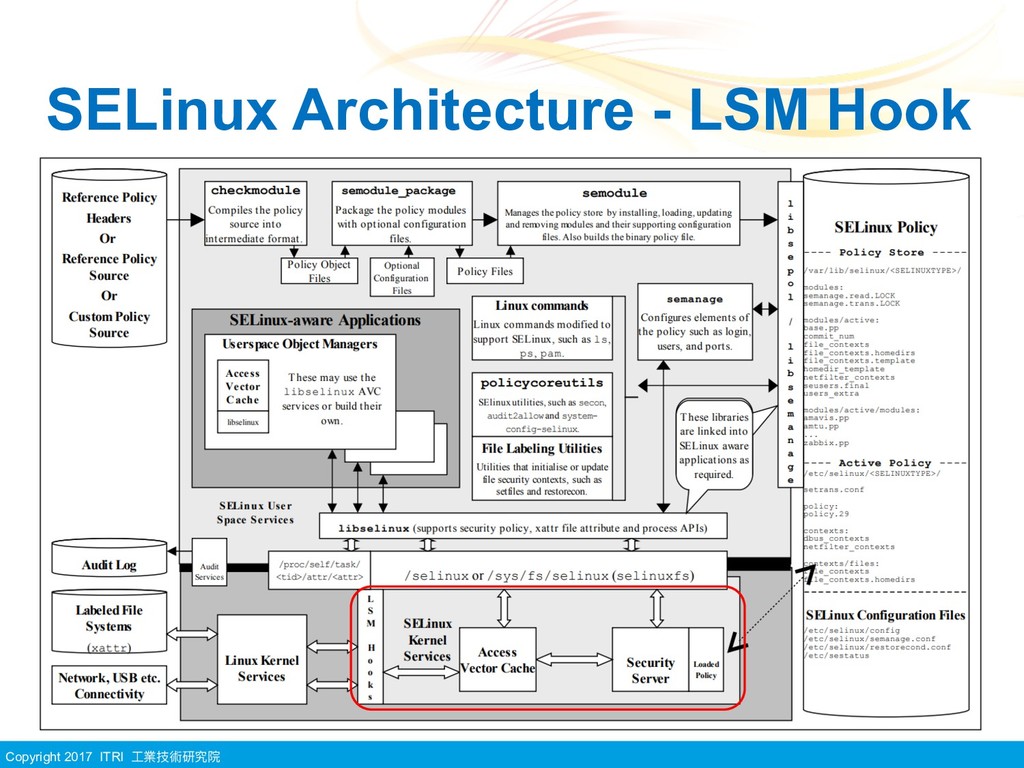
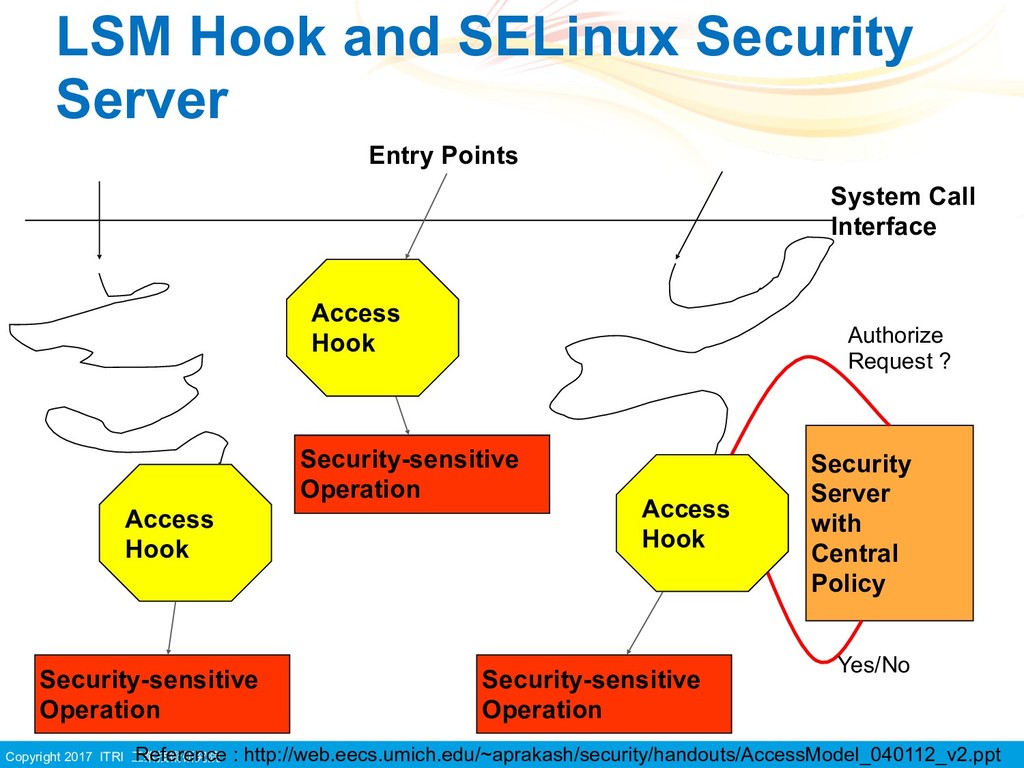
Copyright 2017 ITRI ⼯工業技術研究院 LSM Hook and SELinux Security Server
System Call Interface Entry Points Security Server with Central Policy Access Hook Security-sensitive Operation Authorize Request ? Yes/No Access Hook Access Hook Security-sensitive Operation Security-sensitive Operation Reference : http://web.eecs.umich.edu/~aprakash/security/handouts/AccessModel_040112_v2.ppt -
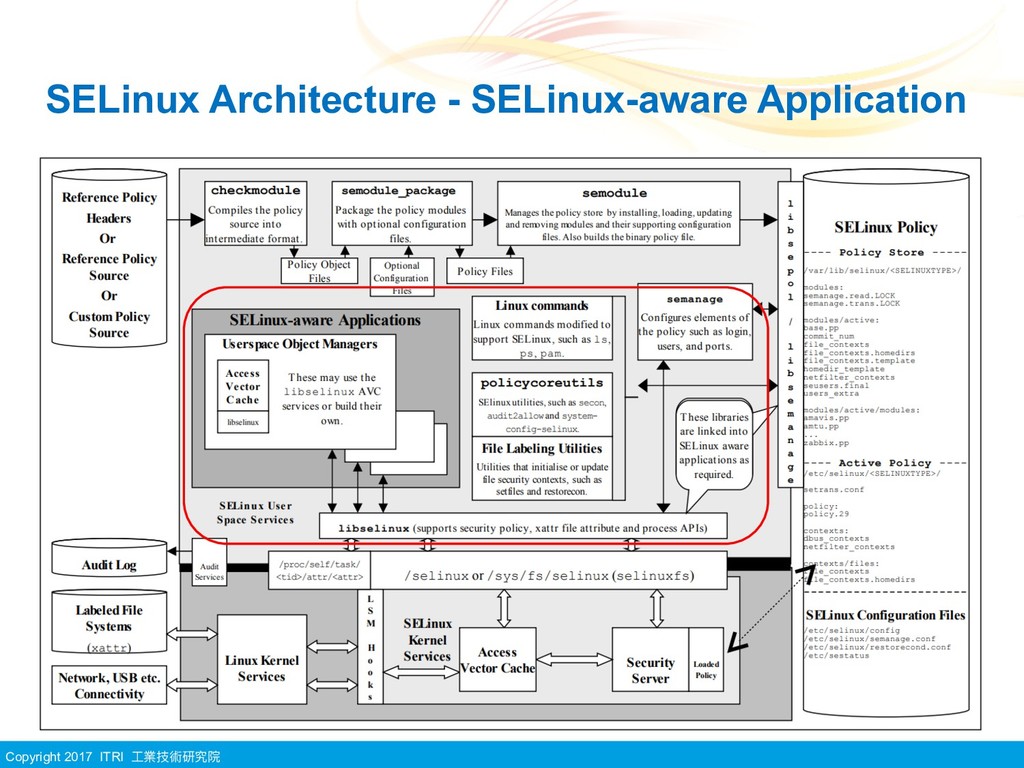
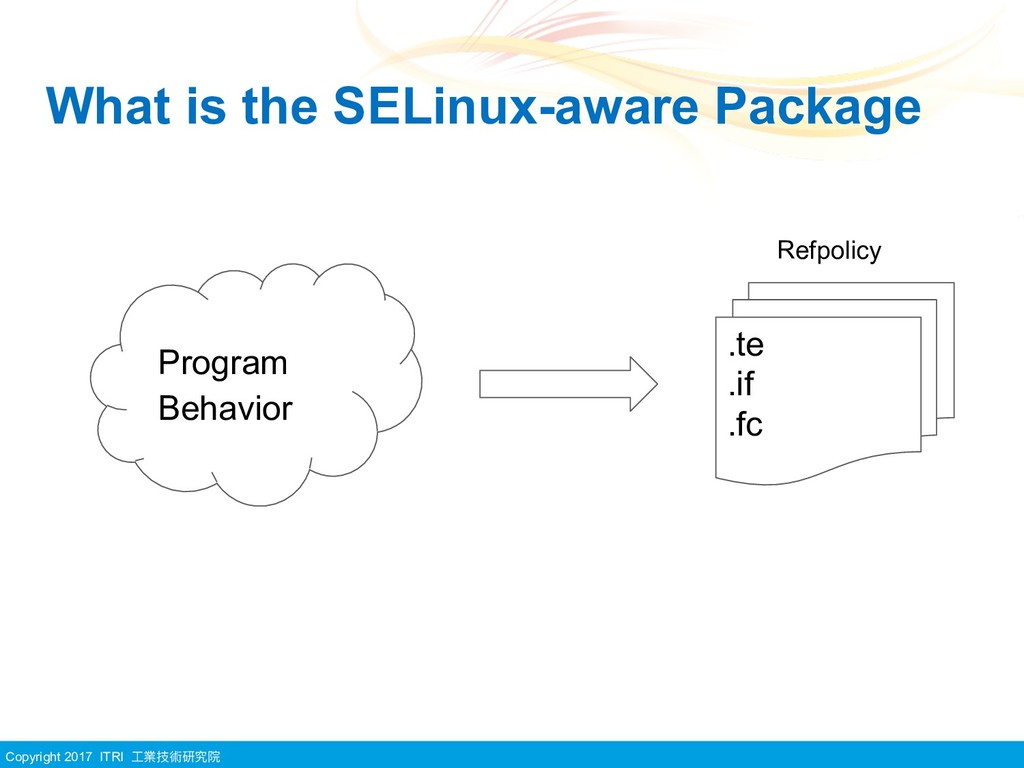
Copyright 2017 ITRI ⼯工業技術研究院 What is the SELinux-aware Package .te
.if .fc Refpolicy Program Behavior -
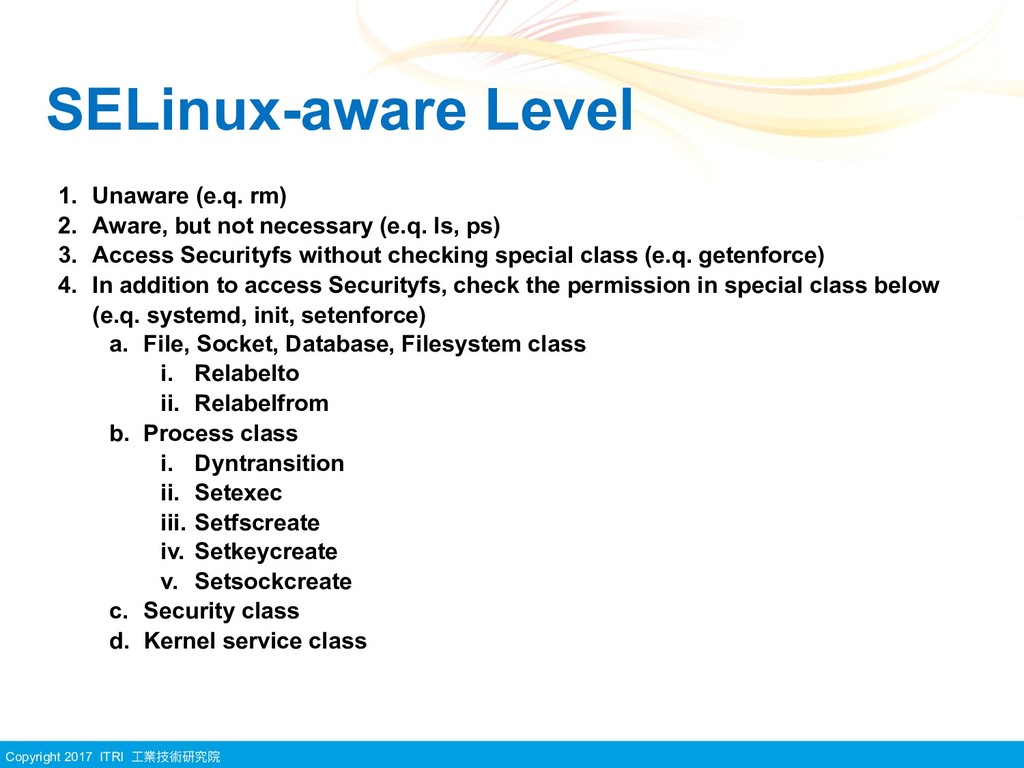
Copyright 2017 ITRI ⼯工業技術研究院 SELinux-aware Level 1. Unaware (e.q. rm)
2. Aware, but not necessary (e.q. ls, ps) 3. Access Securityfs without checking special class (e.q. getenforce) 4. In addition to access Securityfs, check the permission in special class below (e.q. systemd, init, setenforce) a. File, Socket, Database, Filesystem class i. Relabelto ii. Relabelfrom b. Process class i. Dyntransition ii. Setexec iii. Setfscreate iv. Setkeycreate v. Setsockcreate c. Security class d. Kernel service class -
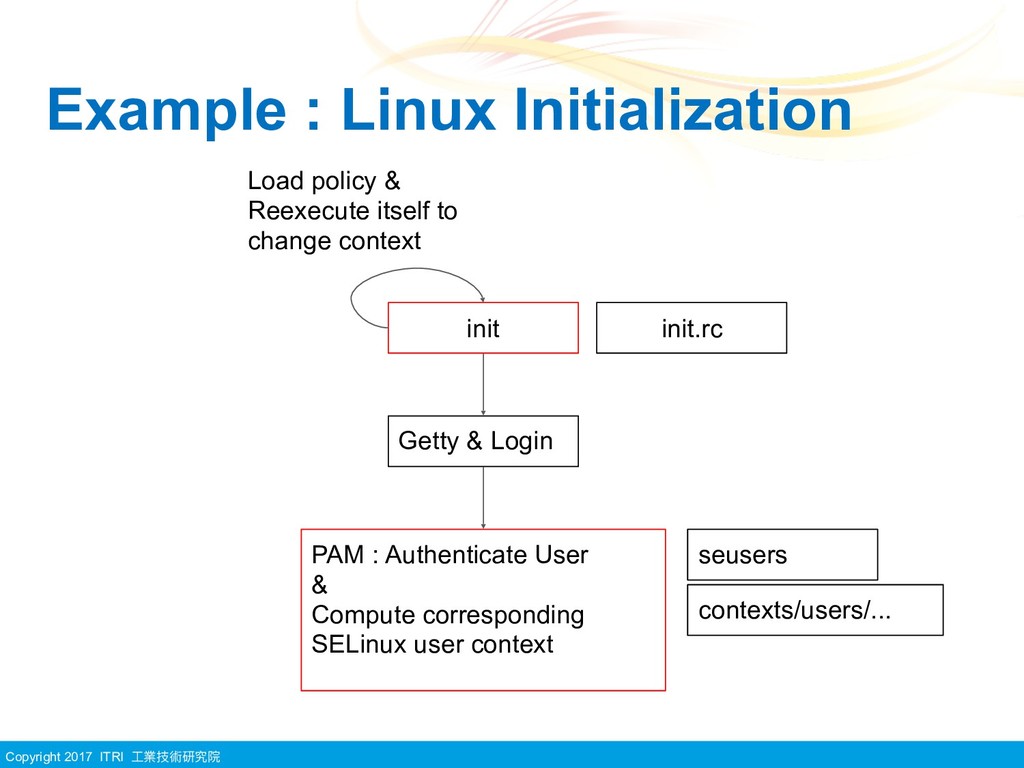
Copyright 2017 ITRI ⼯工業技術研究院 Example : Linux Initialization init Getty
& Login init.rc PAM : Authenticate User & Compute corresponding SELinux user context Load policy & Reexecute itself to change context seusers contexts/users/... -
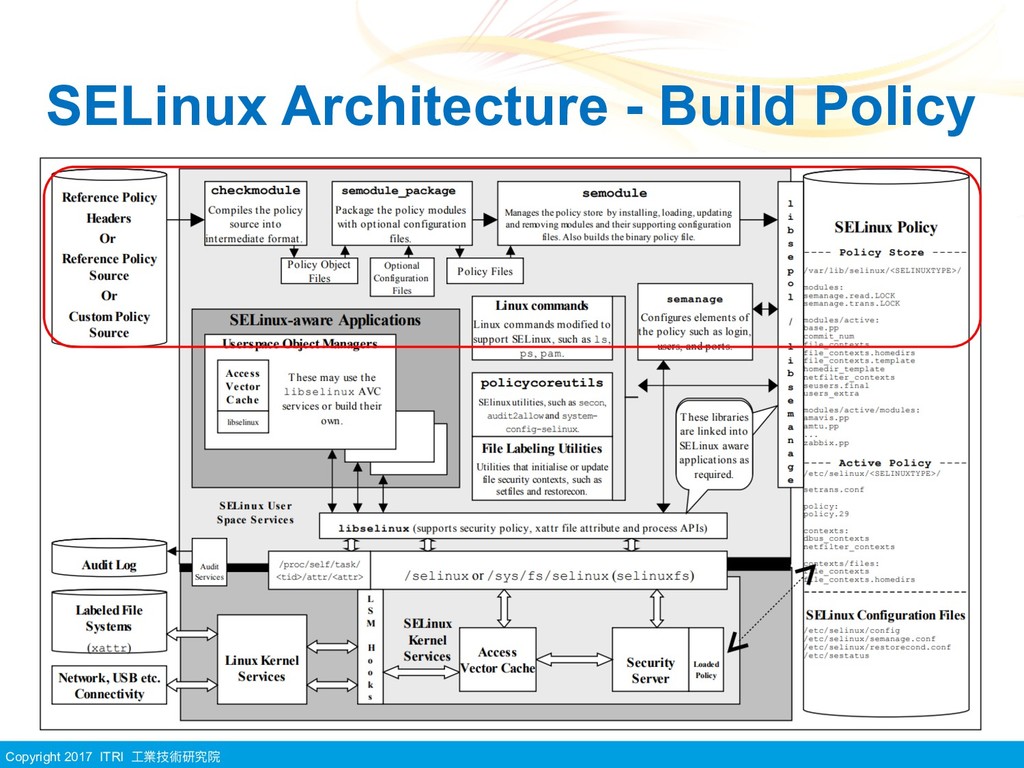
Copyright 2017 ITRI ⼯工業技術研究院 How to Write Policy by Yourself
Monolithic Base Policy Module • All build by 3 file : ◦ .te : like .c file ◦ .if : like .h file ◦ .fc (describe file context) -
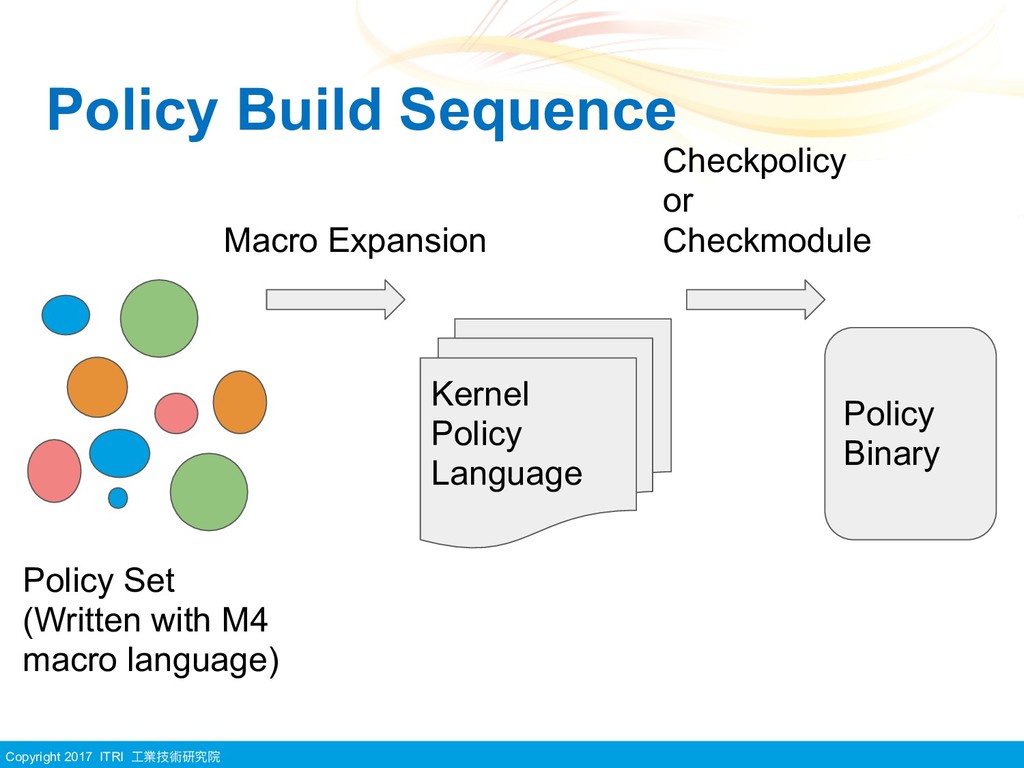
Copyright 2017 ITRI ⼯工業技術研究院 Policy Build Sequence Kernel Policy Language
Policy Set (Written with M4 macro language) Policy Binary Macro Expansion Checkpolicy or Checkmodule -
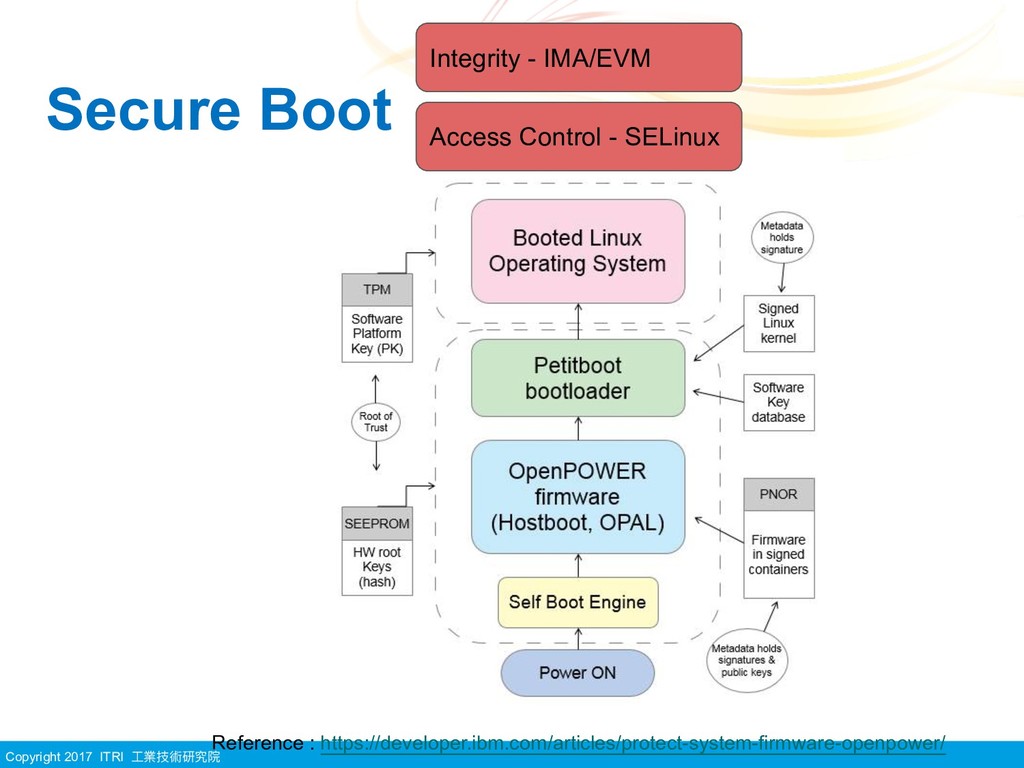
Copyright 2017 ITRI ⼯工業技術研究院 Secure Boot Reference : https://developer.ibm.com/articles/protect-system-firmware-openpower/ Access
Control - SELinux Integrity - IMA/EVM -
Copyright 2017 ITRI ⼯工業技術研究院 Q&A X SELinux Demo #58 SELinux
enforce mode SELinux permissive mode Busybox (Embedded System) Ubuntu 限定指定資料夾 僅能指定程序存取 保護特定程序 不被任何⼈人kill SELinux enforce mode on Raspberry Pi 3 Model B+