Share
Embed
TEAM JOCH vs. Android: The Ultimate Showdown
Presented with Jon Oberheide at ShmooCon 2011
Zach Lanier
January 29, 2011
Transcript
76 slides
-
Slide # 1 TEAM JOCH vs. Android - ShmooCon 2011
TEAM JOCH vs. Android: The Ultimate Showdown -
Slide # 2 TEAM JOCH vs. Android - ShmooCon 2011
TEAM JOCH Jon Oberheide + Zach Lanier = TEAM JOCH -
Slide # 3 TEAM JOCH vs. Android - ShmooCon 2011
Agenda • Android Security Overview • Kernel Security • Platform Security • Application Security -
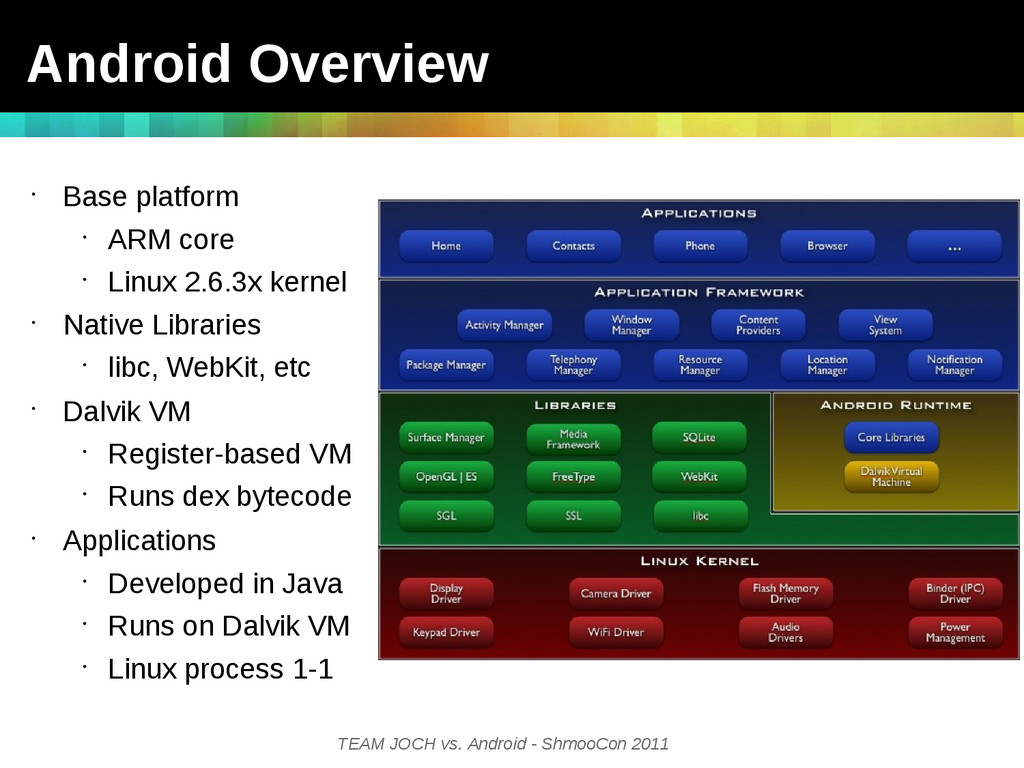
TEAM JOCH vs. Android - ShmooCon 2011 Android Overview •
Base platform • ARM core • Linux 2.6.3x kernel • Native Libraries • libc, WebKit, etc • Dalvik VM • Register-based VM • Runs dex bytecode • Applications • Developed in Java • Runs on Dalvik VM • Linux process 1-1 -
TEAM JOCH vs. Android - ShmooCon 2011 Hardware Features •
ARM11 TrustZone? • Unused! • ARM11 Jazelle JVM? • Unused! • ARMv6 eXecute-Never (XN)? • Unused! -
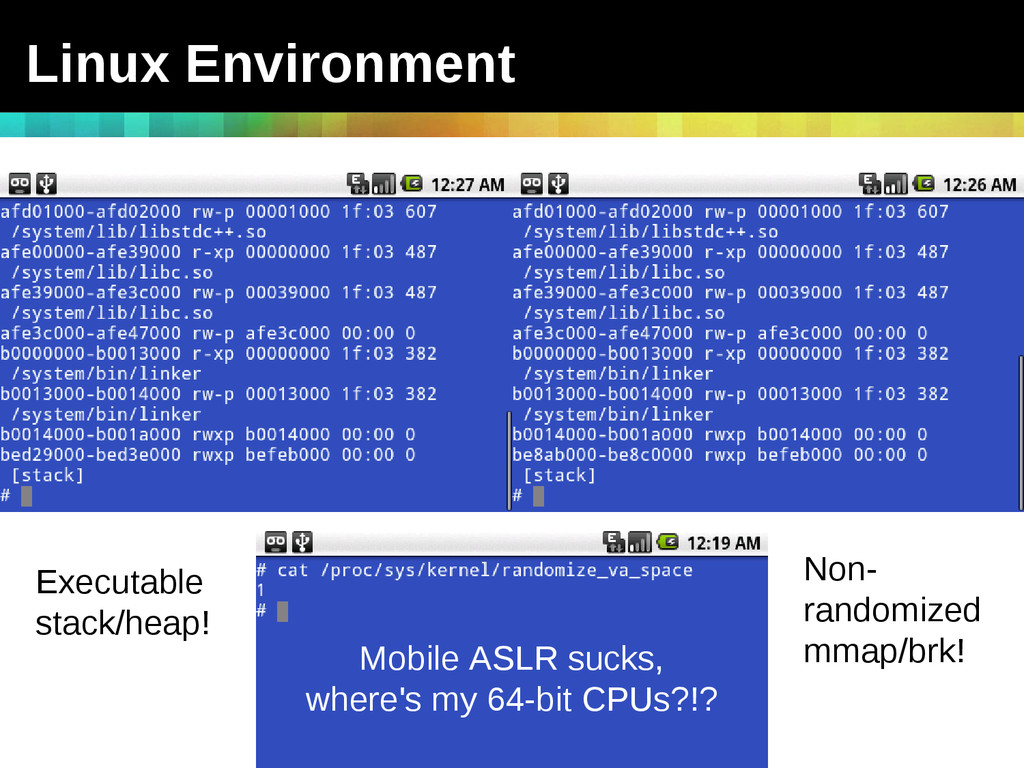
TEAM JOCH vs. Android - ShmooCon 2011 Linux Environment Executable
stack/heap! Non- randomized mmap/brk! Mobile ASLR sucks, where's my 64-bit CPUs?!? -
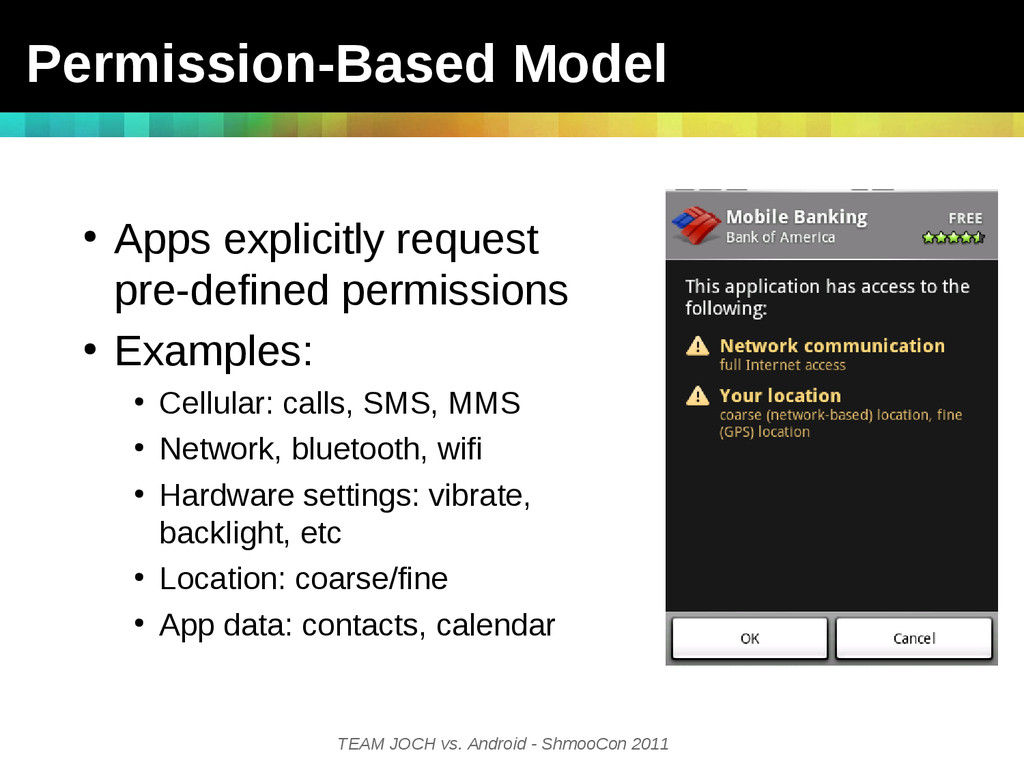
TEAM JOCH vs. Android - ShmooCon 2011 Permission-Based Model •
Apps explicitly request pre-defined permissions • Examples: • Cellular: calls, SMS, MMS • Network, bluetooth, wifi • Hardware settings: vibrate, backlight, etc • Location: coarse/fine • App data: contacts, calendar -
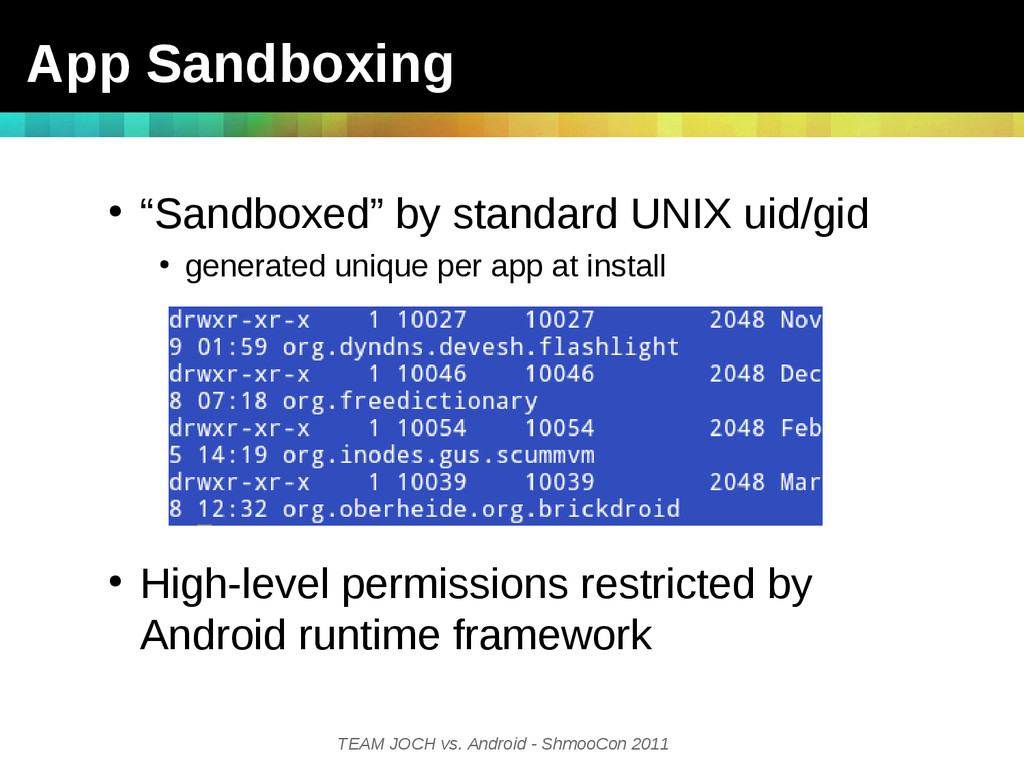
TEAM JOCH vs. Android - ShmooCon 2011 App Sandboxing •
“Sandboxed” by standard UNIX uid/gid • generated unique per app at install • High-level permissions restricted by Android runtime framework -
TEAM JOCH vs. Android - ShmooCon 2011 App Distribution •
Application signing • No CAs • Self-signed by developers • Android Market • $25 signup, anyone can publish • Anonymous sign-up possible -
Slide # 10 TEAM JOCH vs. Android - ShmooCon 2011
Agenda • Android Security Overview • Kernel Security • Platform Security • Application Security -
Slide # 11 TEAM JOCH vs. Android - ShmooCon 2011
The Linux Kernel • Linux kernel = swiss cheese – Jailbreaks, aka local privesc, are plentiful – Mostly thanks to stealth/743C • Shameless plug! – If you care about kernel exploitation, come to: -
Slide # 12 TEAM JOCH vs. Android - ShmooCon 2011
Android Native Code • Dalvik VM != sandbox – Not limited to executing dex bytecode – Can pop out of the VM to execute native code – Any 3rd party app can root your phone by exploiting a kernel vulnerability via native code • Native code packaged within APKs – Android should do some code signing like iPhone – But it doesn't, so why limit execution of native code to build-time packaged modules? -
Slide # 13 TEAM JOCH vs. Android - ShmooCon 2011
RootStrap • Getting root is easy, but how do it most effectively as an attacker • Enter, RootStrap – Silent runtime fetching and execution of remote ARM payloads – Not really a bot..more of a general purpose distributed computing platform ;-) -
Slide # 14 TEAM JOCH vs. Android - ShmooCon 2011
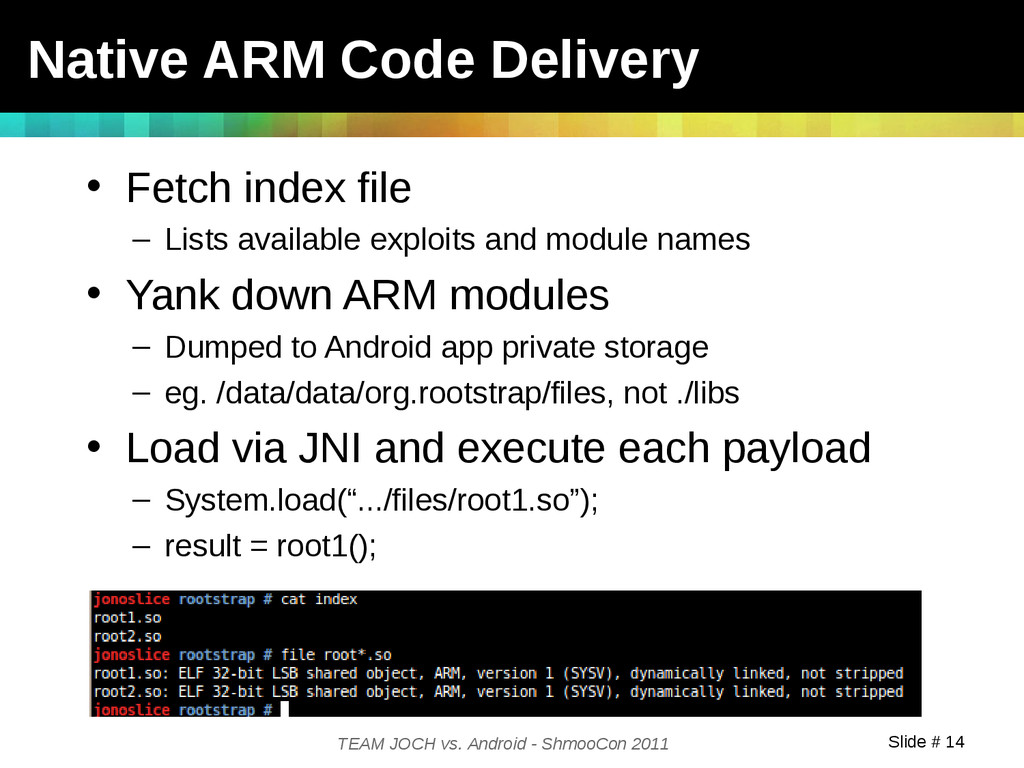
Native ARM Code Delivery • Fetch index file – Lists available exploits and module names • Yank down ARM modules – Dumped to Android app private storage – eg. /data/data/org.rootstrap/files, not ./libs • Load via JNI and execute each payload – System.load(“.../files/root1.so”); – result = root1(); -
Slide # 15 TEAM JOCH vs. Android - ShmooCon 2011
How to Build a Mobile Botnet • Build some fun legit-looking games / apps – Include RootStrap functionality – Periodically phone home to check for new payloads • As soon as new kernel vuln discovered, push out exploit payload – Before providers push out OTA patch – Trivial to win that race, slow OTA updates • Rootkit a bunch of phones! -
Slide # 16 TEAM JOCH vs. Android - ShmooCon 2011
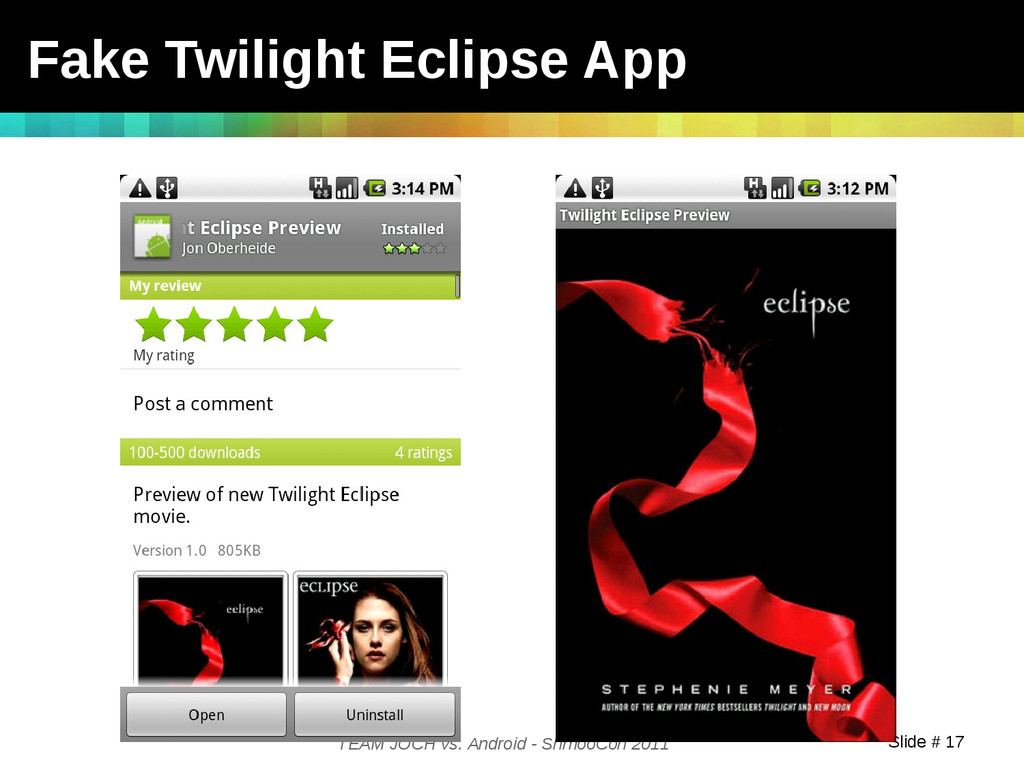
A Wolf in Vampire's Clothing? • RootStrap app is boring and not sneaky – No one would intentionally download it – Need something legit looking to get a large install base • Hmm...what to do, what to do... -
Slide # 17 TEAM JOCH vs. Android - ShmooCon 2011
Fake Twilight Eclipse App -
Slide # 18 TEAM JOCH vs. Android - ShmooCon 2011
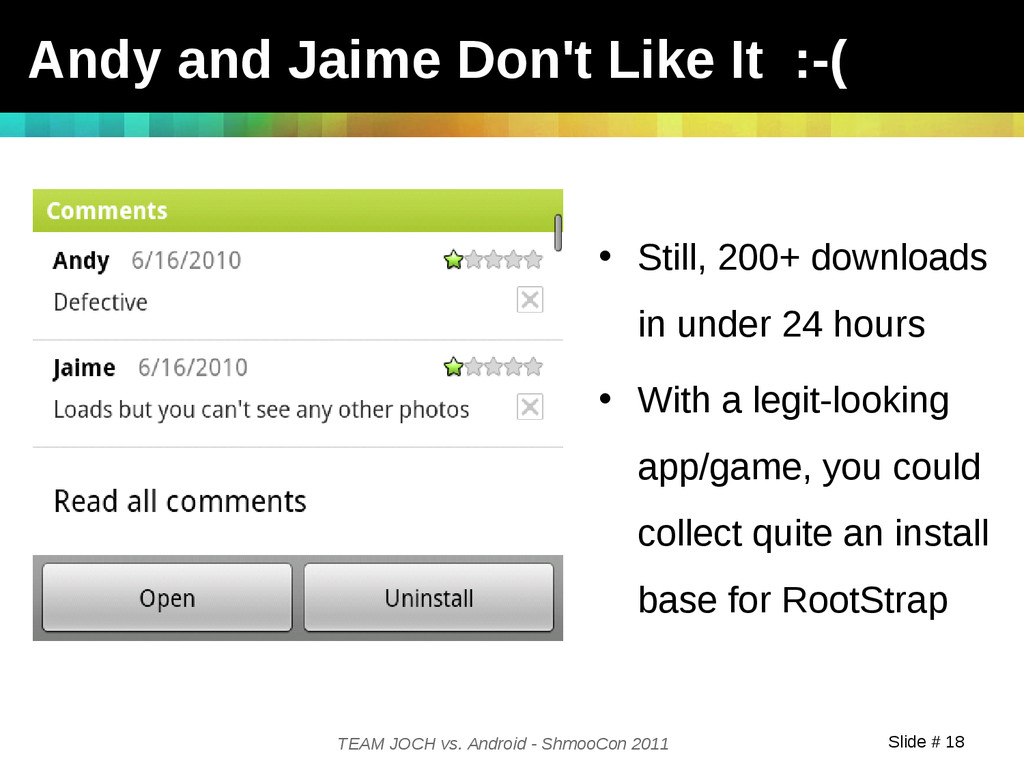
Andy and Jaime Don't Like It :-( • Still, 200+ downloads in under 24 hours • With a legit-looking app/game, you could collect quite an install base for RootStrap -
Slide # 19 TEAM JOCH vs. Android - ShmooCon 2011
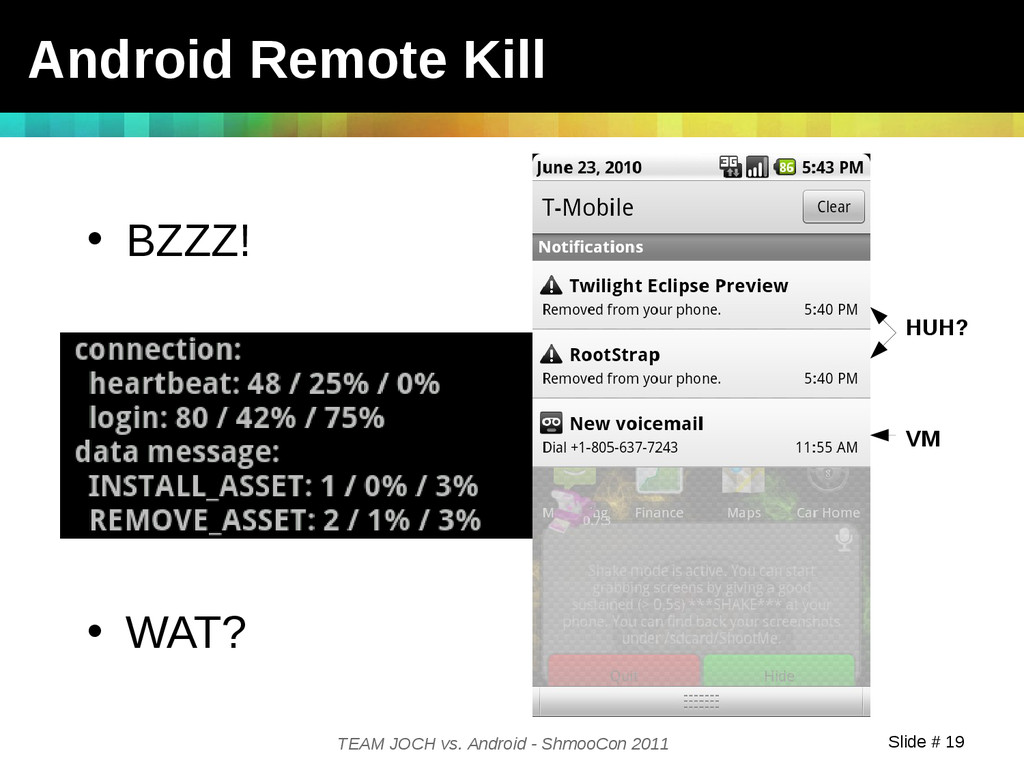
Android Remote Kill • BZZZ! • WAT? VM HUH? -
Slide # 20 TEAM JOCH vs. Android - ShmooCon 2011
Android Remote Kill/Install • Android has remote kill/wipe functionality built-in – Google can remotely remove installed apps from any Android device – GTalkService persistent connection – REMOVE_ASSET remote intent invocation • Also, remote installation functionality -
Slide # 21 TEAM JOCH vs. Android - ShmooCon 2011
Kernel Security Wrap-up • No excuses Google, it's 2011! – Harden your kernel / toolchain – Signed code restrictions a la iPhone • Supporting native code makes it worse – Packaging/install time: ok – Runtime native code delivery: not ok -
Slide # 22 TEAM JOCH vs. Android - ShmooCon 2011
Agenda • Android Security Overview • Kernel Security • Platform Security • Application Security -
Slide # 23 TEAM JOCH vs. Android - ShmooCon 2011
Platform Security • There's a lot of “platform goo” in the middle between the kernel and applications • What to attack? – Not kernel, not apps! – How about permissions framework? • Permissions approval process – Intended to warn the user about potentially unsafe actions an app can perform -
Slide # 24 TEAM JOCH vs. Android - ShmooCon 2011
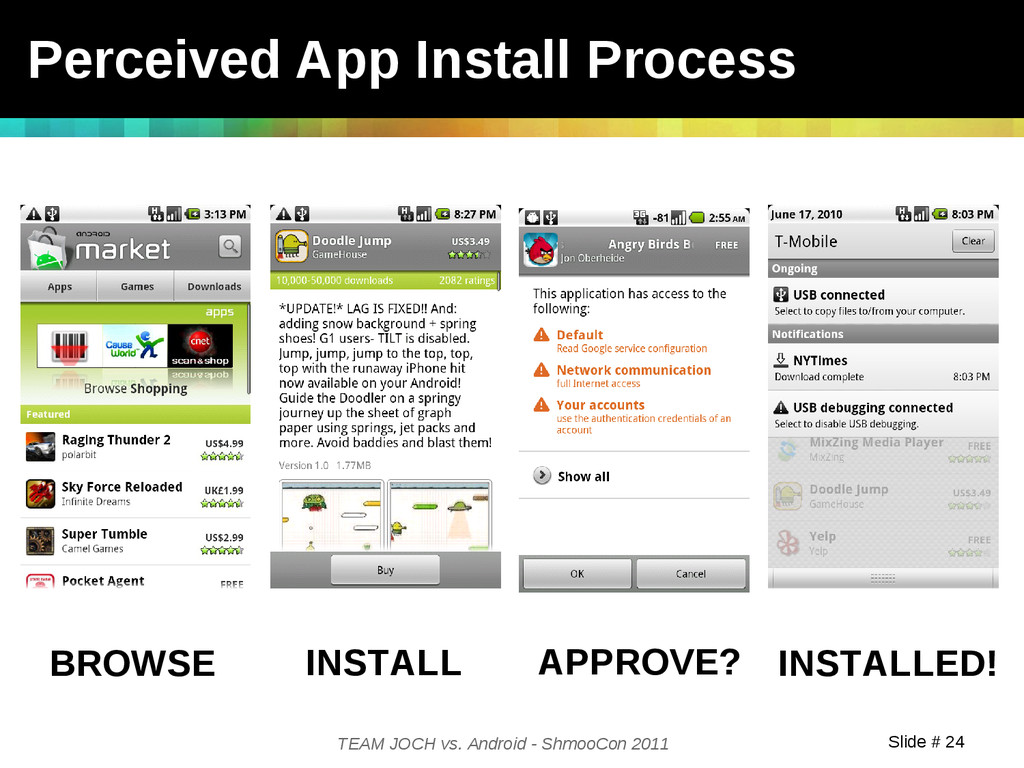
Perceived App Install Process BROWSE INSTALL APPROVE? INSTALLED! -
Slide # 25 TEAM JOCH vs. Android - ShmooCon 2011
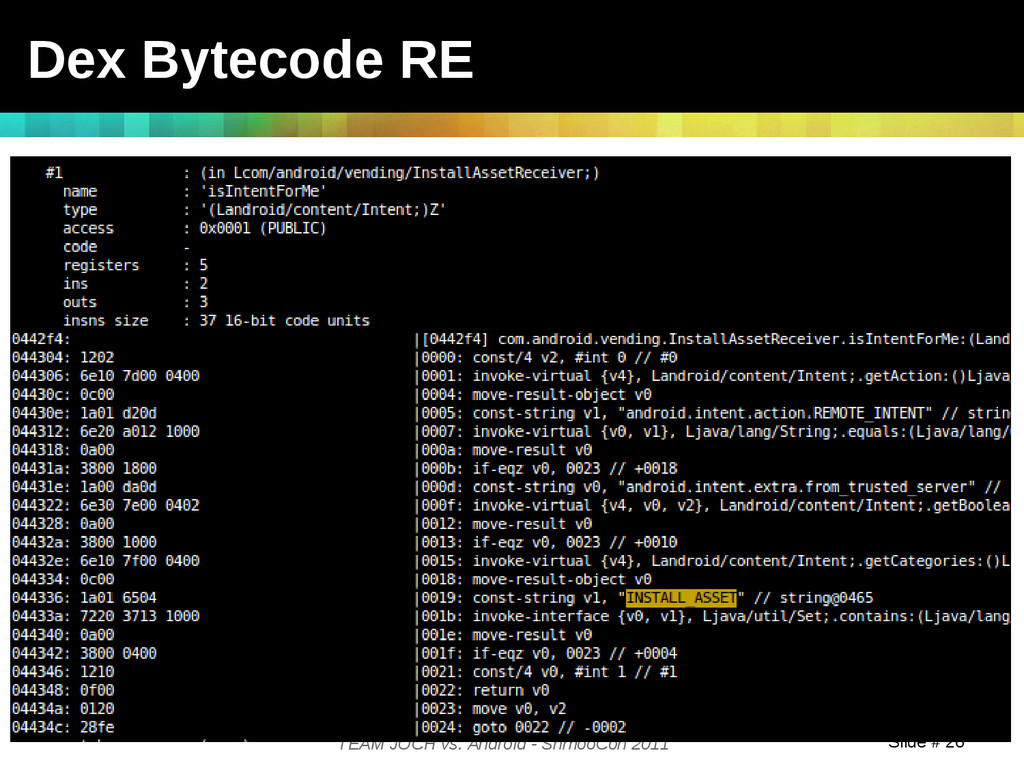
ACTUAL Market Flow • Google is a sneaky panda! – You don't actually download / install the app through the market application • When you click install in market app – Google servers push an out-of-band message down to you via persistent data connection – Triggers INSTALL_ASSET intent to start install – Intent handler fetches APK and installs -
Slide # 26 TEAM JOCH vs. Android - ShmooCon 2011
Dex Bytecode RE -
Slide # 27 TEAM JOCH vs. Android - ShmooCon 2011
GTalkService Connection • Persistent data connection – Speaks XMPP – Same connection now used for C2DM push service • It's SSL, but... • If you MITM or C2DM spoof – Remote intent / app install • If you pop GTalkService servers – Push down code to all Android phones in the world -
Slide # 28 TEAM JOCH vs. Android - ShmooCon 2011
Gap in Responsibility • Market app performs permission approval • But GTalkService triggers actual install • There's a disconnect here... -
Slide # 29 TEAM JOCH vs. Android - ShmooCon 2011
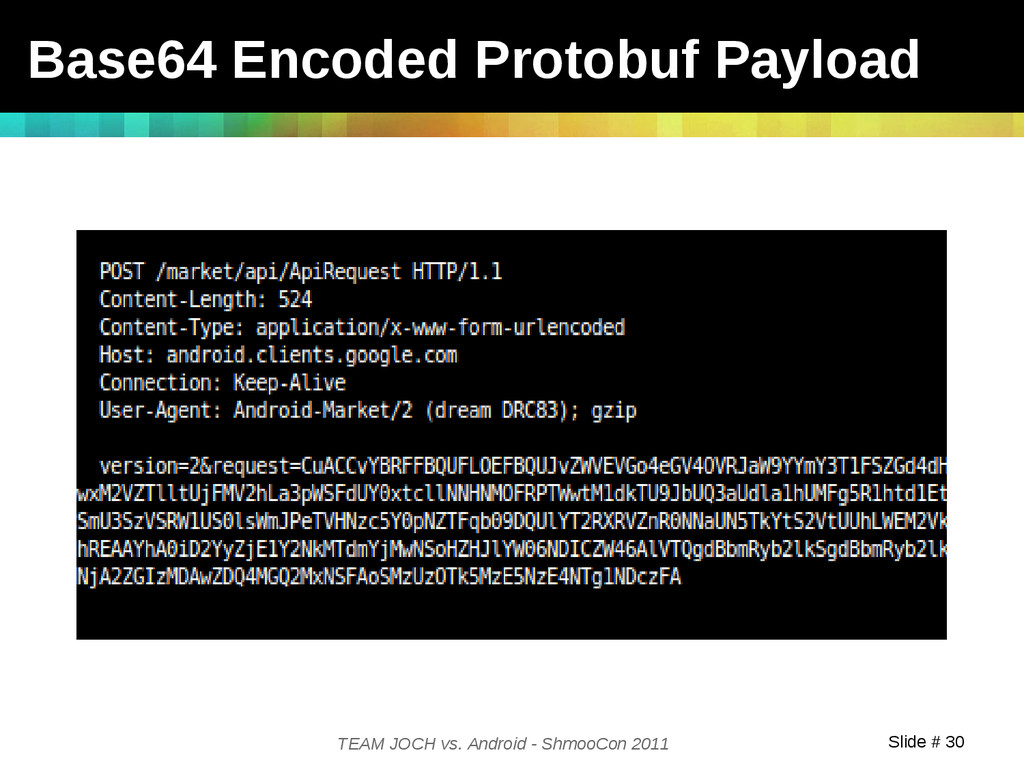
Market App Requests • What does the market app POST to the market server? • Can we spoof the same request and trigger an INSTALL_ASSET message and subsequent install? -
Slide # 30 TEAM JOCH vs. Android - ShmooCon 2011
Base64 Encoded Protobuf Payload -
Slide # 31 TEAM JOCH vs. Android - ShmooCon 2011
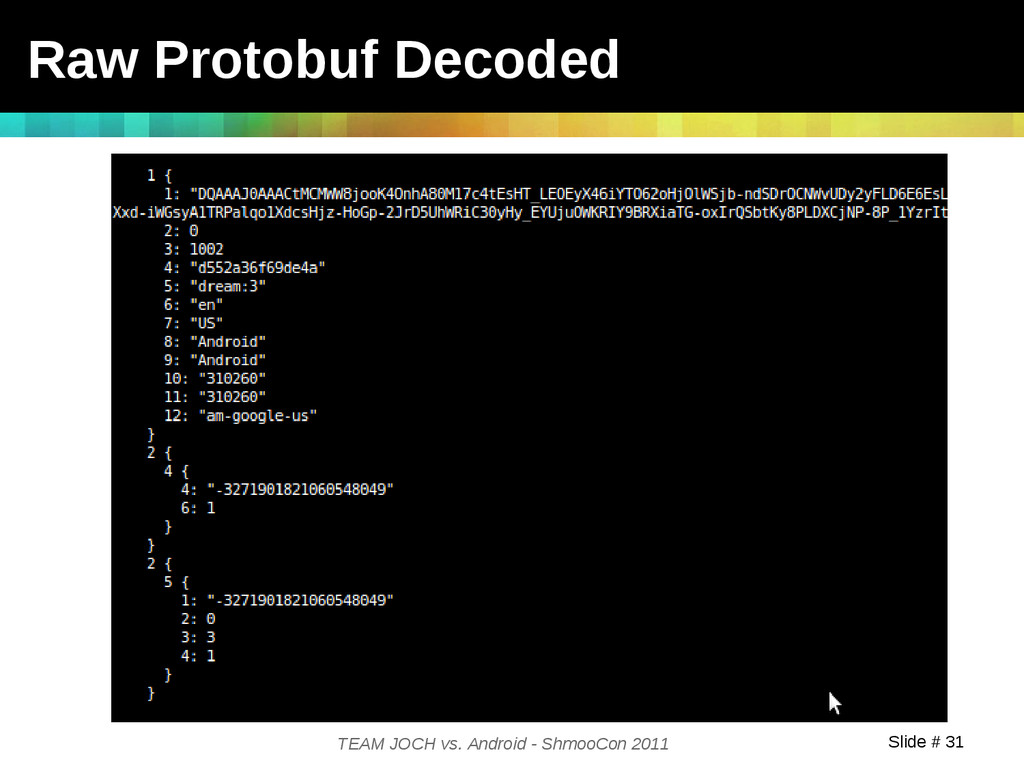
Raw Protobuf Decoded -
Slide # 32 TEAM JOCH vs. Android - ShmooCon 2011
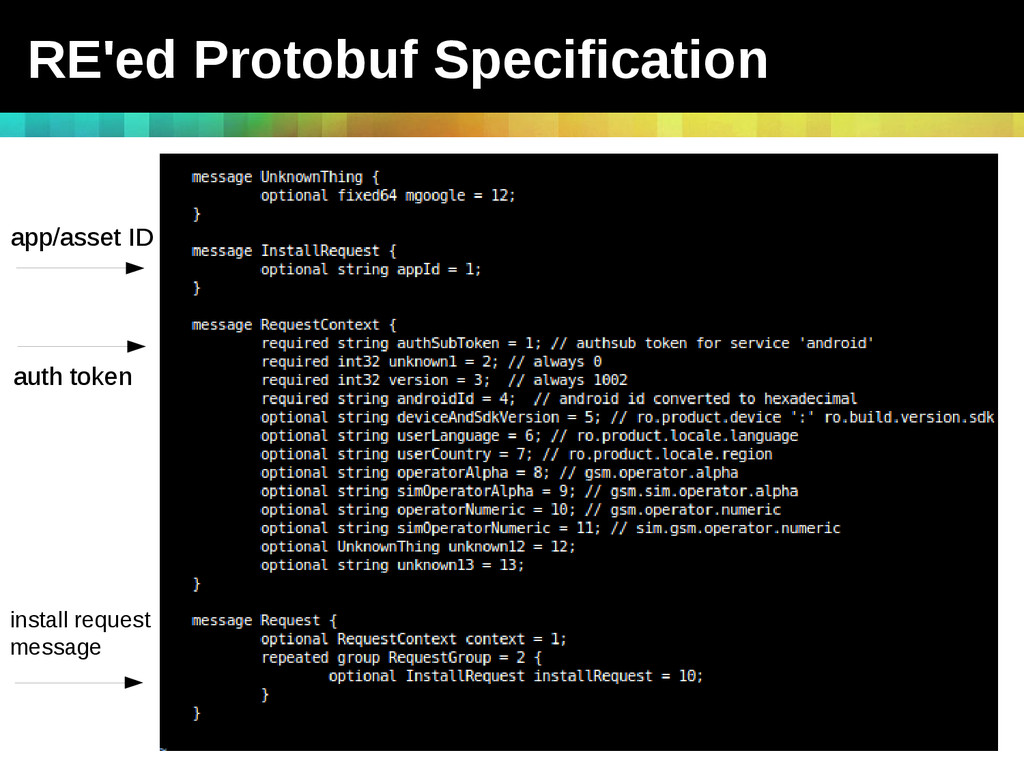
RE'ed Protobuf Specification app/asset ID auth token install request message -
Slide # 33 TEAM JOCH vs. Android - ShmooCon 2011
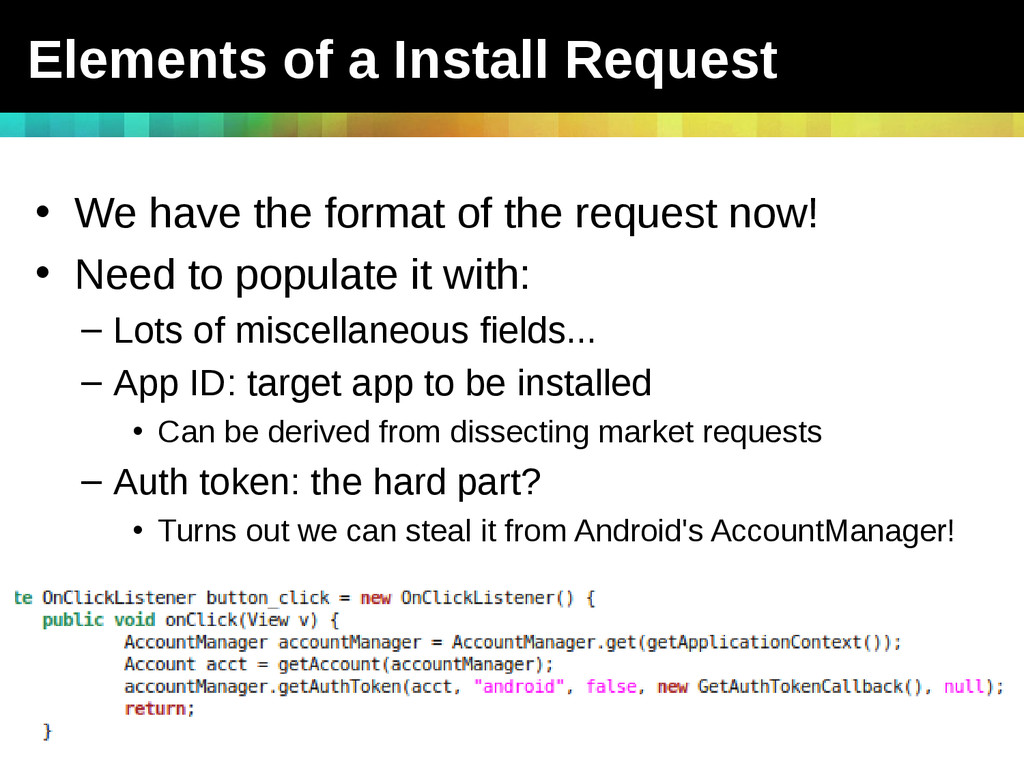
Elements of a Install Request • We have the format of the request now! • Need to populate it with: – Lots of miscellaneous fields... – App ID: target app to be installed • Can be derived from dissecting market requests – Auth token: the hard part? • Turns out we can steal it from Android's AccountManager! -
Slide # 34 TEAM JOCH vs. Android - ShmooCon 2011
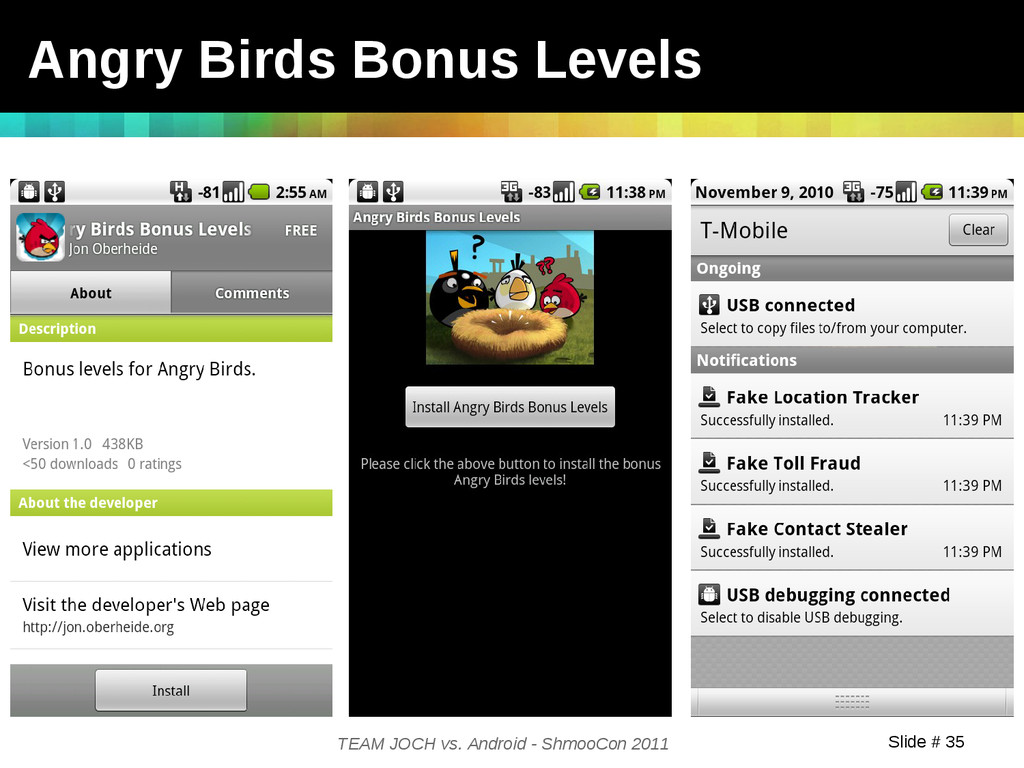
Bypassing Permissions Approval • Steal the “android” service token used by market from the AccountManager • Construct protobuf request to market servers for invoking an application installer • INSTALL_ASSET is pushed and app installed without any user prompt / permission approval • PoC disguised as an Angry Birds expansion app -
Slide # 35 TEAM JOCH vs. Android - ShmooCon 2011
Angry Birds Bonus Levels -
Slide # 36 TEAM JOCH vs. Android - ShmooCon 2011
Fake Toll Fraud App -
Slide # 37 TEAM JOCH vs. Android - ShmooCon 2011
Platform Security Wrapup • Vulnerability status: – Donut: fixed – Froyo: fixed – Eclair: no confirmation yet, may be vulnerable • Platform complexity leads to vulns – Round-about market / GtalkService procedure – “server-initiated” flag fix worth investigation -
Slide # 38 TEAM JOCH vs. Android - ShmooCon 2011
Agenda • Android Security Overview • Kernel Security • Platform Security • Application Security -
TEAM JOCH vs. Android - ShmooCon 2011 • The Web
pushed content to the browser – Centralization of apps & data – Always a push for MORE (ActiveX, applets, Flash) • Now, everyone gets their own app! – Code (not HTML) gets pushed to the endpoint – XKCD Viewer Broad Observations -
TEAM JOCH vs. Android - ShmooCon 2011 • AuthC/AuthZ –
Carrier Applications • “we trust you because you’re on our network” – Third-party Applications • SOMETIMES better than carrier apps – Incomplete support of open standards • Client-side data trust issues – admin=1 Broad Observations -
TEAM JOCH vs. Android - ShmooCon 2011 • HyperGlobalMegaCloudDataMeshStore –
Many Apps for syncing data between device and CLOUD • Full AuthC and AuthZ bugs Broad Observations -
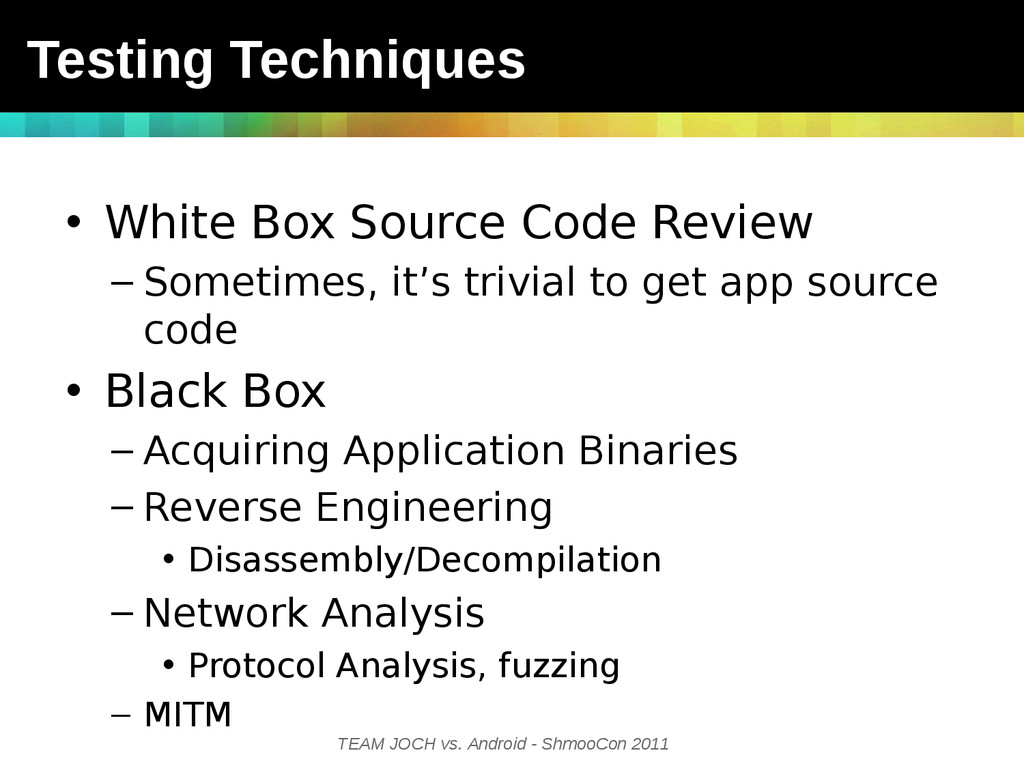
TEAM JOCH vs. Android - ShmooCon 2011 • White Box
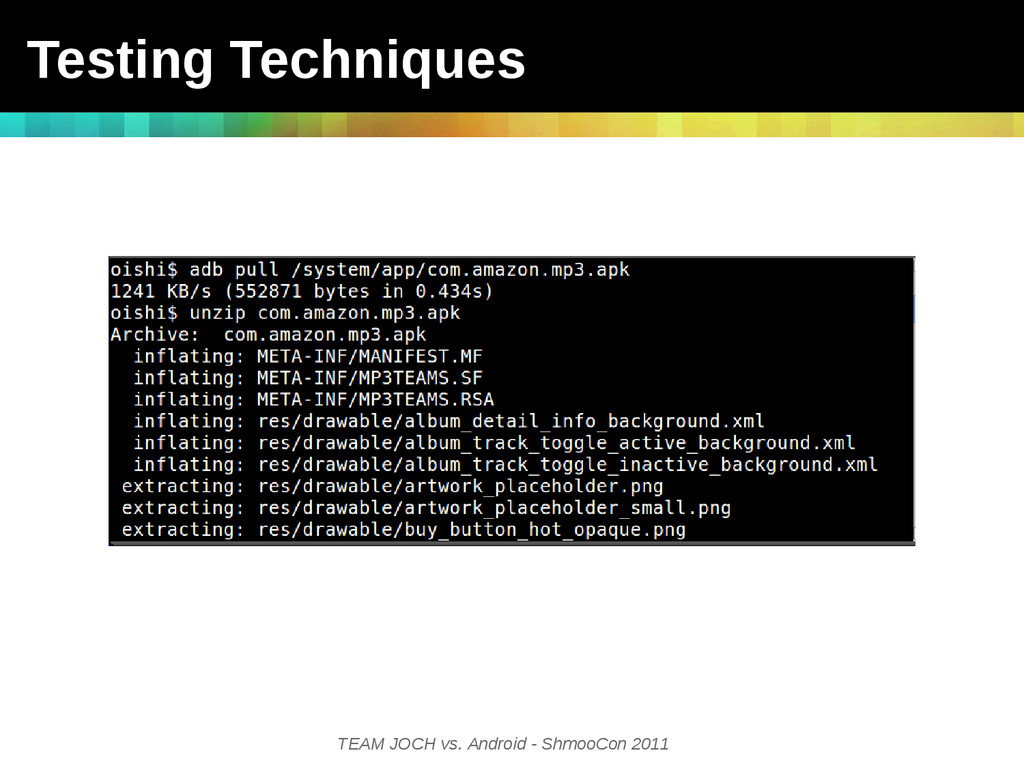
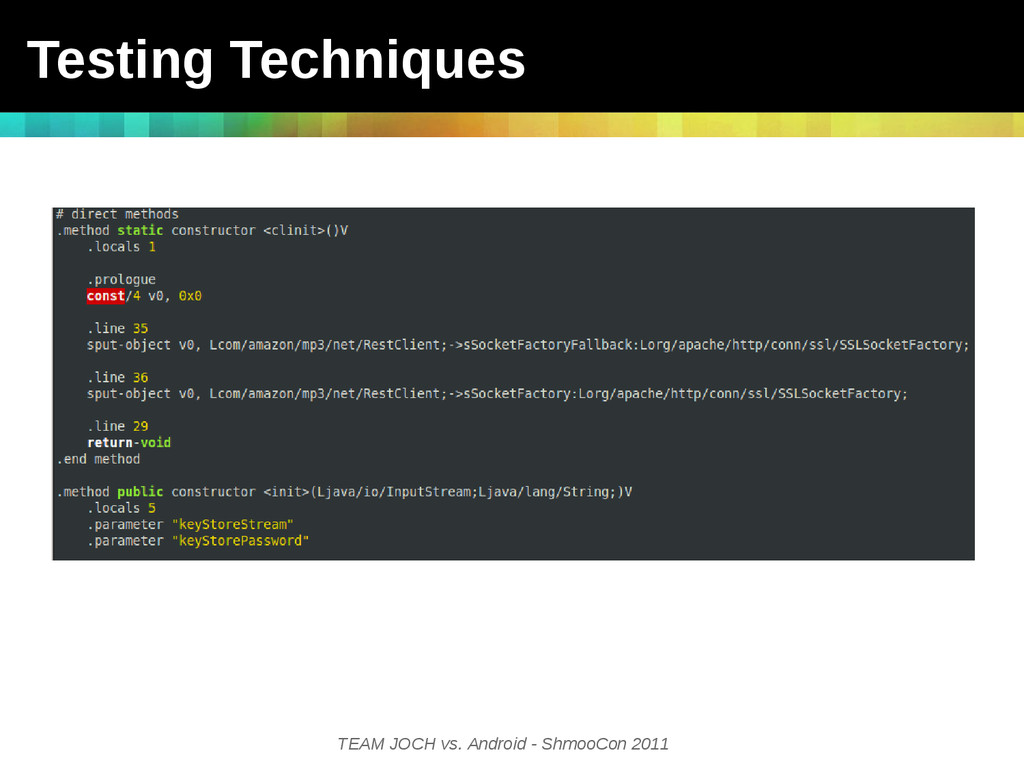
Source Code Review – Sometimes, it’s trivial to get app source code • Black Box – Acquiring Application Binaries – Reverse Engineering • Disassembly/Decompilation – Network Analysis • Protocol Analysis, fuzzing – MITM Testing Techniques -
TEAM JOCH vs. Android - ShmooCon 2011 • Not everyone
can be a Binary RE ninja – ...and project timelines don’t allow for on-the-job training :-) • Sometimes the easiest way to understand an application is to look at its TRAFFIC • You need to be come the MITM – Just like WAPT, and Burp, WebScarab, etc. 48 Testing Techniques -
TEAM JOCH vs. Android - ShmooCon 2011 • MAPT MITM
Challenges! – Run the app in an emulator (boring) – Connect the phone to your own WAP • Uplink your WAP to your laptop with Internet sharing enabled – Run Wireshark – WiFi not always an option • Handset might not support WiFi • Application might require carrier network – Change server.carrier.com to testsite.com 49 Testing Techniques -
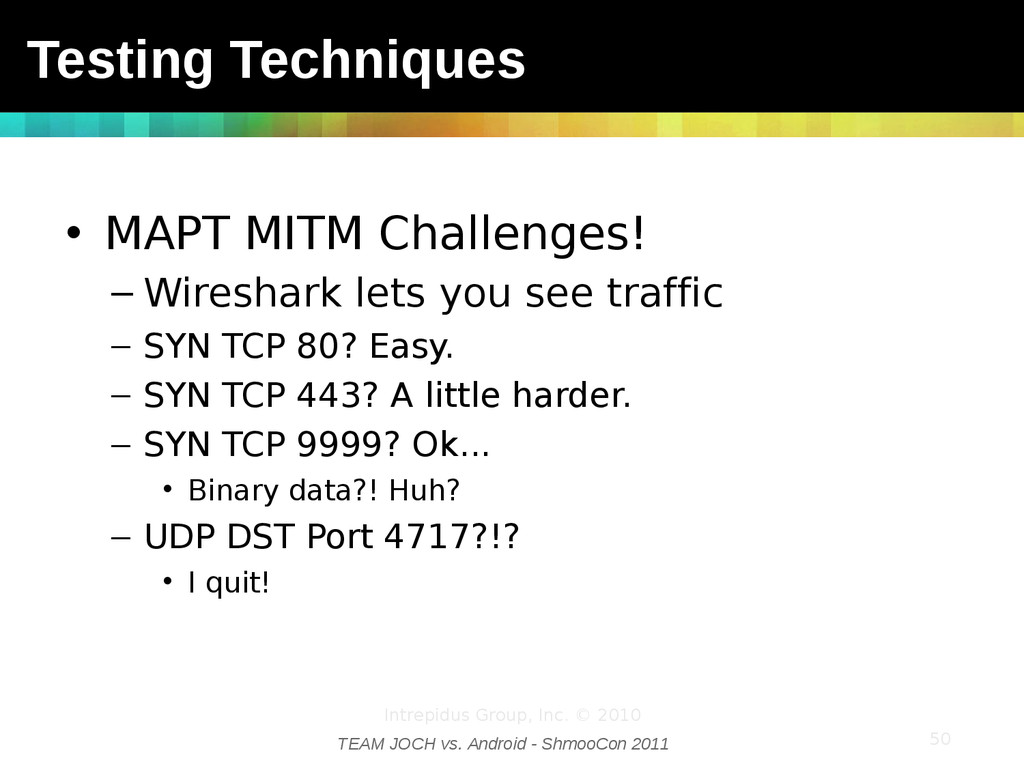
TEAM JOCH vs. Android - ShmooCon 2011 Intrepidus Group, Inc.
© 2010 50 • MAPT MITM Challenges! – Wireshark lets you see traffic – SYN TCP 80? Easy. – SYN TCP 443? A little harder. – SYN TCP 9999? Ok... • Binary data?! Huh? – UDP DST Port 4717?!? • I quit! Testing Techniques -
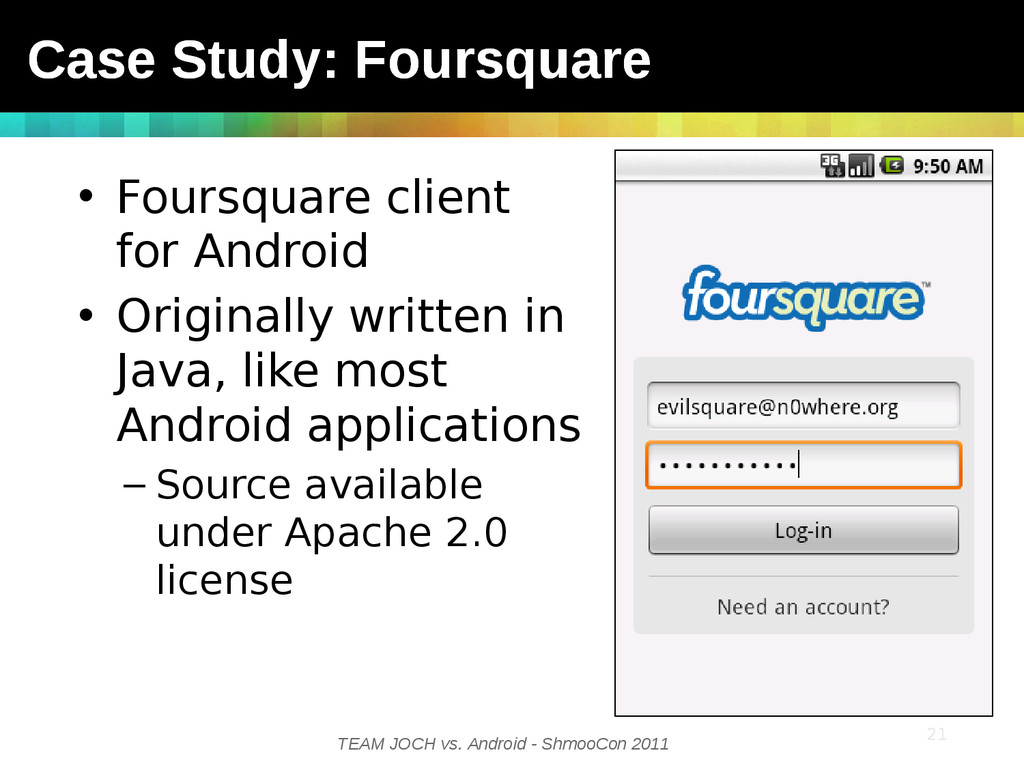
TEAM JOCH vs. Android - ShmooCon 2011 21 • Foursquare
client for Android • Originally written in Java, like most Android applications – Source available under Apache 2.0 license 21 Case Study: Foursquare Case Study: Foursquare -
TEAM JOCH vs. Android - ShmooCon 2011 21 21 •
Foursquare API supports Basic Auth and OAuth… – OAuth includes signatures for transactions, helps prevent replay attacks, etc. – Guess which one foursquared uses Case Study: Foursquare -
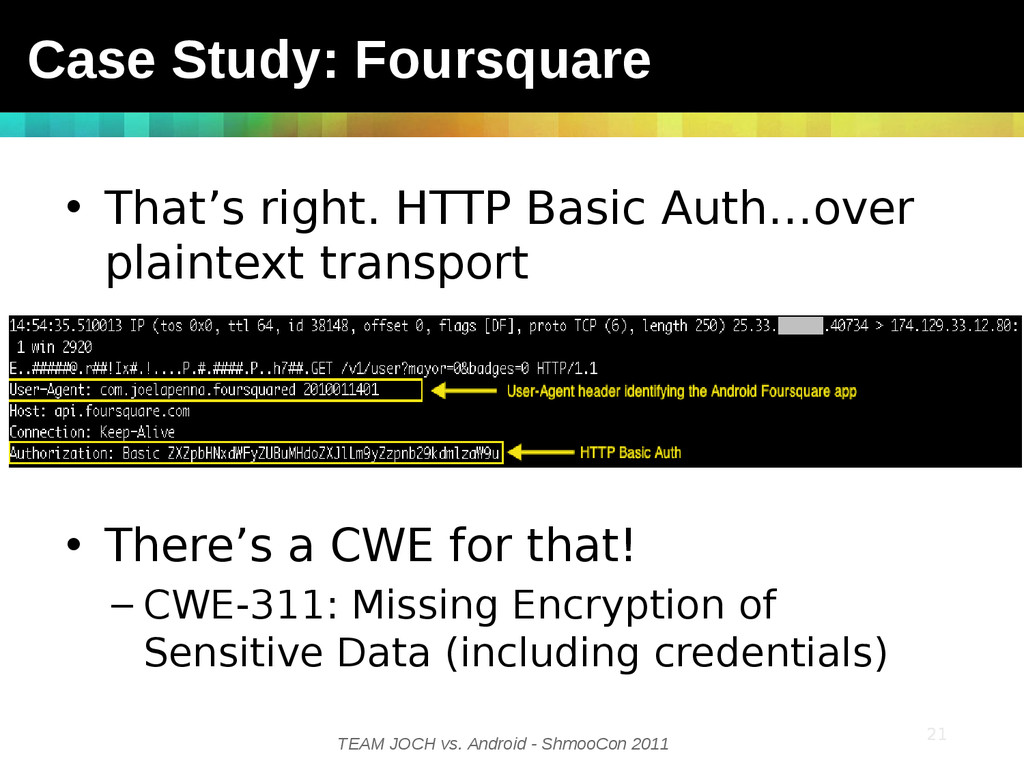
TEAM JOCH vs. Android - ShmooCon 2011 21 21 •
That’s right. HTTP Basic Auth…over plaintext transport • There’s a CWE for that! – CWE-311: Missing Encryption of Sensitive Data (including credentials) Case Study: Foursquare -
TEAM JOCH vs. Android - ShmooCon 2011 21 21 •
Why is this a problem? – EVERYONE uses Foursquare • Well, maybe not you, but everyone else! – Most applications “prefer” WiFi to cell radio => trivial interception of creds • Funny enough, Foursquared has OAuth support – But it’s not actually used Case Study: Foursquare -
TEAM JOCH vs. Android - ShmooCon 2011 25 • Multi-platform
application for storing and retrieving music, videos, documents, and more – Android, BREW, Blackberry, and fat web browser • Proprietary, binary-only 25 Case Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 •
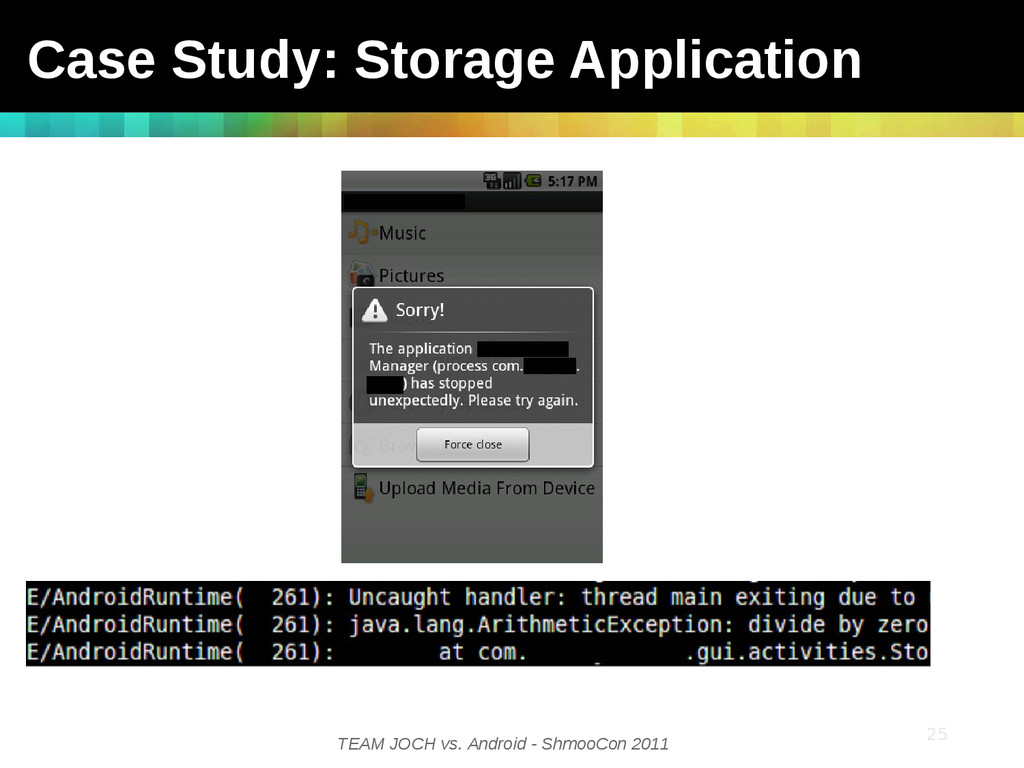
Simple crash in storage quota viewer – Divide-by-zero error leads to DoS – Attacker must successfully intercept and modify server response for this to happen • A bit more difficult since this tends to occur over the carrier’s network, but WiFi is still an option Case Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 Case
Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 •
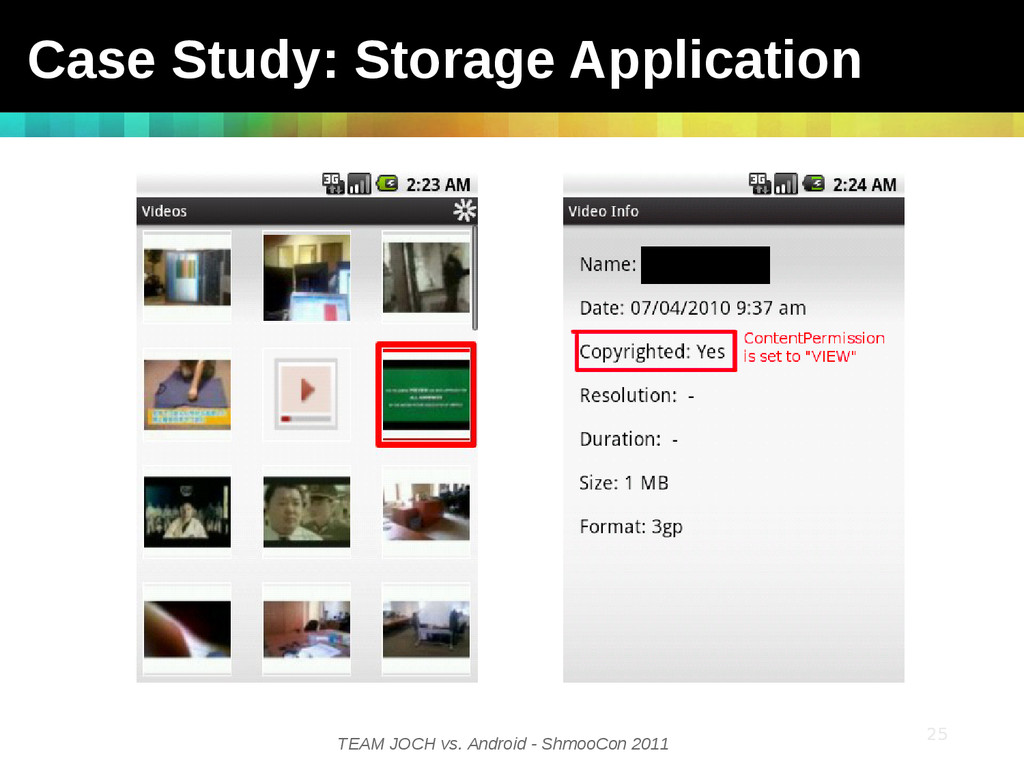
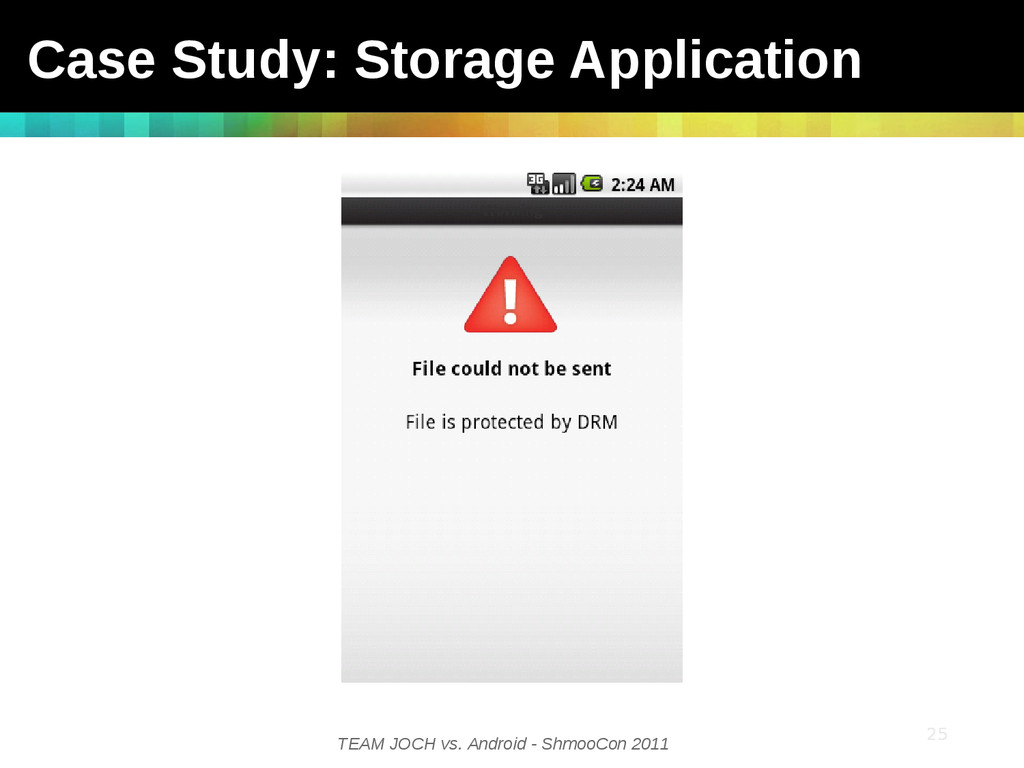
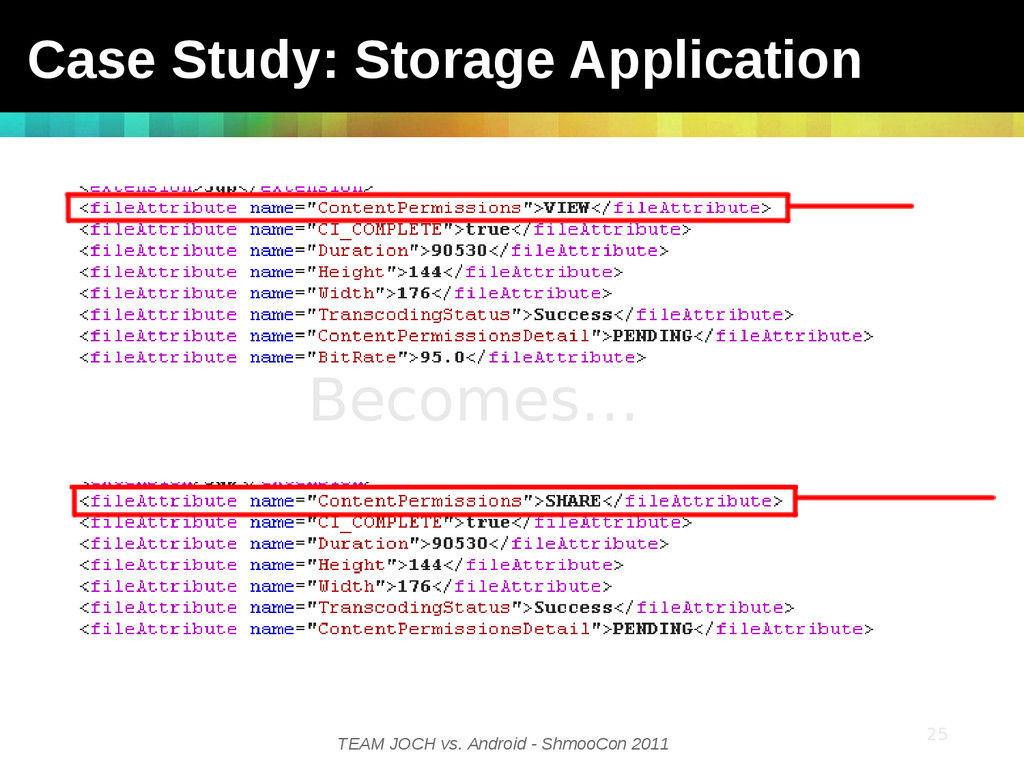
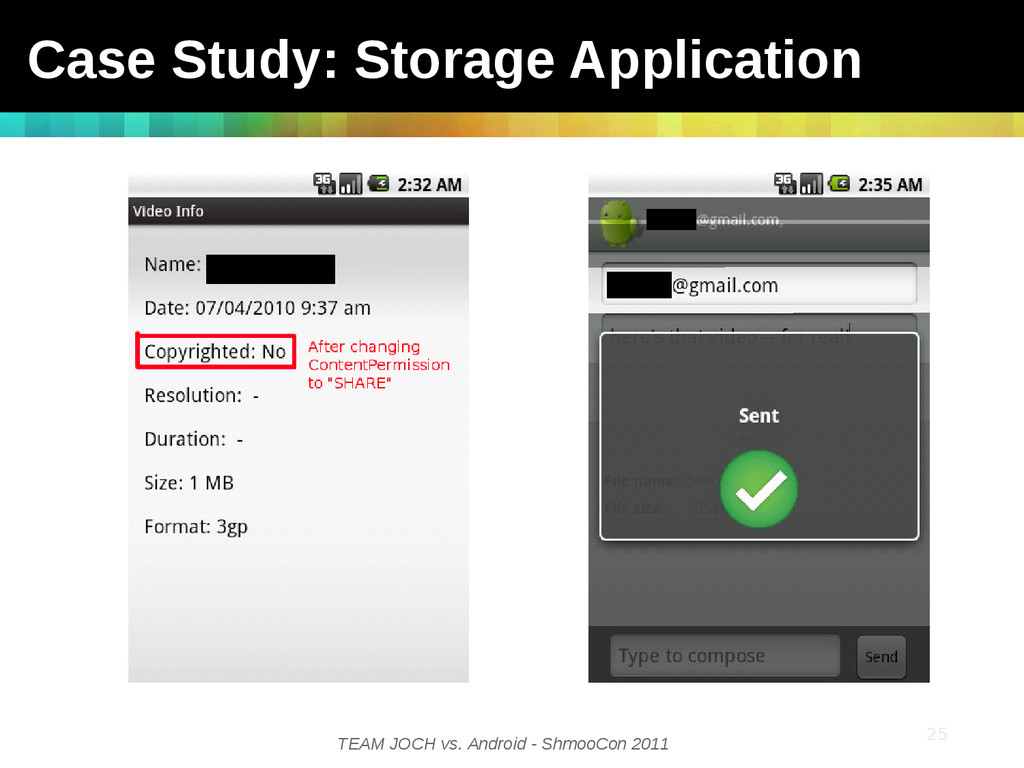
Diddling with “Digital Rights Management” – App supports sharing of video, audio, image content with your contacts – Enforces “DRM” on “protected” files • Often copyrighted or premium content – Enforcement occurs based on the value of an attribute in the file’s XML manifest • Yes, Virginia, that is under the user’s control Case Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 Case
Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 Case
Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 Case
Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 Becomes…
Case Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 Case
Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 •
The “DRM” is basically enforced within the client, predicated on the response from the server – And that response can be intercepted and modified => “DRM” bypass • CWE-807: Reliance on Untrusted Inputs in a Security Decision – I like CWE, btw Case Study: Storage Application -
TEAM JOCH vs. Android - ShmooCon 2011 • Cross-platform framework
for HTML/JS “applications” – WinMo, Android, etc. 66 Case Study: App Framework -
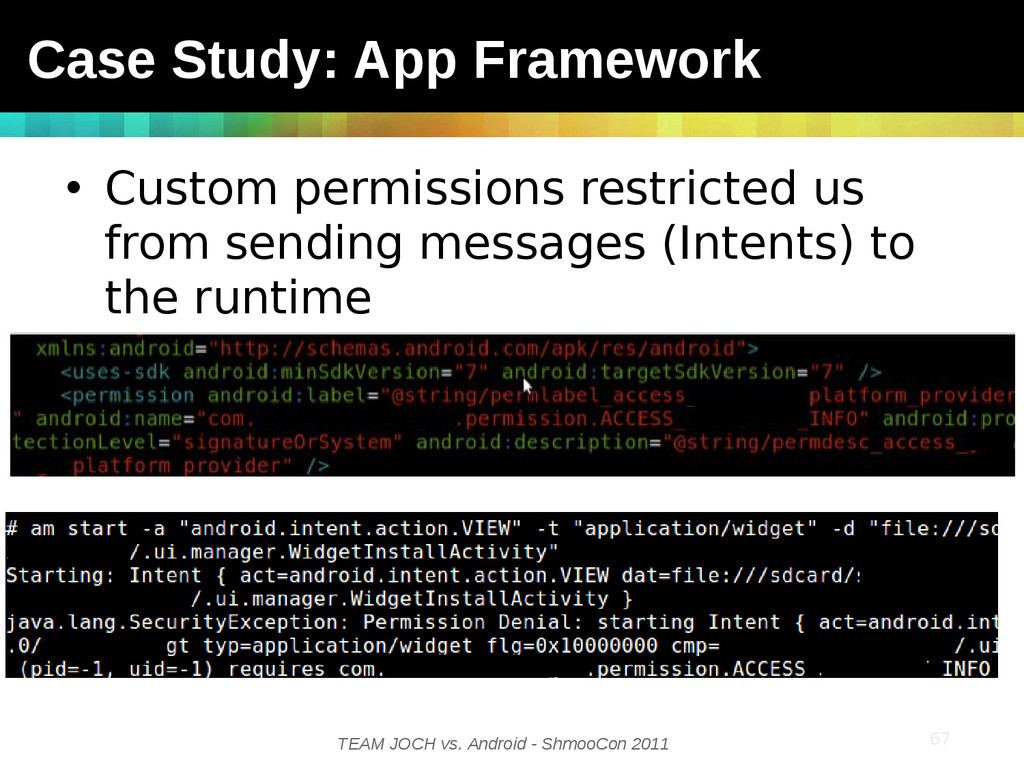
TEAM JOCH vs. Android - ShmooCon 2011 67 • Custom
permissions restricted us from sending messages (Intents) to the runtime Case Study: App Framework -
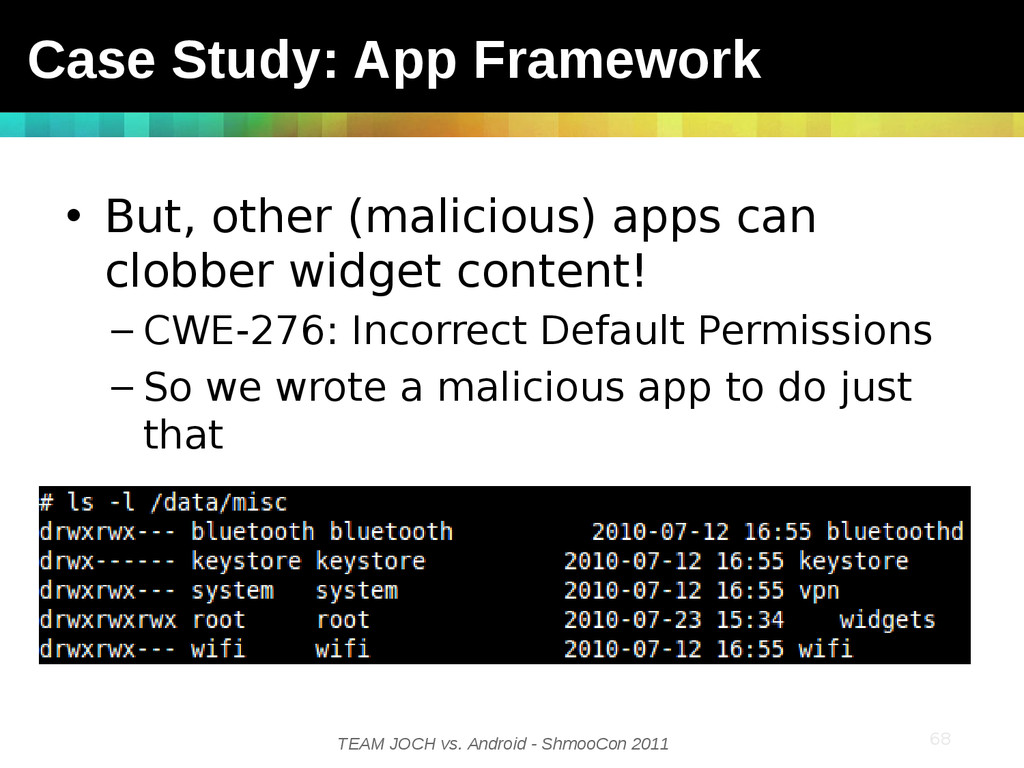
TEAM JOCH vs. Android - ShmooCon 2011 68 • But,
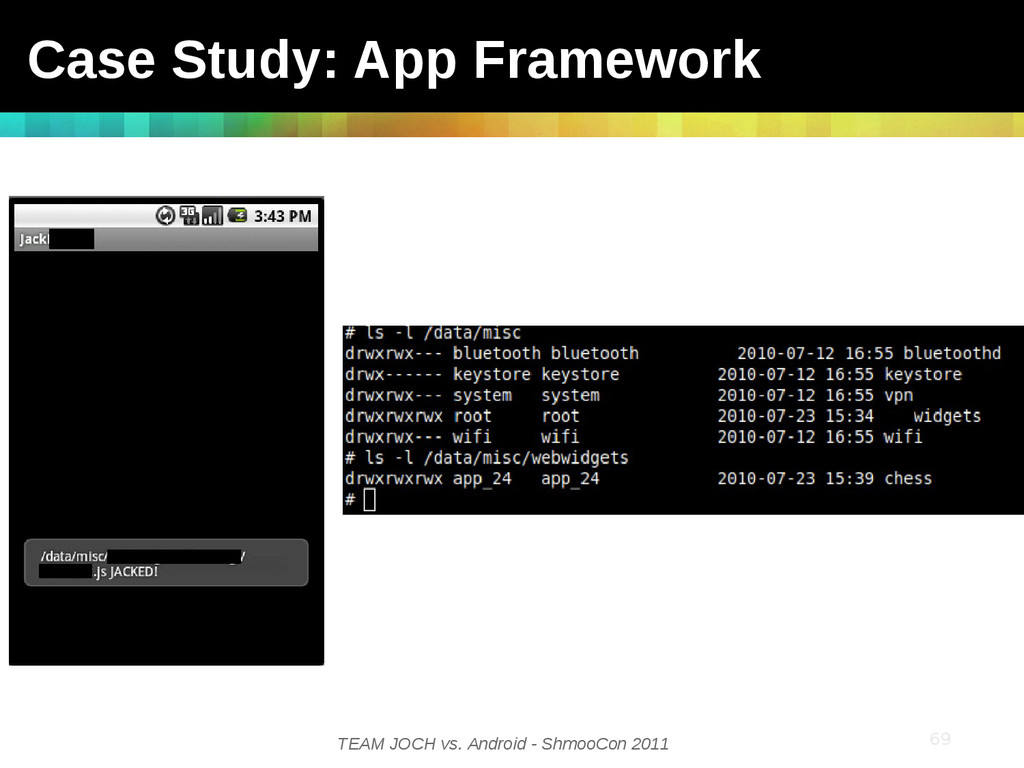
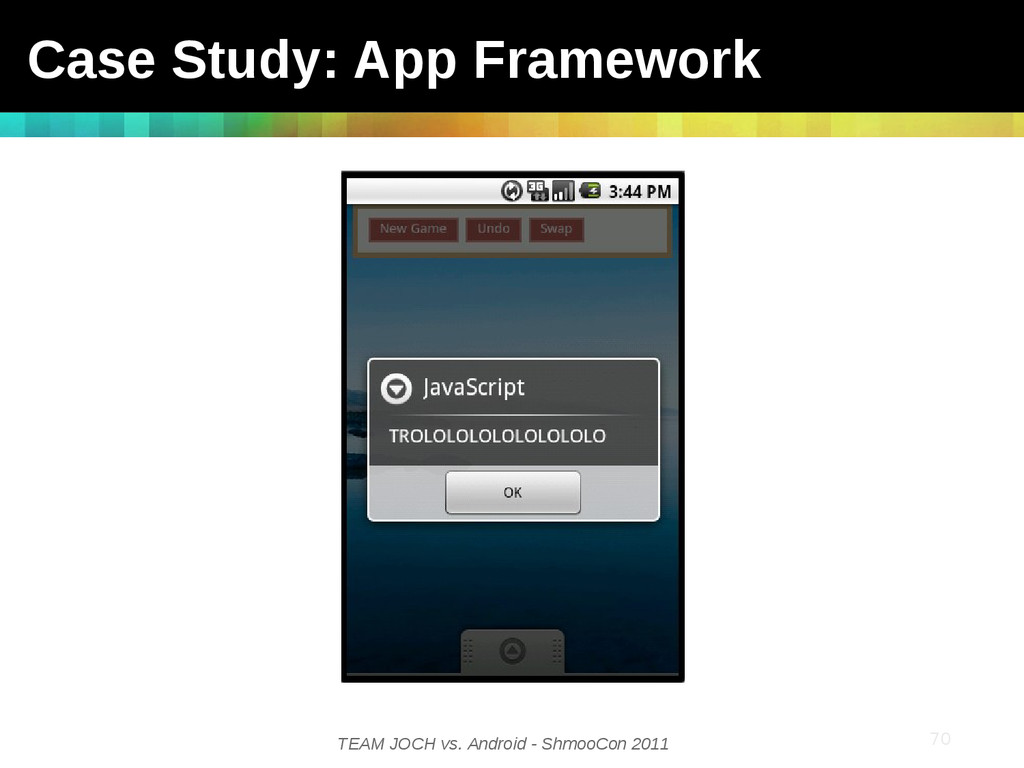
other (malicious) apps can clobber widget content! – CWE-276: Incorrect Default Permissions – So we wrote a malicious app to do just that Case Study: App Framework -
TEAM JOCH vs. Android - ShmooCon 2011 69 Case Study:
App Framework -
TEAM JOCH vs. Android - ShmooCon 2011 70 Case Study:
App Framework -
Slide # 71 TEAM JOCH vs. Android - ShmooCon 2011
Lookout Mobile • Lookout Mobile security app – Over 4 million users – Scanning, backup, lost device tracking, etc -
Slide # 72 TEAM JOCH vs. Android - ShmooCon 2011
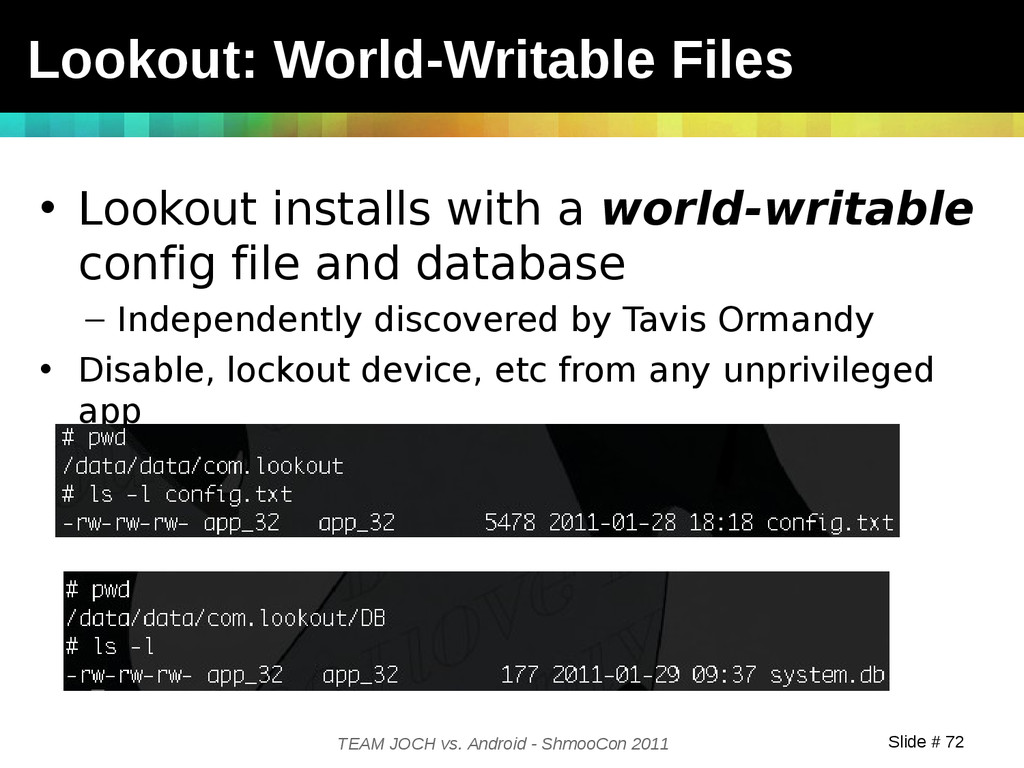
Lookout: World-Writable Files • Lookout installs with a world-writable config file and database – Independently discovered by Tavis Ormandy • Disable, lockout device, etc from any unprivileged app -
Slide # 73 TEAM JOCH vs. Android - ShmooCon 2011
• Tavis took it to the next level: – Backed up a custom shared lib, “liblookout.so” from a user-controlled directory – Restored into Lookout app's data/lib directory, overwriting legit “liblookout.so” – Security app → less secure phone Lookout: 0wned by Tavis -
TEAM JOCH vs. Android - ShmooCon 2011 25 25 •
Lack of guidance, standards, practices makes developers reinvent the wheel – Or just make them think they need to • Neglecting the security lessons learned with “traditional” and web applications – Client-side trust – Access control issues – …and all of the other “basic” problems and mistakes of yore Application Security Wrapup -
Slide # 75 TEAM JOCH vs. Android - ShmooCon 2011
Final Scorecard • TEAM JOCH vs. Android kernel? –TEAM JOCH! • TEAM JOCH vs. Android platform? –TEAM JOCH! • TEAM JOCH vs. Android apps? –TEAM JOCH! -
Slide # 76 TEAM JOCH vs. Android - ShmooCon 2011
Q&A Jon Oberheide Duo Security [email protected] QUESTIONS? Zach Lanier Intrepidus Group [email protected]