Share
Embed
Wicked malware persistence methods
Presented at:
- AppSec EU Allstars 2017: https://2017.appsec.eu/program/
- CONfidence 2017: http://2017.confidence.org.pl/agenda.html
Demos: https://github.com/hasherezade/persistence_demos

hasherezade
May 19, 2017
Transcript
57 slides
-
Agenda 1. Basics of persistence 2. Hunting for malware persistence
artifacts 3. Making persistence hard to spot (tricks + real life examples) -
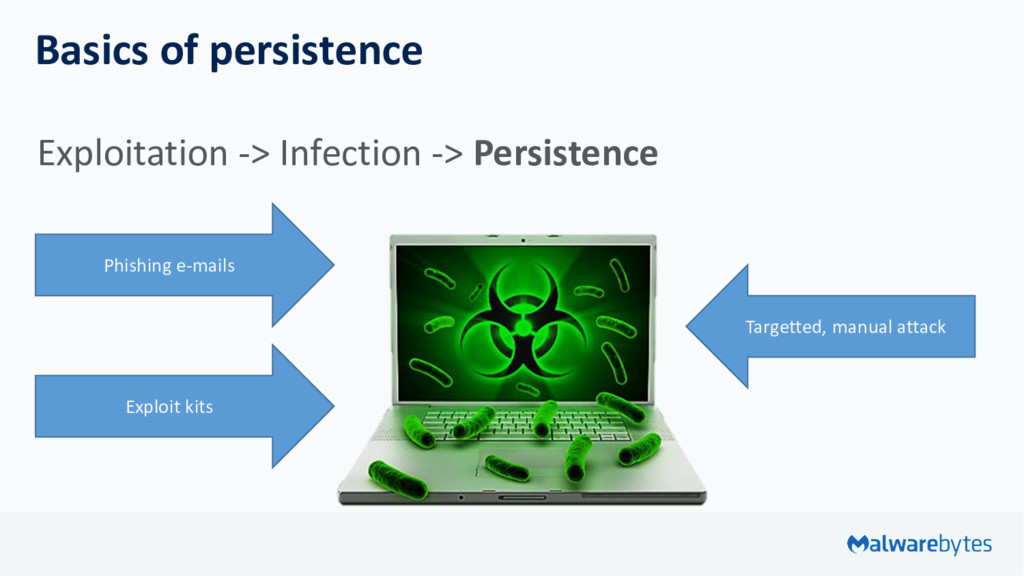
Basics of persistence Exploitation -> Infection -> Persistence Phishing e-mails
Exploit kits Targetted, manual attack -
Basics of persistence •WHO? Most of the malware needs it
(except some ransomware) •WHY? To start the application after each reboot •HOW? Windows offers various legitimate persistence ways – let’s recall them... -
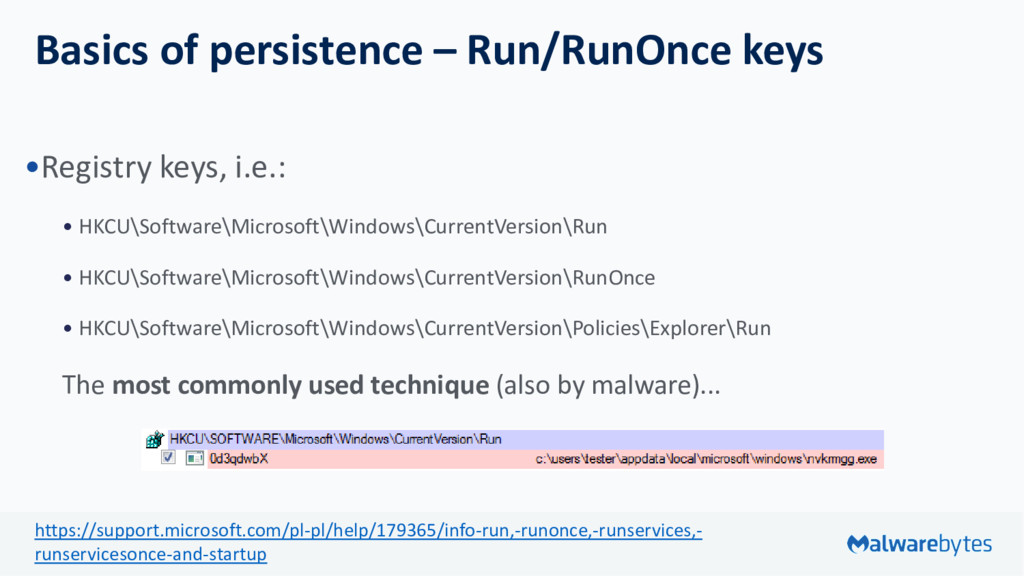
Basics of persistence – Run/RunOnce keys •Registry keys, i.e.: •
HKCU\Software\Microsoft\Windows\CurrentVersion\Run • HKCU\Software\Microsoft\Windows\CurrentVersion\RunOnce • HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\Run The most commonly used technique (also by malware)... https://support.microsoft.com/pl-pl/help/179365/info-run,-runonce,-runservices,- runservicesonce-and-startup -
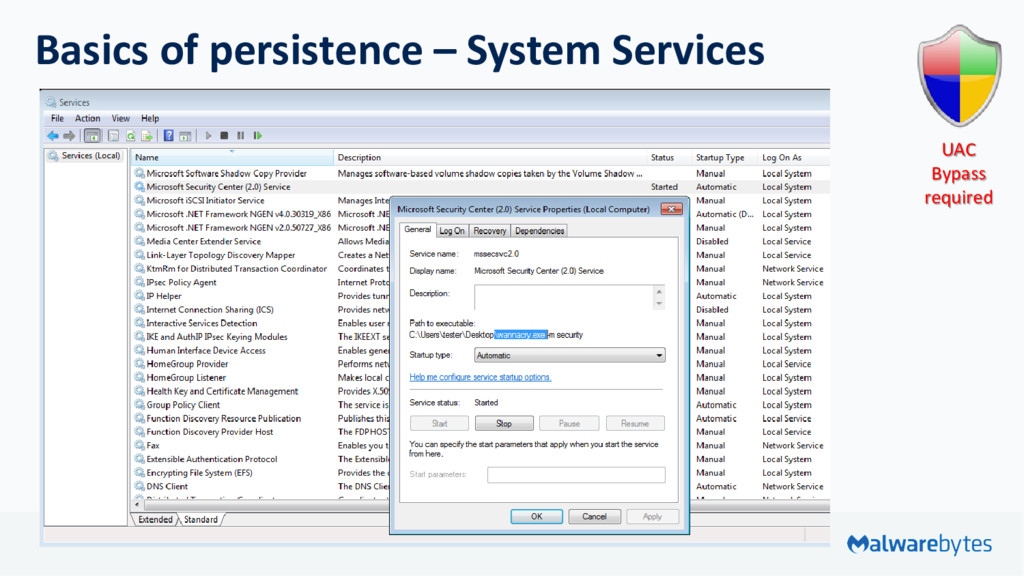
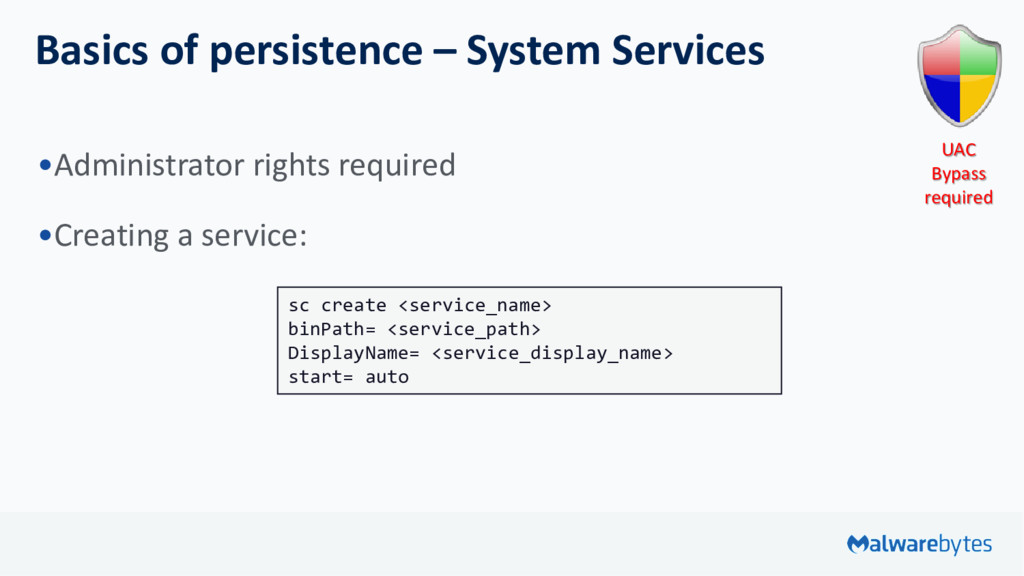
Basics of persistence – System Services •Administrator rights required •Creating
a service: sc create <service_name> binPath= <service_path> DisplayName= <service_display_name> start= auto UAC Bypass required -
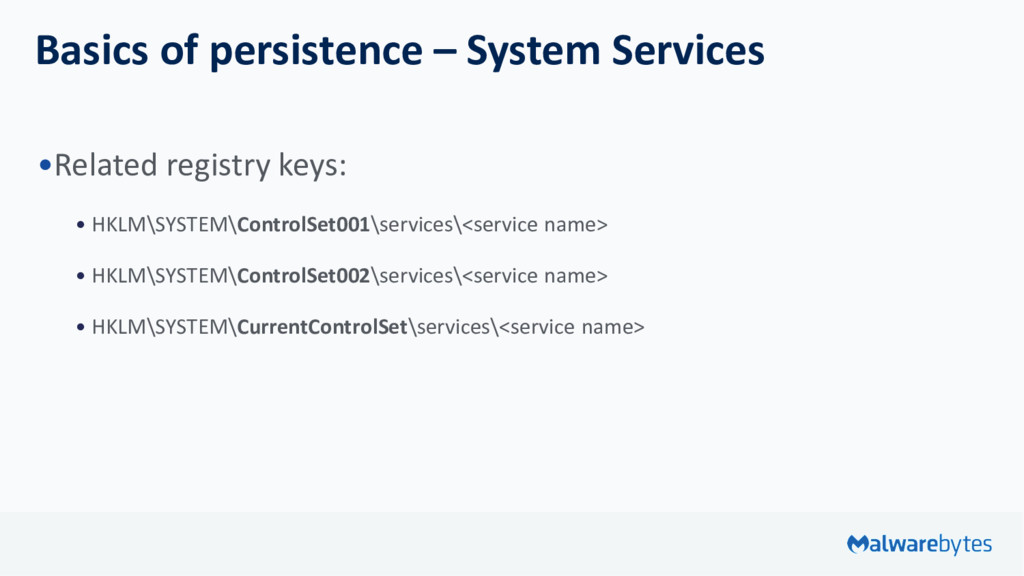
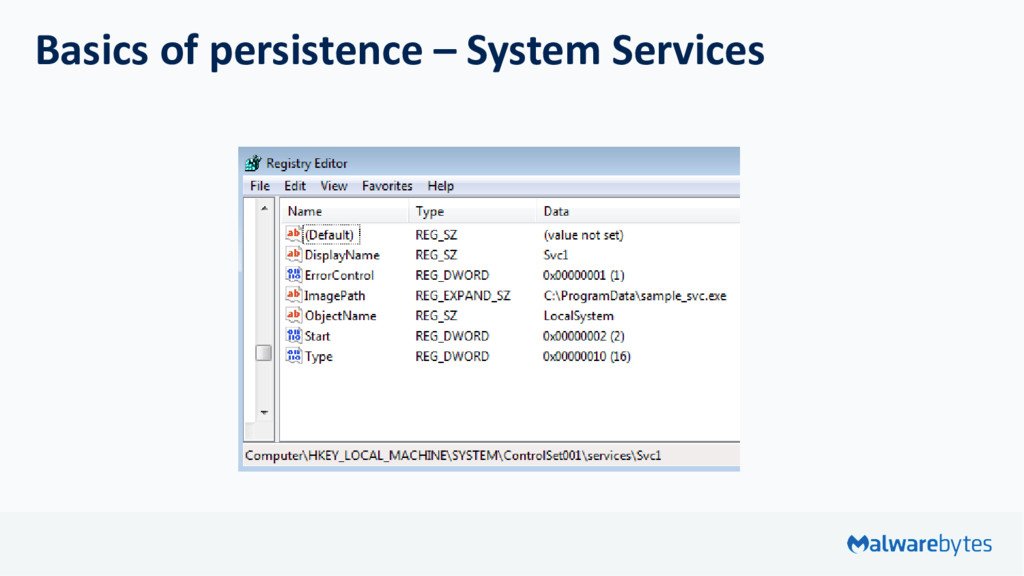
Basics of persistence – System Services •Related registry keys: •
HKLM\SYSTEM\ControlSet001\services\<service name> • HKLM\SYSTEM\ControlSet002\services\<service name> • HKLM\SYSTEM\CurrentControlSet\services\<service name> -
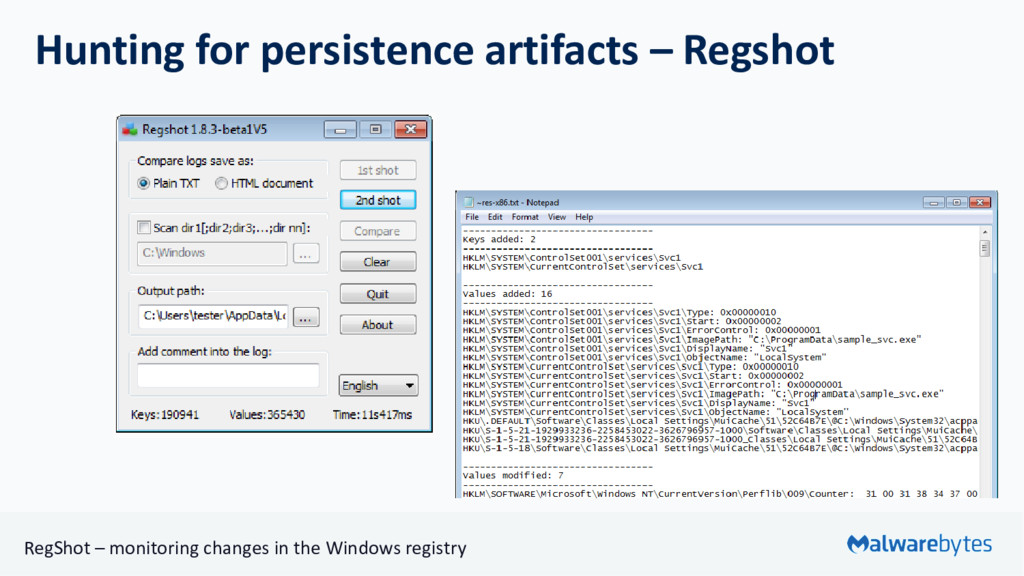
Hunting for persistence artifacts – Regshot RegShot – monitoring changes
in the Windows registry -
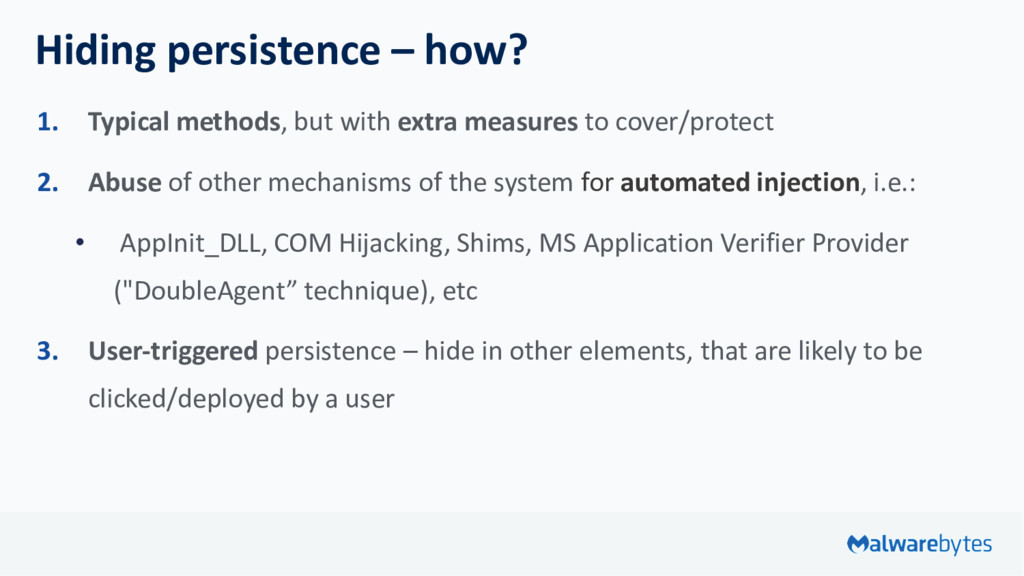
Hiding persistence – how? 1. Typical methods, but with extra
measures to cover/protect 2. Abuse of other mechanisms of the system for automated injection, i.e.: • AppInit_DLL, COM Hijacking, Shims, MS Application Verifier Provider ("DoubleAgent” technique), etc 3. User-triggered persistence – hide in other elements, that are likely to be clicked/deployed by a user -
Typical methods + extra measures •Last minute persistance (i.e. Dridex
v. 3) •Make sample inaccessible: ADS, special folders (i.e. Diamond Fox) •Hide in the plain sight: • behind legitimate applications: Korplug • hide the executable in the windows registry - „fileless” malware • use scripts to load malicious modules – often Powershell -
Last minute persistence 1. Inject and delete yourself -> no
malicious PE on the disk 2. Set callbacks on messages: WM_QUERYENDSESSION, WM_ENDSESSION to detect when the system is going to shut down 3. On shutdown event detected: write yourself on the disk and the Run key for the persistence 4. On system startup: delete the Run key, go to 1. https://www.cyberbit.net/wp- content/uploads/2016/09/Analysis-of-Dridex-AnD-for-IT.pdf -
Make file invisible/inaccessible – special folders •Example: Diamond Fox: https://blog.malwarebytes.com/threat-analysis/2017/03/diamond-fox-p1/
lpt8.{20D04FE0-3AEA-1069-A2D8-08002B30309D} Normal persistence key Not normal folder name -
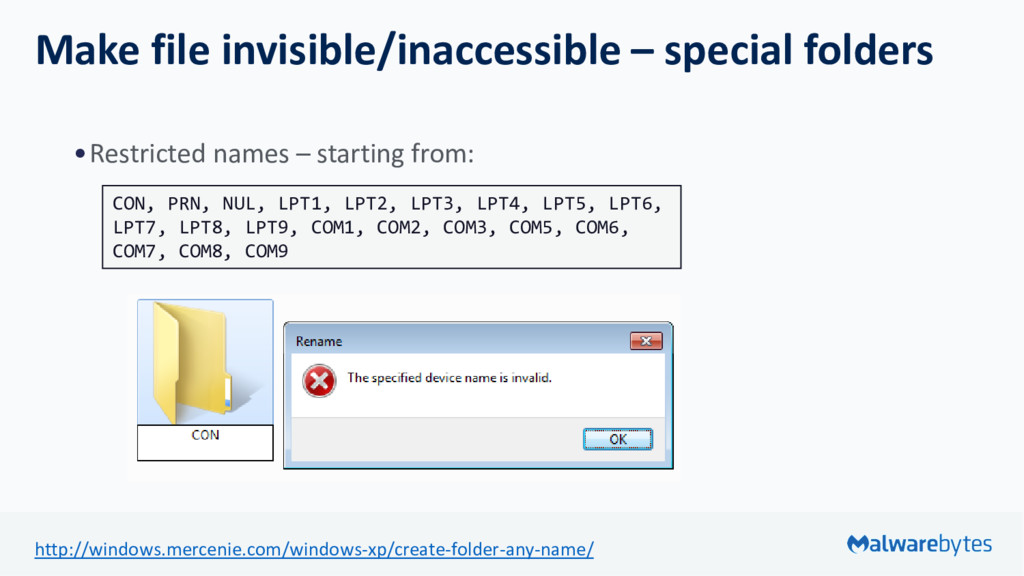
Make file invisible/inaccessible – special folders •Restricted names – starting
from: http://windows.mercenie.com/windows-xp/create-folder-any-name/ CON, PRN, NUL, LPT1, LPT2, LPT3, LPT4, LPT5, LPT6, LPT7, LPT8, LPT9, COM1, COM2, COM3, COM5, COM6, COM7, COM8, COM9 -
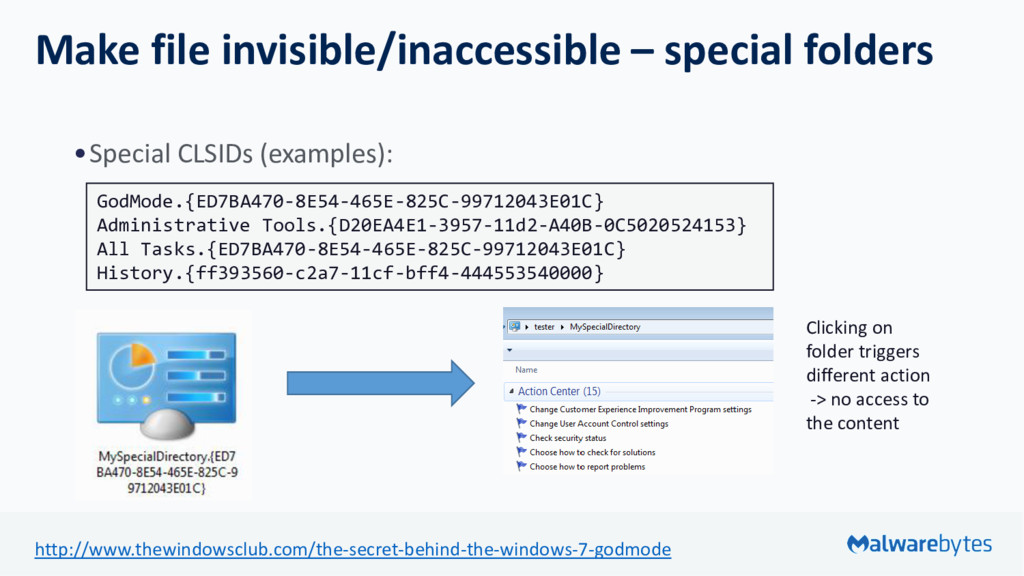
Make file invisible/inaccessible – special folders •Special CLSIDs (examples): http://www.thewindowsclub.com/the-secret-behind-the-windows-7-godmode
GodMode.{ED7BA470-8E54-465E-825C-99712043E01C} Administrative Tools.{D20EA4E1-3957-11d2-A40B-0C5020524153} All Tasks.{ED7BA470-8E54-465E-825C-99712043E01C} History.{ff393560-c2a7-11cf-bff4-444553540000} Clicking on folder triggers different action -> no access to the content -
Make file invisible/inaccessible – special folders Benefits from using special
folders: •User cannot access the content – special CLSID triggers event other than opening the folder •Cannot be removed/renamed in a typical way – restricted name prevents operating on the folder http://www.thewindowsclub.com/the-secret-behind-the-windows-7-godmode -
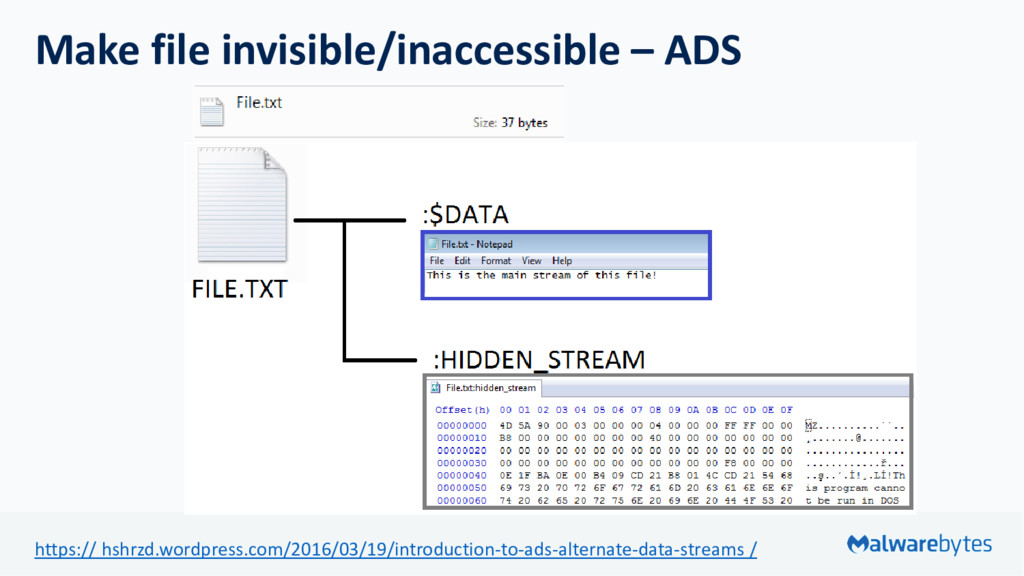
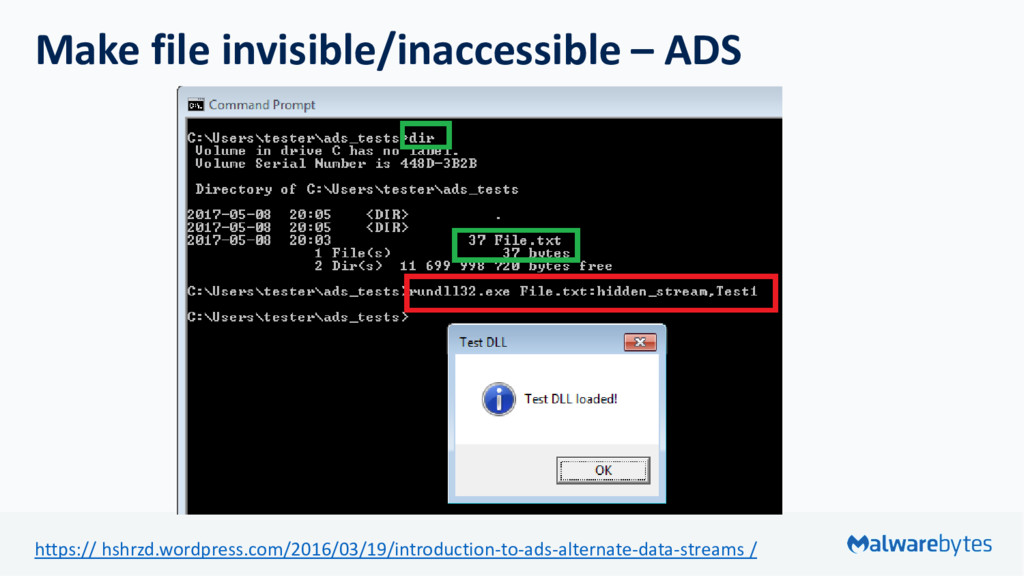
Make file invisible/inaccessible – ADS •ADS - Alternate Data Streams
•A feature of NTFS file system •Implemented, but practicaly not used by Windows... •Only the main stream of the file is listed/accessible in a typical way •Format: https:// hshrzd.wordpress.com/2016/03/19/introduction-to-ads-alternate-data-streams / <filename.extension>:<alternate_stream_name> -
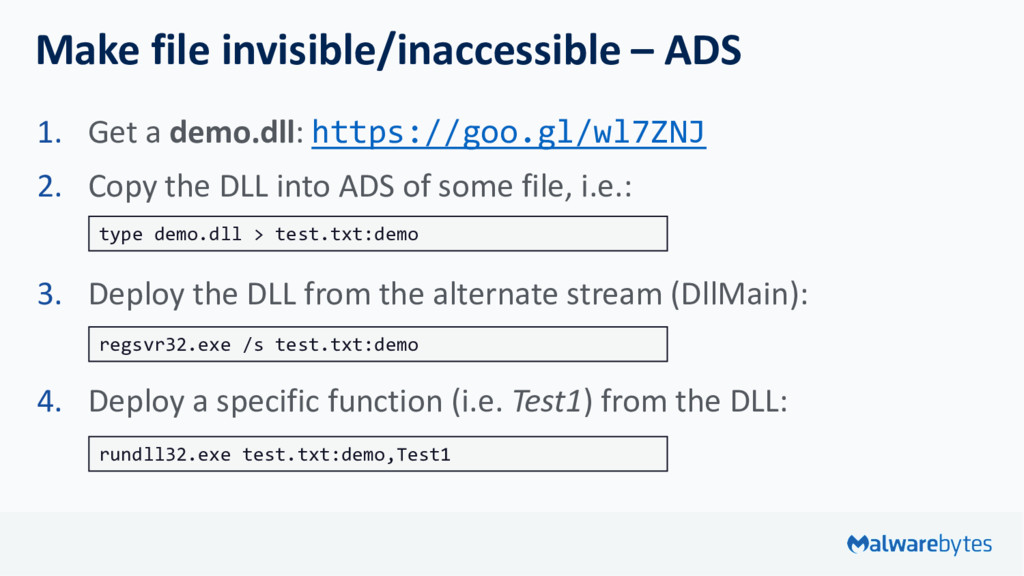
Make file invisible/inaccessible – ADS 1. Get a demo.dll: https://goo.gl/wl7ZNJ
2. Copy the DLL into ADS of some file, i.e.: 3. Deploy the DLL from the alternate stream (DllMain): 4. Deploy a specific function (i.e. Test1) from the DLL: type demo.dll > test.txt:demo regsvr32.exe /s test.txt:demo rundll32.exe test.txt:demo,Test1 -
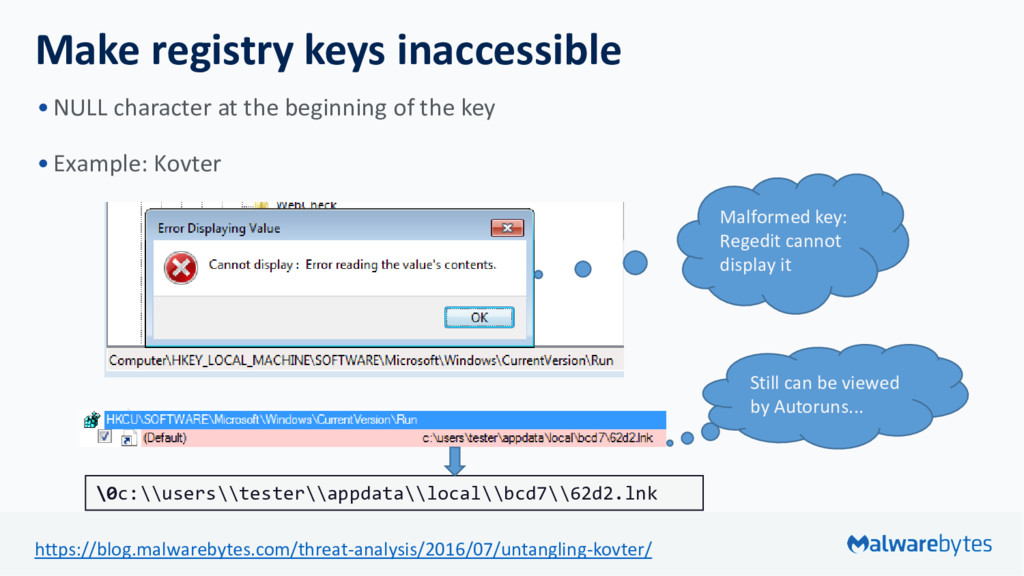
Make registry keys inaccessible •NULL character at the beginning of
the key •Example: Kovter https://blog.malwarebytes.com/threat-analysis/2016/07/untangling-kovter/ \0c:\\users\\tester\\appdata\\local\\bcd7\\62d2.lnk Malformed key: Regedit cannot display it Still can be viewed by Autoruns... -
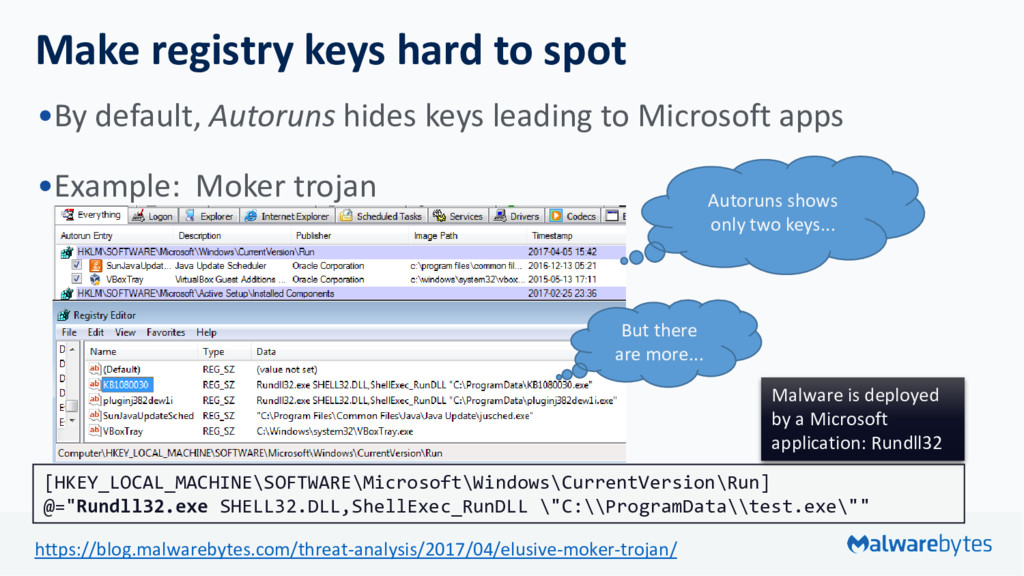
Make registry keys hard to spot •By default, Autoruns hides
keys leading to Microsoft apps •Example: Moker trojan https://blog.malwarebytes.com/threat-analysis/2017/04/elusive-moker-trojan/ [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] @="Rundll32.exe SHELL32.DLL,ShellExec_RunDLL \"C:\\ProgramData\\test.exe\"" Autoruns shows only two keys... But there are more... Malware is deployed by a Microsoft application: Rundll32 -
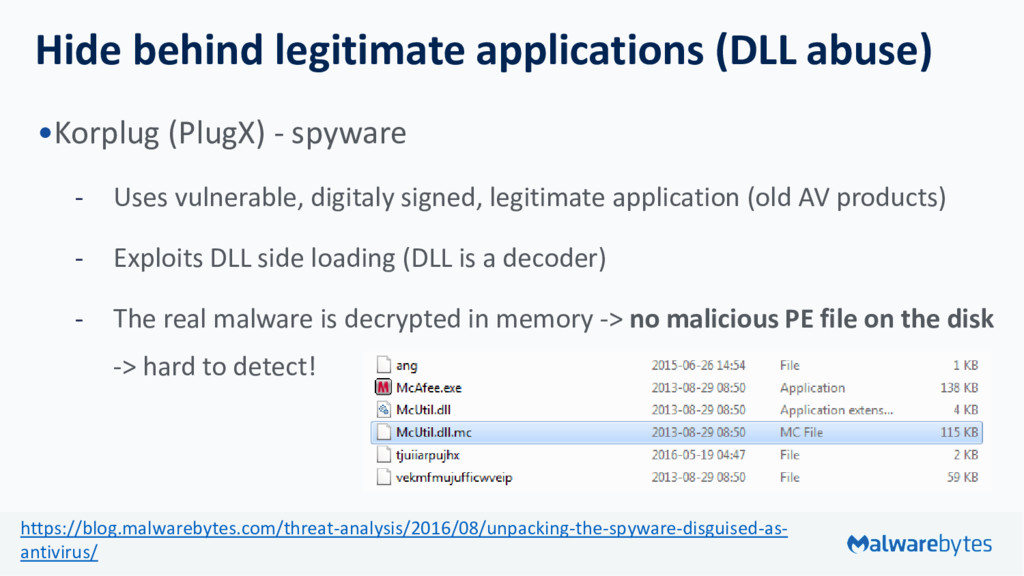
Hide behind legitimate applications (DLL abuse) •Korplug (PlugX) - spyware
- Uses vulnerable, digitaly signed, legitimate application (old AV products) - Exploits DLL side loading (DLL is a decoder) - The real malware is decrypted in memory -> no malicious PE file on the disk -> hard to detect! https://blog.malwarebytes.com/threat-analysis/2016/08/unpacking-the-spyware-disguised-as- antivirus/ -
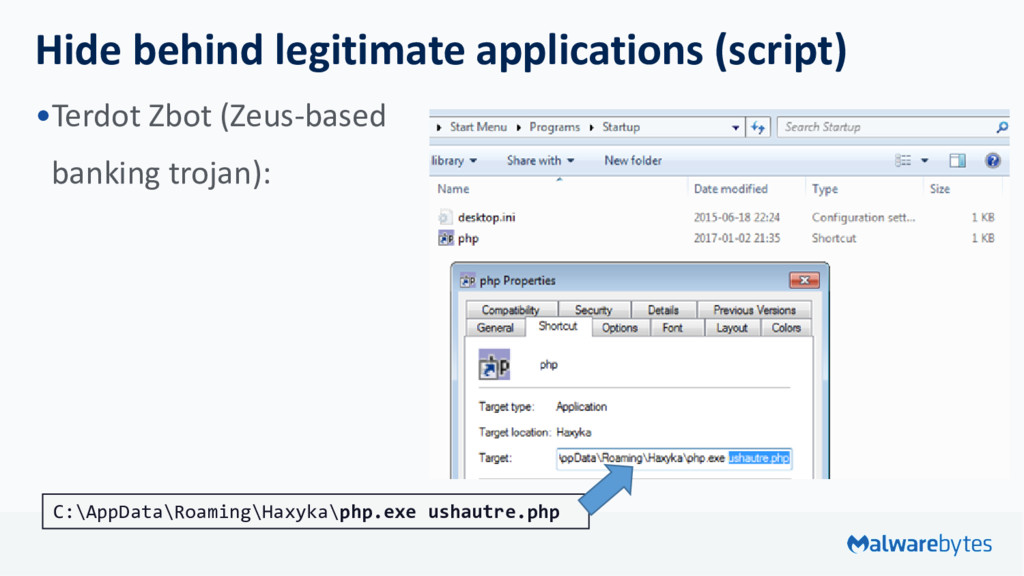
Hide behind legitimate applications (script) •Terdot Zbot (Zeus-based banking trojan):
C:\AppData\Roaming\Haxyka\php.exe ushautre.php -
Hide behind legitimate applications (script) •Terdot Zbot (Zeus-based banking trojan)
- Uses a legitimate application (PHP) - PHP is used to deploy obfuscated script - Script decrypts and loads the malware - The real malware is revealed in memory -> no malicious PE file on the disk - > hard to detect! https://blog.malwarebytes.com/cybercrime/2017/01/zbot-with-legitimate-applications-on-board/ -
Hide code in the registry •So called „fileless” malware •Phasebot
•Poweliks •Gootkit •Kovter •PoshSpy (APT29) using WMI component and PowerShell •Others... -
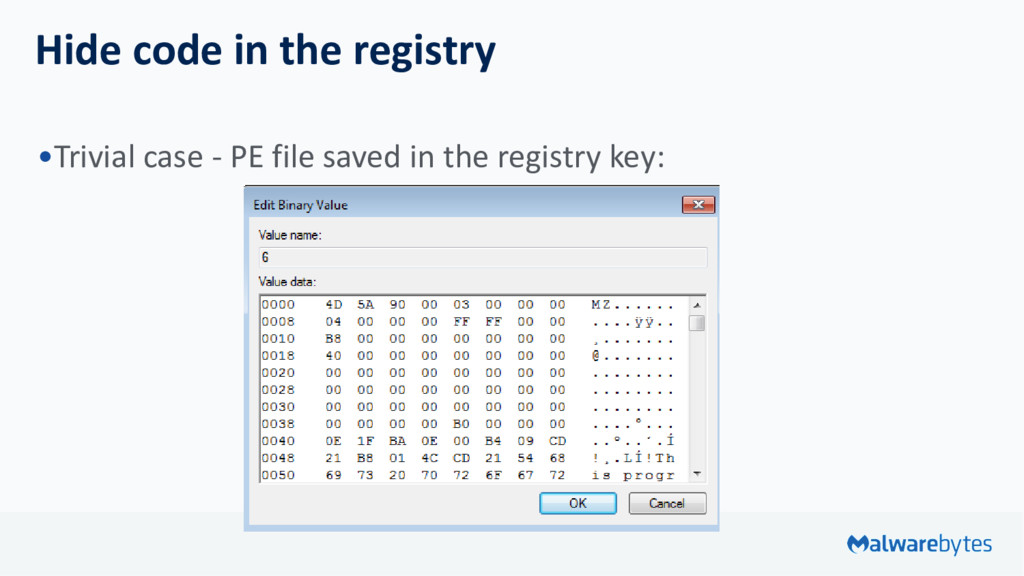
Hide code in the registry •Trivial case - PE file
saved in the registry key: -
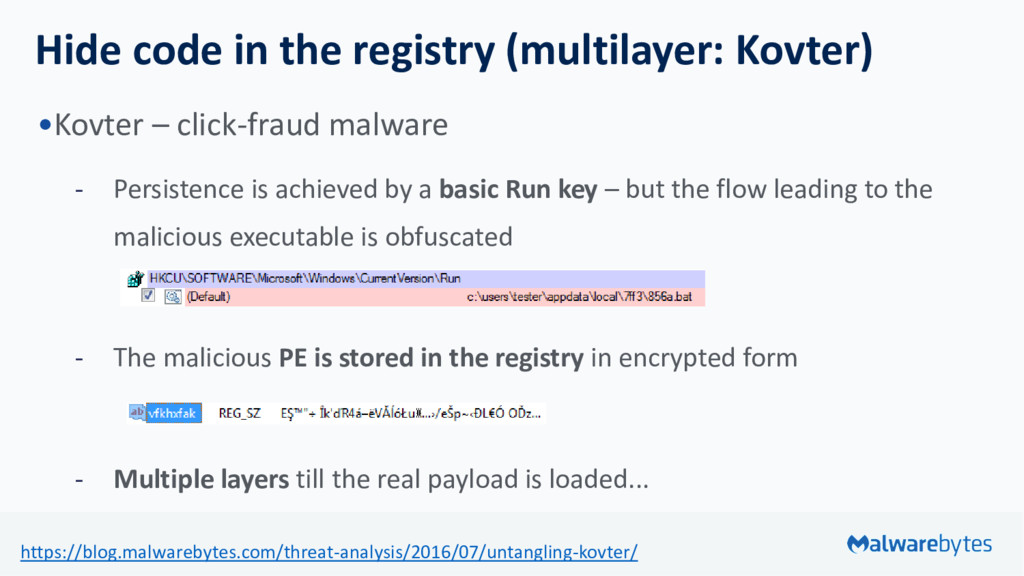
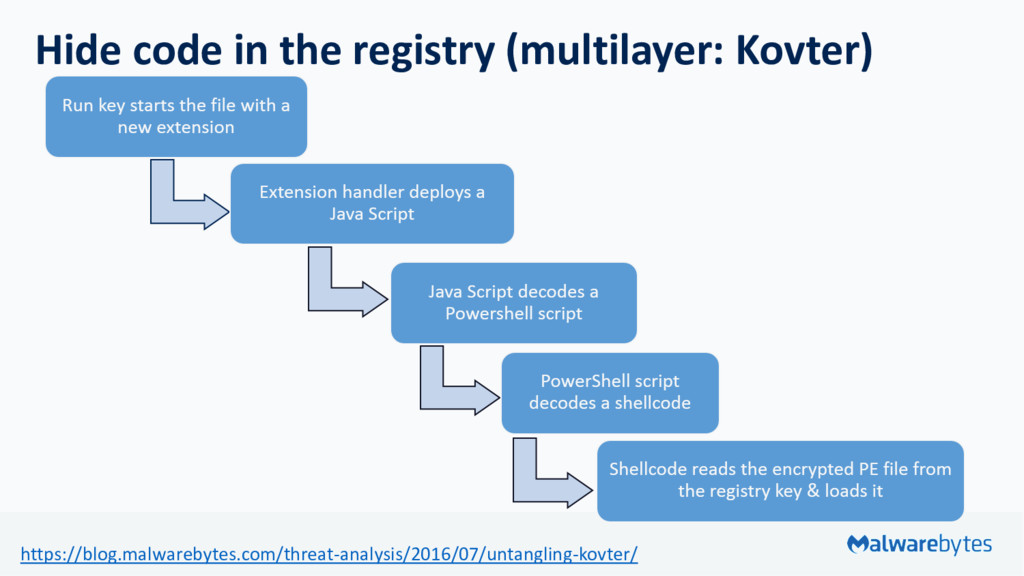
Hide code in the registry (multilayer: Kovter) •Kovter – click-fraud
malware - Persistence is achieved by a basic Run key – but the flow leading to the malicious executable is obfuscated - The malicious PE is stored in the registry in encrypted form - Multiple layers till the real payload is loaded... https://blog.malwarebytes.com/threat-analysis/2016/07/untangling-kovter/ -
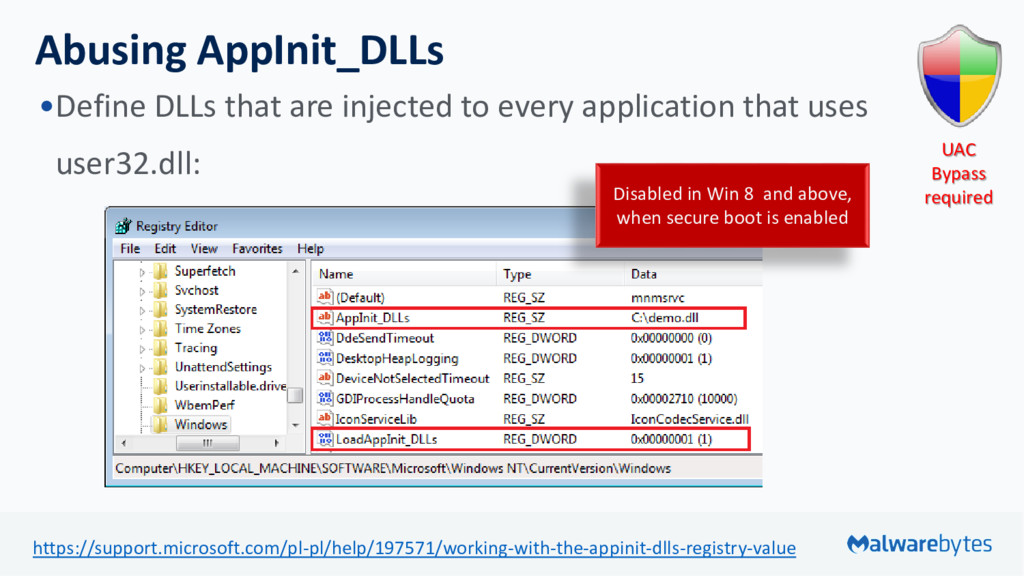
Abusing AppInit_DLLs •Define DLLs that are injected to every application
that uses user32.dll: https://support.microsoft.com/pl-pl/help/197571/working-with-the-appinit-dlls-registry-value UAC Bypass required Disabled in Win 8 and above, when secure boot is enabled -
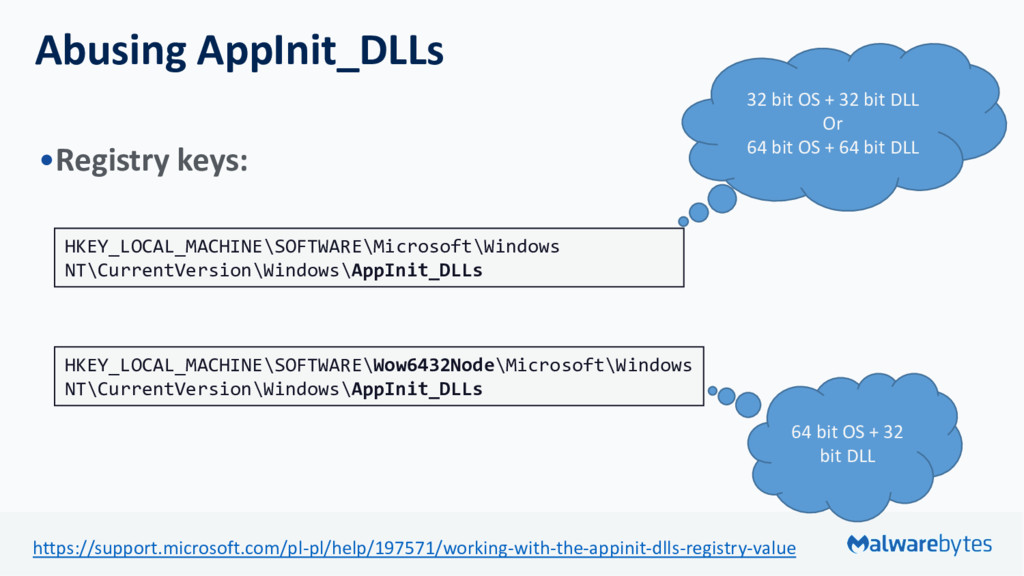
Abusing AppInit_DLLs •Registry keys: https://support.microsoft.com/pl-pl/help/197571/working-with-the-appinit-dlls-registry-value HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows\AppInit_DLLs HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows NT\CurrentVersion\Windows\AppInit_DLLs 32
bit OS + 32 bit DLL Or 64 bit OS + 64 bit DLL 64 bit OS + 32 bit DLL -
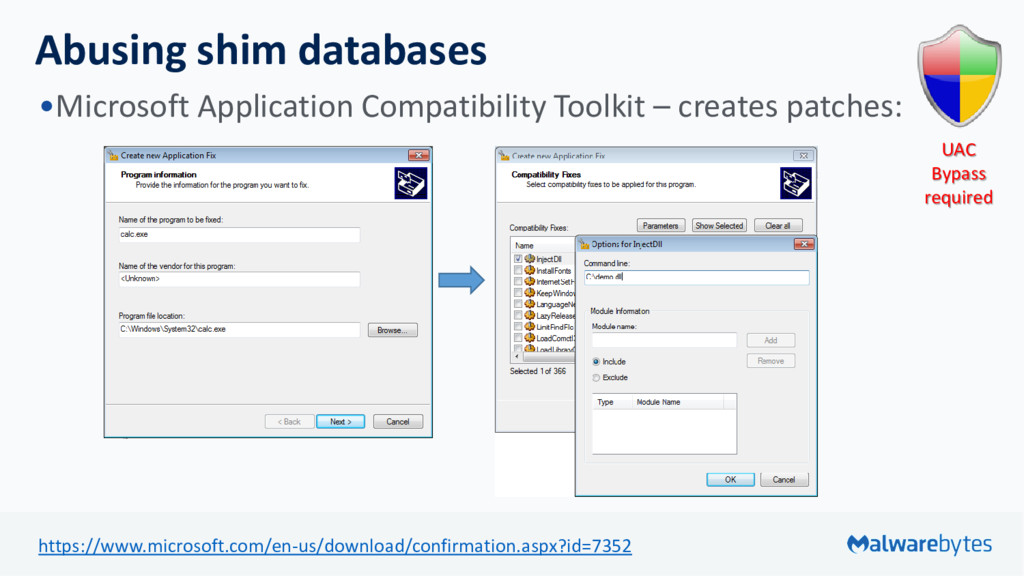
Abusing shim databases •Microsoft Application Compatibility Toolkit – creates patches:
https://www.microsoft.com/en-us/download/confirmation.aspx?id=7352 UAC Bypass required -
Abusing shim databases •Shim Database •Allows setting automated injection of
a patch into selected application •Can be used to automatically load malicious modules when the target application is deployed (DLL, shellcode, etc) UAC Bypass required https://www.fireeye.com/blog/threat-research/2017/05/fin7-shim-databases-persistence.html -
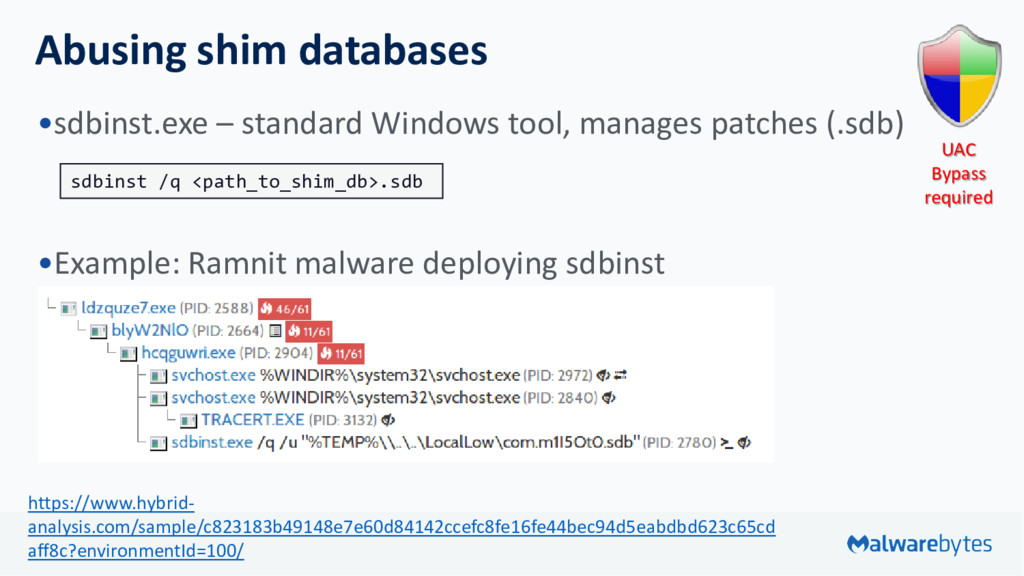
Abusing shim databases •sdbinst.exe – standard Windows tool, manages patches
(.sdb) •Example: Ramnit malware deploying sdbinst https://www.hybrid- analysis.com/sample/c823183b49148e7e60d84142ccefc8fe16fe44bec94d5eabdbd623c65cd aff8c?environmentId=100/ UAC Bypass required sdbinst /q <path_to_shim_db>.sdb -
Abusing shim databases •To trigger less alerts, install a shim
without sdbinst.exe •Example of edited keys: UAC Bypass required [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\InstalledSDB] [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\InstalledSDB\{7c6002f0-559a-488a-9fc1-bd54c33fdfa9}] "DatabasePath"=<path_to_shim>.sdb "DatabaseType"=dword:00010000 [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\Custom\<shimmed_app>.exe] "{7c6002f0-559a-488a-9fc1-bd54c33fdfa9}.sdb"=hex(b):90,58,2d,0d,1a,b7,d2,01 https://github.com/hasherezade/persistence_demos/tree/master/shim_persist -
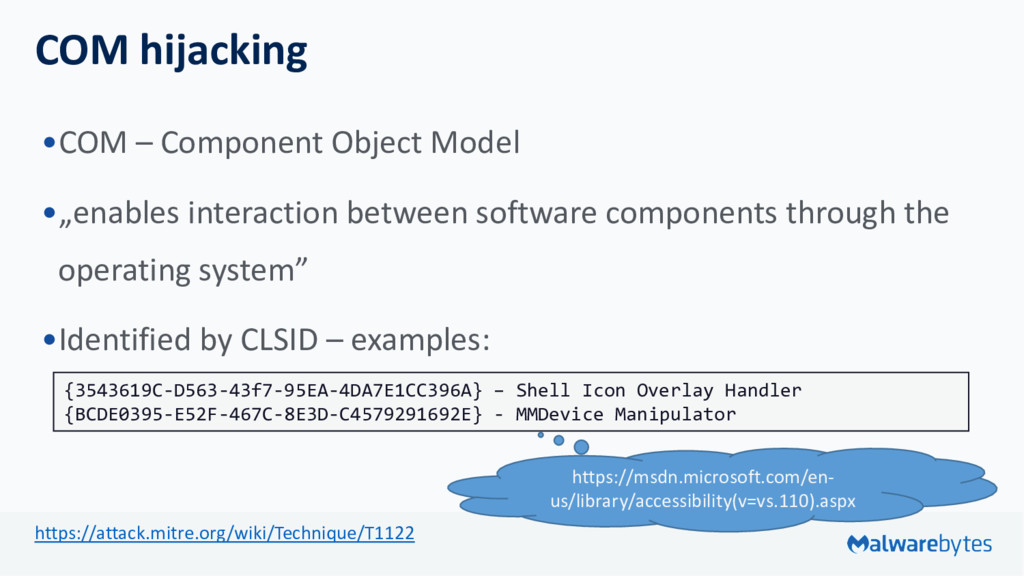
COM hijacking •COM – Component Object Model •„enables interaction between
software components through the operating system” •Identified by CLSID – examples: https://attack.mitre.org/wiki/Technique/T1122 {3543619C-D563-43f7-95EA-4DA7E1CC396A} – Shell Icon Overlay Handler {BCDE0395-E52F-467C-8E3D-C4579291692E} - MMDevice Manipulator https://msdn.microsoft.com/en- us/library/accessibility(v=vs.110).aspx -
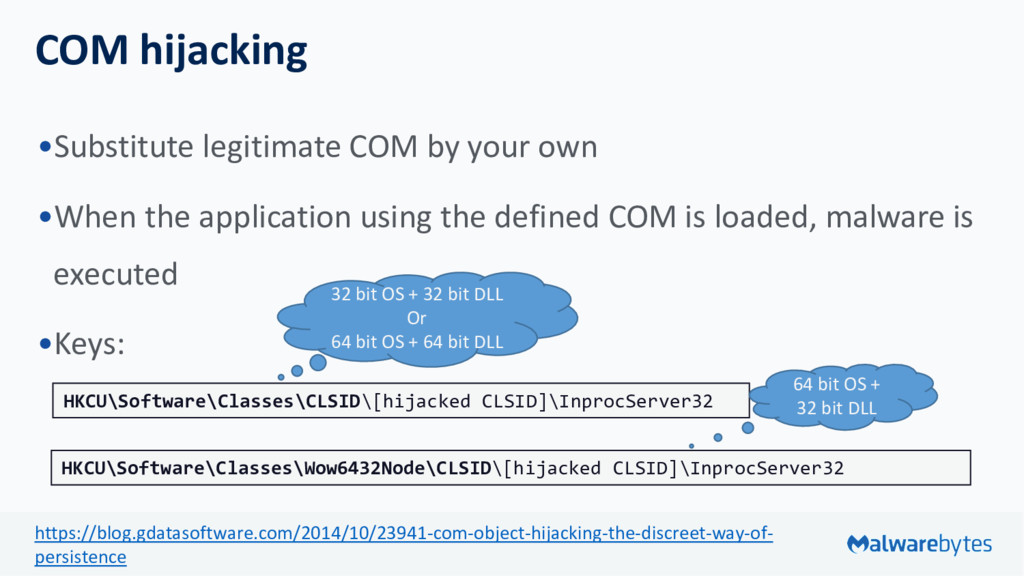
COM hijacking •Substitute legitimate COM by your own •When the
application using the defined COM is loaded, malware is executed •Keys: https://blog.gdatasoftware.com/2014/10/23941-com-object-hijacking-the-discreet-way-of- persistence HKCU\Software\Classes\CLSID\[hijacked CLSID]\InprocServer32 32 bit OS + 32 bit DLL Or 64 bit OS + 64 bit DLL 64 bit OS + 32 bit DLL HKCU\Software\Classes\Wow6432Node\CLSID\[hijacked CLSID]\InprocServer32 -
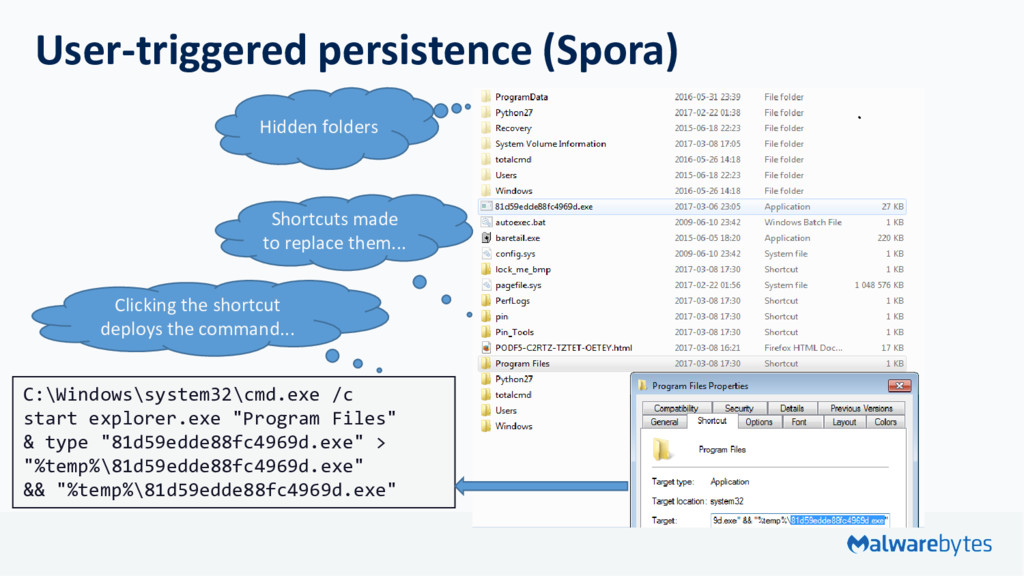
User-triggered persistence (Spora) C:\Windows\system32\cmd.exe /c start explorer.exe "Program Files" &
type "81d59edde88fc4969d.exe" > "%temp%\81d59edde88fc4969d.exe" && "%temp%\81d59edde88fc4969d.exe" Hidden folders Shortcuts made to replace them... Clicking the shortcut deploys the command... -
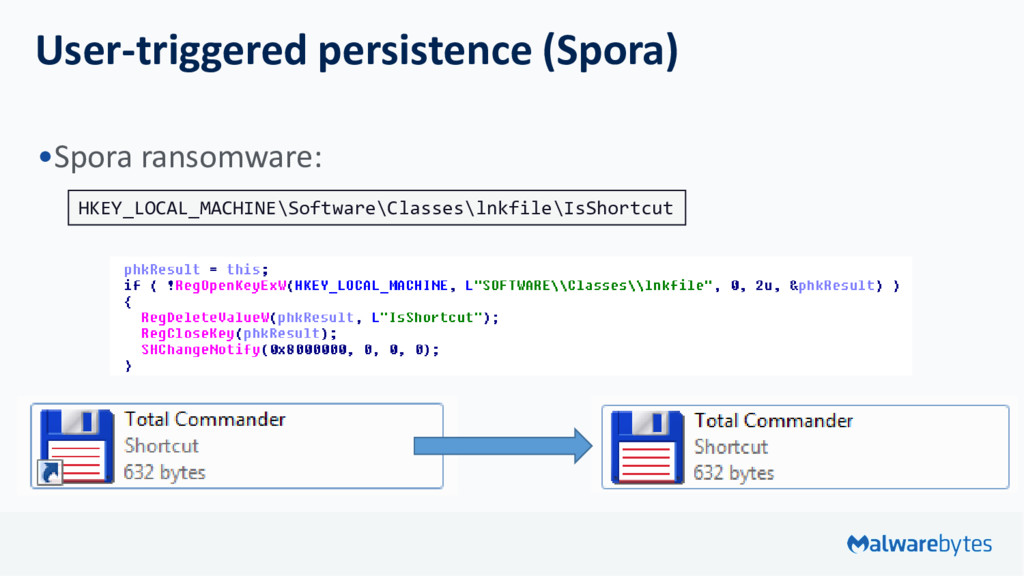
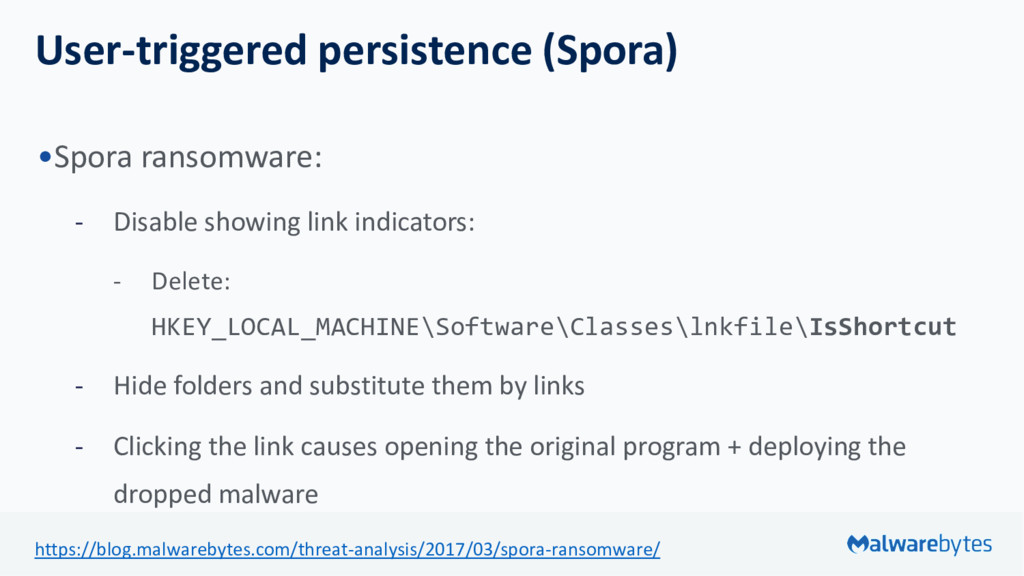
User-triggered persistence (Spora) •Spora ransomware: - Disable showing link indicators:
- Delete: HKEY_LOCAL_MACHINE\Software\Classes\lnkfile\IsShortcut - Hide folders and substitute them by links - Clicking the link causes opening the original program + deploying the dropped malware https://blog.malwarebytes.com/threat-analysis/2017/03/spora-ransomware/ -
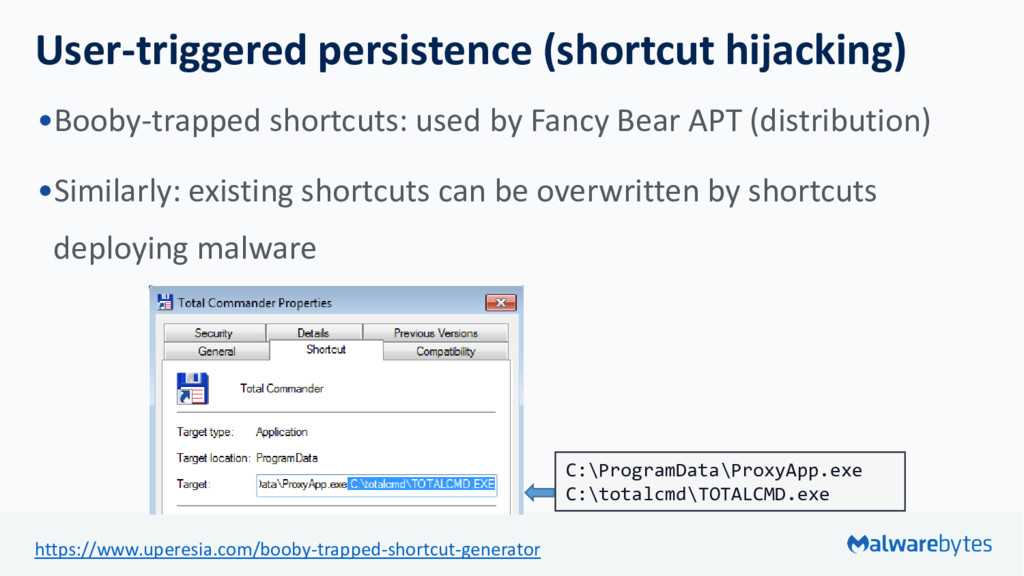
User-triggered persistence (shortcut hijacking) •Booby-trapped shortcuts: used by Fancy Bear
APT (distribution) •Similarly: existing shortcuts can be overwritten by shortcuts deploying malware https://www.uperesia.com/booby-trapped-shortcut-generator C:\ProgramData\ProxyApp.exe C:\totalcmd\TOTALCMD.exe -
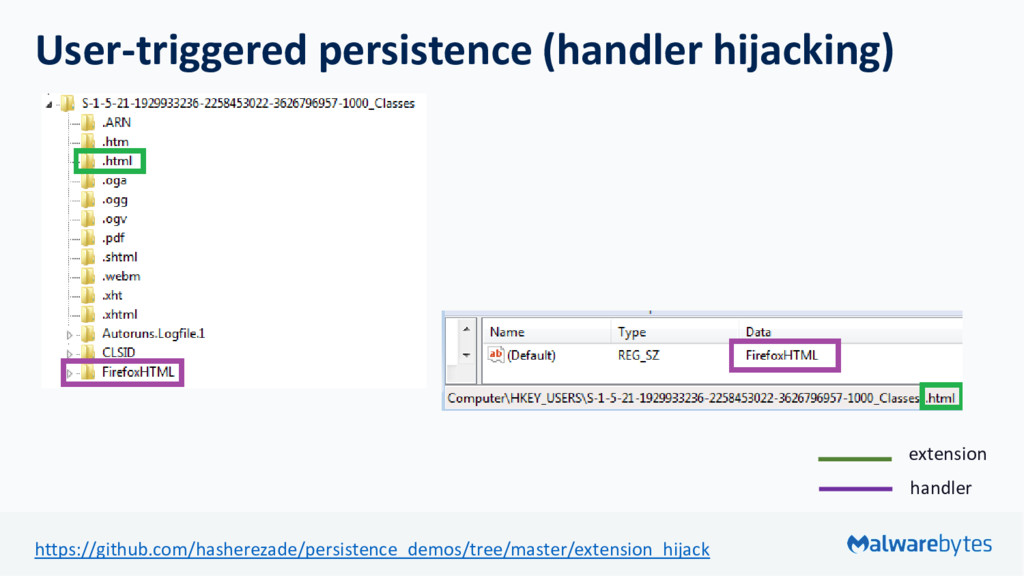
User-triggered persistence (handler hijacking) •Applications handling particular extensions are defined
in the registry •Globaly defined extensions and handlers: in HKEY_CLASSES_ROOT •It can be also defined per user: HKEY_USERS -> <user SID>_Classes •Redefine a handler: no Administrator rights required https://github.com/hasherezade/persistence_demos/tree/master/extension_hijack -
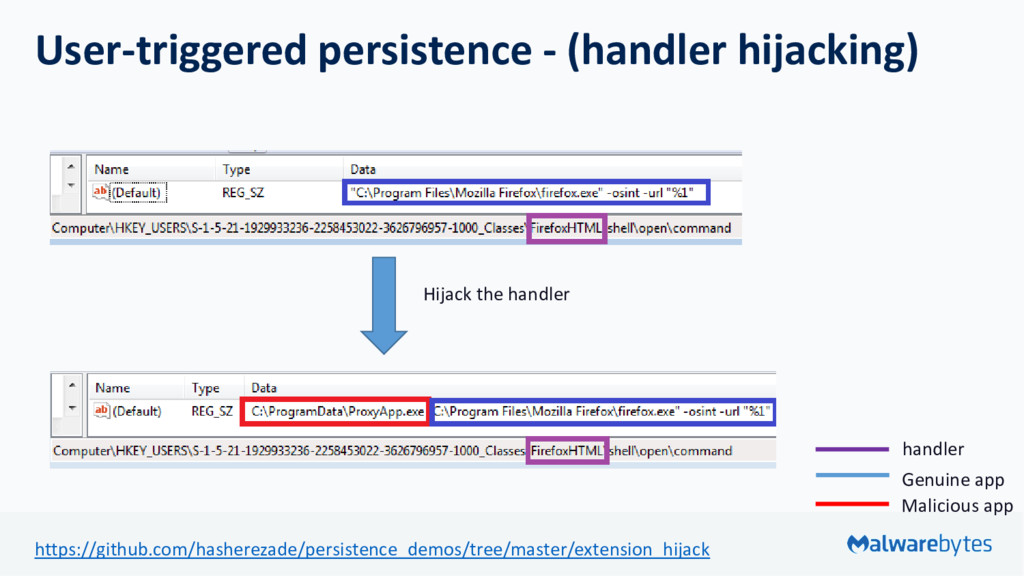
User-triggered persistence (handler hijacking) •When the user click a file
with hijacked extension, the malware is deployed •DEMO: •https://goo.gl/RGPiuY https://github.com/hasherezade/persistence_demos/tree/master/extension_hijack -
Conclusions •Authors of the malware are very creative in finding
new ways of hiding persistence •The easiest way to detect the persistence method is by observing the installation – post-infection analysis is much harder •„Fileless” malware also creates artifacts that can be found in a typical way -
Additional material • [1] https://www.fireeye.com/blog/threat-research/2017/03/dissecting_one_ofap.htm • [2] https://cybellum.com/doubleagentzero-day-code-injection-and-persistence-technique/ • [3]
https://securelist.com/blog/research/77403/fileless-attacks-against-enterprise-networks/ • [4] http://herrcore.blogspot.com.tr/2015/06/malware-persistence-with.html • [5] https://blog.gdatasoftware.com/2014/10/23941-com-object-hijacking-the-discreet-way-of-persistence - COM Object Hijacking • [6] https://www.youtube.com/watch?v=wQEnUISOZPI – „Shims for the Win” • [7] http://0xthem.blogspot.com/2014/03/t-emporal-persistence-with-and-schtasks.html - BITS backdoor • [8] http://www.hexacorn.com/blog/2017/03/18/beyond-good-ol-run-key-part-60/ - persistence via Windows update • [9] https://isc.sans.edu/forums/diary/Wipe+the+drive+Stealthy+Malware+Persistence+Part+3/15448/ - SANS on stealthy malware persistence methods
 hshrzd
 masasuzu
 maguroalternative
 henryofficial
 kworkdev
 pipepasta
 wadayusuke
 sergicalsix
 ryudai
 rist
 raksulrecruiting
 itosoft
 amarelo_n24
 rocio
 skipperchong
 wayneb77
 tenderlove
 honzajavorek
 aleyda
 kneath
 keathley
 427marketing
 trallard
 katarinadahlin
 tmiket