Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Using Python to Fight Cybercrime
Search
Kyle Maxwell
April 26, 2015
Technology
240
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Using Python to Fight Cybercrime
A survey of the ways I use Python as a DFIR / threat intel professional
Kyle Maxwell
April 26, 2015
More Decks by Kyle Maxwell
See All by Kyle Maxwell
In the Lair of the Beholder
krmaxwell
0
120
Incident Patterns
krmaxwell
0
470
Hackertainment
krmaxwell
1
240
Threat Intelligence for Incident Response
krmaxwell
0
210
From Minion to Engineer
krmaxwell
0
140
Why XOR Crypto Sucks
krmaxwell
0
230
Open Source Threat Intelligence - Shakacon
krmaxwell
1
950
Secure Blogging
krmaxwell
0
150
Grabbing fresh evil bits: Maltrieve
krmaxwell
1
170
Other Decks in Technology
See All in Technology
[2026 Oracle Technical Deep Dive] エンタープライズAIエージェントを支えるOCIソリューション。ラインナップと特徴を理解しよう! (2026年9月17日開催)
oracle4engineer
PRO
0
530
検証フェーズはAIの回答を判断するための学習機会
toru_kubota
2
500
[2026 Oracle Technical Deep Dive] AI時代のアプリケーションを支えるCloud NativeとJava EEモダナイゼーション (2026年9月17日開催)
oracle4engineer
PRO
0
120
1万名の社員が使う認証基盤で どう信頼性を担保するか?
kairim0
0
210
『GOエコノミー 』(相乗りサービス) におけるスペック駆動開発
mot_techtalk
1
310
ai_cording_with_k8s_knowledge.pdf
mochizuki875
1
290
サーバーフルコンピューティング?AWS Lambda
iwatatomoya
1
250
予測不能な実行エージェントを安全にサクッと試せるサンドボックス環境の話
sansantech
PRO
0
120
Datadog の学び方 - あるいは、オブザーバビリティを学ぶとは何か
mananyuki
1
460
営業オントロジーの作り方と、エージェントからの辿り方 ── ナレッジワークの現場から
kworkdev
PRO
1
270
組み立てて楽しむ AWS Blocks 入門
kmiya84377
0
210
いちAWSエンジニアのAI活用を振り返る #devio2026 / devio osaka 2026 kawahara
masahirokawahara
2
380
Featured
See All Featured
HTML-Aware ERB: The Path to Reactive Rendering @ RubyCon 2026, Rimini, Italy
marcoroth
5
770
GitHub's CSS Performance
jonrohan
1033
470k
Noah Learner - AI + Me: how we built a GSC Bulk Export data pipeline
techseoconnect
PRO
0
450
jQuery: Nuts, Bolts and Bling
dougneiner
66
8.6k
Sharpening the Axe: The Primacy of Toolmaking
bcantrill
46
3k
実際に使うSQLの書き方 徹底解説 / pgcon21j-tutorial
soudai
PRO
203
76k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
State of Search Keynote: SEO is Dead Long Live SEO
ryanjones
0
310
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.1k
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
590
Done Done
chrislema
187
17k
Side Projects
sachag
456
43k
Transcript
Using Python to Fight Cybercrime Kyle Maxwell, PyData Dallas April
26, 2015 @kylemaxwell http://goo.gl/oPQ8k2
What I Do Incident Response Threat Intelligence
What I Don’t Do Application Security Penetration Testing
Areas of Interest Reverse-engineer malware Analyze incidents for trends Track
bad guys
Triage Malware What is it? ➔ hashing ➔ IOC matching
What does it do? ➔ behavioral analysis
Manage Malware Maltrieve [ maltrieve.org ] ➔ web crawler to
fetch malware Viper [ viper.li ] ➔ store and classify malware
Cuckoo Sandbox [ cuckoosandbox.org ] “Throw any suspicious file at
it and in a matter of seconds Cuckoo will provide you back some detailed results outlining what such file did when executed inside an isolated environment.” Analyze Malware
Track bad guys Moving beyond technical indicators (IOCs) Enumerate infrastructure
Attribution (with caveats) Describe methods
All About the APIs
Passive DNS What resolutions were seen, and when?
WHOIS Historical: ➔ registrant changes over time Reverse: ➔ domains
with same registrant
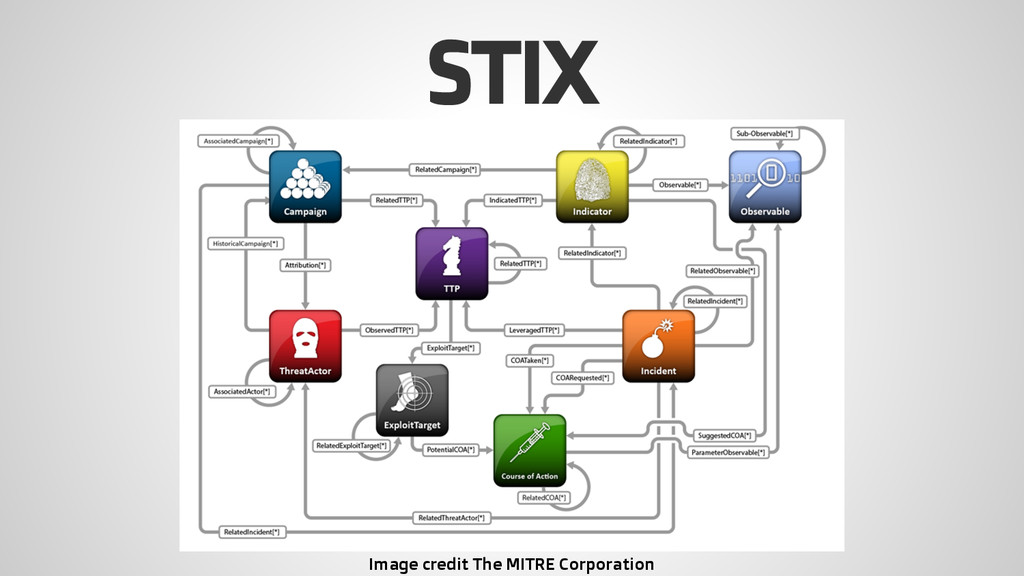
Image credit The MITRE Corporation STIX
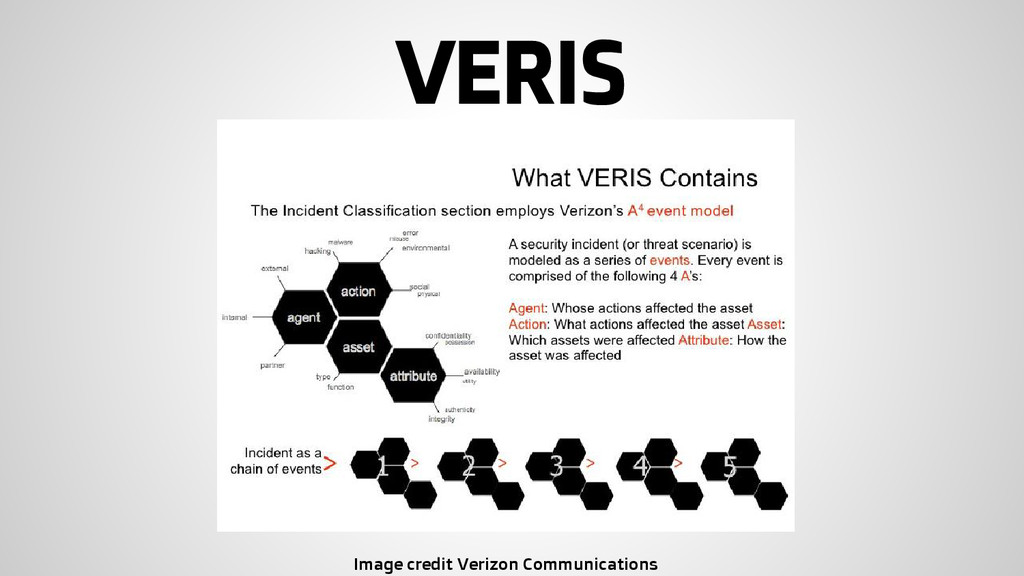
VERIS Image credit Verizon Communications
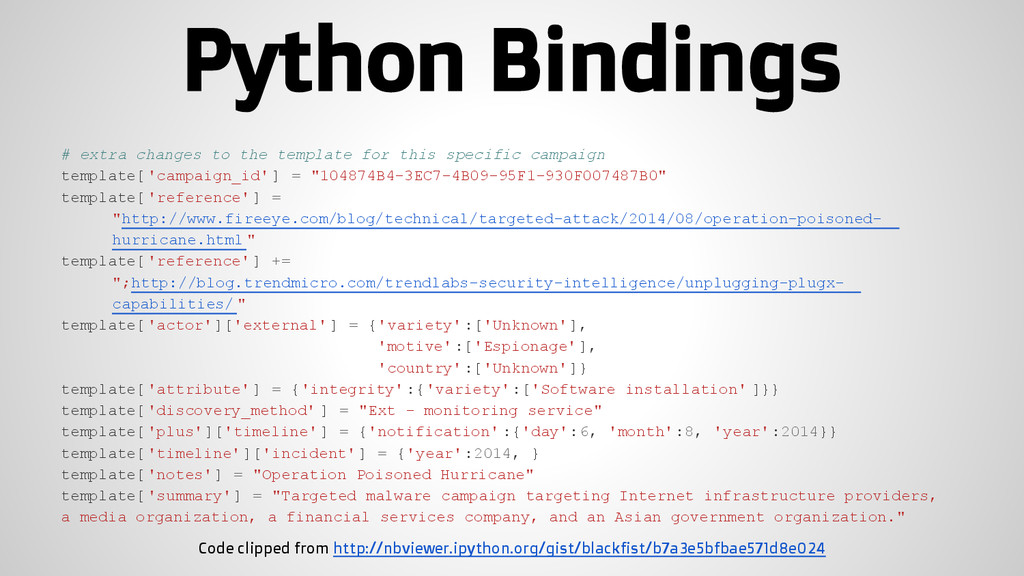
Python Bindings # extra changes to the template for this
specific campaign template['campaign_id' ] = "104874B4-3EC7-4B09-95F1-930F007487B0" template['reference' ] = "http://www.fireeye.com/blog/technical/targeted-attack/2014/08/operation-poisoned- hurricane.html " template['reference' ] += ";http://blog.trendmicro.com/trendlabs-security-intelligence/unplugging-plugx- capabilities/ " template['actor']['external'] = {'variety':['Unknown'], 'motive':['Espionage' ], 'country':['Unknown']} template['attribute' ] = {'integrity' :{'variety':['Software installation' ]}} template['discovery_method' ] = "Ext - monitoring service" template['plus']['timeline'] = {'notification' :{'day':6, 'month':8, 'year':2014}} template['timeline']['incident'] = {'year':2014, } template['notes'] = "Operation Poisoned Hurricane" template['summary'] = "Targeted malware campaign targeting Internet infrastructure providers, a media organization, a financial services company, and an Asian government organization." Code clipped from http://nbviewer.ipython.org/gist/blackfist/b7a3e5bfbae571d8e024
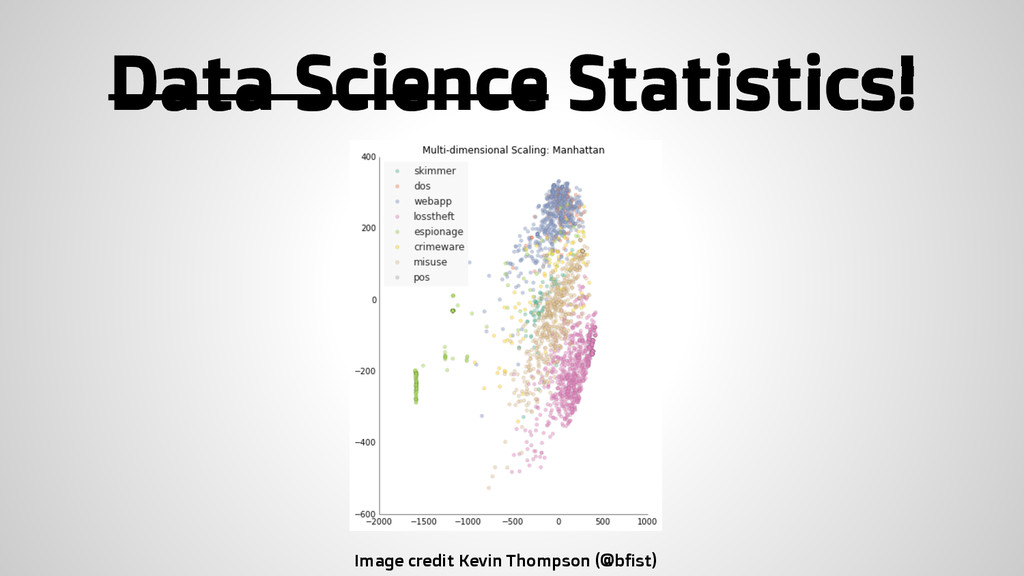
Data Science Statistics! Image credit Kevin Thompson (@bfist)
So much else! ➔ Log analysis ➔ Web interfaces ➔
Forensic examinations ➔ Red teaming / pentesting
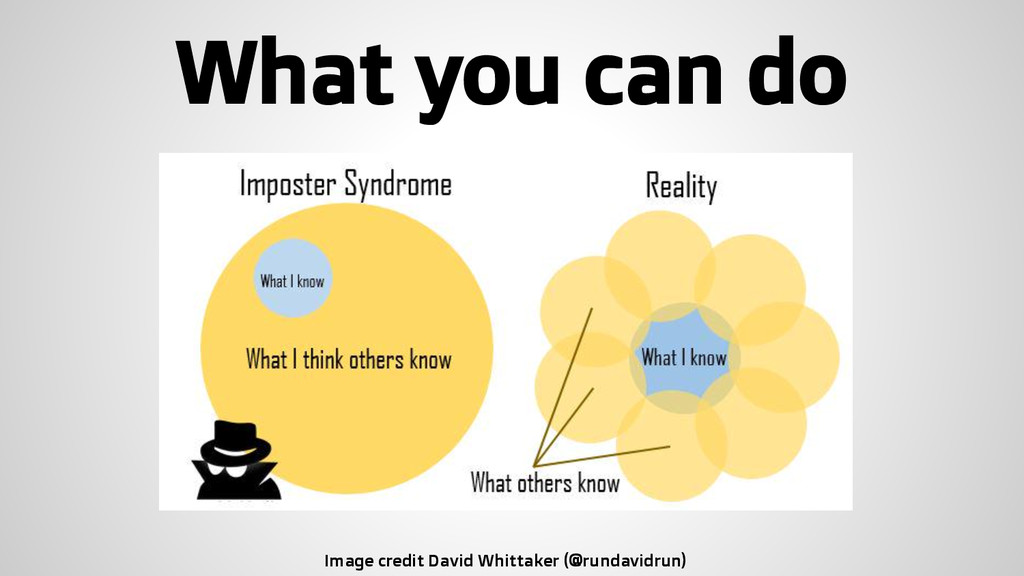
What you can do Image credit David Whittaker (@rundavidrun)
Q&A @kylemaxwell || xwell.org github.com/krmaxwell Icons made by Freepik from
www.flaticon.com and used under Creative Commons license


 krmaxwell
 oracle4engineer
 toru_kubota
 kairim0
 mot_techtalk
 mochizuki875
 iwatatomoya
 sansantech
 mananyuki
 kworkdev
 kmiya84377
 masahirokawahara
 marcoroth
 jonrohan
 techseoconnect
 dougneiner
 bcantrill
 soudai
 destraynor
 ryanjones
 reverentgeek
 marktimemedia
 chrislema
 sachag