Share
Embed
ADRecon BH USA 2018 : Arsenal and DEF CON 26 Demo Labs Presentation
Demo of ADRecon presented on 08th and 12th August at BlackHat USA 2018 Arsenal and DEF CON 26 Demo Labs.
https://www.blackhat.com/us-18/arsenal/schedule/index.html#adrecon-active-directory-recon-11912
https://www.defcon.org/html/defcon-26/dc-26-demolabs.html
Prashant
August 08, 2018
Transcript
46 slides
-
Sydney Level 8, 59 Goulburn Street Sydney NSW 2000 Melbourne
Level 15, 401 Docklands Drive Docklands VIC 3008 Tel. 1300 922 923 Intl. +61 2 9290 4444 www.senseofsecurity.com.au Sense of Security Pty Ltd ABN 14 098 237 908 @ITSecurityAU Compliance, Protection & Business Confidence 08 & 11 August 18 ADRecon https://github.com/sense-of-security/adrecon BlackHat USA 2018 – Arsenal and DEF CON 26 Demo Labs -
What is ADRecon ? 08 & 11 August 18 •
ADRecon provides a holistic picture of the current state of AD environment. • Extracts & combines various artefacts from an Active Directory environment • The information is presented in specially formatted Excel report (optional) • Summary views with metrics to facilitate analysis (Excel Only) • Can be run by normal unprivileged domain user* using • a domain-member or • a standalone workstation * some features require privileged user. Sense of Security - 2018 -
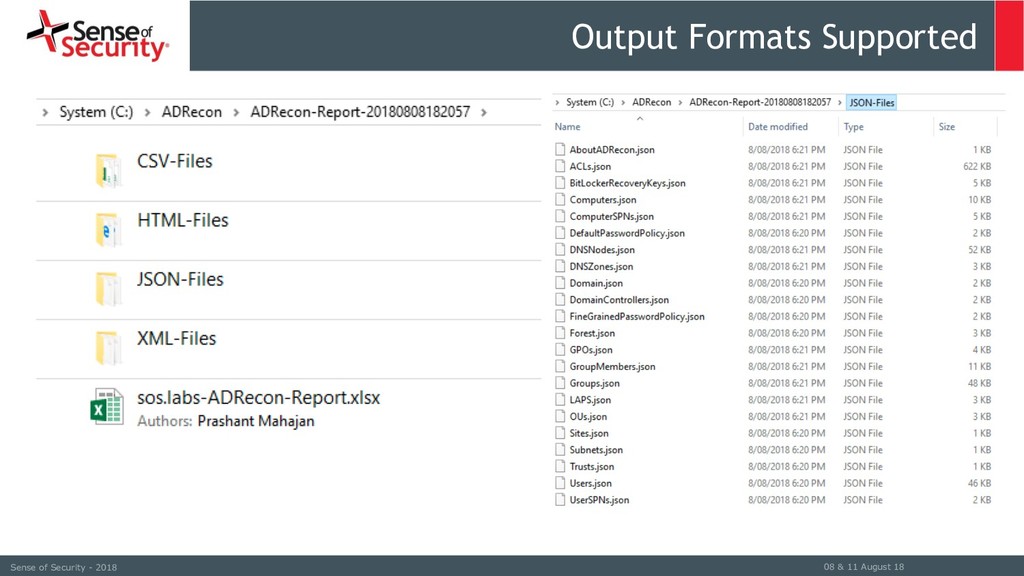
Output Formats Supported 08 & 11 August 18 Sense of
Security - 2018 -
• Blue Team • Purple Team • Red Team •
System administrators • Security professionals Friendly plug • BloodHound 2.0, LogonTracer, PowerUpSQL: A PowerShell Toolkit for Attacking SQL Servers in Enterprise Environments at BlackHat USA 2018 - Arsenal • ADVANCED INFRASTRUCTURE HACKING - 2018 EDITION Training – NotSoSecure at BlackHat Europe 2018 (3 - 6 December) 08 & 11 August 18 Sense of Security - 2018 Who uses ADRecon ? -
1. User credentials and access to a Windows host with
network access to the Domain Controller • TCP 9389 for ADWS or • TCP 389 for LDAP 2. Windows Host Prerequisites • .NET Framework 3.0 or later (Windows 7 includes 3.0) • PowerShell 2.0 or later (Windows 7 includes 2.0) 3. Optional • Microsoft Excel (to generate the report) • Remote Server Administration Tools (RSAT): • Windows 10 (https://www.microsoft.com/en-au/download/details.aspx?id=45520) • Windows 7 (https://www.microsoft.com/en-au/download/details.aspx?id=7887) 08 & 11 August 18 Sense of Security - 2018 Prerequisites -
08 & 11 August 18 Sense of Security - 2018
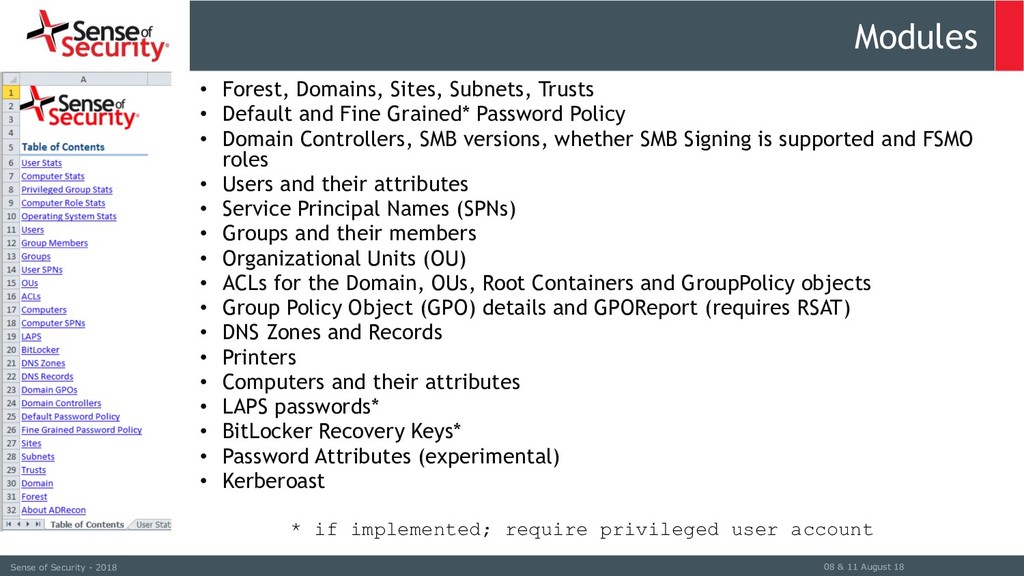
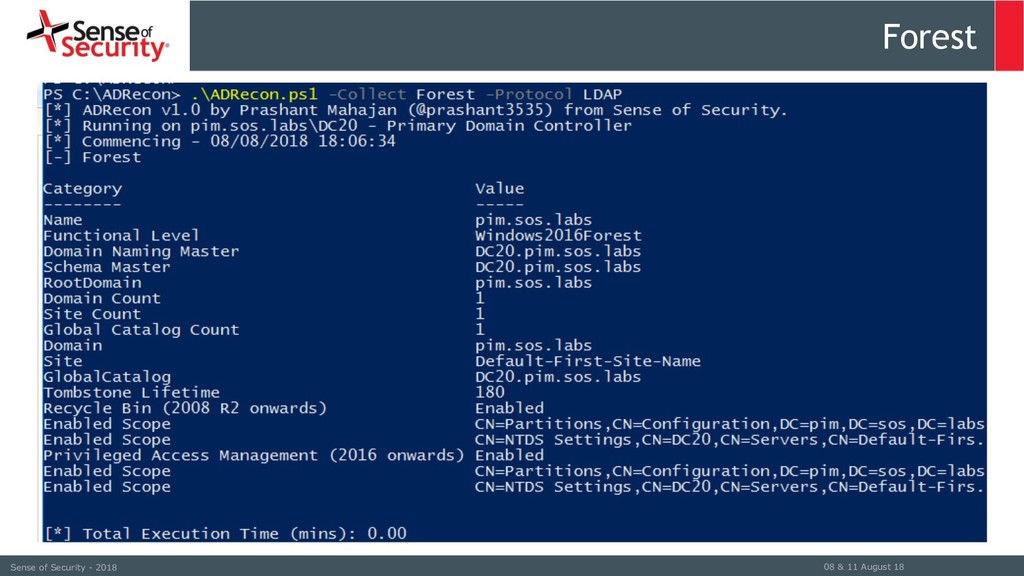
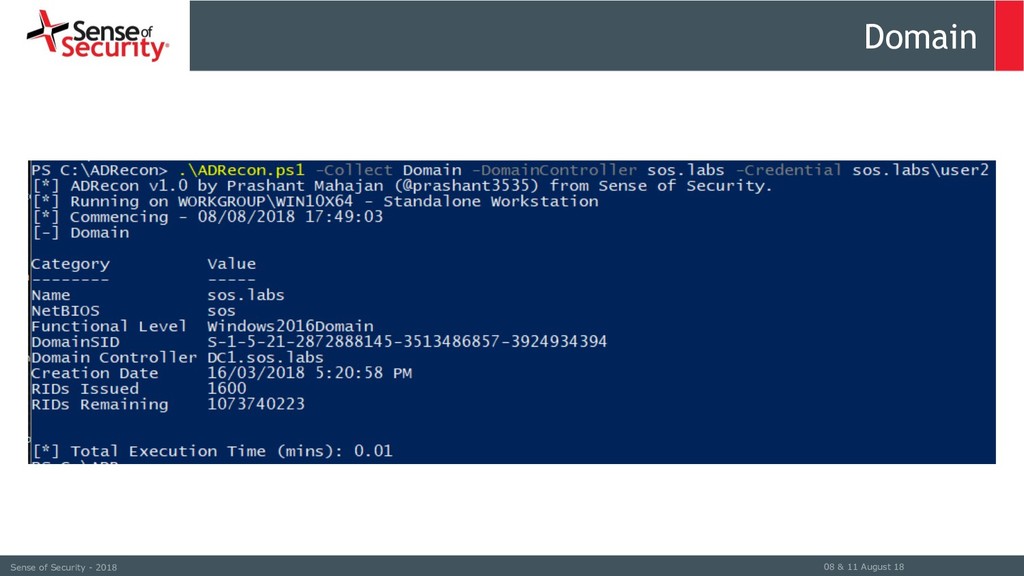
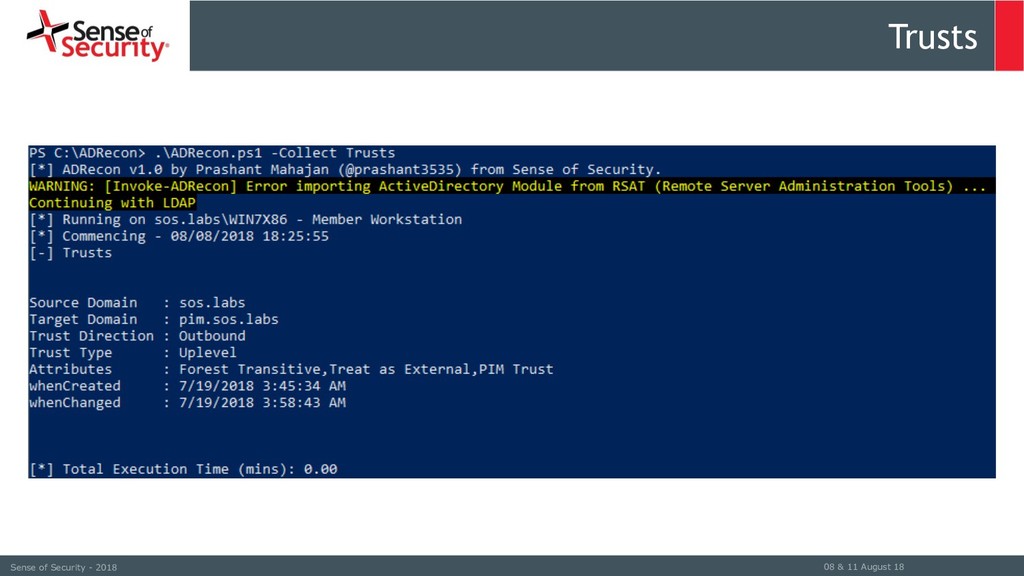
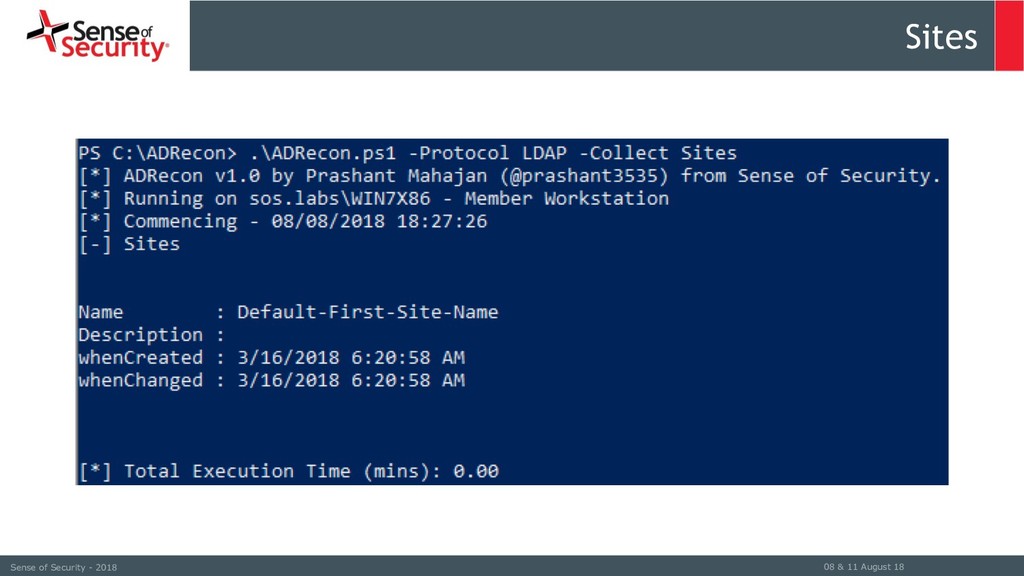
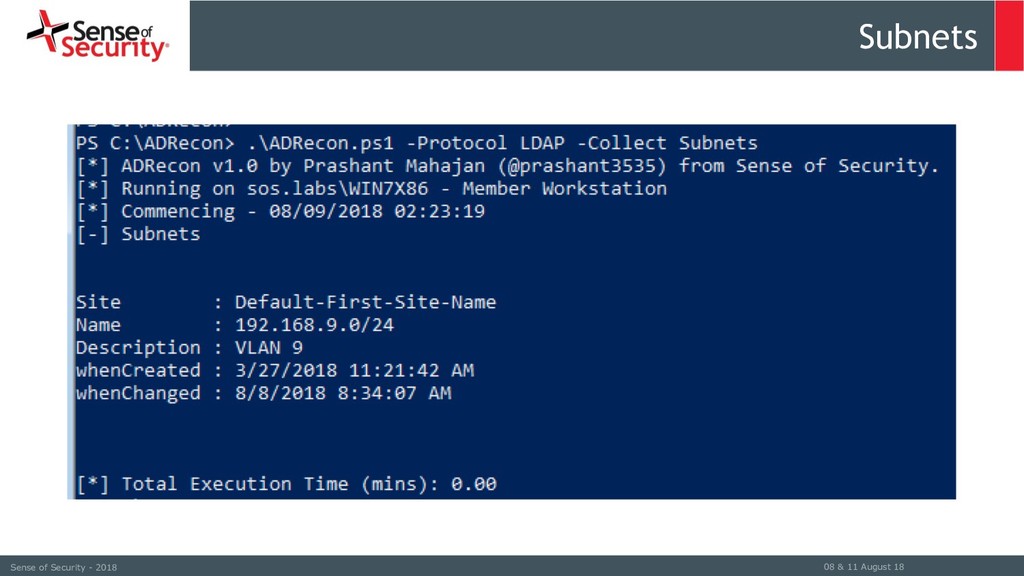
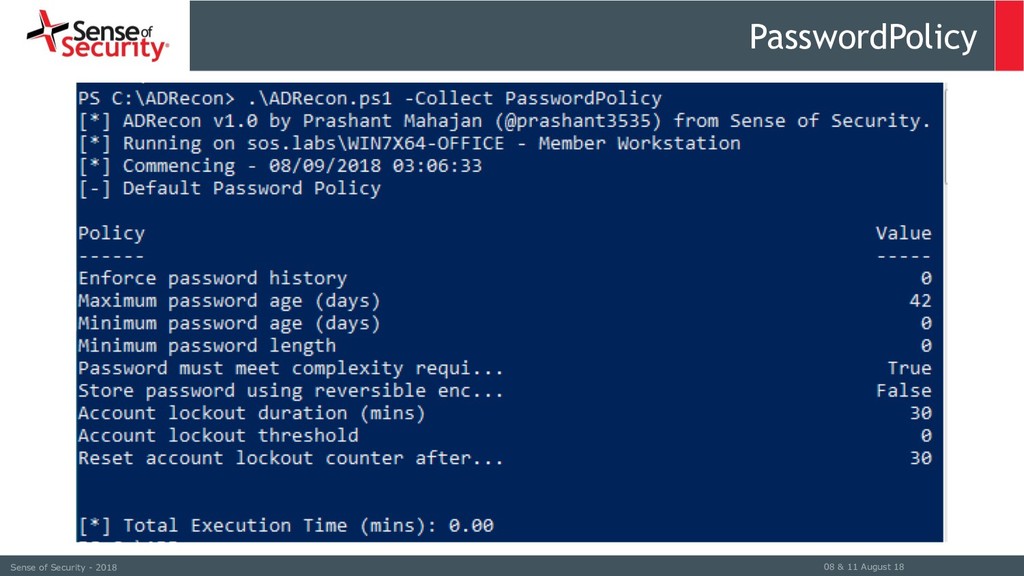
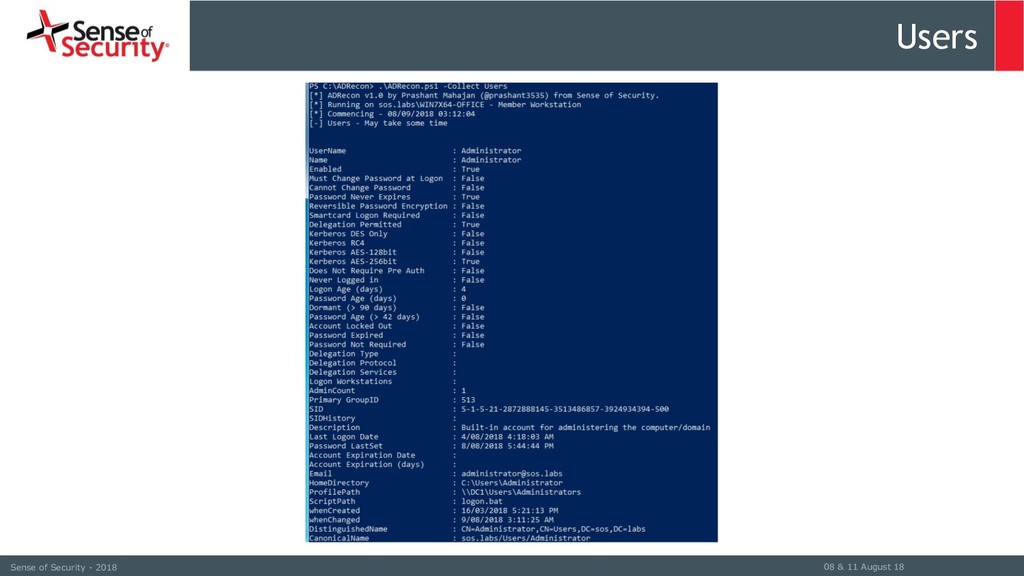
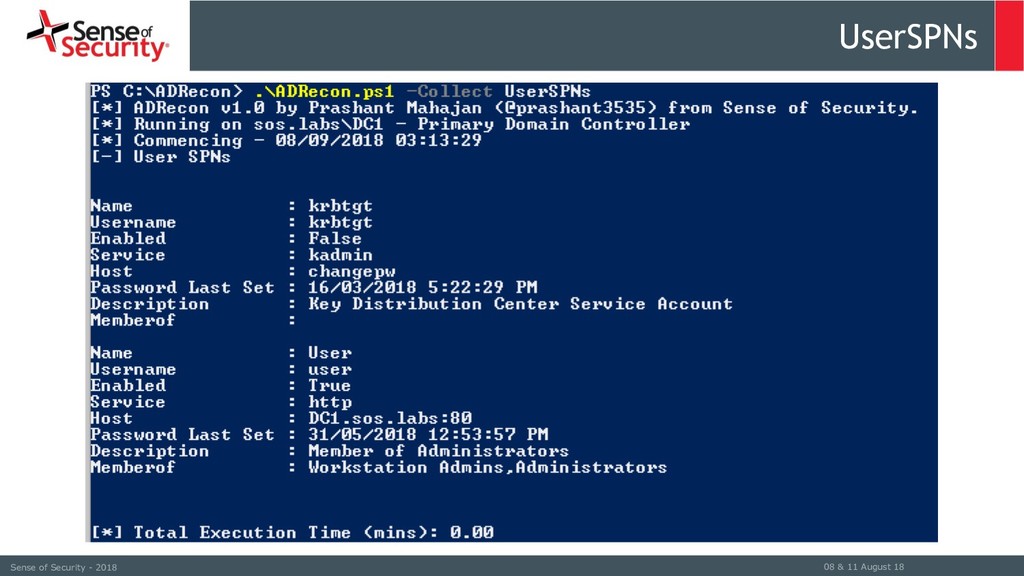
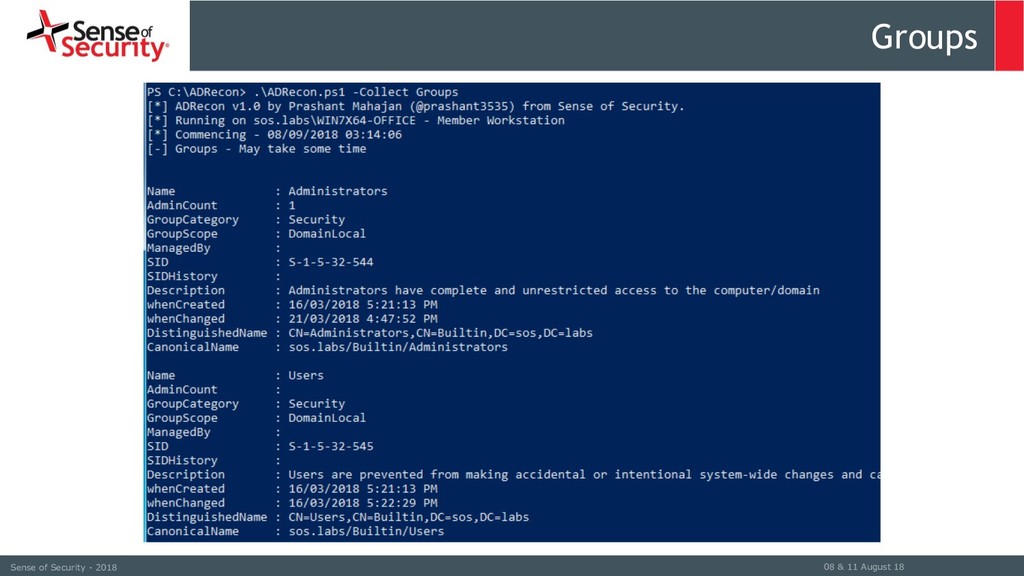
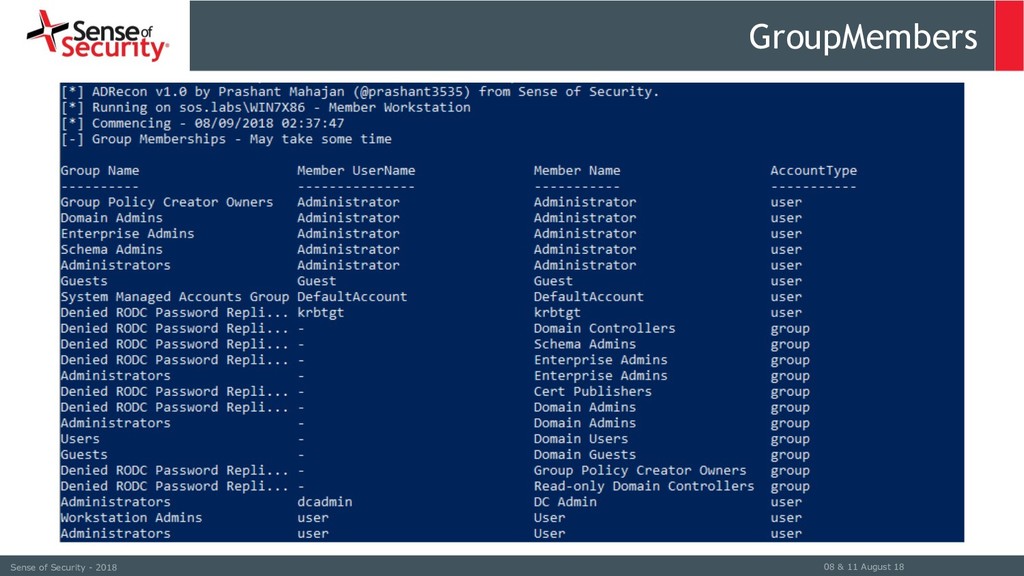
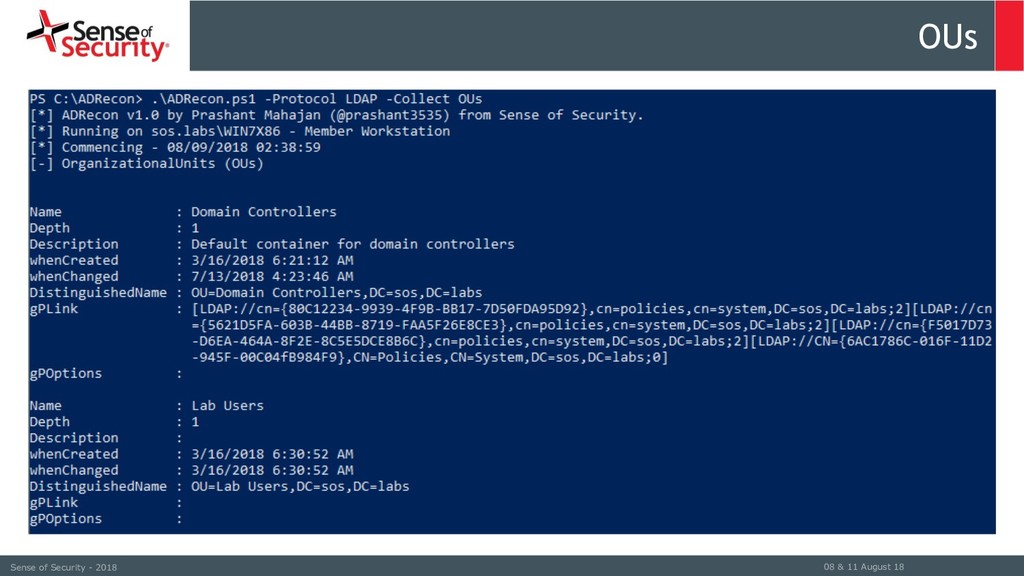
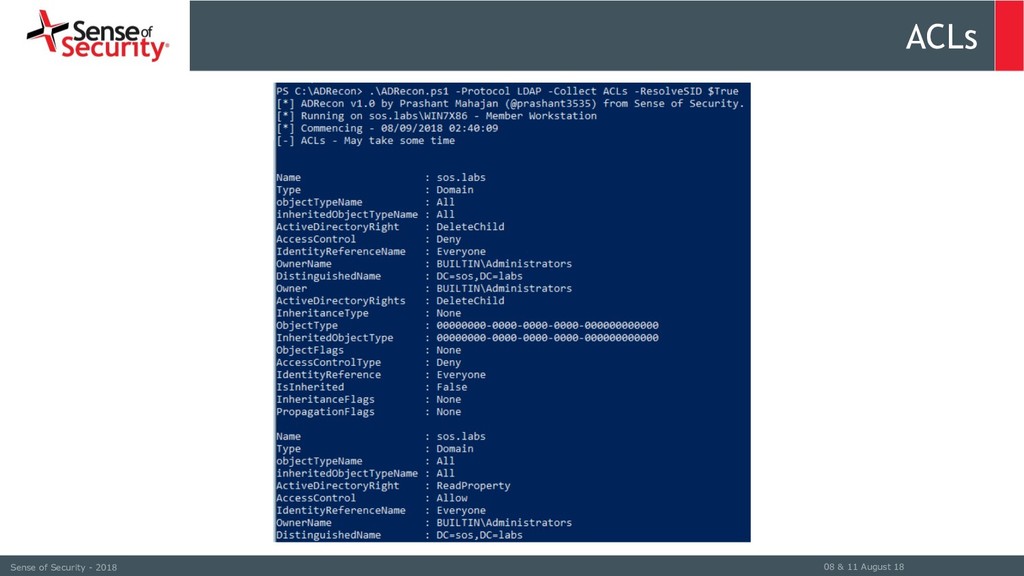
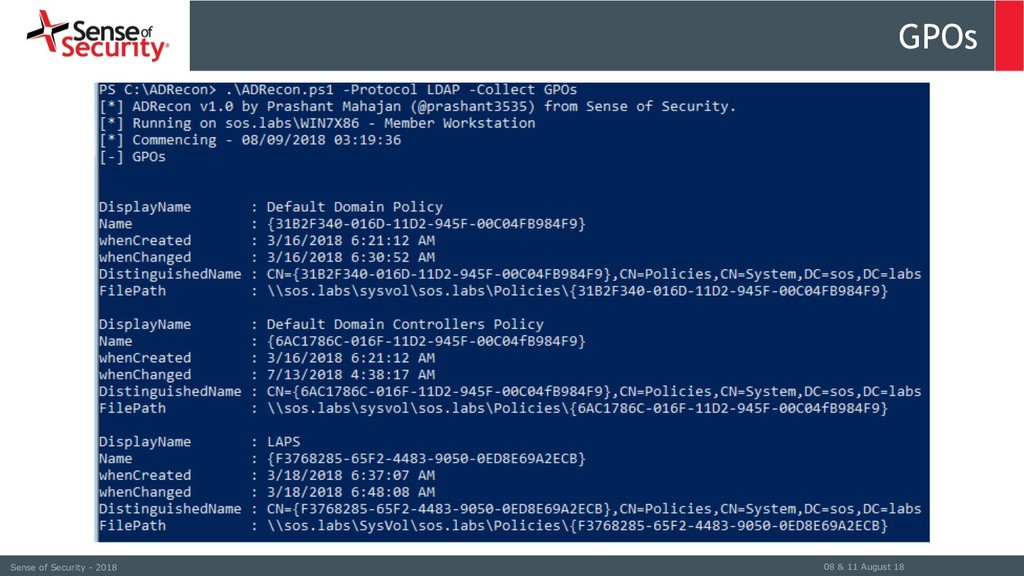
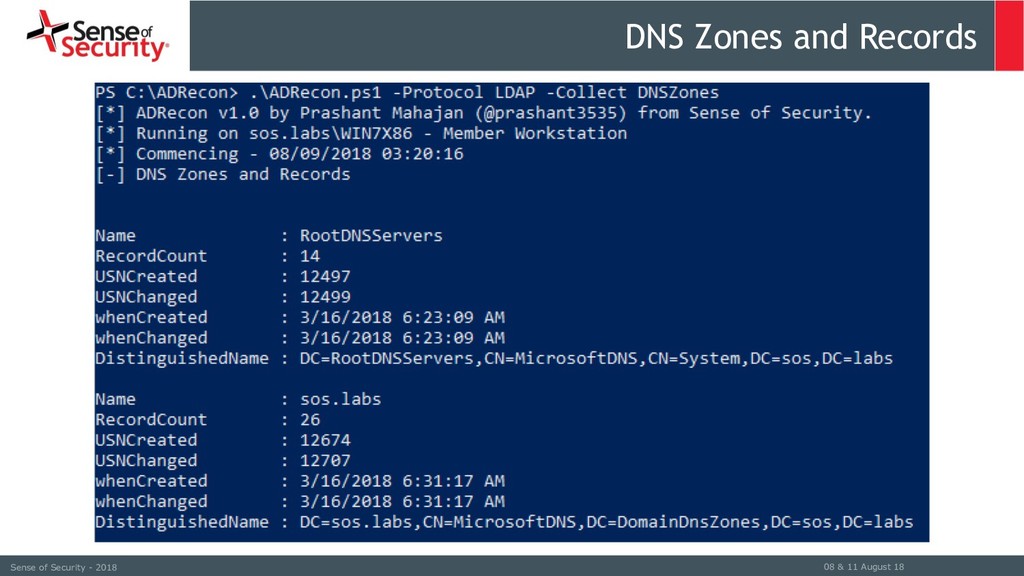
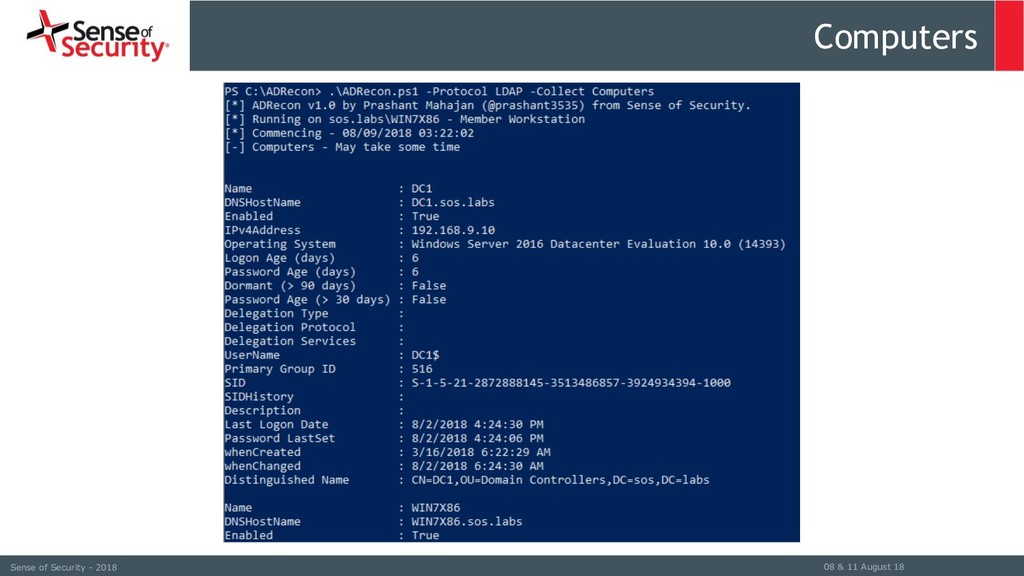
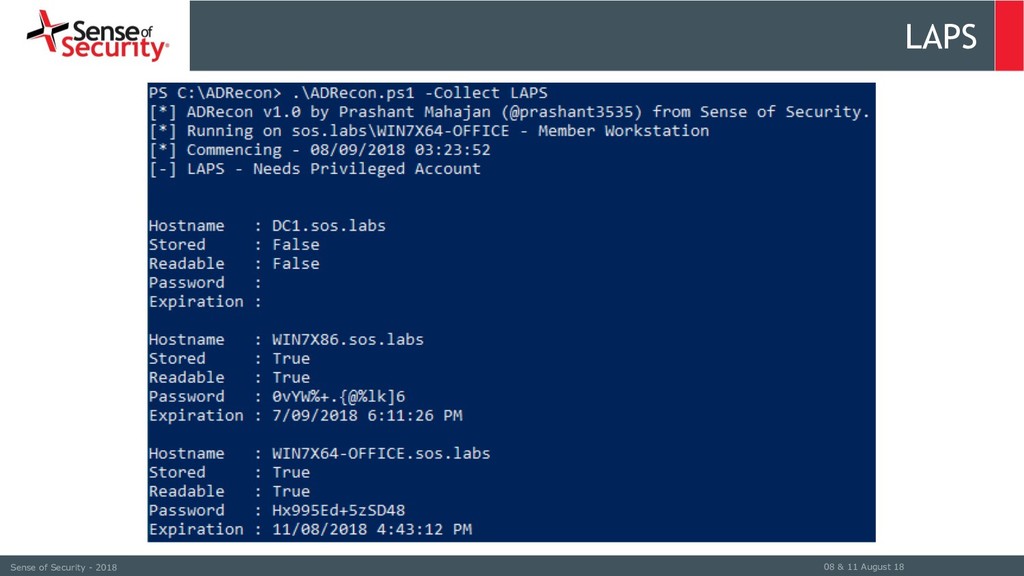
Modules • Forest, Domains, Sites, Subnets, Trusts • Default and Fine Grained* Password Policy • Domain Controllers, SMB versions, whether SMB Signing is supported and FSMO roles • Users and their attributes • Service Principal Names (SPNs) • Groups and their members • Organizational Units (OU) • ACLs for the Domain, OUs, Root Containers and GroupPolicy objects • Group Policy Object (GPO) details and GPOReport (requires RSAT) • DNS Zones and Records • Printers • Computers and their attributes • LAPS passwords* • BitLocker Recovery Keys* • Password Attributes (experimental) • Kerberoast * if implemented; require privileged user account -
08 & 11 August 18 Sense of Security - 2018
Parameters • -Protocol <String> • Which protocol to use; ADWS (default) or LDAP • -DomainController <String> • Domain Controller IP Address or Domain FQDN. • -Credential <PSCredential> • Domain Credentials. • -GenExcel <String> • Path for ADRecon output folder containing the CSV files to generate the ADRecon-Report.xlsx. Use it to generate the ADRecon-Report.xlsx when Microsoft Excel is not installed on the host used to run ADRecon. • -OutputDir <String> • Path for ADRecon output folder to save the CSV/XML/JSON/HTML files and the ADRecon-Report.xlsx. (The folder specified will be created if it doesn't exist) (Default pwd) • -Collect <String> • Which modules to run (Comma separated; e.g Forest,Domain. Default all) • Valid values include: Forest, Domain, Trusts, Sites, Subnets, PasswordPolicy, FineGrainedPasswordPolicy, DomainControllers, Users, UserSPNs, Groups, GroupMembers, OUs, ACLs, GPOs, GPOReport, DNSZones, Printers, Computers, ComputerSPNs, LAPS, BitLocker. • -OutputType <String> • Output Type; Comma seperated; e.g CSV,STDOUT,Excel (Default STDOUT with -Collect parameter, else CSV and Excel). • Valid values include: STDOUT, CSV, XML, JSON, HTML, Excel, All (excludes STDOUT). • -DormantTimeSpan <Int> • Timespan for Dormant accounts. (Default 90 days) • -PassMaxAge <Int> • Maximum machine account password age. (Default 30 days) • - ResolveSIDs <Bool> • Whether to resolve SIDs in the ACLs module. (Default False) • -PageSize <Int> • The PageSize to set for the LDAP searcher object. (Default 200) • -Threads <Int> • The number of threads to use during processing objects (Default 10) • -Log <Switch> • Create ADRecon Log using Start-Transcript -
08 & 11 August 18 Sense of Security - 2018
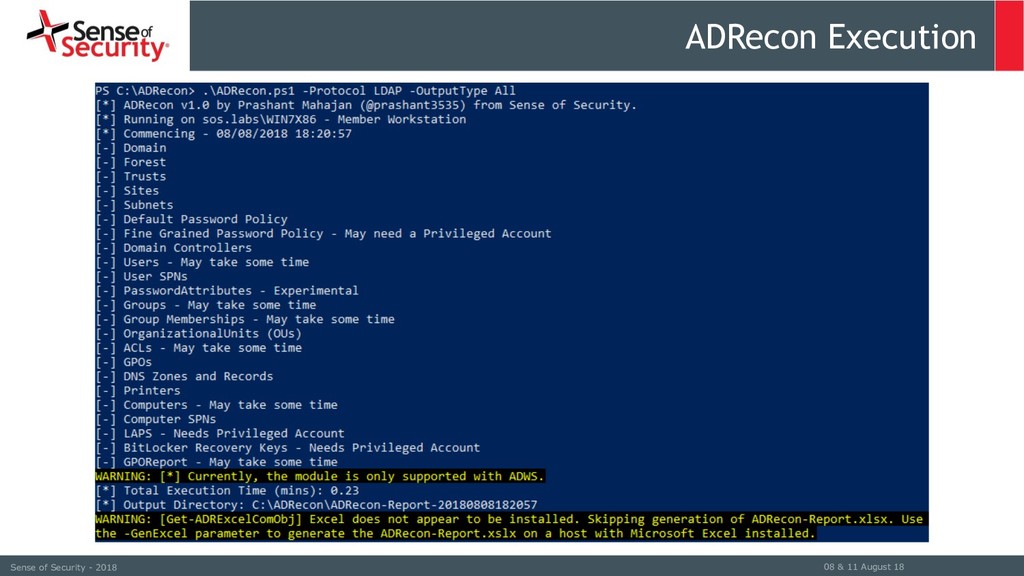
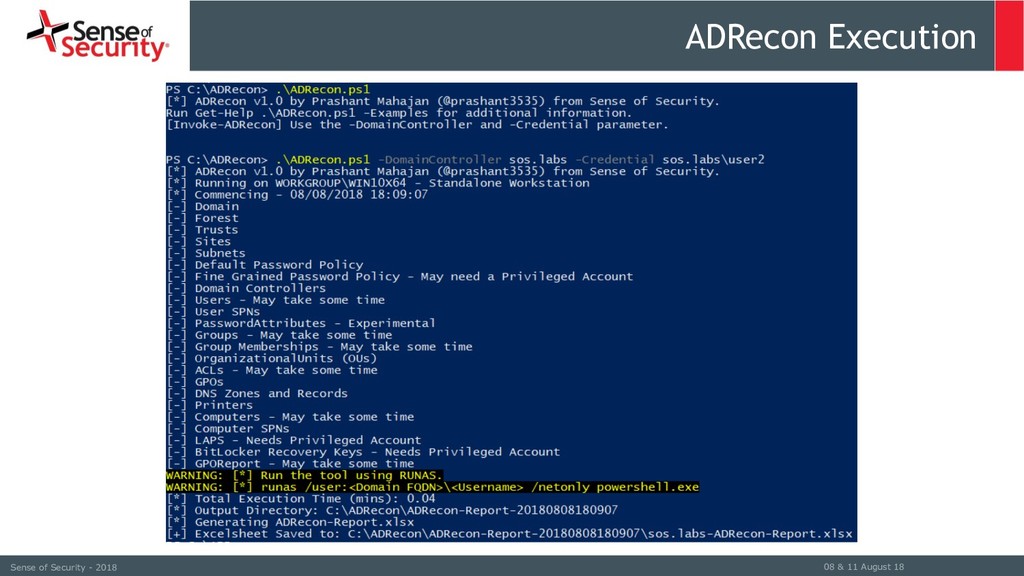
ADRecon Execution -
08 & 11 August 18 Sense of Security - 2018
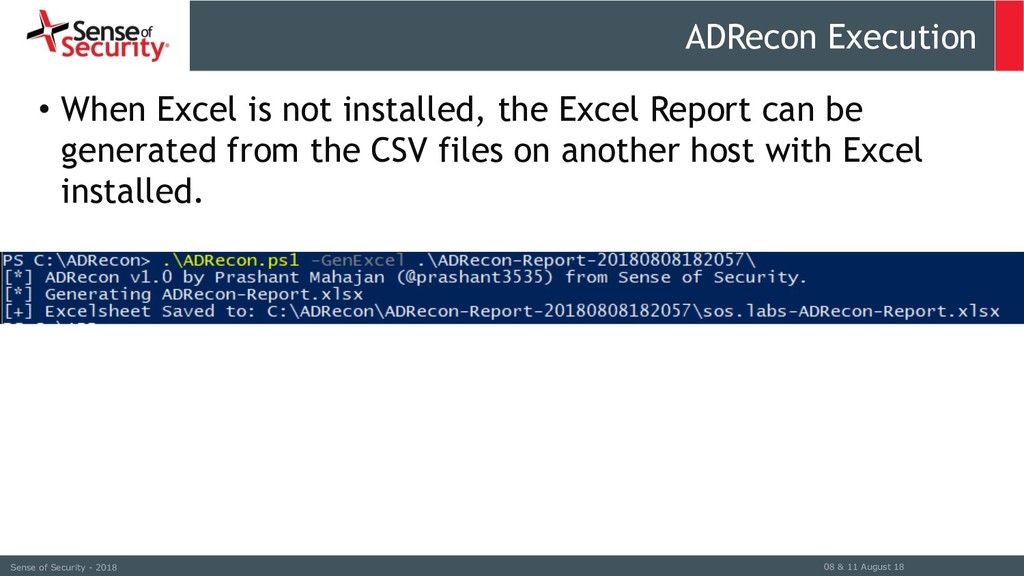
ADRecon Execution • When Excel is not installed, the Excel Report can be generated from the CSV files on another host with Excel installed. -
08 & 11 August 18 Sense of Security - 2018
ADRecon Execution -
08 & 11 August 18 Sense of Security - 2018
PasswordPolicy -
08 & 11 August 18 Sense of Security - 2018
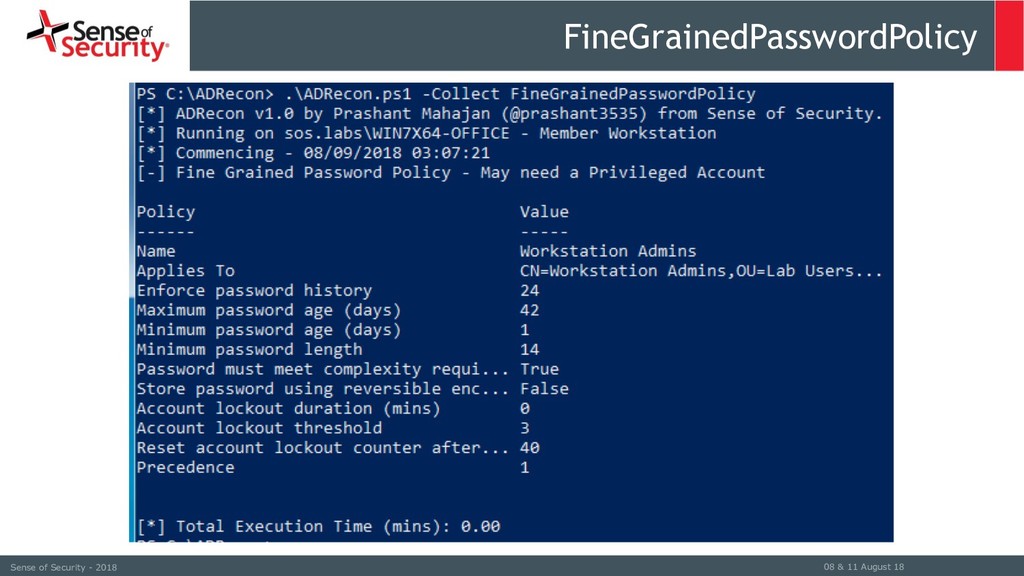
FineGrainedPasswordPolicy -
08 & 11 August 18 Sense of Security - 2018
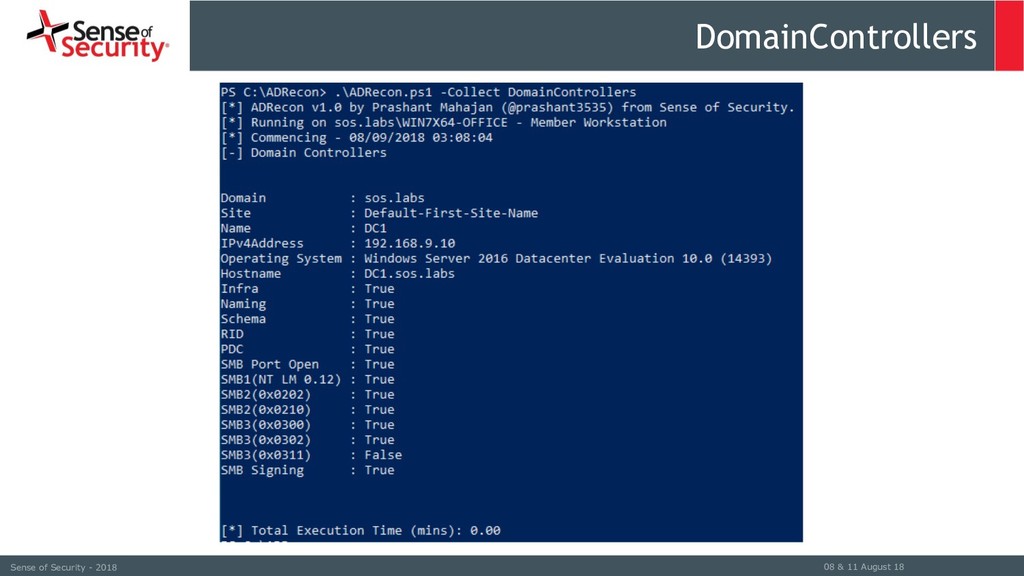
DomainControllers -
08 & 11 August 18 Sense of Security - 2018
GroupMembers -
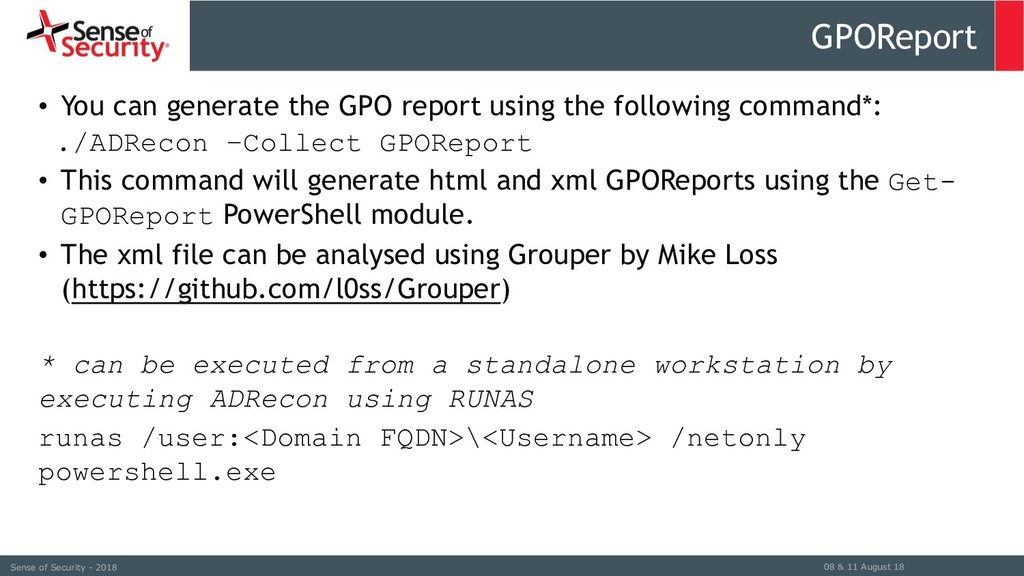
• You can generate the GPO report using the following
command*: ./ADRecon –Collect GPOReport • This command will generate html and xml GPOReports using the Get- GPOReport PowerShell module. • The xml file can be analysed using Grouper by Mike Loss (https://github.com/l0ss/Grouper) * can be executed from a standalone workstation by executing ADRecon using RUNAS runas /user:<Domain FQDN>\<Username> /netonly powershell.exe 08 & 11 August 18 Sense of Security - 2018 GPOReport -
08 & 11 August 18 Sense of Security - 2018
DNS Zones and Records -
08 & 11 August 18 Sense of Security - 2018
DNS Zones and Records -
08 & 11 August 18 Sense of Security - 2018
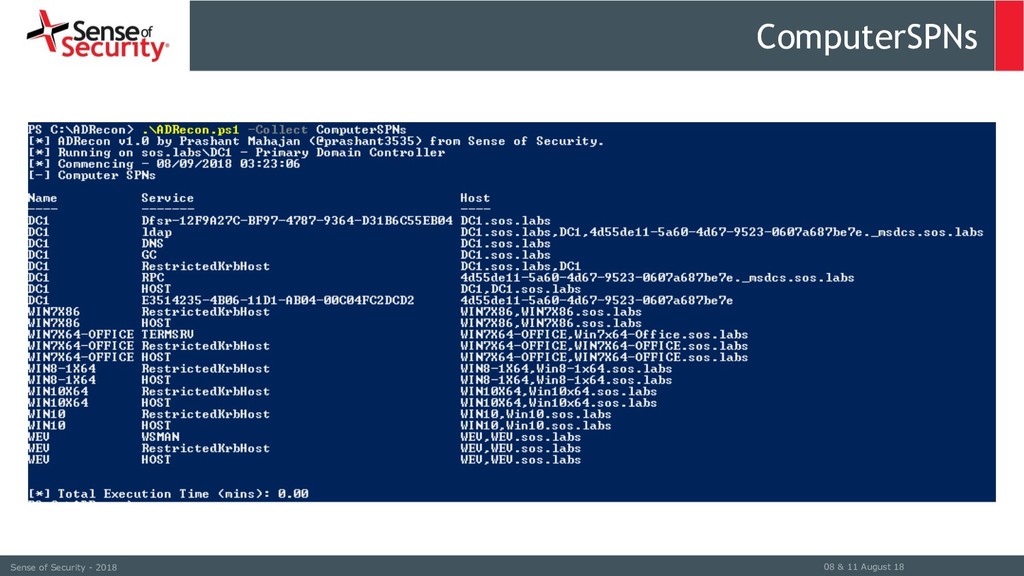
ComputerSPNs -
08 & 11 August 18 Sense of Security - 2018
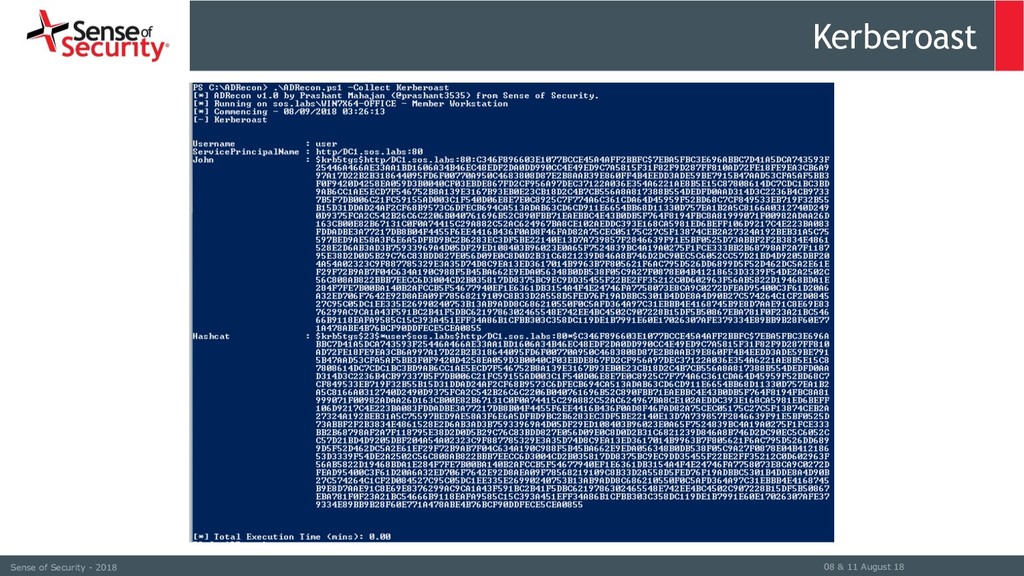
Kerberoast -
08 & 11 August 18 Sense of Security - 2018
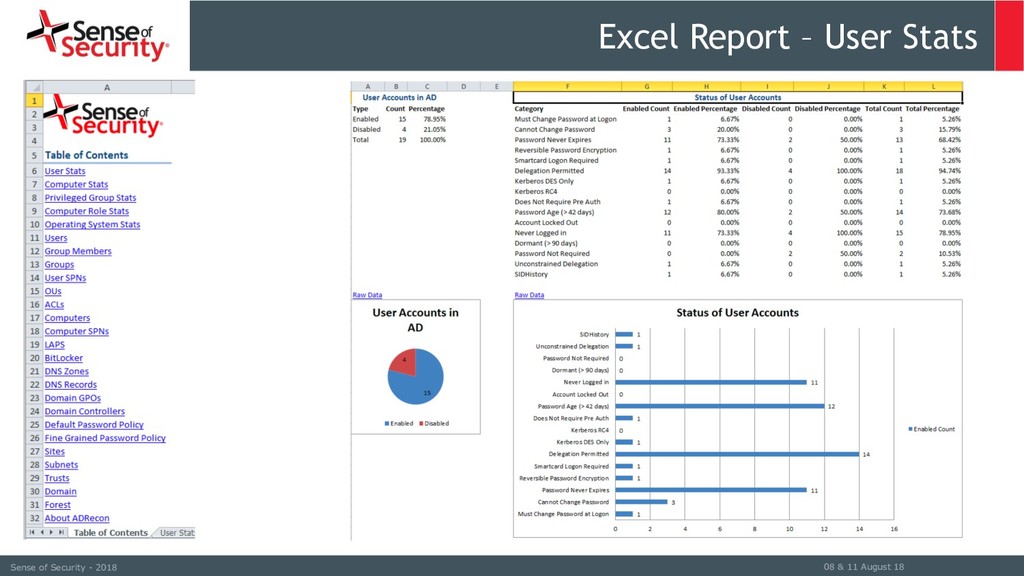
Excel Report – User Stats -
08 & 11 August 18 Sense of Security - 2018
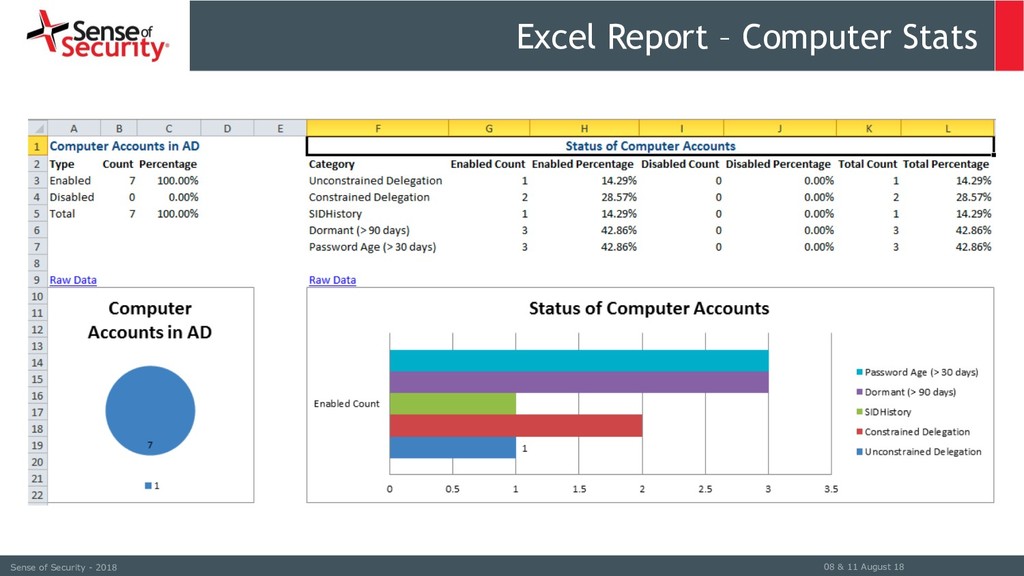
Excel Report – Computer Stats -
08 & 11 August 18 Sense of Security - 2018
Excel Report – Privileged Group Stats -
08 & 11 August 18 Sense of Security - 2018
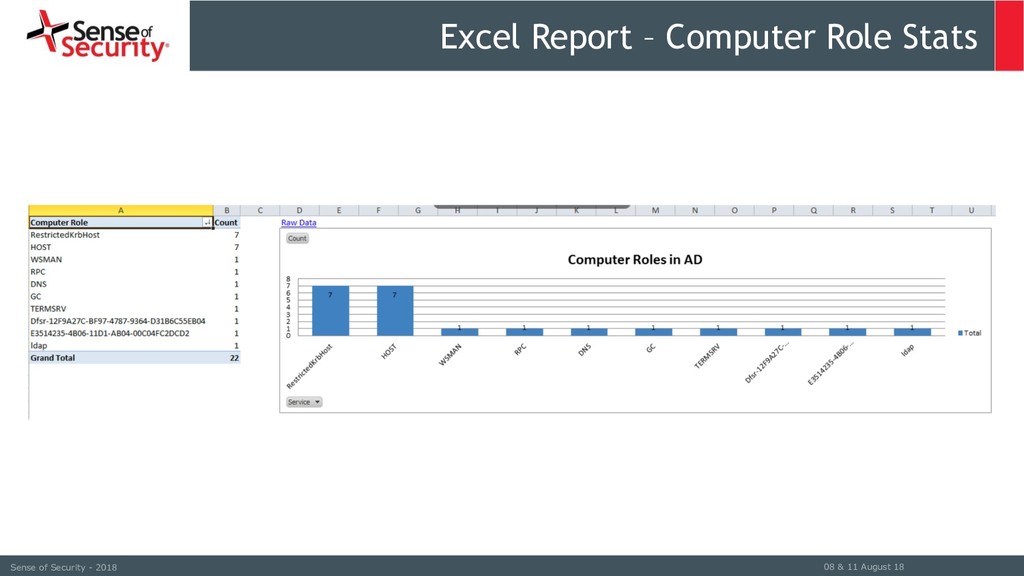
Excel Report – Computer Role Stats -
08 & 11 August 18 Sense of Security - 2018
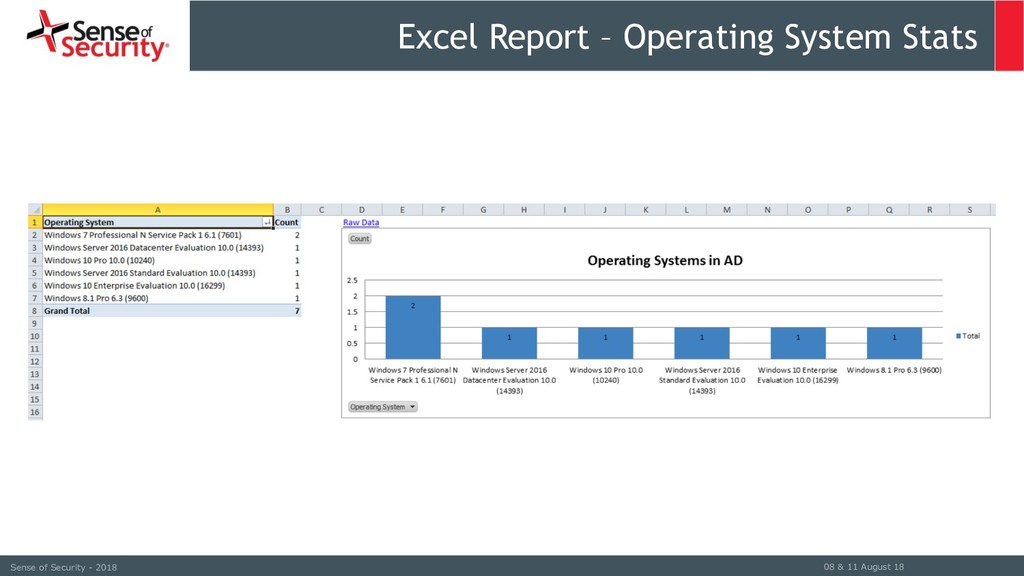
Excel Report – Operating System Stats -
• Replace System.DirectoryServices.DirectorySearch with System.DirectoryServices.Protocols and add support for LDAP
STARTTLS and LDAPS (TCP port 636). • Add option to filter default ACLs. • Gather ACLs for other objects such as Users, Group, etc. • Additional export and storage option: export to SQLite. • Use the EPPlus library for Excel Report generation and remove the dependency on MS Excel. • List issues identified and provide recommended remediation advice based on analysis of the data. • Add PowerShell Core support. 08 & 11 August 18 Sense of Security - 2018 Future Plans -
• Test the tool, suggest changes, improvements, enhancements, etc. •
Add / Promote / Write about the tool • Report / track / suggest / fix issues Pull requests are always welcome J Issue tracker (https://github.com/sense-of-security/ADRecon/issues) 08 & 11 August 18 Sense of Security - 2018 How to contribute ? -
08 & 11 August 18 Sense of Security - 2018
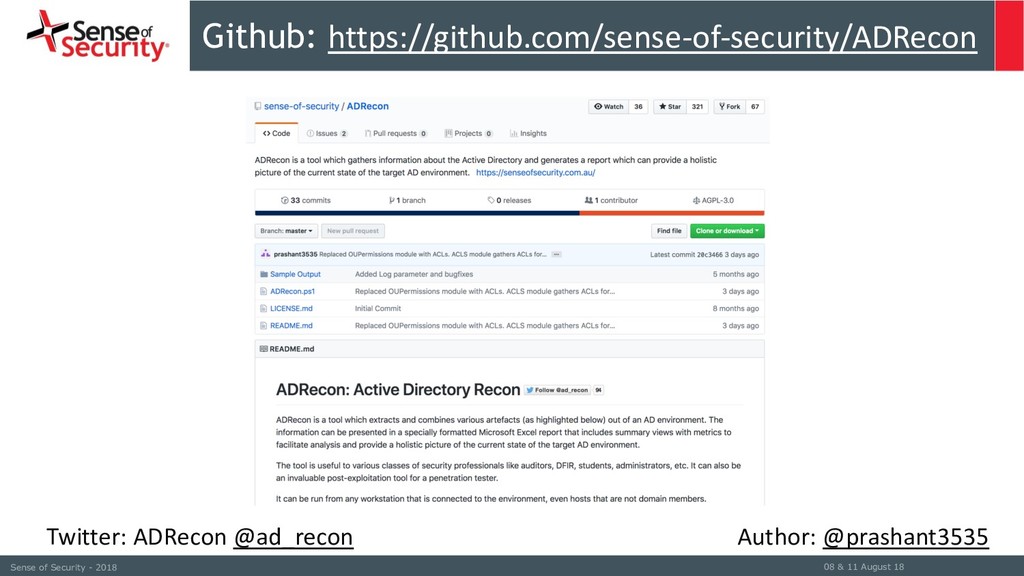
Github: https://github.com/sense-of-security/ADRecon Twitter: ADRecon @ad_recon Author: @prashant3535 -
Sydney Level 8, 59 Goulburn Street Sydney NSW 2000 Melbourne
Level 15, 401 Docklands Drive Docklands VIC 3008 Tel. 1300 922 923 Intl. +61 2 9290 4444 www.senseofsecurity.com.au Sense of Security Pty Ltd ABN 14 098 237 908 @ITSecurityAU Security, it’s all we do. Knowledge, Experience & Trust. Questions? Github: https://github.com/sense-of-security/ADRecon Twitter: ADRecon @ad_recon Author: @prashant3535 -
Sydney Level 8, 59 Goulburn Street Sydney NSW 2000 Melbourne
Level 15, 401 Docklands Drive Docklands VIC 3008 Tel. 1300 922 923 Intl. +61 2 9290 4444 www.senseofsecurity.com.au Sense of Security Pty Ltd ABN 14 098 237 908 @ITSecurityAU Security, it’s all we do. Knowledge, Experience & Trust. Thank You! © 2002 – 2018 Sense of Security Pty Limited. All rights reserved. Some images used under license from Shutterstock.com or with permission from respective trademark owners. No part of this publication may be reproduced, distributed, or transmitted in any form or by any means, including photocopying, recording, or other electronic or mechanical methods, without the prior written permission of the publisher. Github: https://github.com/sense-of-security/ADRecon Twitter: ADRecon @ad_recon Author: @prashant3535 -
• BitLocker module updated to include Recovery Key ID, Creation
Date, TPM Recovery Password, etc. • Renamed DCs module to DomainControllers and updated with enumeration of SMB versions and SMB signing support. • Added support for output formats: XML, JSON, HTML. (Use -OutputType parameter). • Added FineGrainedPasswordPolicy module as a separate module after being separated from PasswordPolicy module. • User module updated to include Delegation enumeration (Unconstrained/Constrained with the list of servers and protocol), supported kerberos encryption algorithms (DES, RC4, AES) and include other attributes such as Account Expiration, Delegation Permitted, homeDirectory, Email, ScriptPath and SmartcardLogonRequired. • Computer module updated in include Delegation enumeration (Unconstrained/Constrained with the list of servers and protocol). • Computer module (LDAP) updated to perform DNS lookup to populate IPv4Address column. • DomainControllers module (ADWS) updated concatenate OperatingSystemHotfix, OperatingSystemServicePack and OperatingSystemVersion attributes in Operating Version column. • Computer module updated to include OperatingSystemHotfix, OperatingSystemServicePack and OperatingSystemVersion attributes concatenated in Operating Version column. • Added Sites, Subnets , Trusts and PasswordAttributes modules. • Added Computer Stats sheet in the Excel report. • Updated User Statistics sheet in the Excel report to cover the added attributes. • Use Pivot Tables for calculation of count in the stats sheets in the Excel Report. • Use excel formulae for count calculation in the user and computer stats sheets in the Excel Report. • Updated UserSPNs module to include Enabled and Memberof attribute. • Renamed OUPermissions module to ACLs and updated to enumerate ACLs for Domain, OUs, Root Containers and GroupPolicy objects. 08 & 11 August 18 Sense of Security - 2018 Changelog since BlackHat Asia 2018 -
References • What Are Active Directory Functional Levels? (https://technet.microsoft.com/en-us/library/cc787290(v=ws.10).aspx) •
The KRBTGT Account – What is it ? (https://blogs.technet.microsoft.com/janelewis/2006/12/19/the-krbtgt-account-what-is-it/) • Active Directory Service Principal Names (SPNs) Descriptions (https://adsecurity.org/?page_id=183) • Privileged Accounts and Groups in Active Directory (https://github.com/MicrosoftDocs/windowsserverdocs/blob/master/WindowsServerDocs/identity/ad-ds/plan/security-best- practices/Appendix-B--Privileged-Accounts-and-Groups-in-Active-Directory.md) • How to use the UserAccountControl flags to manipulate user account properties (https://support.microsoft.com/en- au/kb/305144) • All Active Directory Attributes (https://msdn.microsoft.com/en-us/library/ms675090(v=vs.85).aspx) • Infrastructure FSMO Role (https://msdn.microsoft.com/en-us/library/cc223753.aspx) • Active Directory: Password Policies (https://social.technet.microsoft.com/wiki/contents/articles/24159.active-directory- password-policies.aspx) • Active Directory-Integrated DNS Zone (https://docs.microsoft.com/en-us/windows-server/identity/ad-ds/plan/active-directory- integrated-dns-zones) • PowerView (https://github.com/PowerShellEmpire/PowerTools/tree/master/PowerView) • BloodHound (https://github.com/BloodHoundAD/BloodHound) • Grouper (https://github.com/l0ss/Grouper) • Get-LAPSPasswords (https://github.com/kfosaaen/Get-LAPSPasswords/blob/master/Get-LAPSPasswords.ps1) • PowerShell Code: ADSI Convert Domain Distinguished Name to Fully Qualified Domain Name (https://adsecurity.org/?p=440) • Active Directory OU Permissions Report (https://gallery.technet.microsoft.com/Active-Directory-OU-1d09f989) • Active Directory password attribute selection (https://www.ibm.com/support/knowledgecenter/en/ssw_aix_71/com.ibm.aix.security/ad_password_attribute_selection.htm) • unicodePwd (https://msdn.microsoft.com/en-us/library/cc223248.aspx) • userPassword (https://msdn.microsoft.com/en-us/library/cc223249.aspx) -
• Building an Effective Active Directory Lab Environment for Testing
(https://adsecurity.org/?p=2653) • Setting up an Active Directory Lab (https://www.psattack.com/articles/20160718/setting-up-an-active- directory-lab-part-1/) • Detection Lab (https://github.com/clong/DetectionLab) • AutomatedLab (https://github.com/AutomatedLab/AutomatedLab) • Invoke-ADLabDeployer (https://github.com/outflanknl/Invoke- ADLabDeployer) • Creating Real Looking User Accounts in AD Lab (https://www.darkoperator.com/blog/2016/7/30/creating-real-looking- user-accounts-in-ad-lab) • Create Lab User Accounts 2.0 (https://gallery.technet.microsoft.com/Create-Lab-User-Accounts- 844f7ba1) 08 & 11 August 18 Sense of Security - 2018 Building your own AD Lab