Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
GitHub ActionsとAWSをOIDC認証で連携する
Search
Kazuhiro Seo
April 26, 2025
Technology
250
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
GitHub ActionsとAWSをOIDC認証で連携する
GitHub ActionsとAWSをOIDC認証で連携する
Kazuhiro Seo
April 26, 2025
More Decks by Kazuhiro Seo
See All by Kazuhiro Seo
PostgreSQL 18で考えるUUID主キー
kazuhiro1982
0
570
Gradleとちょっと仲良くなろう
kazuhiro1982
0
130
JavaとWebAssembly
kazuhiro1982
0
170
SpringBoot 3.0 のNative Imageを試してみた
kazuhiro1982
0
470
セッションデータの管理にSpring Sessionを利用する
kazuhiro1982
0
3.8k
AWSのLake Formation Governed Tablesを触ってみた
kazuhiro1982
0
470
VS CodeとRemote Containerで開発環境もコード管理しよう
kazuhiro1982
1
780
SpringBootをコンテナで動かしてみる
kazuhiro1982
0
440
Serverless FrameworkでWebサイトの更新を検知して通知する
kazuhiro1982
0
550
Other Decks in Technology
See All in Technology
フィンテック養成勉強会#68
finengine
0
200
M5Stackで作る BLEマウス GPSログの世界
tomokusaba
PRO
0
460
[EMNLP26] RIGEL: Self-Distilled Score Adaptation for Image and Video Captioning Evaluation
keio_smilab
PRO
0
110
トークン化預金DCJPYの取り組みと活用ユースケース
finengine
0
220
Persisting Massive Data with Rails ~Designing for 60 billion rows, and fighting the bottlenecks~ Railsで挑む大量データ永続化 〜600億件を永続化するための設計とボトルネックとの戦い〜
occhi
0
780
Refining Active Record
shugo
0
190
JAWS-UGグッズ職人仕事の流儀
kentapapa
0
130
その Valkey 使いこなしていますか?
onk
PRO
5
1.8k
Conditional PED-ANOVA: Hyperparameter Importance in Hierarchical & Dynamic Search Spaces
pfn
PRO
0
150
【データ横丁主催】AI エージェント時代のTranslytical Data Platform
shisyu_gaku
0
210
~最速でビジネスインパクトを創出する~ Sansanのデータ基盤と活用事例
sansantech
PRO
0
110
小規模OSSモデルは サイバーセキュリティ業務に どこまで使えるか
bbrbbq
0
170
Featured
See All Featured
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
610
Documentation Writing (for coders)
carmenintech
77
5.6k
A Guide to Academic Writing Using Generative AI - A Workshop
ks91
PRO
1
530
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
350
Leveraging Curiosity to Care for An Aging Population
cassininazir
1
540
SEO in 2025: How to Prepare for the Future of Search
ipullrank
3
3.9k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.2k
The Anti-SEO Checklist Checklist. Pubcon Cyber Week
ryanjones
0
270
[RailsConf 2023] Rails as a piece of cake
palkan
59
7.1k
The agentic SEO stack - context over prompts
schlessera
0
970
Making Projects Easy
brettharned
120
6.8k
Transcript
GitHub Actions とAWS をOIDC 認証で連携する
自己紹介 妹尾一弘 株式会社カオナビ (2025.03~) サーバーサイドエンジニア Go 書いてます 副業 英単語学習アプリ: モチタン
インフラ支援 JavaDo Java 勉強会コミュニティ 運営スタッフ
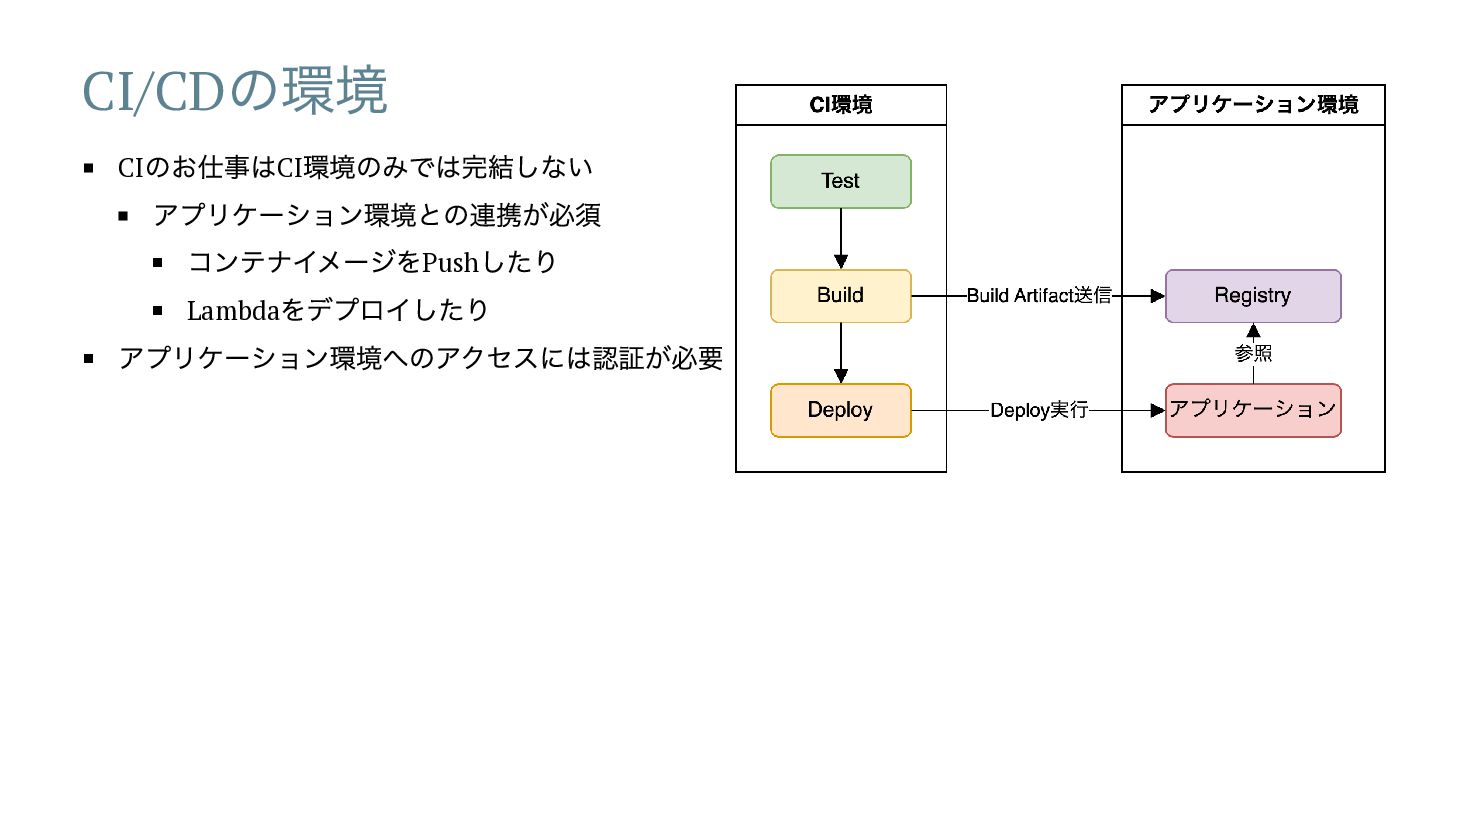
CI/CD の環境 CI のお仕事はCI 環境のみでは完結しない アプリケーション環境との連携が必須 コンテナイメージをPush したり Lambda をデプロイしたり
アプリケーション環境へのアクセスには認証が必要
CI/CD の認証の課題 人の認証はRole 利用が普及したが、CI 環境 ではまだ静的なシークレットの利用が多い IAM ユーザーのアクセスキーによる管理 漏洩リスクが心配 定期的な更新が必要
管理コストが高い
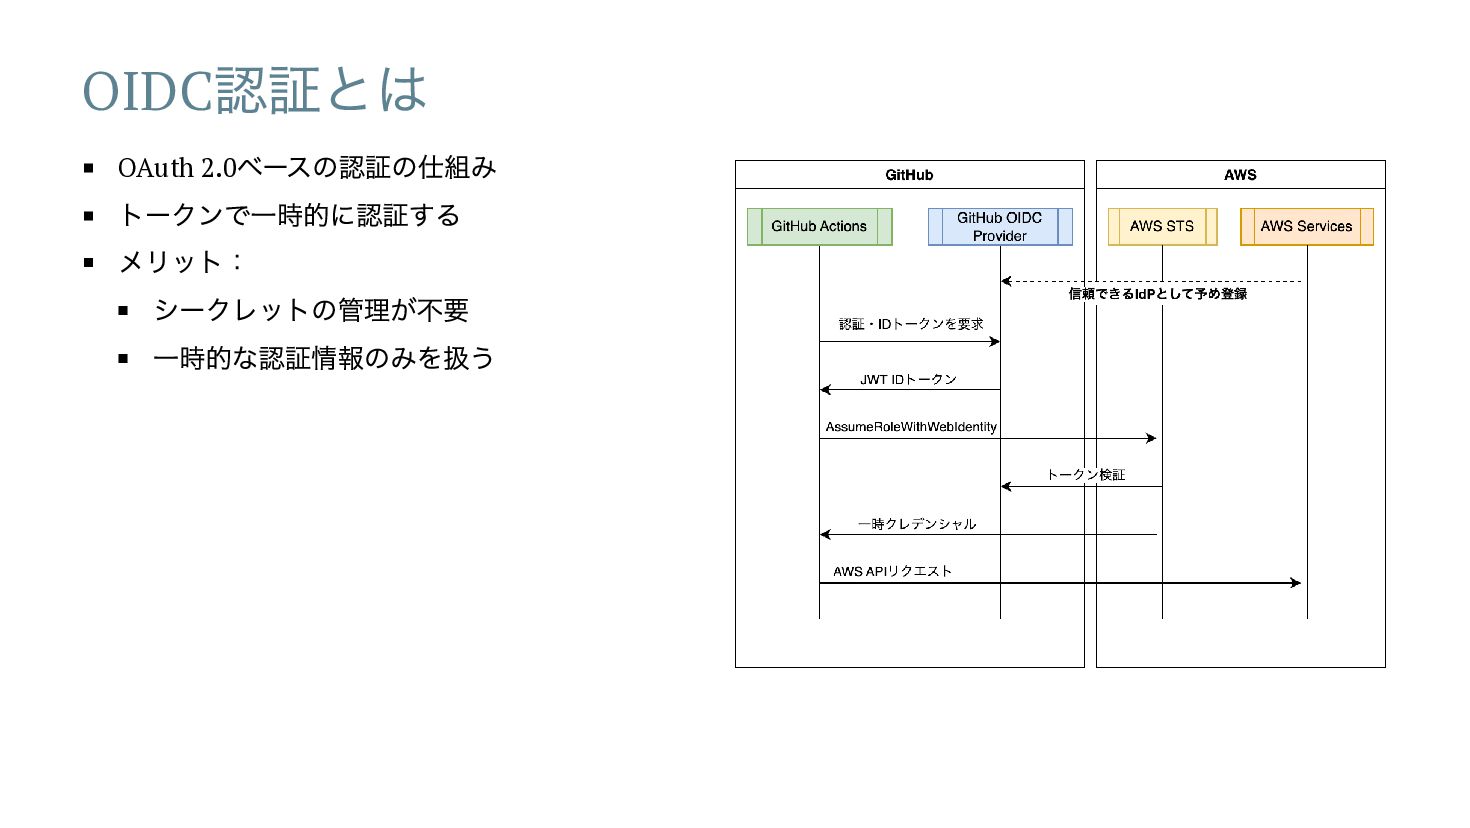
OIDC 認証とは OAuth 2.0 ベースの認証の仕組み トークンで一時的に認証する メリット: シークレットの管理が不要 一時的な認証情報のみを扱う
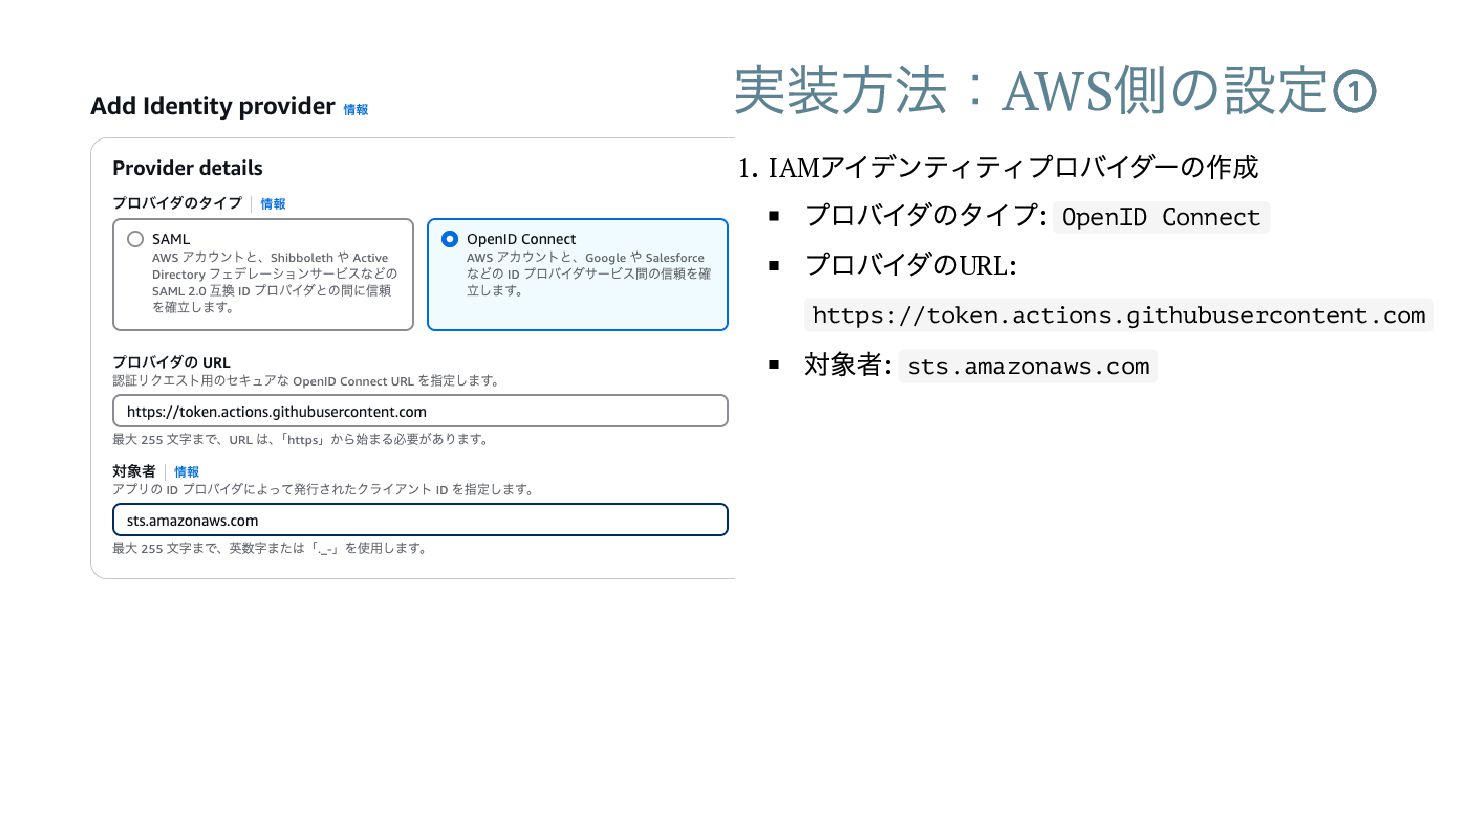
実装方法:AWS 側の設定① 1. IAM アイデンティティプロバイダーの作成 プロバイダのタイプ: OpenID Connect プロバイダのURL: https://token.actions.githubusercontent.com
対象者: sts.amazonaws.com
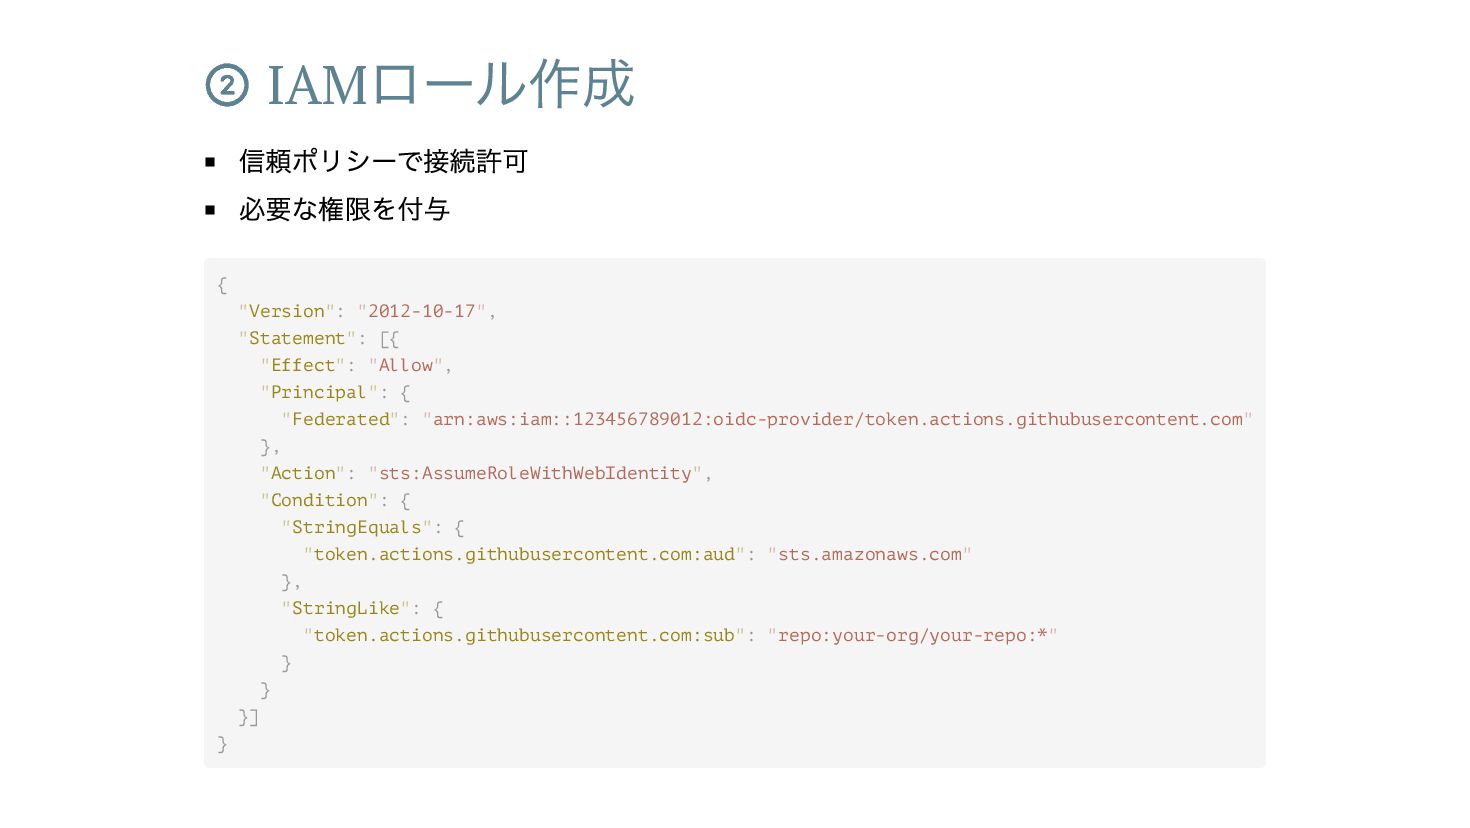
② IAM ロール作成 信頼ポリシーで接続許可 必要な権限を付与 { "Version": "2012-10-17", "Statement": [{
"Effect": "Allow", "Principal": { "Federated": "arn:aws:iam::123456789012:oidc-provider/token.actions.githubusercontent.com" }, "Action": "sts:AssumeRoleWithWebIdentity", "Condition": { "StringEquals": { "token.actions.githubusercontent.com:aud": "sts.amazonaws.com" }, "StringLike": { "token.actions.githubusercontent.com:sub": "repo:your-org/your-repo:*" } } }] }
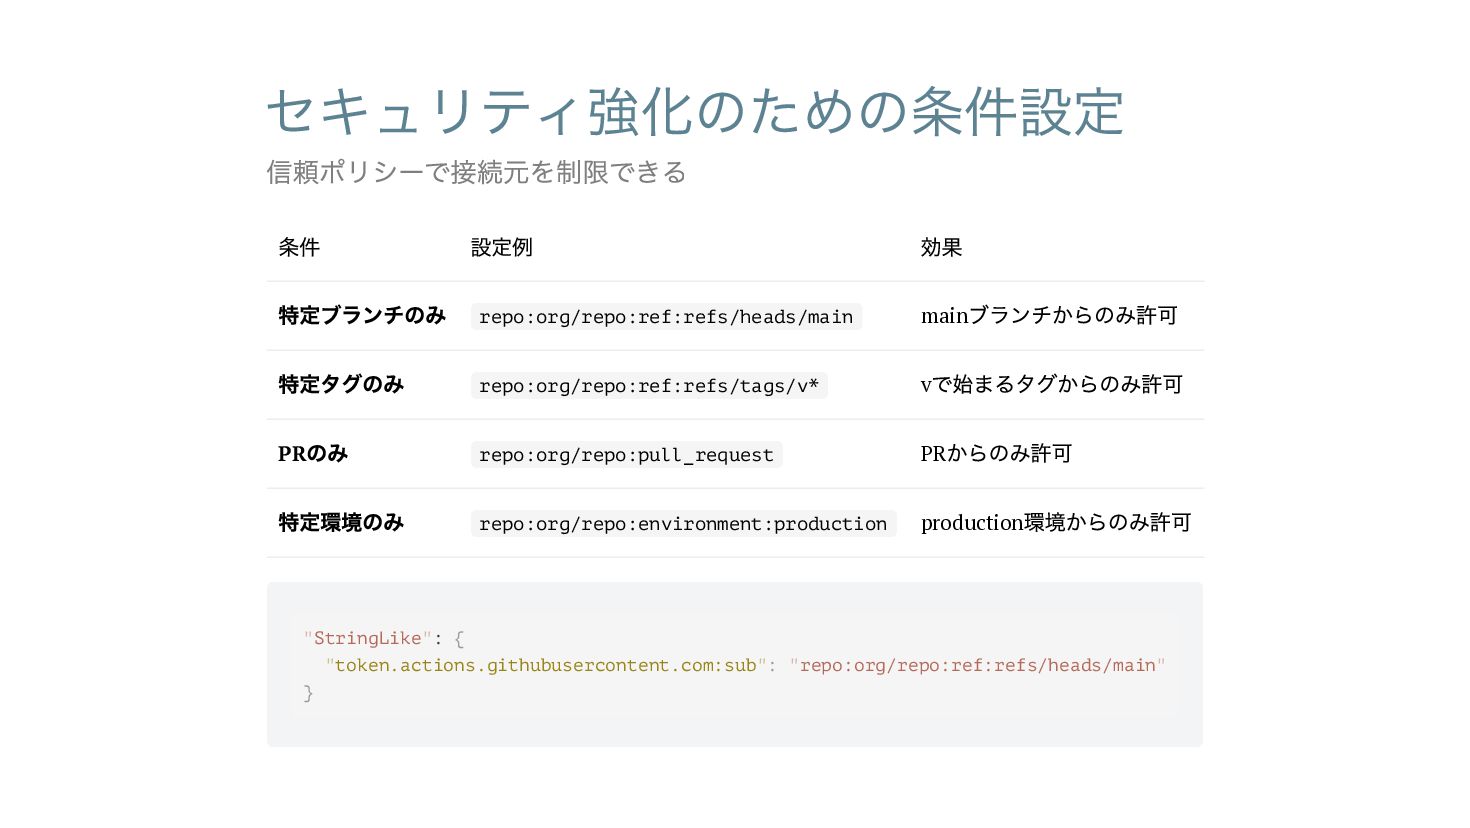
セキュリティ強化のための条件設定 条件 設定例 効果 特定ブランチのみ repo:org/repo:ref:refs/heads/main main ブランチからのみ許可 特定タグのみ repo:org/repo:ref:refs/tags/v*
v で始まるタグからのみ許可 PR のみ repo:org/repo:pull_request PR からのみ許可 特定環境のみ repo:org/repo:environment:production production 環境からのみ許可 信頼ポリシーで接続元を制限できる "StringLike": { "token.actions.githubusercontent.com:sub": "repo:org/repo:ref:refs/heads/main" }
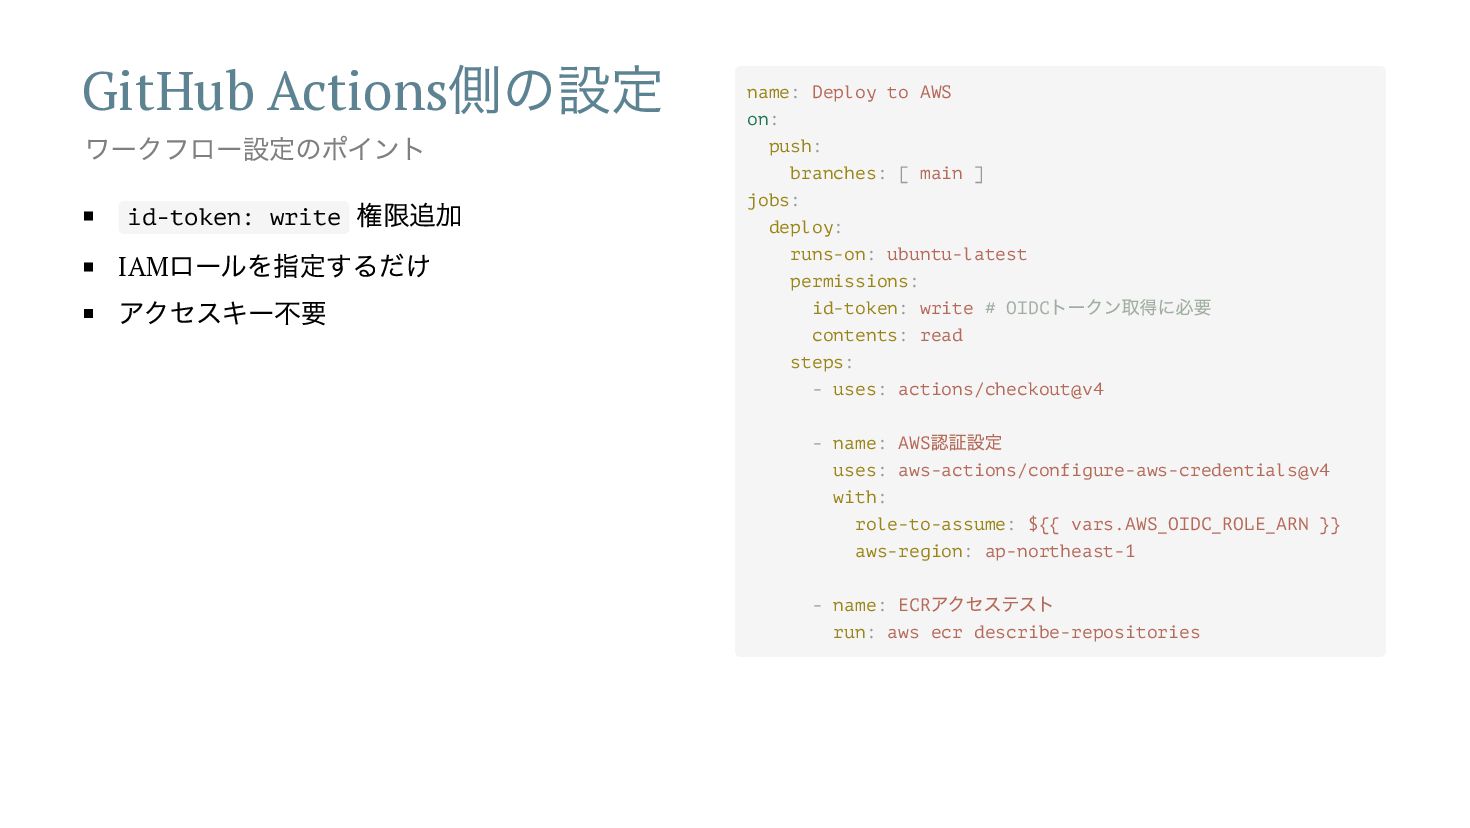
GitHub Actions 側の設定 id-token: write 権限追加 IAM ロールを指定するだけ アクセスキー不要 ワークフロー設定のポイント
name: Deploy to AWS on: push: branches: [ main ] jobs: deploy: runs-on: ubuntu-latest permissions: id-token: write # OIDC トークン取得に必要 contents: read steps: - uses: actions/checkout@v4 - name: AWS 認証設定 uses: aws-actions/configure-aws-credentials@v4 with: role-to-assume: ${{ vars.AWS_OIDC_ROLE_ARN }} aws-region: ap-northeast-1 - name: ECR アクセステスト run: aws ecr describe-repositories
まとめ 静的な認証情報が不要になる シンプルな設定で実装可能 柔軟なアクセス制御ができる OIDC 認証を使うことで
ありがとうございました


 kazuhiro1982
 finengine
 tomokusaba
 keio_smilab
 occhi
 shugo
 kentapapa
 onk
 pfn
 shisyu_gaku
 sansantech
 bbrbbq
 pedronauck
 marktimemedia
 carmenintech
 ks91
 baasie
 cassininazir
 ipullrank
 aleyda
 ryanjones
 palkan
 schlessera
 brettharned