Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
BPFの現在
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
kwi
January 13, 2017
Technology
1.1k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
BPFの現在
Linux eBPFをネットワーク機能まわりで使う使い方について。
kwi
January 13, 2017
More Decks by kwi
See All by kwi
SmartCitizen紹介
kwi
0
380
こんなのどうかな?
kwi
1
440
加古川パスタ♡の件
kwi
0
200
給食データを味わう
kwi
0
140
rocket-up
kwi
0
78
測ってみようよ
kwi
1
490
神戸市ウェブサイト動態
kwi
0
360
Code for 選挙
kwi
0
310
Code for Japan Summit 2017 紹介
kwi
0
170
Other Decks in Technology
See All in Technology
[FECONF-2026] 신대륙을 향한 카카오페이증권 프론트엔드 항해기 (이주승)
l1ghthouse
0
350
AIエージェント統制はAPIから——押さえるべき5つの要素
nagix
0
110
re:Inventで、人生は変わったのか? / growth-builders-hub-1-reinvent-2026
mhrtech
2
190
書き手が人でもAIでも正しくなる道、 SREを埋め込んだDeveloper Platform / tech drivers day8
chmikata
4
890
Flutter Widget Previewerで始めるUIプレビューとVRTの自動化
sakusaku3939
0
190
AIで選択肢が広がった組織設計の理想と現実
konifar
16
7.5k
増え続けるプロダクトの品質をどう担保するか。ProductSpecとTypeScriptによる取り組み
joere
3
320
なぜAI時代に技術記事を書くのか?どう書くのか? 〜bunの場合〜
kworkdev
PRO
0
3.4k
SLOを阻む不安
sraku2159
0
200
Building Audio Plugin Ecosystem for Android in 2026
atsushieno
1
110
構造で守らせる データ・法務・セキュリティ・開発チームとつくる AI時代のデータガバナンスとデータ基盤のリアル
legalontechnologies
PRO
3
710
なぜ東京にいる私が、新潟の技術コミュニティを運営するのか by 八雲慎之助
yakumo
0
210
Featured
See All Featured
Easily Structure & Communicate Ideas using Wireframe
afnizarnur
194
17k
The Myth of the Modular Monolith - Day 2 Keynote - Rails World 2024
eileencodes
28
3.7k
Build The Right Thing And Hit Your Dates
maggiecrowley
39
3.5k
Practical Tips for Bootstrapping Information Extraction Pipelines
honnibal
25
2.1k
How To Stay Up To Date on Web Technology
chriscoyier
790
250k
Creating an realtime collaboration tool: Agile Flush - .NET Oxford
marcduiker
35
2.6k
So, you think you're a good person
axbom
PRO
2
2.2k
Unsuck your backbone
ammeep
672
58k
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Designing for Performance
lara
612
70k
The Cost Of JavaScript in 2023
addyosmani
55
10k
GraphQLとの向き合い方2022年版
quramy
50
15k
Transcript
BPF の現在 Kawai, Hiroaki
cBPF, eBPF • BPF = Berkeley Packet Filter • cBPF
= Classic BPF – eBPF と区別するとき • tcpdump/libpcap – フィルタ式 – nfbpf_compile root@ubuntu:~# tcpdump -d arp (000) ldh [12] (001) jeq #0x806 jt 2 jf 3 (002) ret #262144 (003) ret #0 root@ubuntu:~# tcpdump -dd arp { 0x28, 0, 0, 0x0000000c }, { 0x15, 0, 1, 0x00000806 }, { 0x6, 0, 0, 0x00040000 }, { 0x6, 0, 0, 0x00000000 }, root@ubuntu:~# tcpdump -ddd arp 4 40 0 0 12 21 0 1 2054 6 0 0 262144 6 0 0 0
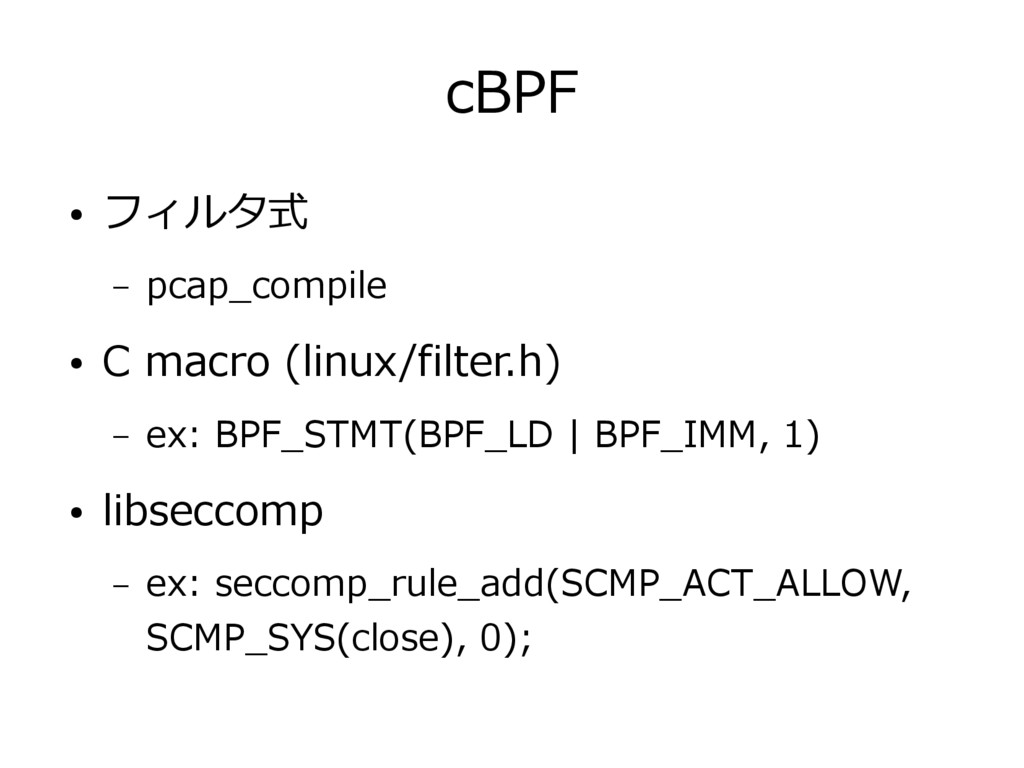
cBPF • フィルタ式 – pcap_compile • C macro (linux/filter.h) –
ex: BPF_STMT(BPF_LD | BPF_IMM, 1) • libseccomp – ex: seccomp_rule_add(SCMP_ACT_ALLOW, SCMP_SYS(close), 0);
eBPF • eBPF = 命令セットとして整備(別物) – ISA (Instruction Set Architecture)
– 64bit(x86_64, ARM64と整ってきたので) • JIT in kernel – CPU 命令セットにマッピング – cBPF も eBPF 経由で JIT される https://events.linuxfoundation.org/sites/events/files/slides/ebpf_on_the_mainframe_lcon_2015.pdf
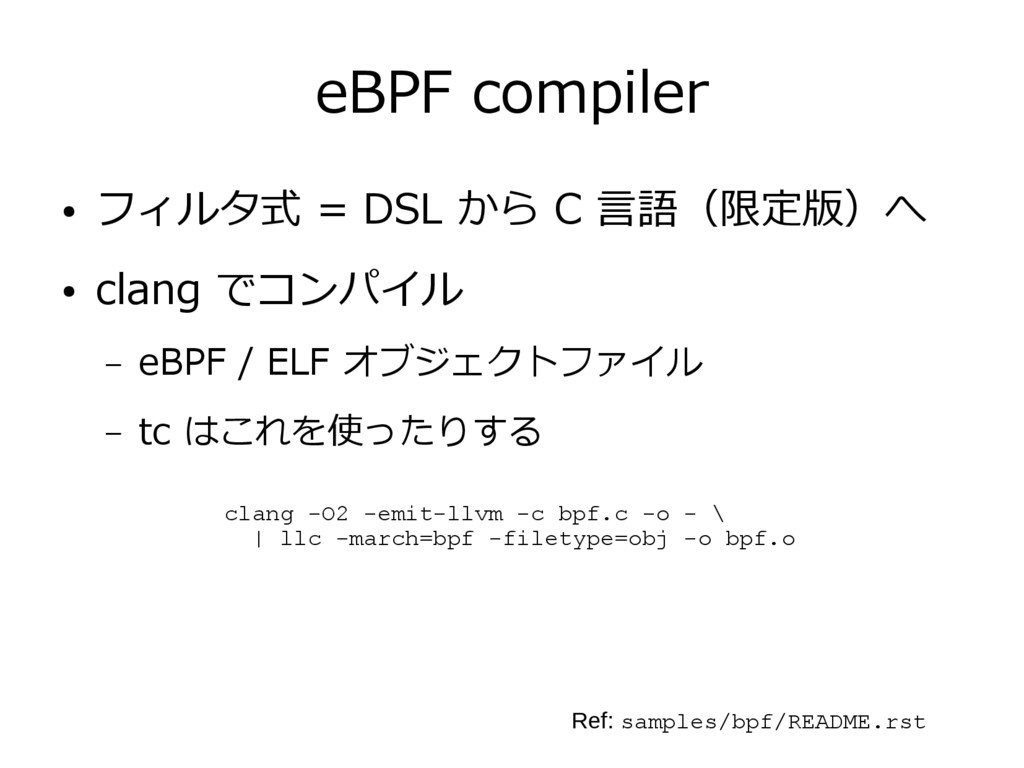
eBPF compiler • フィルタ式 = DSL から C 言語(限定版)へ •
clang でコンパイル – eBPF / ELF オブジェクトファイル – tc はこれを使ったりする clang -O2 -emit-llvm -c bpf.c -o - \ | llc -march=bpf -filetype=obj -o bpf.o Ref: samples/bpf/README.rst
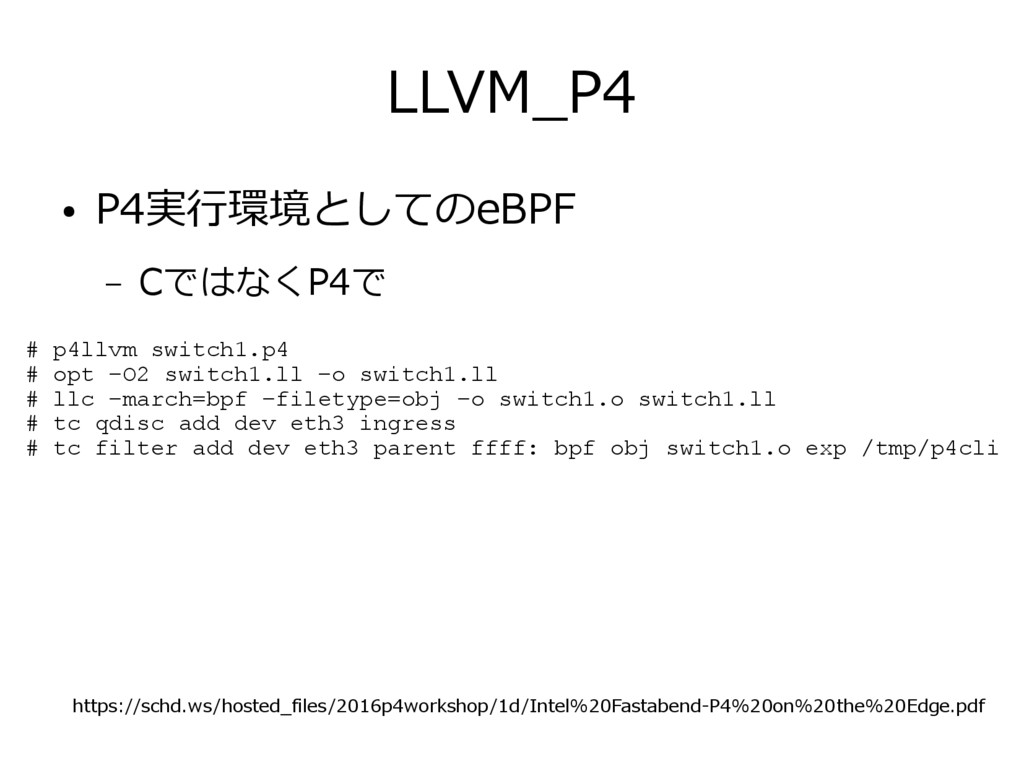
LLVM_P4 • P4実行環境としてのeBPF – CではなくP4で # p4llvm switch1.p4 # opt
–O2 switch1.ll –o switch1.ll # llc –march=bpf –filetype=obj –o switch1.o switch1.ll # tc qdisc add dev eth3 ingress # tc filter add dev eth3 parent ffff: bpf obj switch1.o exp /tmp/p4cli https://schd.ws/hosted_files/2016p4workshop/1d/Intel%20Fastabend-P4%20on%20the%20Edge.pdf
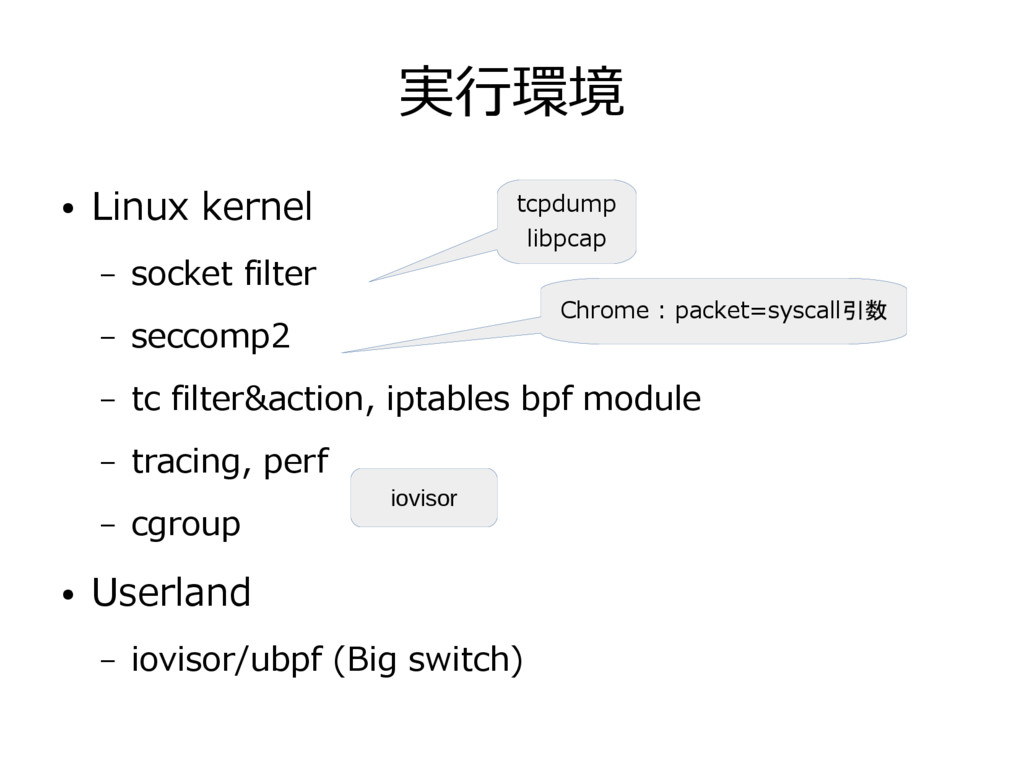
実行環境 • Linux kernel – socket filter – seccomp2 –
tc filter&action, iptables bpf module – tracing, perf – cgroup • Userland – iovisor/ubpf (Big switch) Chrome : packet=syscall引数 tcpdump libpcap iovisor
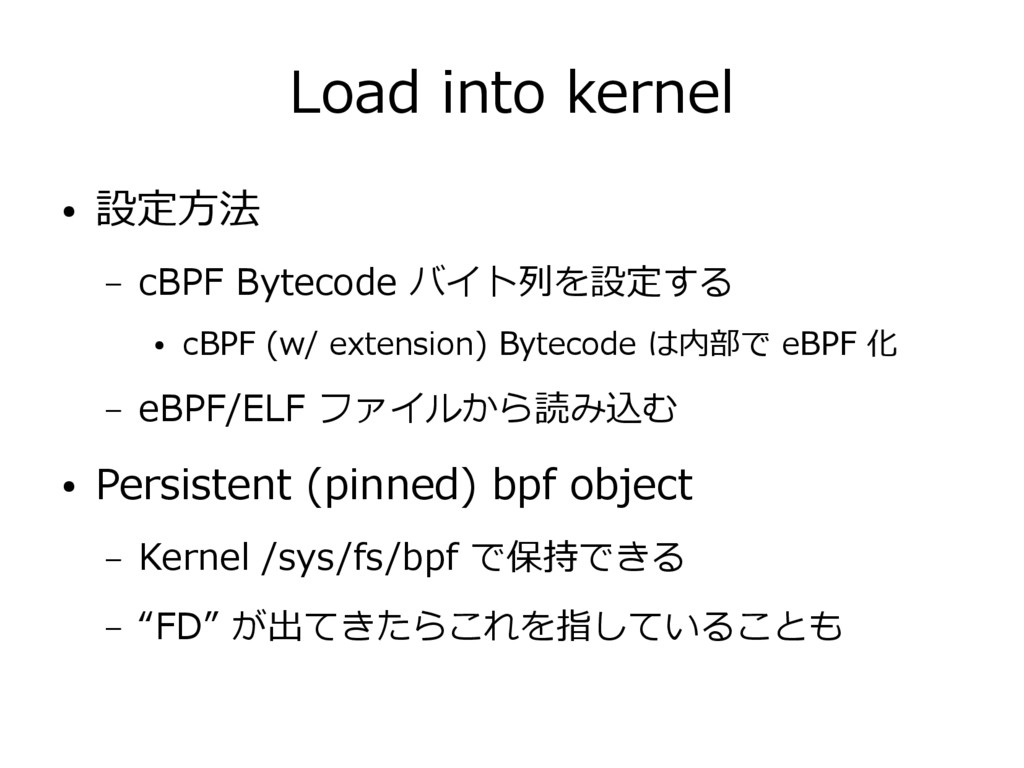
Load into kernel • 設定方法 – cBPF Bytecode バイト列を設定する •
cBPF (w/ extension) Bytecode は内部で eBPF 化 – eBPF/ELF ファイルから読み込む • Persistent (pinned) bpf object – Kernel /sys/fs/bpf で保持できる – “FD” が出てきたらこれを指していることも
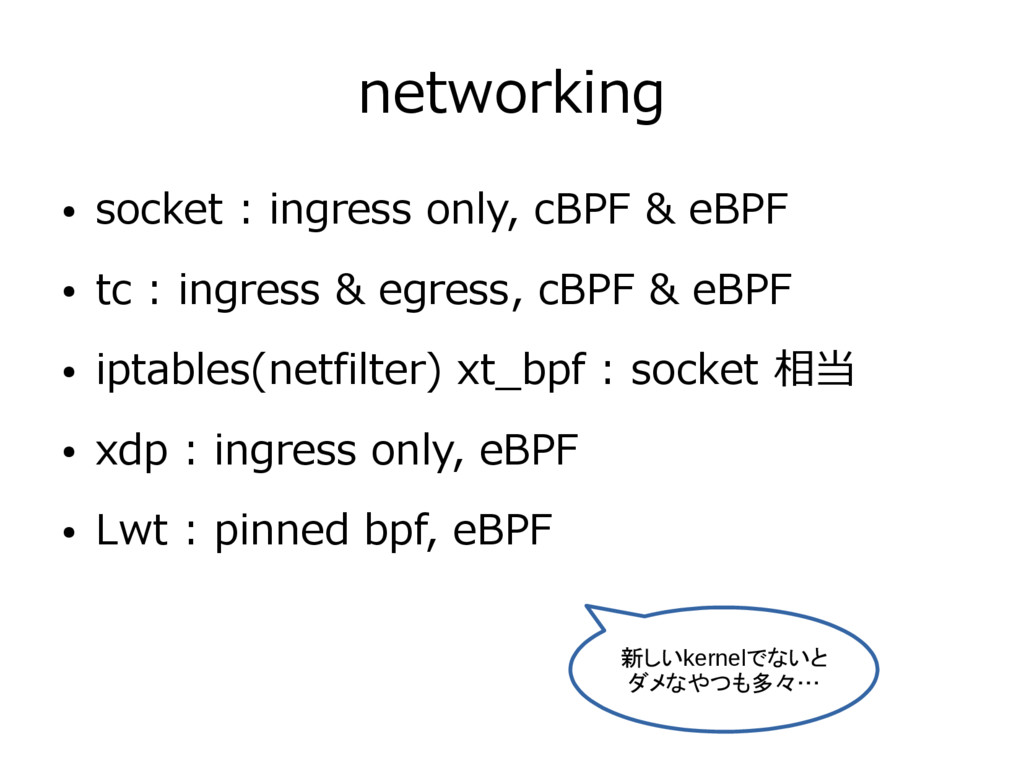
networking • socket : ingress only, cBPF & eBPF •
tc : ingress & egress, cBPF & eBPF • iptables(netfilter) xt_bpf : socket 相当 • xdp : ingress only, eBPF • Lwt : pinned bpf, eBPF 新しいkernelでないと ダメなやつも多々…
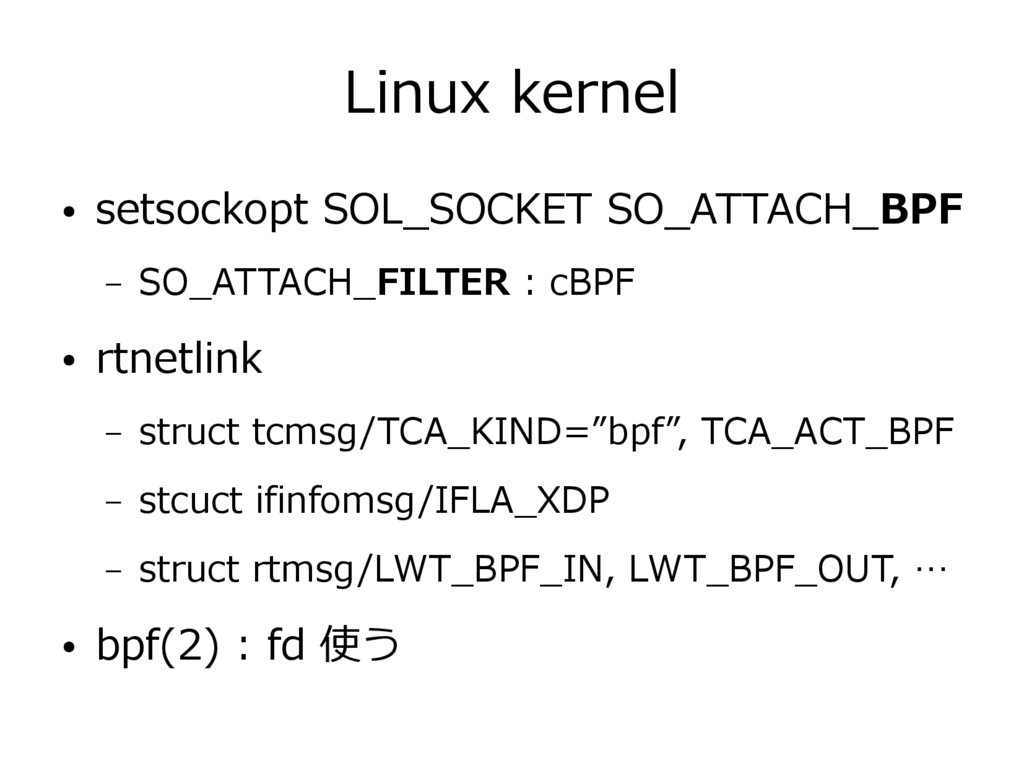
Linux kernel • setsockopt SOL_SOCKET SO_ATTACH_BPF – SO_ATTACH_FILTER : cBPF
• rtnetlink – struct tcmsg/TCA_KIND=”bpf”, TCA_ACT_BPF – stcuct ifinfomsg/IFLA_XDP – struct rtmsg/LWT_BPF_IN, LWT_BPF_OUT, … • bpf(2) : fd 使う
bpf_prog_type • in-kernel での制限チェックで使われる • Packet data にアクセスできるか等 • きちんと完了するプログラムか等
• BPF fd の属性値として保持される • linux/bpf.h – BPF_PROG_TYPE_* – fdinfo (4.8~) SOCKET_FILTER KPROBE SCHED_CLS, SCHED_ACT TRACEPOINT XDP PERF_EVENT CGROUP_SKB, CGROUP_SOCK LWT_IN, LWT_OUT, LWT_XMIT
eBPF in C • 引数と返値 – tc : struct __sk_buff
• filter classifier と filter action で返値の意味が異なる – xdp : struct xdp_md : sk_buff に似せてある • BPF MAP – パケット数えたり – ルールを保持したり
BPF MAP • 種類 – BPF_TABLE • BPF_HASH • BPF_HISTOGRAM
• BPF_STACK_TRACE – BPF_TABLE_PUBLIC – BPF_PERF_OUTPUT – BPF_PERF_ARRAY root@ubuntu:/proc/3463/fd# ls -l total 0 lrwx------ 1 root root 64 Dec 22 02:21 0 -> /dev/pts/17 lrwx------ 1 root root 64 Dec 22 02:21 1 -> /dev/pts/17 lrwx------ 1 root root 64 Dec 22 02:21 10 -> anon_inode:bpf-map lrwx------ 1 root root 64 Dec 22 02:21 11 -> anon_inode:bpf-map lrwx------ 1 root root 64 Dec 22 02:21 12 -> anon_inode:bpf-prog lrwx------ 1 root root 64 Dec 22 02:21 13 -> anon_inode:bpf-prog lrwx------ 1 root root 64 Dec 22 02:21 14 -> anon_inode:bpf-prog lrwx------ 1 root root 64 Dec 22 02:21 15 -> anon_inode:bpf-prog lrwx------ 1 root root 64 Dec 22 02:21 2 -> /dev/pts/17 lr-x------ 1 root root 64 Dec 22 02:21 3 -> /dev/urandom lr-x------ 1 root root 64 Dec 22 02:21 4 -> pipe:[35440] l-wx------ 1 root root 64 Dec 22 02:21 5 -> pipe:[35440] lrwx------ 1 root root 64 Dec 22 02:21 6 -> socket:[35441] lr-x------ 1 root root 64 Dec 22 02:21 7 -> pipe:[35442] l-wx------ 1 root root 64 Dec 22 02:21 8 -> pipe:[35442] lrwx------ 1 root root 64 Dec 22 02:21 9 -> socket:[35443]
Writing eBPF • iovisor/bcc 使う(依存は増える) – BPF_MAP_GET_NEXT_KEY 無かったりとかもある • tc
filter classifier 使うのが現実的な選択 • C言語はコンパイラのココロを読みながら書く – prog_load失敗する=ココロが通じなかったとき • bpf_trace_printk – cat /sys/kernel/debug/tracing/trace_pipe
Tools • ubpf-disassembler (ubpf) – eBPF • bpfc (netsniff-ng) –
cBPF (w/ extension) • bpf_dbg (kernel) – eBPF


 kwi
 l1ghthouse
 nagix
 mhrtech
 chmikata
 sakusaku3939
 konifar
 joere
 kworkdev
 sraku2159
 atsushieno
 legalontechnologies
 yakumo
 afnizarnur
 eileencodes
 maggiecrowley
 honnibal
 chriscoyier
 marcduiker
 axbom
 ammeep
 lara
 addyosmani
 quramy